
lil-pwny
 papermtn/lil-pwny
Fast offline auditing of Active Directory passwords using Python.
authenticationpassword-crackingvulnerability-analysis
papermtn/lil-pwnyFast offline auditing of Active Directory passwords using Python.
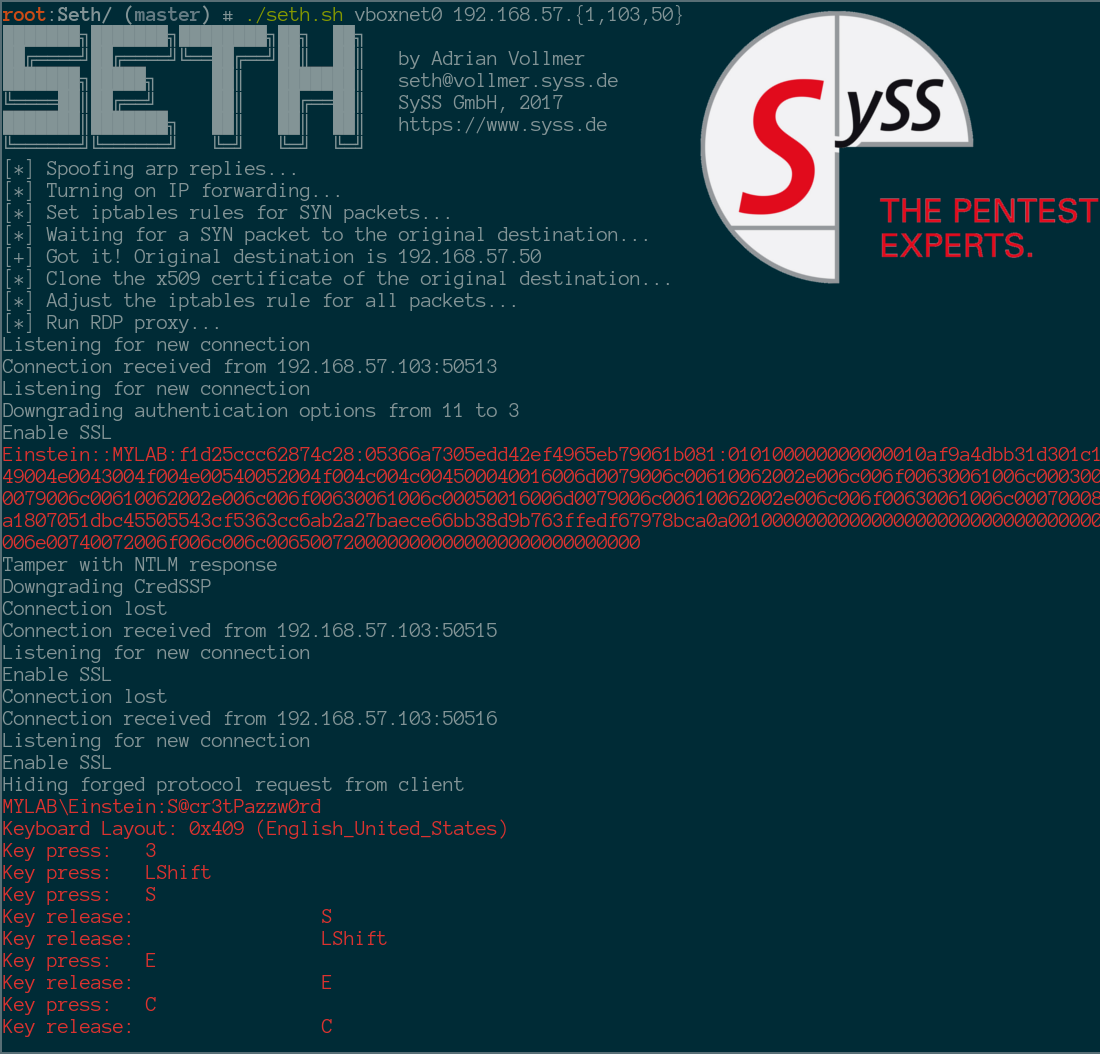 syss-research/seth
Perform a MitM attack and extract clear text credentials from RDP connections
 dropbox/securitybot
Distributed alerting for the masses!
 0xmandor/cve-2025-50433
Proof of concept for a critical Monnit Cloud account takeover (CVE-2025-50433), exploiting missing token-email validation in password reset and…
 george0papasotiriou/cve-2026-11116-snmpv3-authentication-bypass-via-default-engineid
Demonstrates CVE-2026-11116 SNMPv3 authentication bypass caused by guessable default EngineIDs, with a Python pysnmp simulation and guidance for…
 kartik2005221/cve-2025-58434-poc
Proof-of-concept exploit for CVE-2025-58434, demonstrating unauthenticated account takeover in Flowise via leaked password reset tokens. Includes…
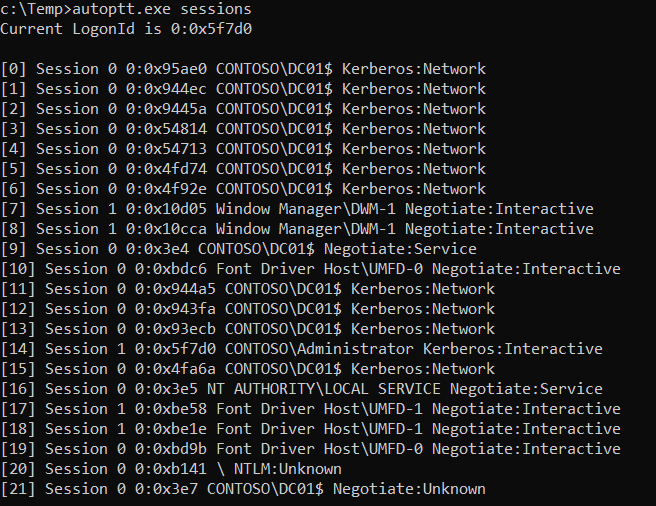 ricardojoserf/autoptt
Automated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
 e-m-e-k-a/moniker-link-lab-setup
Penetration testing lab demonstrating CVE-2024-21413 moniker link exploitation for NTLM credential theft, including attack execution, hash cracking,…
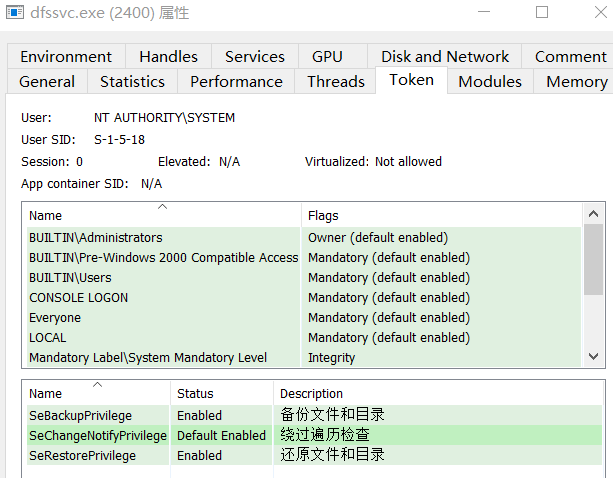 crisprss/magicnetdefs
Similar to Petitpotam, the netdfs service is enabled in Windows Server and AD environments, and the abused RPC method allows privileged processes to…
 pr0x13/idict
PHP-based iCloud Apple ID dictionary attack tool that bypasses account lockout and secondary authentication to brute-force credentials.
 secnigma/cve-2021-3560-polkit-privilege-esclation
Automated Bash PoC for CVE-2021-3560 polkit privilege escalation. Exploits dbus timing attack to inject a sudo user and gain root shell on vulnerable…
 b5null/invoke-badsuccessor.ps1
PowerShell Script to automatically abuse the BadSuccessor vulnerability (CVE-2025-53779)
 aakashtyal/2fa-bypass-using-a-brute-force-attack-cve-2025-60424
Demonstrates a brute-force attack bypassing two-factor authentication in Nagios Fusion due to missing rate limiting and lockout, with CVE-2025-60424…
 jwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report
Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…
 rickidevs/cve-2026-26717
Technical write-up of CVE-2026-26717, an HMAC timing attack in OpenFUN Richie LMS webhook authentication, including vulnerable code, impact, and fix…
 mreza-en/cve-2021-21994_poc
Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.
 kh4sh3i/cve-2022-23131
Python exploit for CVE-2022-23131 targeting Zabbix SAML SSO authentication bypass. Includes Shodan and FOFA dorks for vulnerable instance discovery.
 nfc-tools/mfoc
Offline nested attack tool that recovers MIFARE Classic authentication keys using known default or user-supplied keys for assessing NFC/RFID card…