
MemorizingTrustManager
 ge0rg/memorizingtrustmanager
A "plugin" for Android Java to allow asking the user about SSL certificates
android-securityauthenticationcryptography+3
ge0rg/memorizingtrustmanagerA "plugin" for Android Java to allow asking the user about SSL certificates
 tyranid/blackhat-usa-2022-demos
Demos for the Blackhat USA 2022 talk "Taking Kerberos to the Next Level"
 qax-a-team/mscache
a tool to manipulate dcc(domain cached credentials) in windows registry, based mainly on the work of mimikatz and impacket
 rickgeex/proxylogon
ProxyLogon is the formally generic name for CVE-2021-26855, a vulnerability on Microsoft Exchange Server that allows an attacker bypassing the…
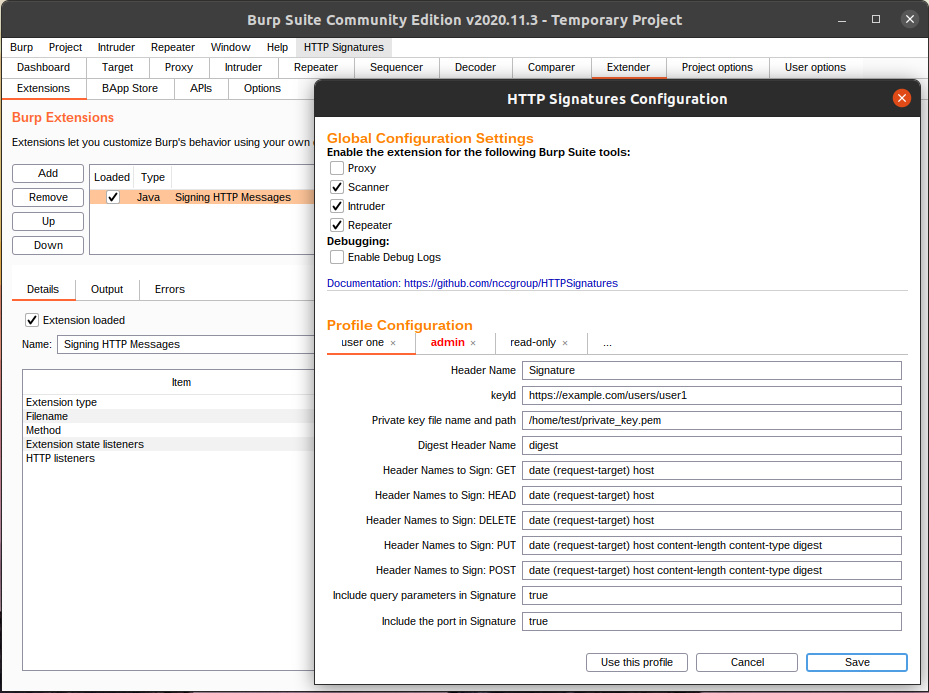 nccgroup/httpsignatures
A Burp Suite extension implementing the Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 draft.
 agentsid-dev/agentsid-scanner
Security scanner for MCP servers. Grades auth, permissions, injection risks, and tool safety. The Lighthouse of agent security.
 blackxploit-404/torchat
TorChat - Secure, private, and anonymous peer-to-peer chat over the Tor network
 kartik2005221/cve-2025-58434-and-59528-poc
Modular PoC for CVE-2025-58434 (account takeover) and CVE-2025-59528 (RCE) in Flowise. Automates the full attack chain from unauthenticated token…
 chybeta/cve-2017-11427-demo
The Demo for CVE-2017-11427
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
 geniuszly/gencrushsstiexploit
is a PoC for CVE-2024-4040 tool for exploiting the SSTI vulnerability in CrushFTP
 exfil0/cve-2025-59718-poc
Fortinet announced two closely related authentication‑bypass vulnerabilities on 9 December 2025. Both flaws involve improper verification of…
 oscerd/cve-2026-84181
Runnable Spring Boot and Quarkus proof-of-concept reproducing the Apache Camel camel-shiro thread-bound-subject authentication bypass, with affected…
 oscerd/cve-2026-85301
Runnable proof-of-concept reproducer for the Apache Camel camel-keycloak issuer validation bypass (CWE-287), demonstrating affected and patched…
 ritwick7/sudostamp
Approve sudo on a Linux workstation with a fingerprint on your Android phone. LAN only; the ECDSA key never leaves the phone's TEE and speaks the…
 azureadtrent/cve-2026-52824
Technical analysis and PoC of CVE-2026-52824: default APP_SECRET in the Kimai Docker image enabling unauthenticated login link forgery. Affects <=…
 george0papasotiriou/cve-2026-11116-snmpv3-authentication-bypass-via-default-engineid
Demonstrates CVE-2026-11116 SNMPv3 authentication bypass caused by guessable default EngineIDs, with a Python pysnmp simulation and guidance for…
 d1se0/cve-2024-10924-bypass-mfa-wordpress-lab
Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…