
 wolfssl/wolfssh
Small, portable embeddable SSHv2 client and server library in C with SCP, SFTP, port forwarding, and post-quantum key exchange for embedded and IoT…
 foxboron/attezt
An open-source TPM device-attest-01 CA server
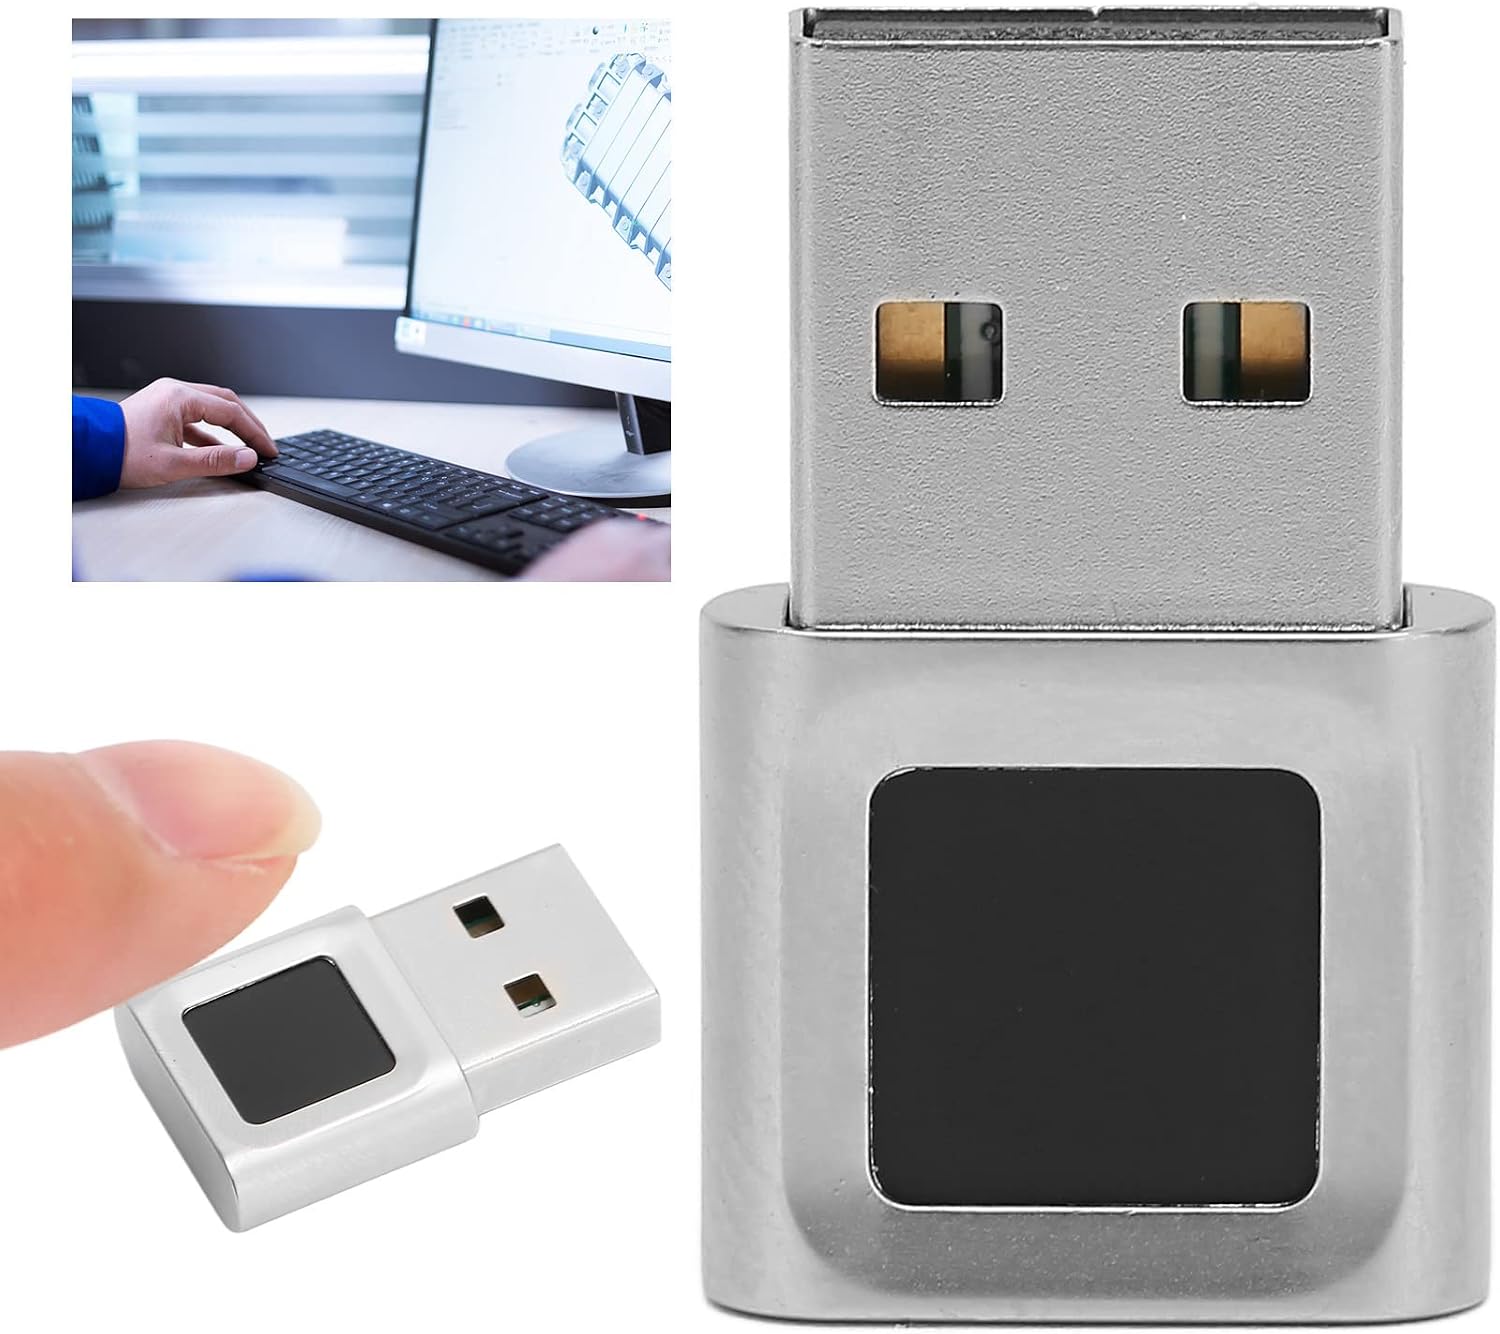 omgrant/ft9201-libfprint
Linux libfprint driver for the Focal-systems FT9201 (2808:93a9) USB fingerprint reader — runs FocalTech's own Windows matching engine natively on…
 remenis/cve-2025-63667
Vatilon-based IP camera firmwares issue Session-Id tokens without verifying credentials, allowing attackers to obtain sessions and retrieve plaintext…
 netsecfish/dlink
Proof-of-concept exploit and analysis for command injection and hardcoded backdoor credentials in D-Link NAS devices, enabling unauthenticated remote…
 zzz66686/cve-2017-14263
Proof-of-concept exploit for CVE-2017-14263 in Honeywell NVR devices. Demonstrates session hijacking and privilege escalation from guest to admin via…
 on3sk-0x1/cve-2026-19900-poc
Proof-of-concept exploit for CVE-2026-19900, an authentication bypass and remote code execution vulnerability in LB-LINK X-PRO routers, allowing…
 d-raco/cve-2024-31964
Proof-of-concept exploit for CVE-2024-31964, a temporary authentication bypass in Mitel 6900w Series SIP phones allowing unauthenticated POST…
 joelczk/cve-2025-48461
Technical disclosure of a predictable session cookie vulnerability (CVE-2025-48461) in Advantech WISE-4060 IoT portal, enabling bruteforce…
 cappricio-securities/cve-2024-5947
Deep Sea Electronics DSE855 - Authentication Bypass
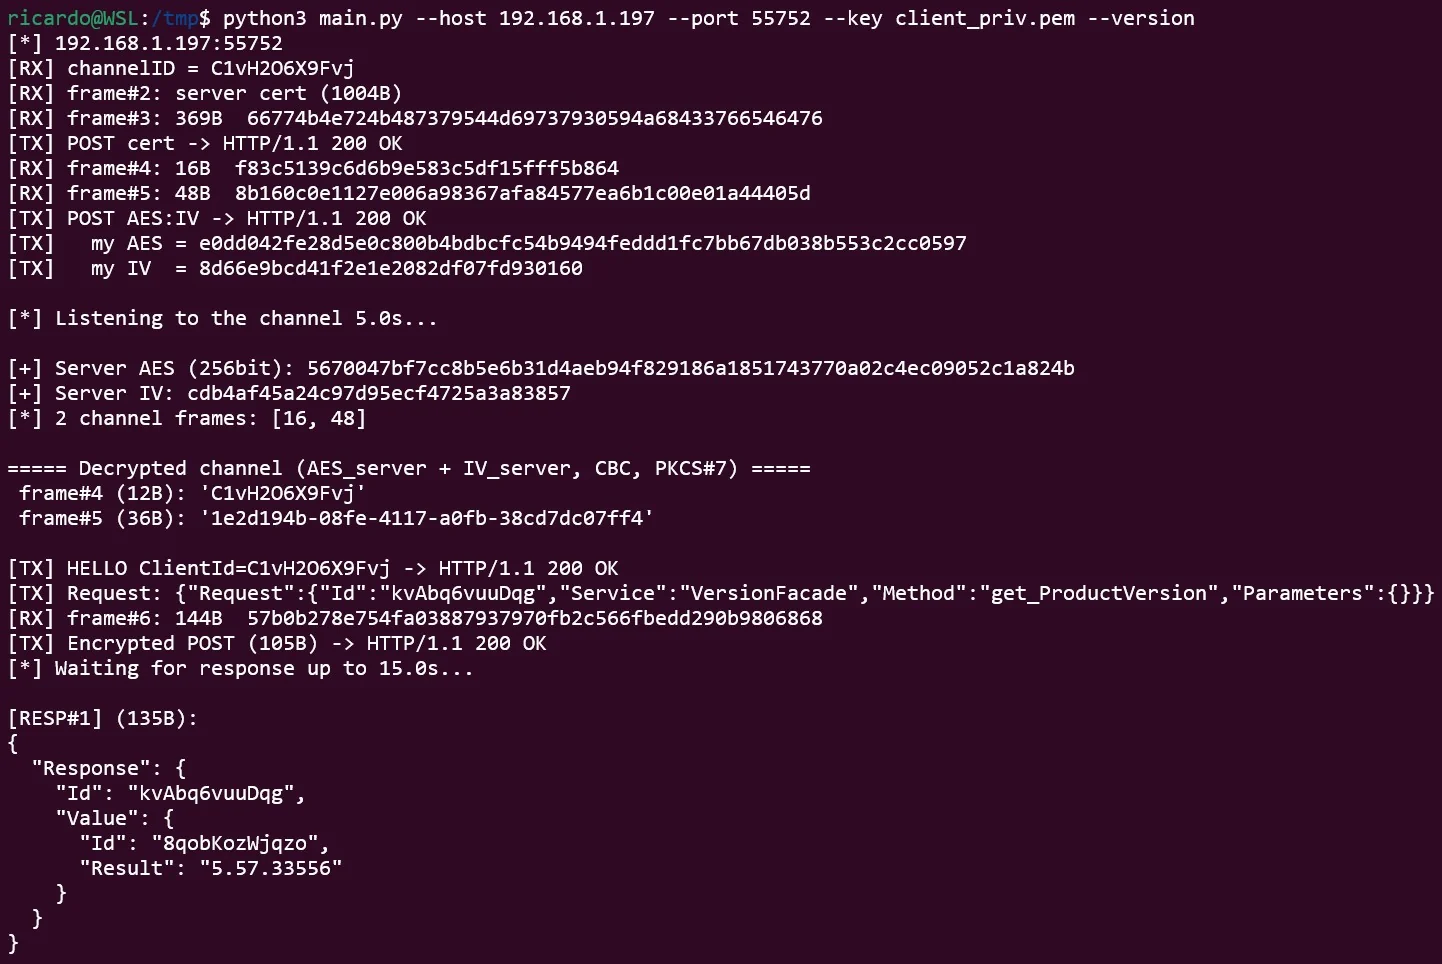 ricardojoserf/axis-rce
Unauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)