
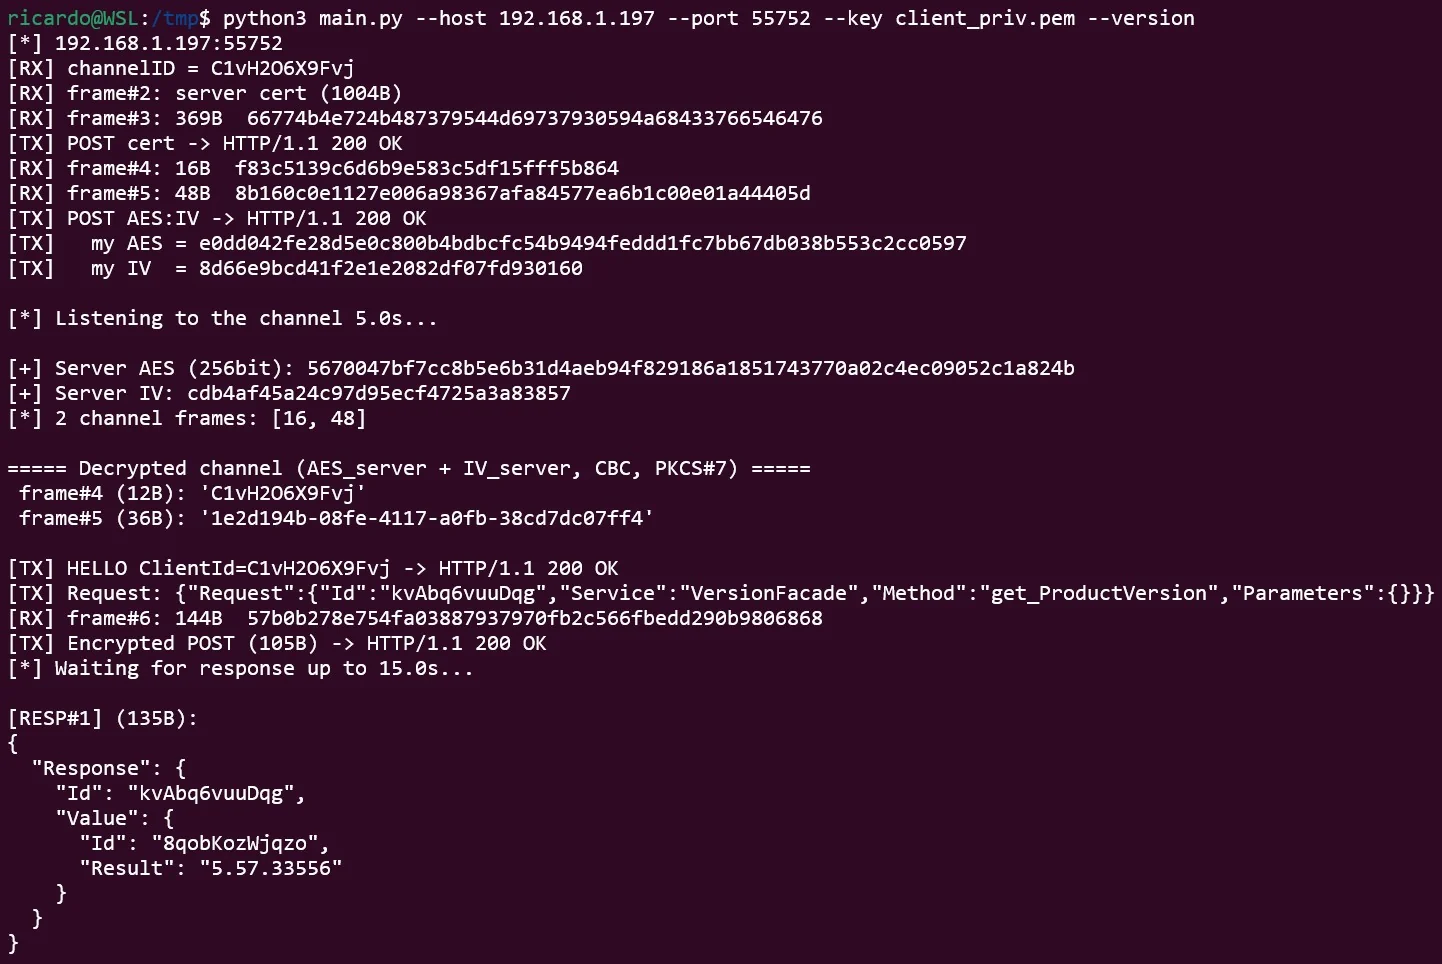
axis-RCE
 ricardojoserf/axis-rce
Unauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)
authenticationcryptographyexploitation+6
6
ricardojoserf/axis-rceUnauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)
 affolter-engineering/mqattack
Rust CLI for MQTT penetration testing: subscribe/publish, broker fingerprinting, ACL probing, topic enumeration, credential brute-force, and Last…
 ylianst/meshcentral
A complete web-based remote monitoring and management web site. Once setup you can install agents and perform remote desktop session to devices on…
 digiprosec/microtrick
Self-contained Python PoC exploiting the MikroTrick SSH chain (CVE-2026-86060, CVE-2026-67279) to gain unauthenticated full admin access on MikroTik…
 dinosn/mikrotrick-poc
CVE-2026-67276 RouterOS SSH public-key authentication bypass lab PoC
 on3sk-0x1/cve-2026-19900-poc
Proof-of-concept exploit for CVE-2026-19900, an authentication bypass and remote code execution vulnerability in LB-LINK X-PRO routers, allowing…
 tony102741/cve-2026-15469
Advisory and technical analysis of CVE-2026-15469, a hard-coded RSA-512 mesh group private key in TP-Link Deco routers, including root cause, impact,…
 aye468448-eng/cve-2026-0073-android-adbd-authentication-bypass
PoC for CVE-2026-0073, an Android ADB authentication bypass enabling network attackers to connect to previously paired devices over wireless…
 hunt-benito/the-same-key-opens-every-box-cve-2026-71960-hard-coded-jwt-secret-in-cudy-wr3000-mesh-mqtt
PoC toolkit that unpacks router firmware, decrypts device secrets, forges JWT tokens, and exploits CVE-2026-71960/71961 to take over Cudy WR3000 mesh…
 f7p-h4nn1b4l/cve-2018-9995-dvr-credentials-extractor
This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.
 michaeladamgroberman/cve-2025-1242
CVE-2025-1242: Hardcoded iothubowner Connection String — Gardyn Home Kit (ICSA-26-055-03)
 kensh1k/cve-2026-36438
Documentation of CVE-2026-36438: a vulnerability in Intelbras VIP 1230 B/D G4 devices allowing remote attackers to obtain administrator account…
 synwall/synwall
Linux kernel module implementing a zero-configuration, OTP-based firewall for IoT devices. Transparently authenticates network traffic using a…
 sectestannaquinn/cve-2026-0073-android-adbd-authentication-bypass-poc
Proof-of-concept exploit for CVE-2026-0073, an Android ADB authentication bypass allowing network attackers to connect to devices with ADB over TCP…
 umair-aziz025/dahua-cve-research
Dahua IP camera CVE research toolkit (CVE-2021-33044/33045, CVE-2025-31700/31701)
 remenis/cve-2025-67159
Vatilon-based IP camera firmware allows authentication bypass and plaintext credential exposure via web.cgi API requests.
 remenis/cve-2025-67158
Revotech I6032W-FHW IP camera firmware fails to validate authentication fields in API requests, allowing attackers to bypass authentication and…
 kirubel-cve/cve-2025-65427
Proof-of-concept exploit for CVE-2025-65427: missing rate limiting on Dbit N300 T1 Pro router login API enabling brute-force attacks and…