
CVE-2026-18963
 alt3kx/cve-2026-18963
Detection and verification tool for CVE-2026-18963, a Keycloak reset-credentials state bypass. Performs version fingerprinting, realm/client/user…
authenticationexploitationinformation-gathering+4
4
alt3kx/cve-2026-18963Detection and verification tool for CVE-2026-18963, a Keycloak reset-credentials state bypass. Performs version fingerprinting, realm/client/user…
 h4zaz/cve-2026-8794
Username Enumeration via Authentication Timing Side-Channel in PaperCut NG
 h4zaz/cve-2026-8793
esponsible disclosure write-ups for CVE-2026-8793 - PaperCut NG 25.0.11
 mreza-en/cve-2021-21994_poc
Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.
 azureadtrent/cve-2026-52824
Technical analysis and PoC of CVE-2026-52824: default APP_SECRET in the Kimai Docker image enabling unauthenticated login link forgery. Affects <=…
 0xrixet/craftcms-poc-cve-2026-31266
Security research on Craft CMS authentication mechanism
 xmyronn/cve-2026-10288-auth-bypass
Proof-of-concept exploit for an authentication bypass in Hotel and Tourism Reservation System 1.0, allowing unauthenticated admin access via inverted…
 michaeladamgroberman/cve-2026-28766
CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 xmyronn/cve-2026-10243-auth
Proof of concept demonstrating unauthenticated access to critical admin functions in Smart Parking System 1.0, allowing account creation, data…
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
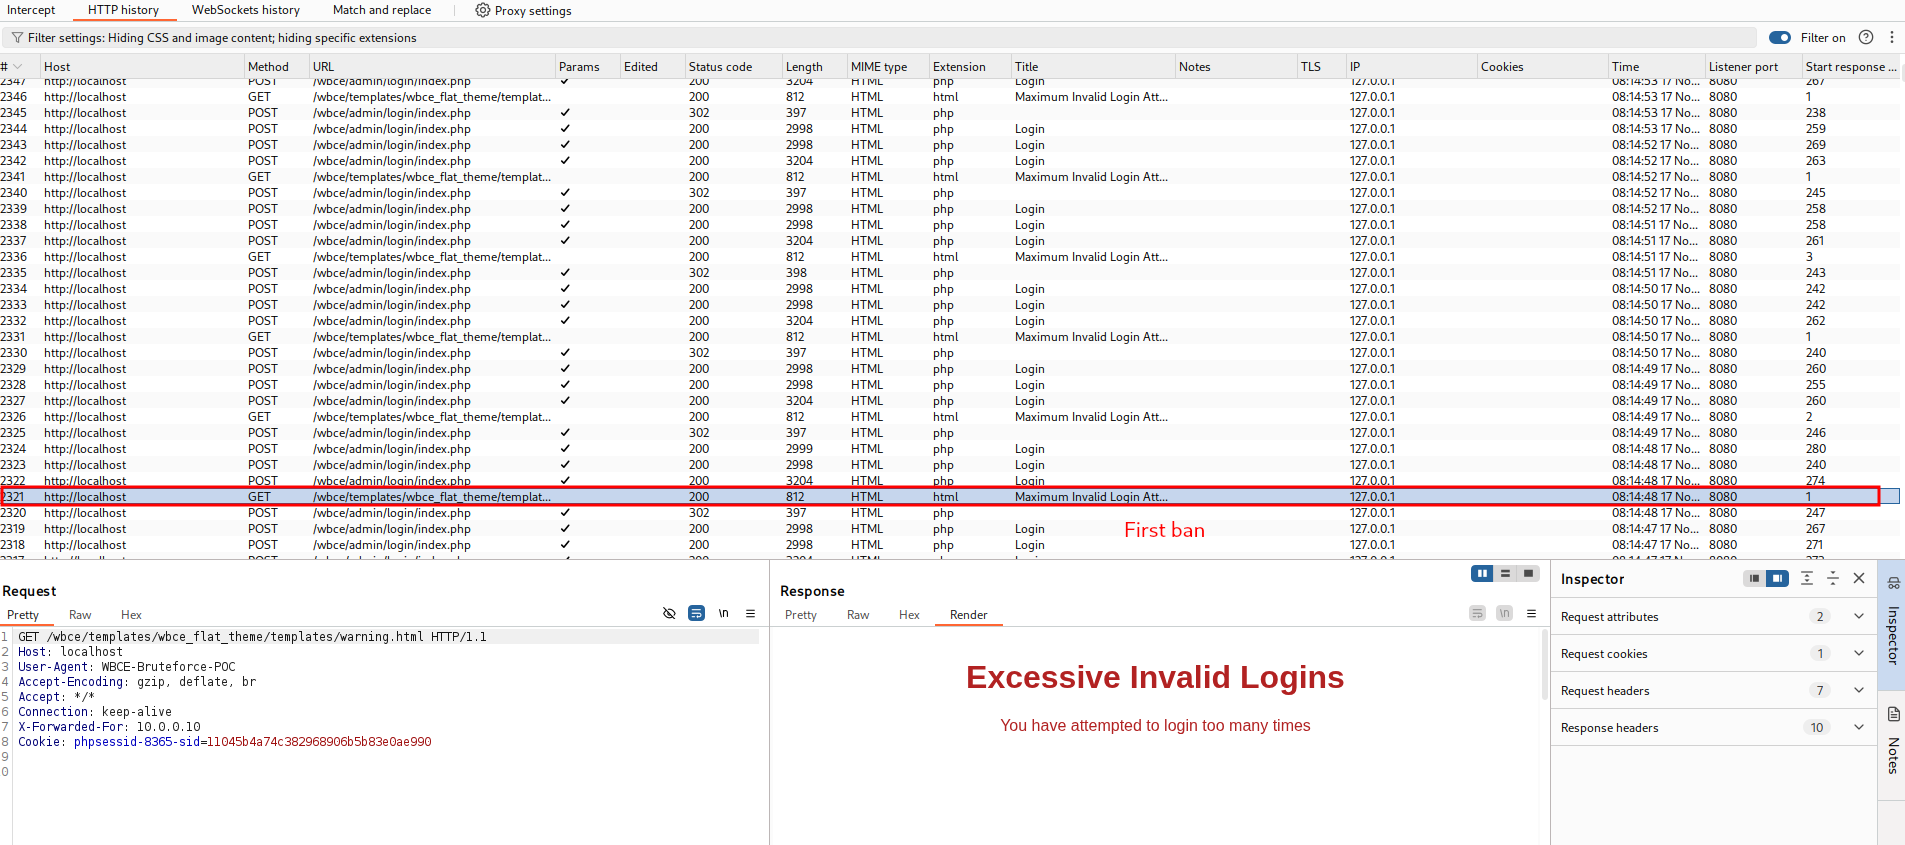 lukasz-rybak/cve-2025-66204
Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…
 popyue/cve-2025-47812
RCE for WingFTP v4.7.3