
CVE-2026-24061
 obrunolima1910/cve-2026-24061
🚨 Exploit CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd, for instant root shell access without authentication.
authenticationeducationexploitation+3
obrunolima1910/cve-2026-24061🚨 Exploit CVE-2026-24061, a critical remote authentication bypass in GNU inetutils-telnetd, for instant root shell access without authentication.
 ish3ng0m4/cve-2026-24061-telnetd
CVE-2026-24061 GNU Inetutils Telnetd Authentication Bypass
 ilokaas/cve-2026-24061-payload
A PoC exploit for CVE-2026-24061 - GNU InetUtils telnetd Argument Injection Authentication Bypass
 harygovind/cve-2026-24061
CVE-2026-24061-PoC
 sh4den/cve-2026-24061
Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…
 akpmarcelin/cve-2026-24061-lab
Reproduction lab for CVE-2026-24061, an authentication bypass in GNU InetUtils telnetd. Provides a Vagrant-based isolated environment and…
 anxs3c/cve-2026-24061-gnu-inetutils-telnetd
GNU-InetUtils-telnetd-Authentication-Bypass-Vulnerability
 ahmadsadeeq/telnetdbypass-
CVE-2026-24061 — GNU InetUtils Telnetd Authentication Bypass Scanner
 ekomssavior/telnet_scan
scanner/exploiter CVE-2026-24061 & CVE-2026-32746
 franckferman/cve-2026-24061
GNU InetUtils telnetd - Unauthenticated Remote Root via NEW-ENVIRON Variable Injection.
 hd0x01/cve-2026-24061-nse
The script performs a full Telnet negotiation mirroring the exact byte sequence of a real telnet -a client session.
 mbanyamer/cve-2026-24061-gnu-inetutils-telnetd-remote-authentication-bypass-root-shell-
Proof-of-concept exploit for GNU Inetutils telnetd authentication bypass (CVE-2026-24061) that spawns a root shell via crafted NEW-ENVIRON USER…
 canpilayda/inetutils-telnetd-cve-2026-24061
Walkthrough of the CVE-2026-24061 authentication bypass in GNU Inetutils telnetd, demonstrated in a Hackviser lab environment.
 buzz075/cve-2026-24061
Deep technical analysis and scanner for CVE-2026-24061, a critical authentication bypass in GNU InetUtils telnetd, including exploit chain, PoC, and…
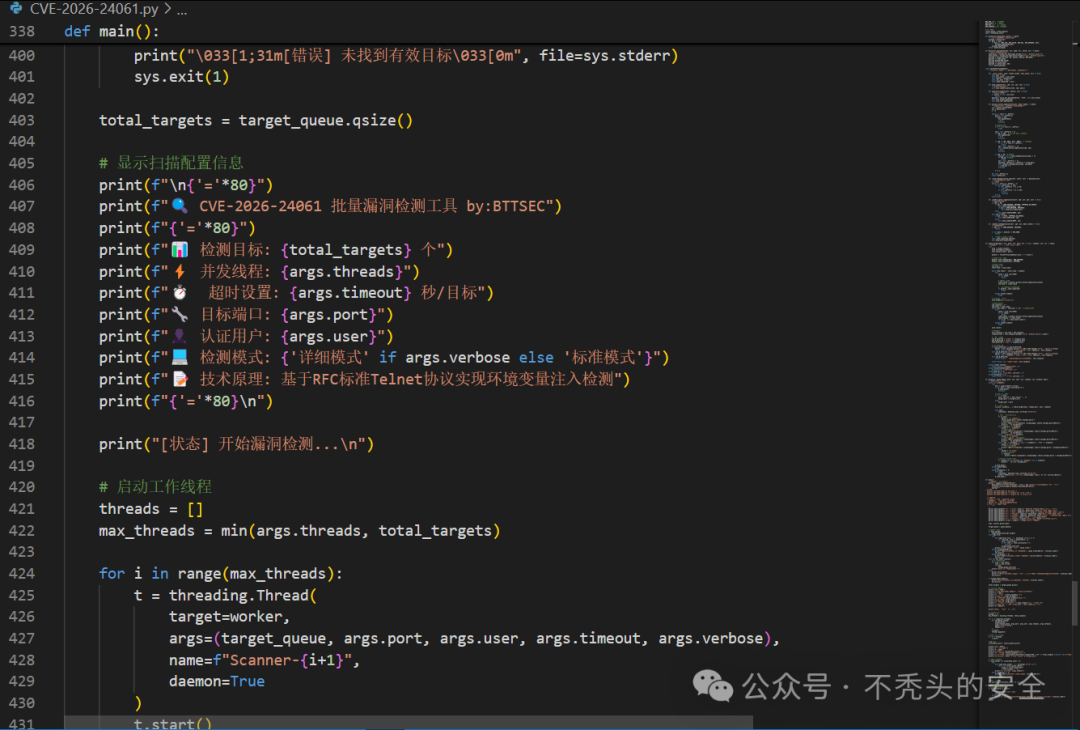 my0723/gnu-inetutils-telnet-cve-2026-24061-
GNU Inetutils telnet远程认证绕过漏洞(CVE-2026-24061),该漏洞源于 GNU Inetutils telnetd 组件中对环境变量处理不当,攻击者可利用该漏洞,通过构造恶意的 USER 环境变量并发送至受影响的 telnet…
 gabs-hub/cve-2026-24061_lab
Educational Docker lab demonstrating CVE-2026-24061, an authentication bypass in GNU telnetd allowing root access via argument injection in the USER…
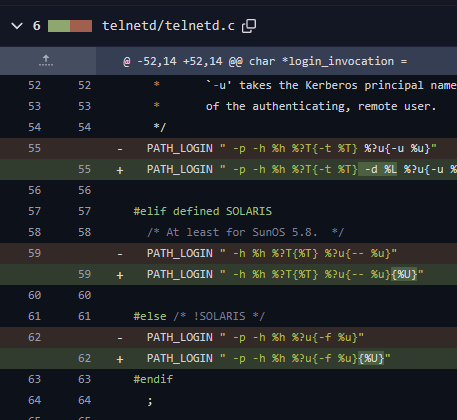 lucaspdiniz/cve-2026-24061
Vulnerability in GNU InetUtils telnetd Enables Remote Root Access
 monstertsl/cve-2026-24061
Python-based scanner that detects CVE-2026-24061 in GNU Inetutils telnetd, allowing batch testing of multiple targets for the authentication bypass…