

spire
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
authenticationauthentication-authorizationcloud-infrastructure-security+5
2.6k
spiffe/spireWorkload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 lissy93/awesome-privacy
🦄 A curated list of privacy & security-focused software and services
 arensballiu/flowise-cve-2025-58434-passwordreset
Unauthenticated password reset exploit for Flowise AI ≤ 3.0.5. Abuses the /api/v1/account/forgot-password endpoint to change any user's password…
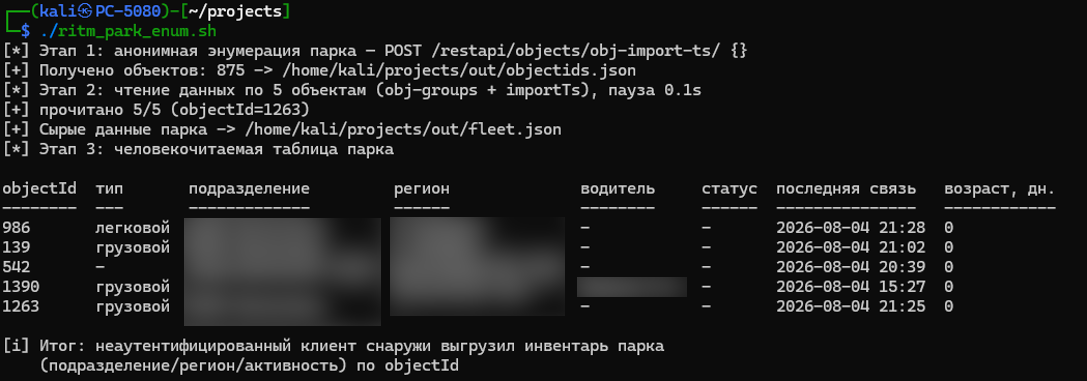 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 o-sec/cve-2026-41452-poc
Proof-of-concept exploit for CVE-2026-41452, a critical authentication bypass in Krayin CRM <= 2.2.4 allowing unauthenticated admin account takeover…
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
 pcrosby-1990/cip-security-poc
Proof-of-concept reproducing CVE-2021-22681's hardcoded-key flaw and validating a per-device mutual TLS/CRL fix over simulated EtherNet/IP, with IEC…
 razureink/cve-2024-1708-connectwise_rce_reproduction
Reproduction of cve-2024-1708-connectwise_rce_reproduction
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 mrash/fwknop
Single Packet Authorization > Port Knocking
 kajzingerakos/cve-2026-25253
Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click remote code execution in OpenClaw via authentication token theft and cross-site…
 0xblackash/cve-2026-20079
CVE-2026-20079
 ready2disclose/cve-2022-43110
CVE-2022-43110
 joshuavanderpoll/cve-2025-69985
Python exploit for CVE-2025-69985 targeting FUXA SCADA software. Sends crafted JSON payload to /api/runscript endpoint to bypass authentication and…
 perunchess/cve-2025-66698
Proof-of-concept for CVE-2025-66698: authentication bypass in Veda v5.4.8 via empty ticket parameter, enabling enumeration of users, policies, and…
 dairrow/cve-2025-31161
PoC Authentication Bypass to RCE to Exploit CVE-2025-31161