
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2026-20079 — CVE-2026-20079 | Kitploit
Tools/GitHubGitHub/0xblackash/cve-2026-20079
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingAuthenticationRed Teaming
GitHub0xblackash/cve-2026-20079

CVE-2026-20079

CVE-2026-20079

View Repository
2317 months agoNot yet reviewed
Share

🚨 CVE-2026-20079 "Critical Cisco FMC Zero-Day"

cisco-exploit

Critical Authentication Bypass Leading to Root RCE in Cisco Secure Firewall Management Center

Severity CVSS Cisco FMC Published

📋 Overview

CVE-2026-20079 is a critical vulnerability in the web interface of Cisco Secure Firewall Management Center (FMC) Software.

An unauthenticated remote attacker can bypass authentication and execute arbitrary scripts with root privileges on the underlying operating system.

  • CVE ID: CVE-2026-20079
  • CWE: CWE-288 (Authentication Bypass Using an Alternate Path or Channel)
  • CVSS v3.1 Base Score: 10.0 (Critical)
  • Vector: CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:H/A:H

Root Cause: An improper system process created at boot time that allows crafted HTTP requests to bypass authentication.


🛠️ Impact

  • Unauthenticated remote exploitation
  • Full root access to the FMC appliance
  • Ability to execute arbitrary scripts and commands
  • Potential compromise of managed Firewall Threat Defense (FTD) devices (Scope: Changed)
  • Complete loss of confidentiality, integrity, and availability

This vulnerability affects the management plane of Cisco's on-premises firewall infrastructure, making it extremely dangerous in production environments.


🔍 Affected Products

Vulnerable:

  • Cisco Secure Firewall Management Center (on-premises) versions:
    • 7.0.x (all)
    • 7.1.x (all)
    • 7.2.0 – 7.2.10.2
    • 7.3.0 – 7.3.1.2
    • 7.4.0 – 7.4.3
    • 7.6.0 – 7.6.3
    • 7.7.0 – 7.7.11

Not Affected:

  • Cloud-Delivered FMC (cdFMC)
  • Cisco Secure Firewall ASA Software
  • Cisco Secure Firewall Threat Defense (FTD) devices (when not managed by vulnerable FMC)

✅ Fixed Versions

Cisco has released patches. Refer to the official advisory for exact fixed releases per branch.

Recommendation: Upgrade to the latest fixed version as soon as possible.

⚠️ Exploitation Details

cve-2026-20079

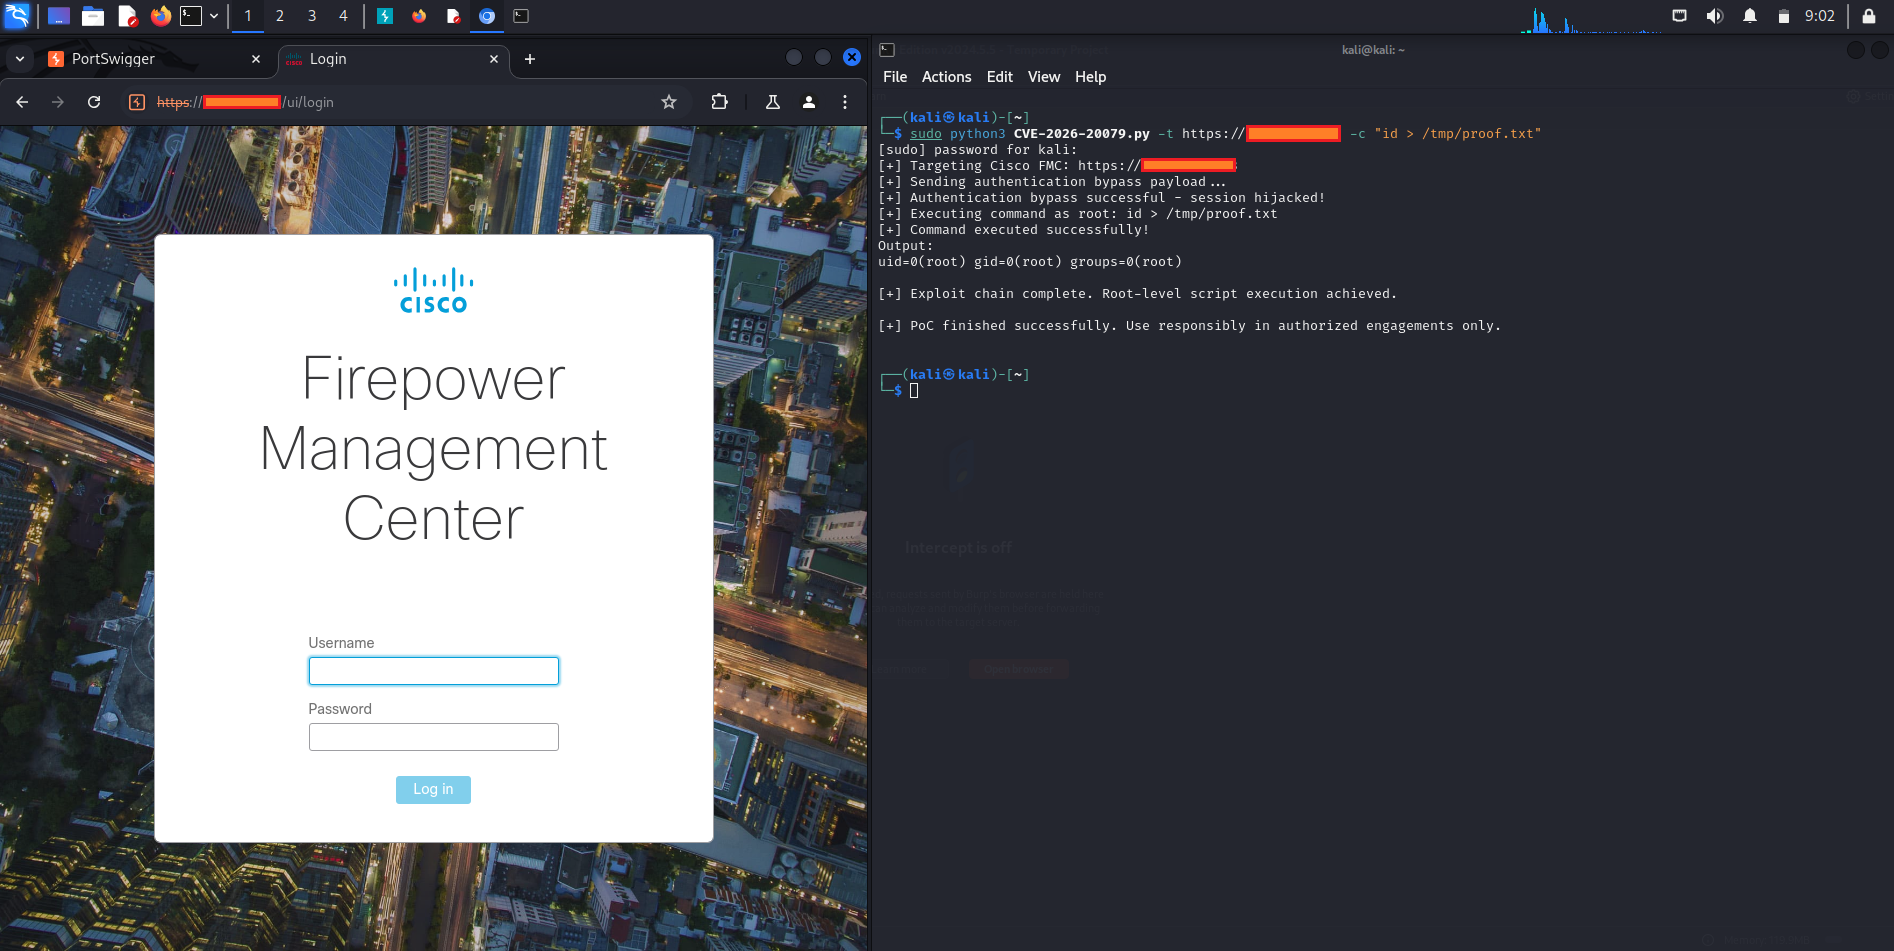
Attackers can exploit this vulnerability by sending specially crafted HTTP requests to the FMC web interface. The flaw stems from a misconfigured boot-time process that creates an alternate authentication path, allowing unauthenticated execution of scripts as root.

Public Proof-of-Concept (PoC) exploits have surfaced shortly after disclosure.


🛡️ Mitigation

  1. Immediate Action: Apply the security patch provided by Cisco.
  2. No official workarounds are available — patching is the only remediation.
  3. Restrict access to the FMC management interface (use firewall rules, VPN, or zero-trust segmentation).
  4. Monitor for suspicious HTTP traffic targeting the FMC web interface.
  5. Use Cisco's Software Checker tool to verify your version.

Official Cisco Security Advisory: https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-onprem-fmc-authbypass-5JPp45V2



📚 References

  • NVD Detail Page
  • Cisco Official Advisory
  • Related Vulnerability: CVE-2026-20131 (Another critical RCE in the same product)

📝 Notes

  • This repository is for documentation, research, and defensive purposes only.
  • Exploitation for malicious intent is illegal and strongly discouraged.
  • Always follow responsible disclosure practices.
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    708
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    500
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    398
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    341
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    259
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →