
CVE-2026-PSA-2026-00043-1
 horkimhab/cve-2026-psa-2026-00043-1
Proof-of-concept exploit for an unauthenticated root authentication bypass in Proxmox VE 7.0-8.0.3, intended for authorized security testing and…
authenticationeducationexploitation+3
horkimhab/cve-2026-psa-2026-00043-1Proof-of-concept exploit for an unauthenticated root authentication bypass in Proxmox VE 7.0-8.0.3, intended for authorized security testing and…
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 synacktiv/captaincredz
CaptainCredz is a modular and discreet password-spraying tool.
 i3umi3iei3ii/centos-control-web-panel-cve
CentOS Control Web Panel, Root Privilege Escalation
 popyue/cve-2025-47812
RCE for WingFTP v4.7.3
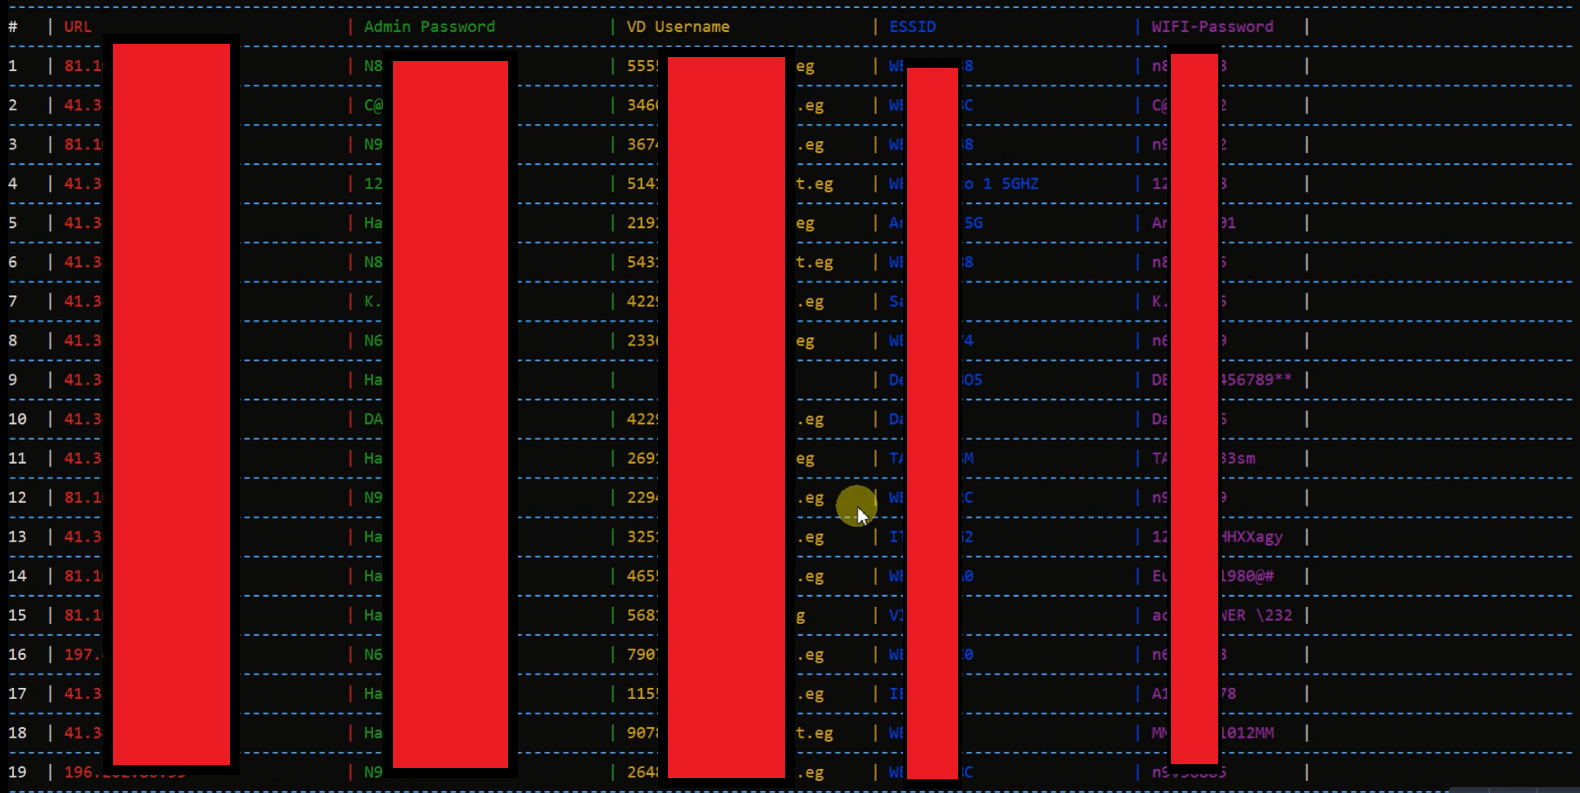 minanagehsalalma/cve-2026-34472-auth-bypass-zte-h188a-router
Technical breakdown of CVE-2026-34472, an auth bypass via leaked credentials affecting ZTE H188A routers.
 zzz66686/cve-2017-14263
Proof-of-concept exploit for CVE-2017-14263 in Honeywell NVR devices. Demonstrates session hijacking and privilege escalation from guest to admin via…
 almounah/silph
Stealthy In-Memory Local Password Harvester (SILPH) tool: dump LSA, SAM and DCC2 with indirect syscall
 benjojo/totp-ssh-fluxer
Take security by obscurity to the next level (this is a bad idea, don't really use this please)
 lkarlslund/ldapnomnom
Quietly and anonymously bruteforce Active Directory usernames at insane speeds from Domain Controllers by (ab)using LDAP Ping requests (cLDAP)
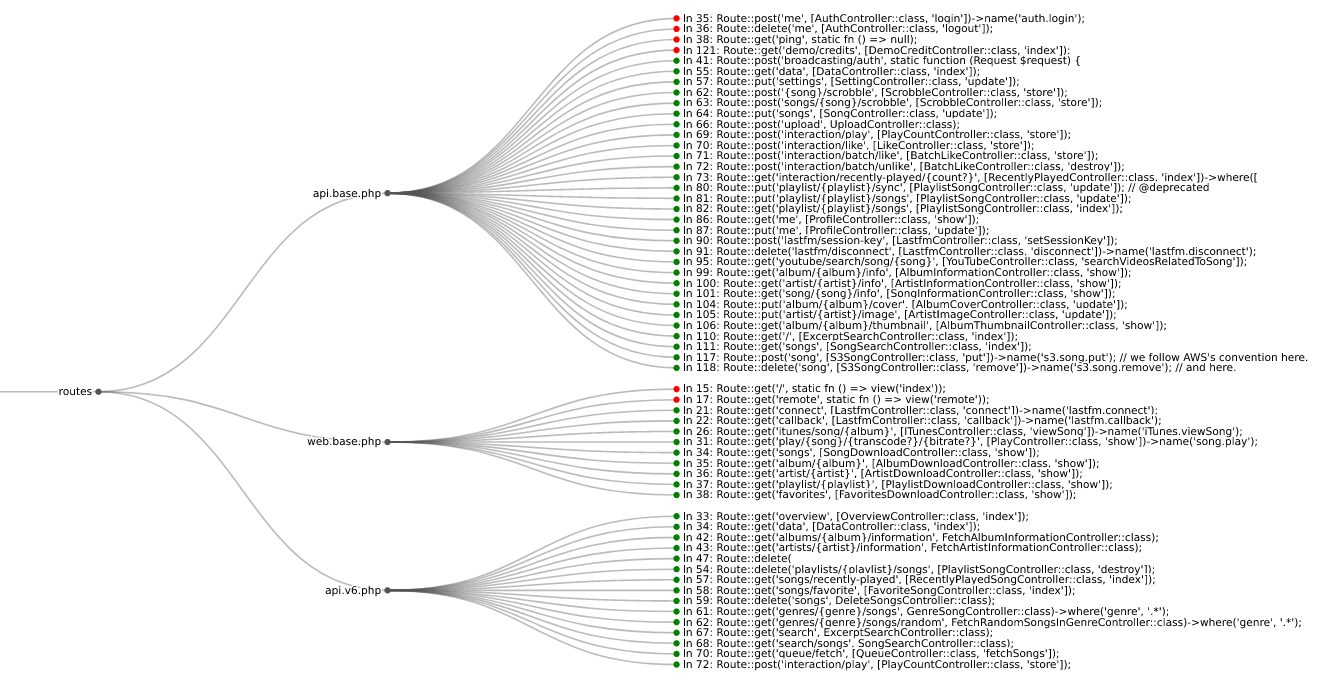 mschwager/route-detect
Find authentication (authn) and authorization (authz) security bugs in web application routes.
 pwnfoo/ntlmrecon
Enumerate information from NTLM authentication enabled web endpoints 🔎