CVE-2026-10288-AUTH-BYPASS

Proof-of-concept exploit for an authentication bypass in Hotel and Tourism Reservation System 1.0, allowing unauthenticated admin access via inverted…

Proof-of-concept exploit for an authentication bypass in Hotel and Tourism Reservation System 1.0, allowing unauthenticated admin access via inverted…

Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…

Security research on Craft CMS authentication mechanism

Validates and exploits VMware ESXi SFCB authentication bypass (CVE-2021-21994) via a probe/fuzz harness, enabling unauthenticated CIM-XML enumeration.

esponsible disclosure write-ups for CVE-2026-8793 - PaperCut NG 25.0.11

RCE for WingFTP v4.7.3

Proof of concept demonstrating unauthenticated access to critical admin functions in Smart Parking System 1.0, allowing account creation, data…

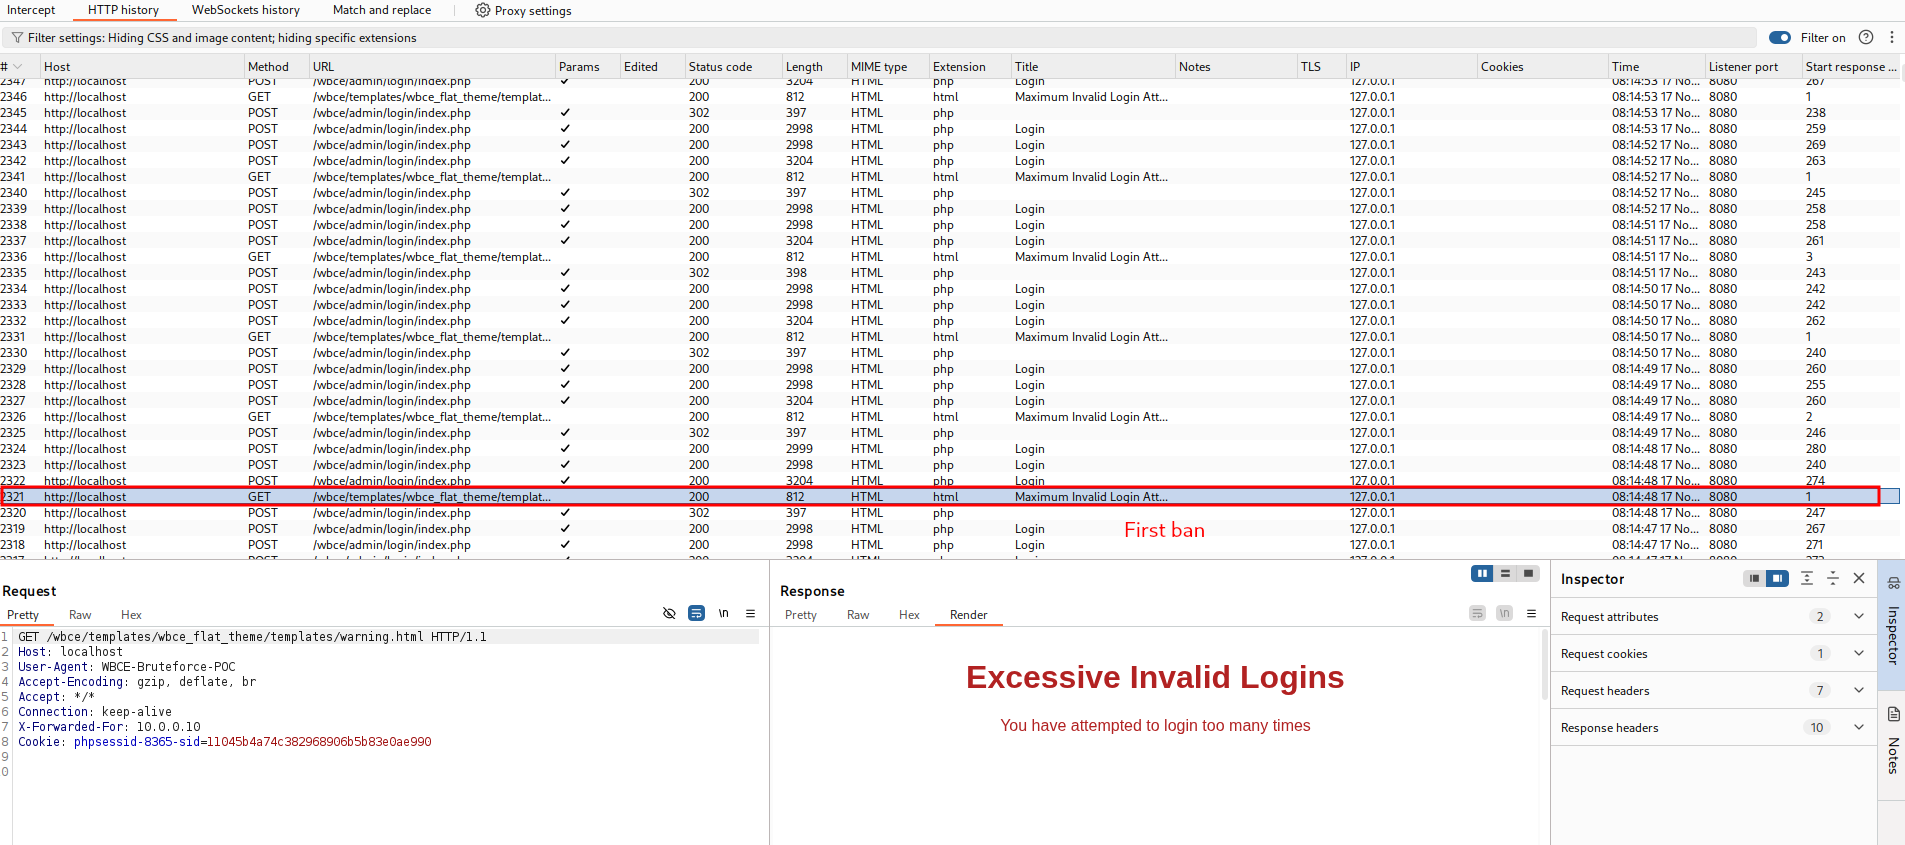
Proof-of-concept for CVE-2025-66204: brute-force protection bypass in WBCE CMS via spoofed X-Forwarded-For header, with automated Python exploit…

Detection and verification tool for CVE-2026-18963, a Keycloak reset-credentials state bypass. Performs version fingerprinting, realm/client/user…

CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)

Username Enumeration via Authentication Timing Side-Channel in PaperCut NG

Technical analysis and PoC of CVE-2026-52824: default APP_SECRET in the Kimai Docker image enabling unauthenticated login link forgery. Affects <=…