

TATS
 icemoonhsv/tats
Analyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
authenticationidentity-access-managementlog-analysis+2
icemoonhsv/tatsAnalyze and track OAuth 2.0, OIDC, and Microsoft Entra ID tokens from Burp, mitmproxy, or Chrome DevTools captures. Visualize token lifecycles,…
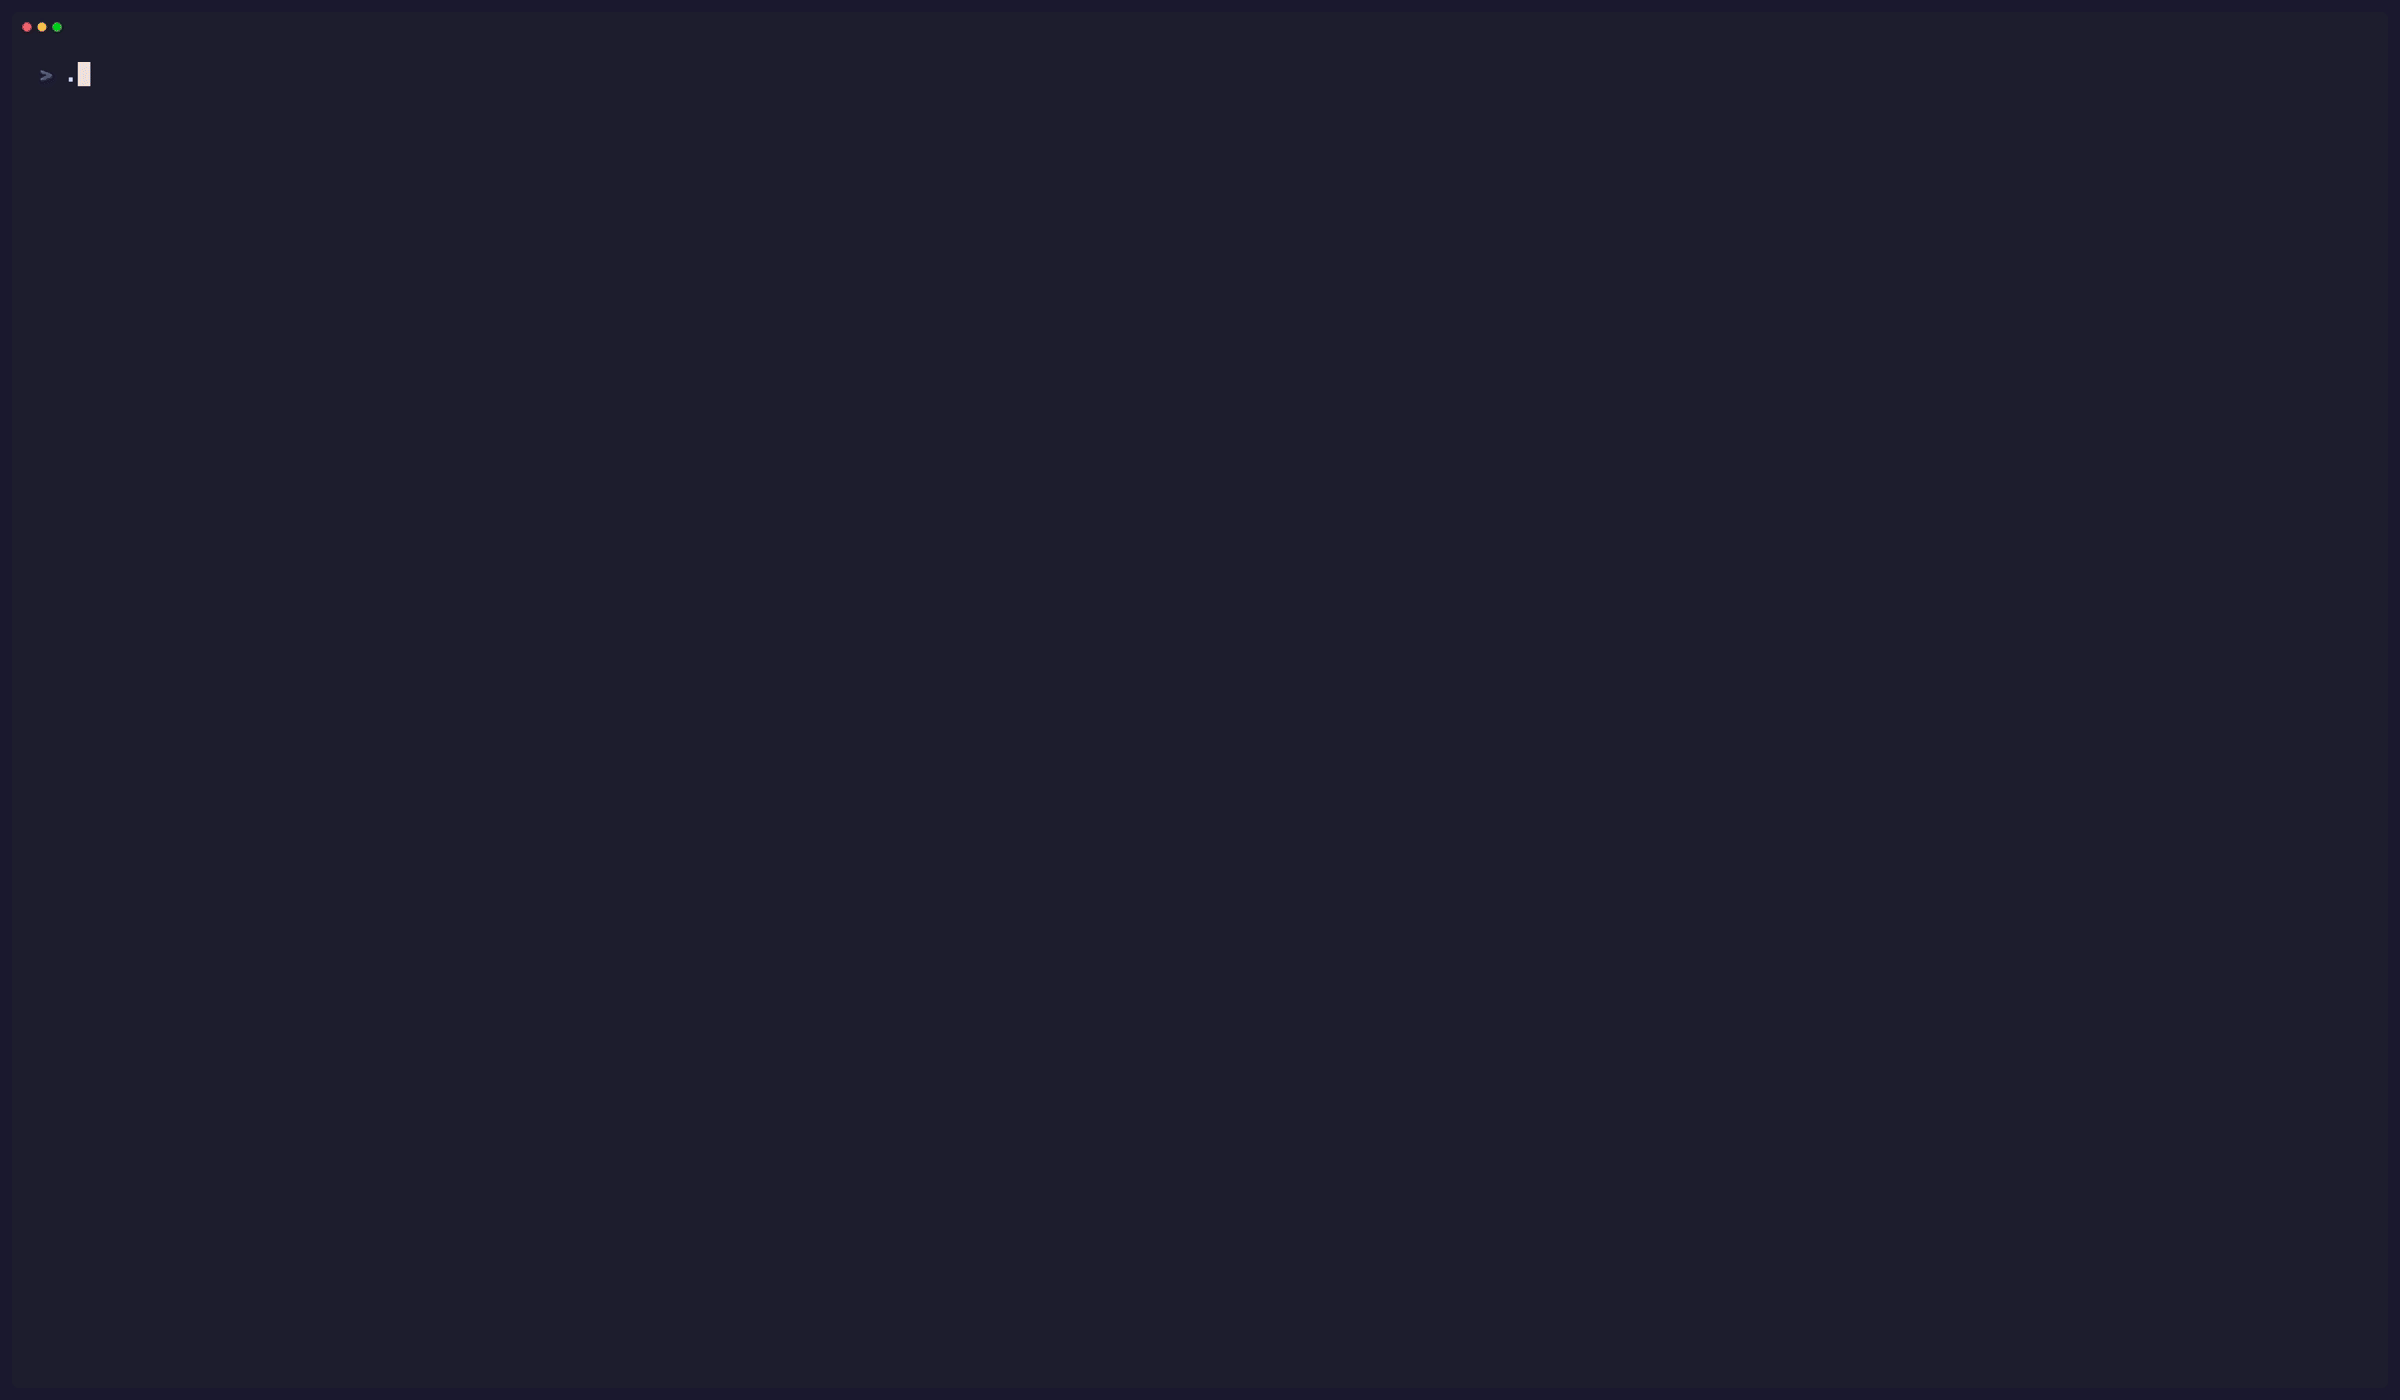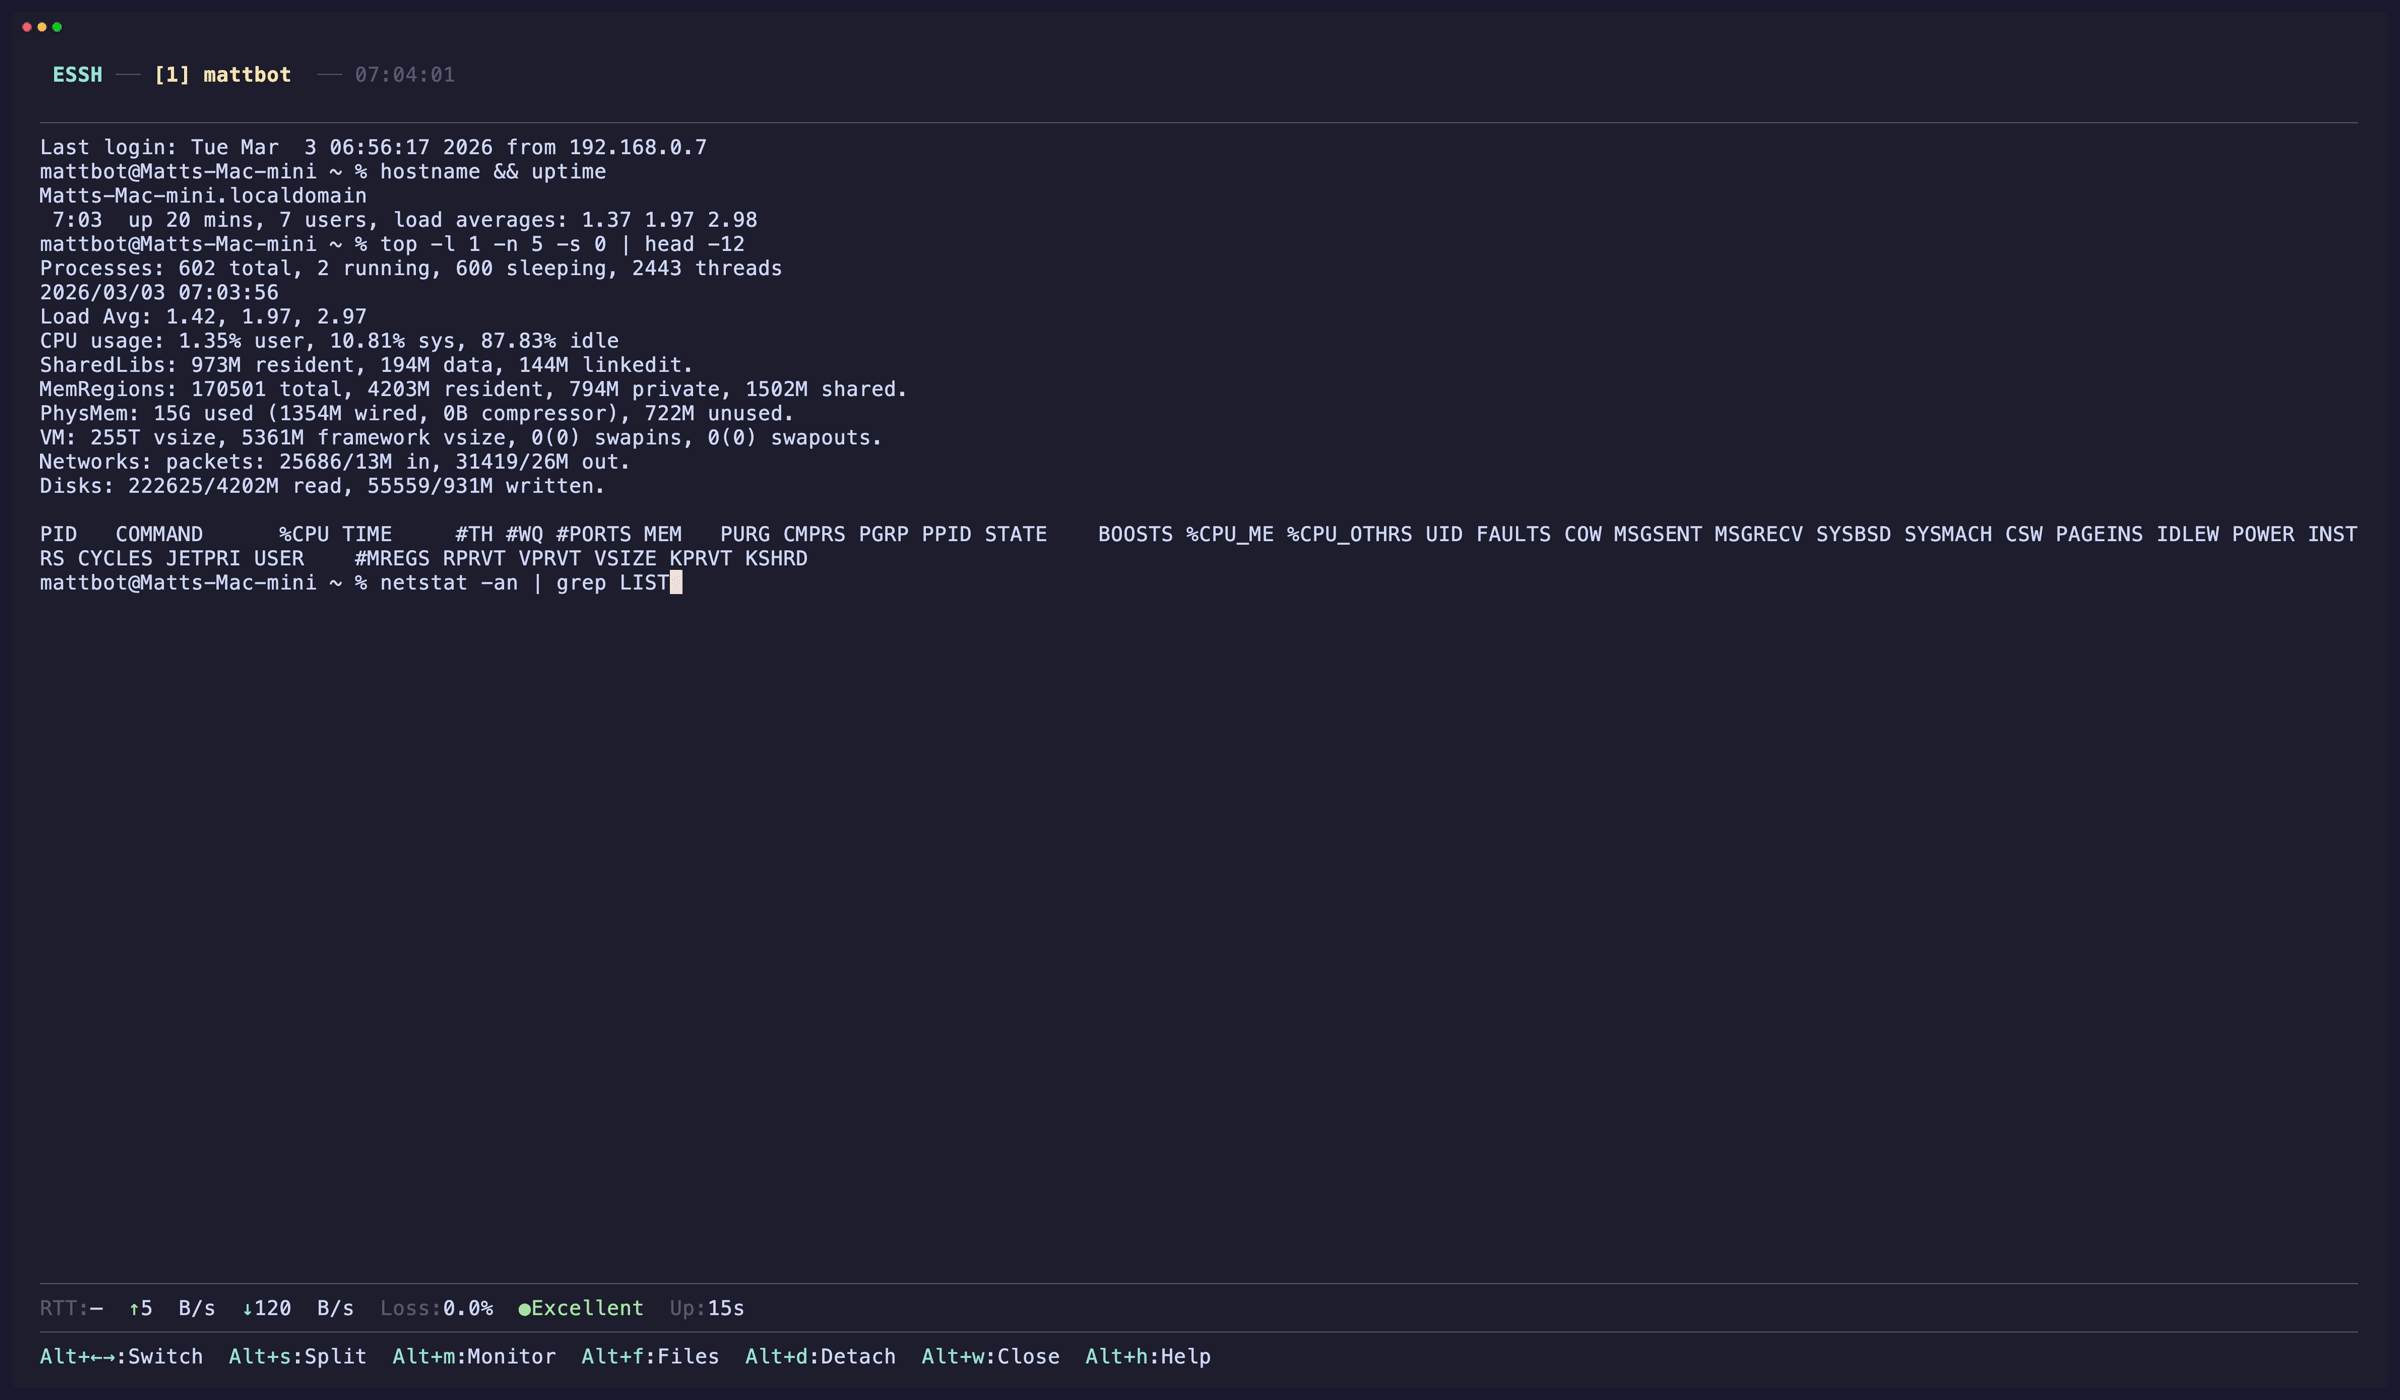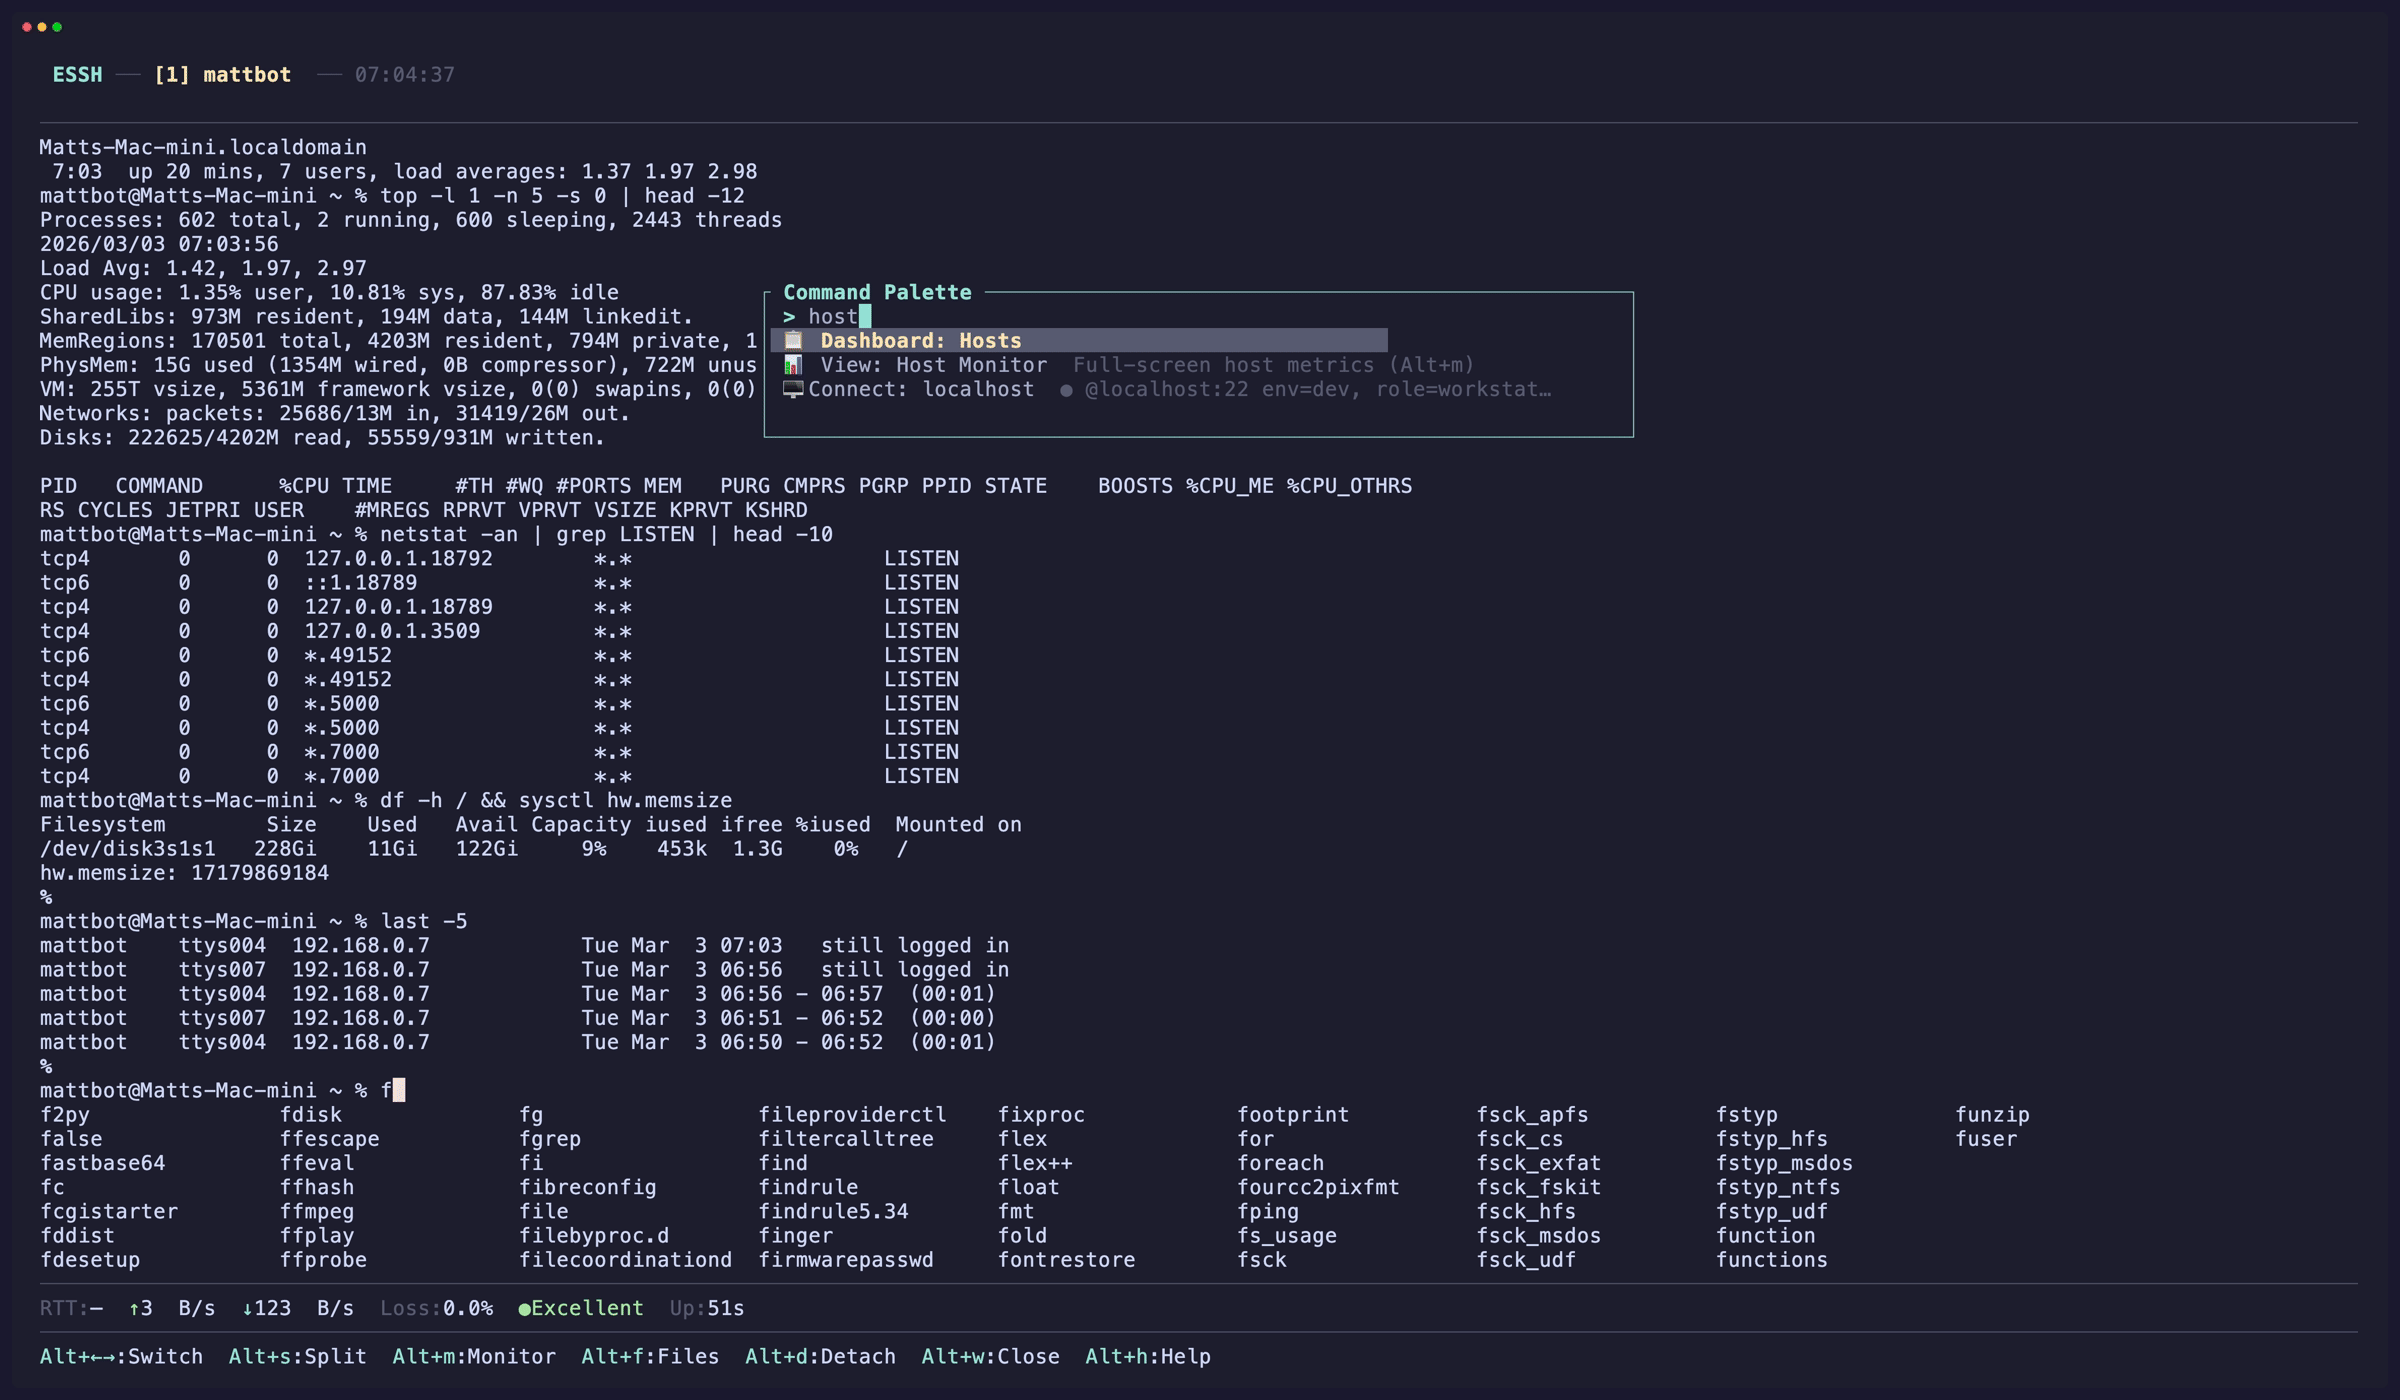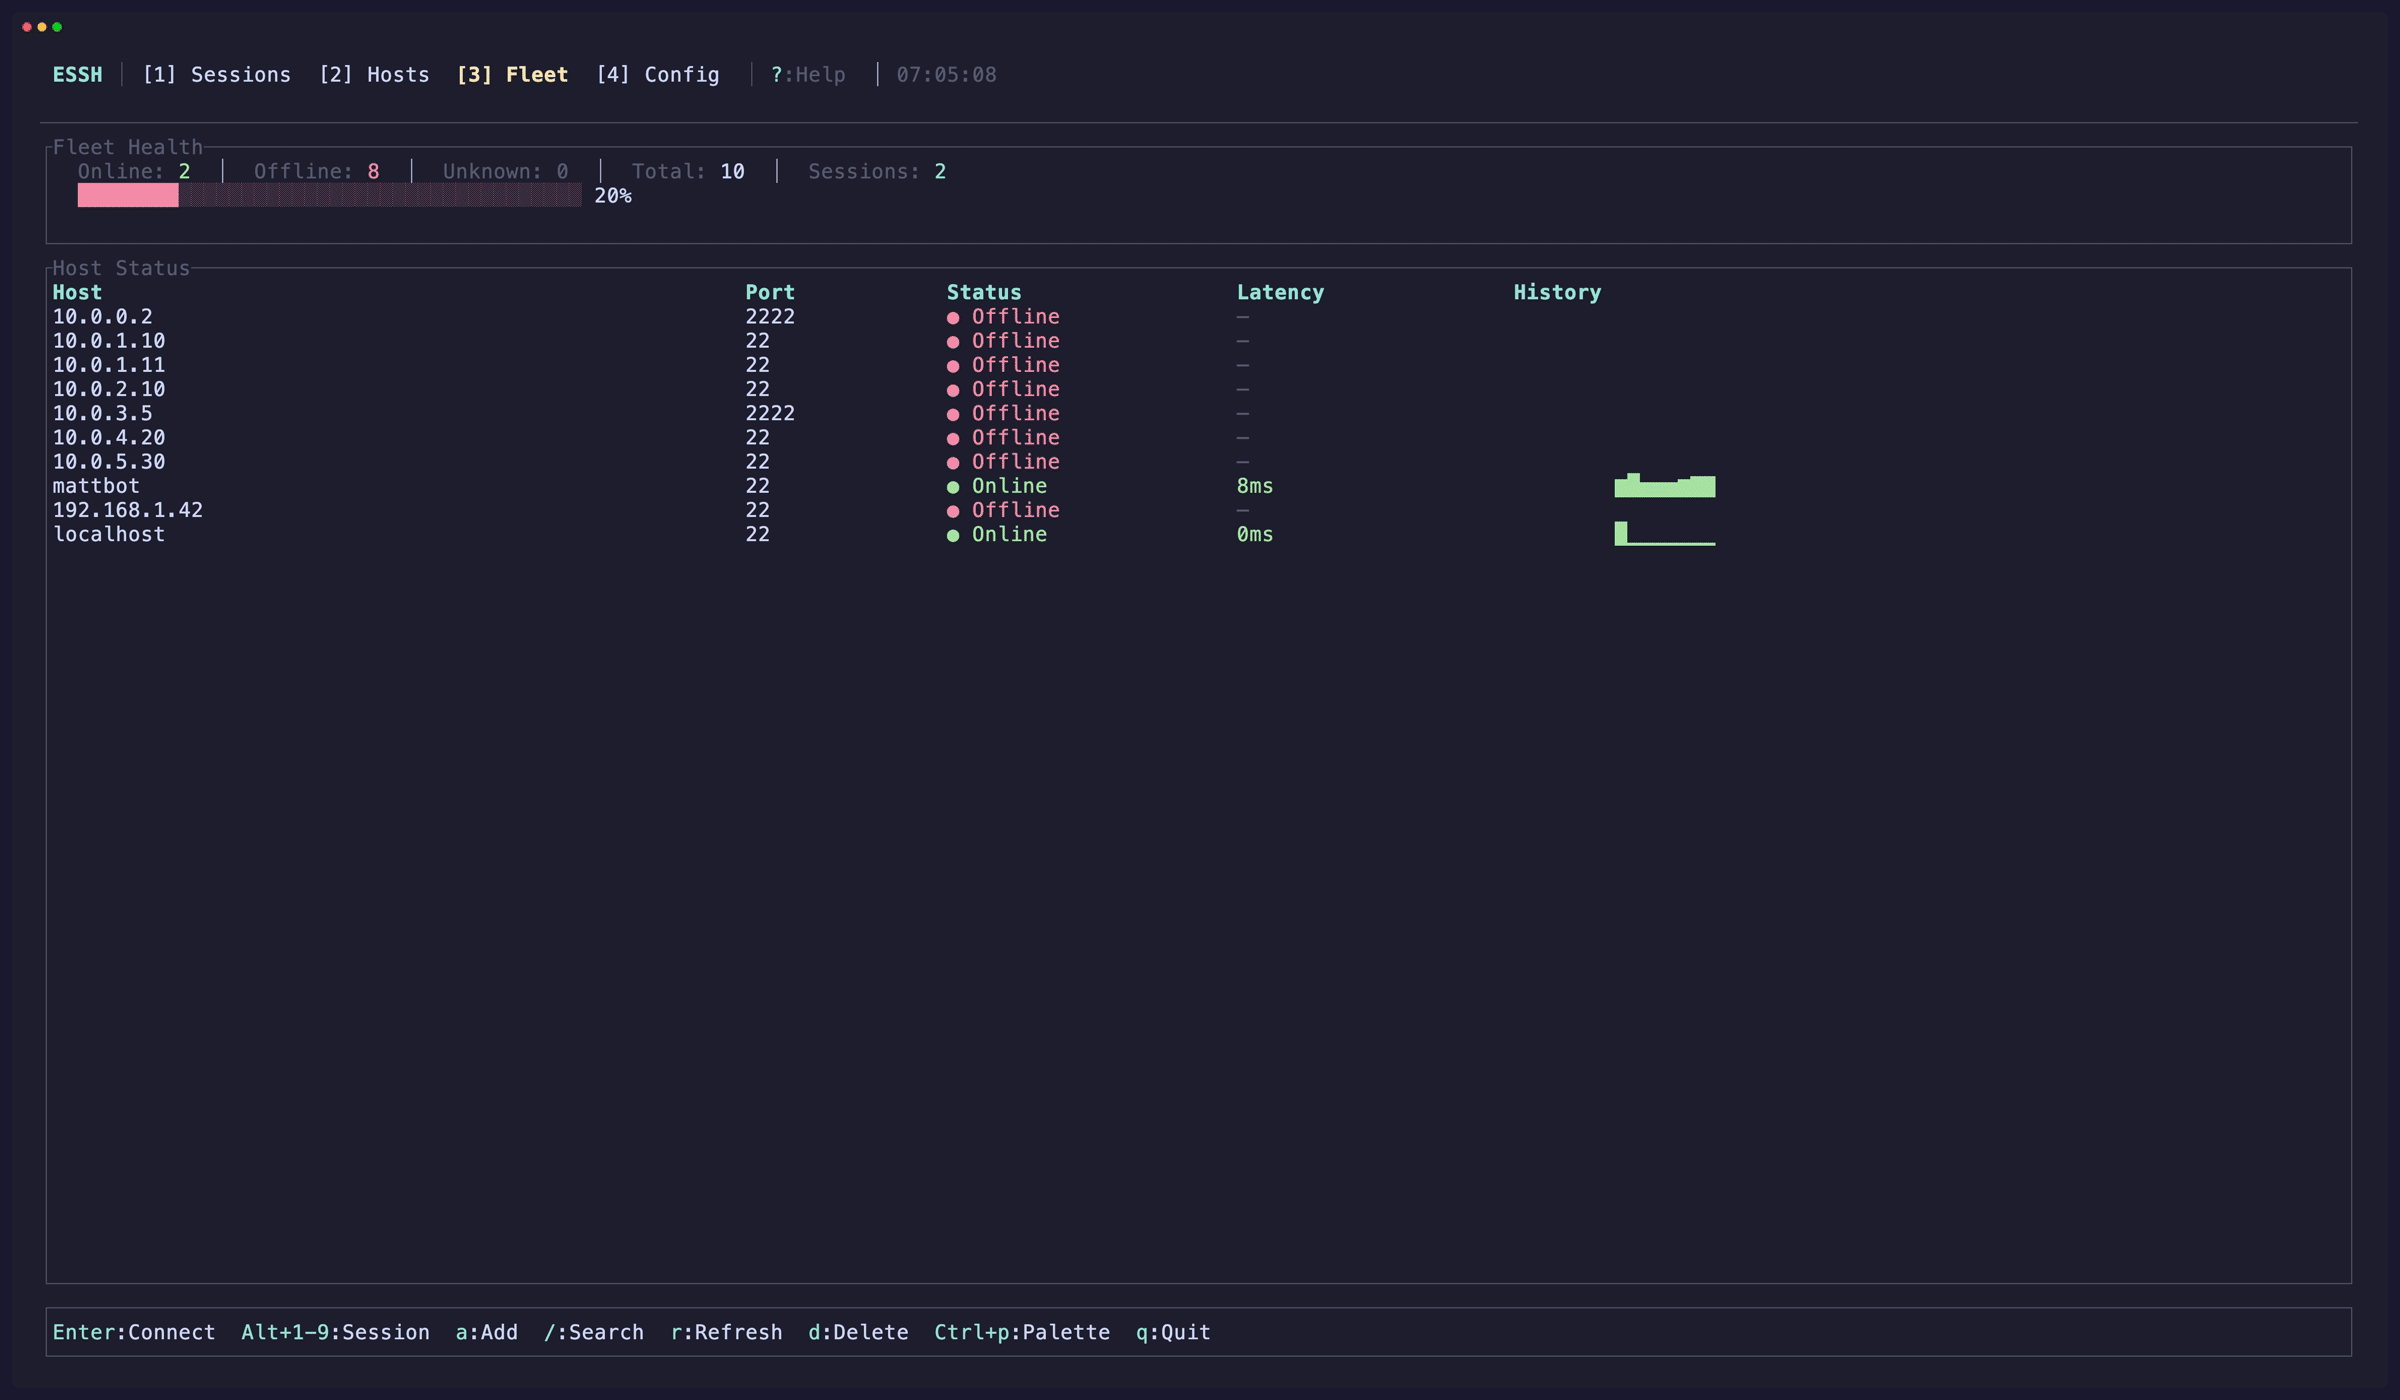 matthart1983/essh
Enhanced SSH client with TUI — manage connections, keys, and sessions
 dropbox/securitybot
Distributed alerting for the masses!
 zenzue/cve-2025-50154
PowerShell toolkit to audit, harden, and hunt for insecure NTLM/SMB usage, addressing CVE-2025-50154 credential leak risks with event log analysis…
 andrei-dr/cpanel-cve-2026-41940-ioc
CVE-2026-41940 cPanel/WHM auth bypass IOC scanner — fixes false positives in upstream detection script, adds log cross-correlation
 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
 cyberark/ketshash
A little tool for detecting suspicious privileged NTLM connections, in particular Pass-The-Hash attack, based on event viewer logs.
 target/strelka-ui
Strelka Web UI for File Submission and Analysis
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
 skraft9/cve-2025-44823
Authenticated API Key Exposure in Nagios Log Server 2024R1.3.1
 kn6869610/cve-2018-10933
Leveraging it is a simple matter of presenting the server with the SSH2_MSG_USERAUTH_SUCCESS message, which shows that the login already occurred…
 cy3erdr4g0n/cve-2024-10924
Exploit for CVE-2024-10924, a critical authentication bypass in WordPress Really Simple Security plugin (versions 9.0.0-9.1.1.1). Allows…