

CVE-2023-7028
 yoryio/cve-2023-7028
Exploit for CVE-2023-7028 - GitLab CE/EE
authenticationexploitationlabs-practice+3
yoryio/cve-2023-7028Exploit for CVE-2023-7028 - GitLab CE/EE

 kit-lang/packages/kit-oauth
OAuth 2.0 client library for Kit applications supporting authorization code, PKCE, client credentials, and refresh token flows with built-in provider…
 ipsbruno/cve-2022-1162
Exploit tool for CVE-2022-1162 that enumerates GitLab users and performs authentication bypass via a crafted login request.
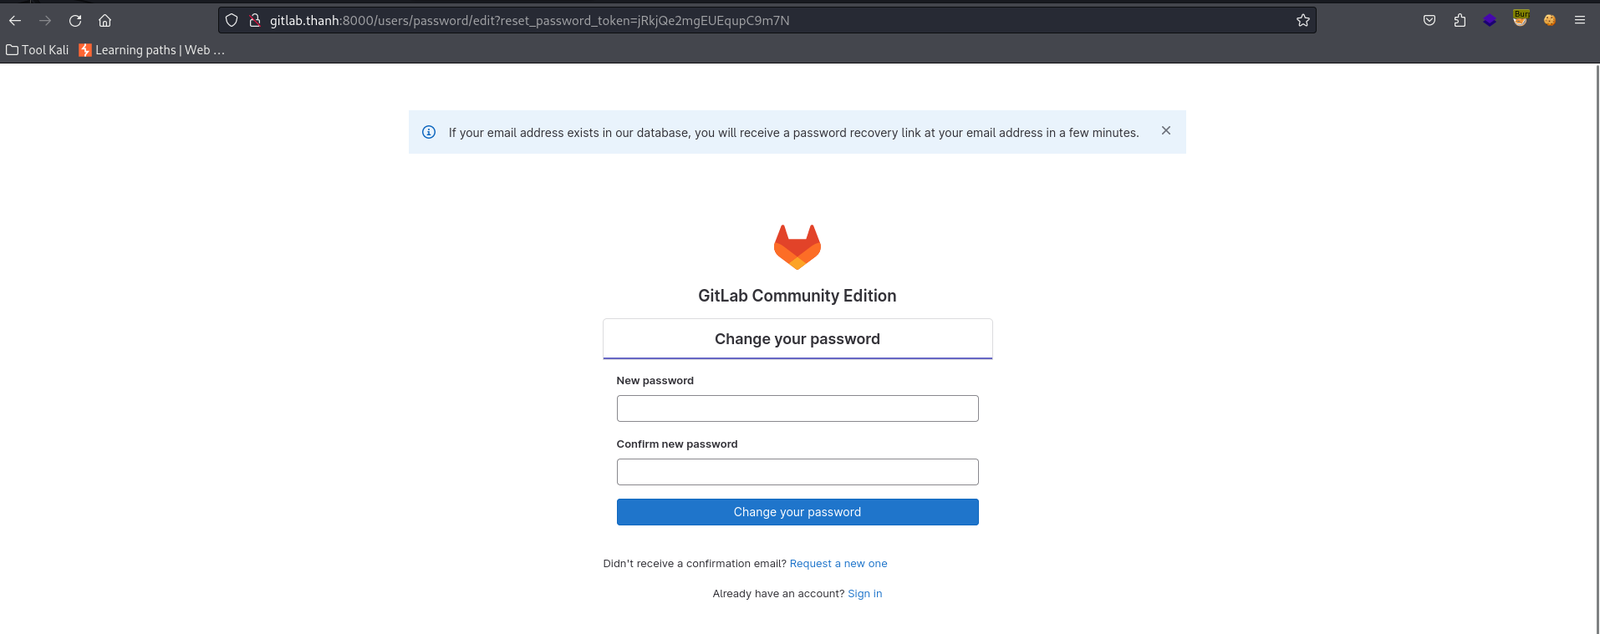 thanhlam-attt/cve-2023-7028
Exploit for GitLab account takeover via CVE-2023-7028, demonstrating password reset bypass by injecting attacker email to receive reset token.
 greenwolf/cve-2022-1162
Exploit for CVE-2022-1162: hardcoded password bypass in GitLab CE/EE OmniAuth accounts, enabling unauthorized login with a known credential.
 hackeremmen/gitlab-exploit
Exploit for GitLab CVE-2023-7028: password reset bypass via dual email verification, allowing unauthorized account takeover. Includes affected…