

CheatSheetSeries
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
api-securityauthenticationcloud-security+6
33.2k
owasp/cheatsheetseriesThe OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
 flaviupopescu/cve-2022-28601
A Two-Factor Authentication (2FA) bypass vulnerability in "Simple 2FA Plugin for Moodle" by LMS Doctor
 inflixim4be/cve-2020-15367
Exploit for CVE-2020-15367: brute-force authentication attack against Venki Supravizio BPM 10.1.2 login page, leveraging user enumeration to gain…
 menevarad007/cve-2026-37749
Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
 xmyronn/cve-2026-10288-auth-bypass
Proof-of-concept exploit for an authentication bypass in Hotel and Tourism Reservation System 1.0, allowing unauthenticated admin access via inverted…
 enochgitgamefied/nextjs-cve-2025-29927
Intentionally vulnerable Next.js application demonstrating CVE-2025-29927 authentication bypass via middleware WAF evasion. Designed for security…
 debajyoti0-0/cve-2026-60206
Technical analysis and Proof-of-Concept for CVE-2026-60206, a critical Oracle WebLogic Server SAML authentication bypass vulnerability.
 helloandrewpaul/session-fixation-in-vvveb-cms-v1.0.6.1
CVE-2025-8517 proof-of-concept demonstrating session fixation in Vvveb CMS v1.0.6.1, enabling full administrative account takeover via arbitrary…
 l0ggg/cve-2026-55040
Exploit code for CVE-2026-55040, it can create auth header for any validate account.
 imthenachoman/how-to-secure-a-linux-server
Step-by-step guide for hardening a Linux server, covering SSH security, firewalls, intrusion detection, auditing, and system configuration to reduce…
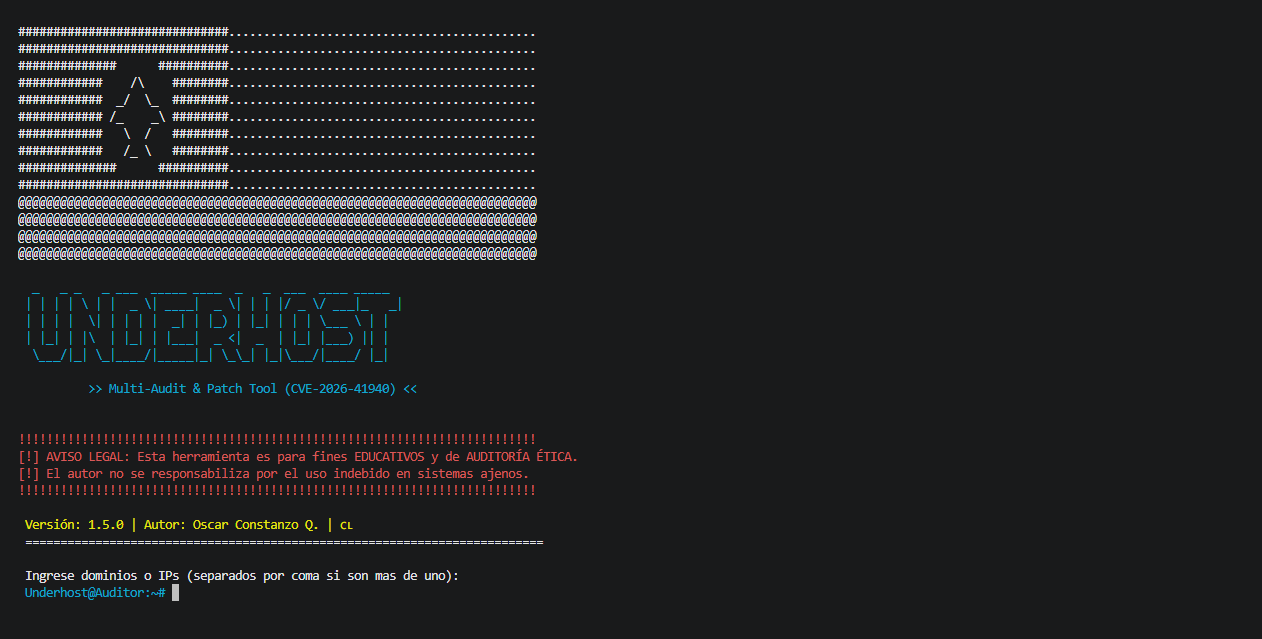 underh0st/cpanel-audit-remediation-tool
Audit and incident response tool for CVE-2026-41940 vulnerability
 blackhatexploitation/exploit-for-cve-2026-18963
Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…
 asterisk/asterisk
The official Asterisk Project repository.
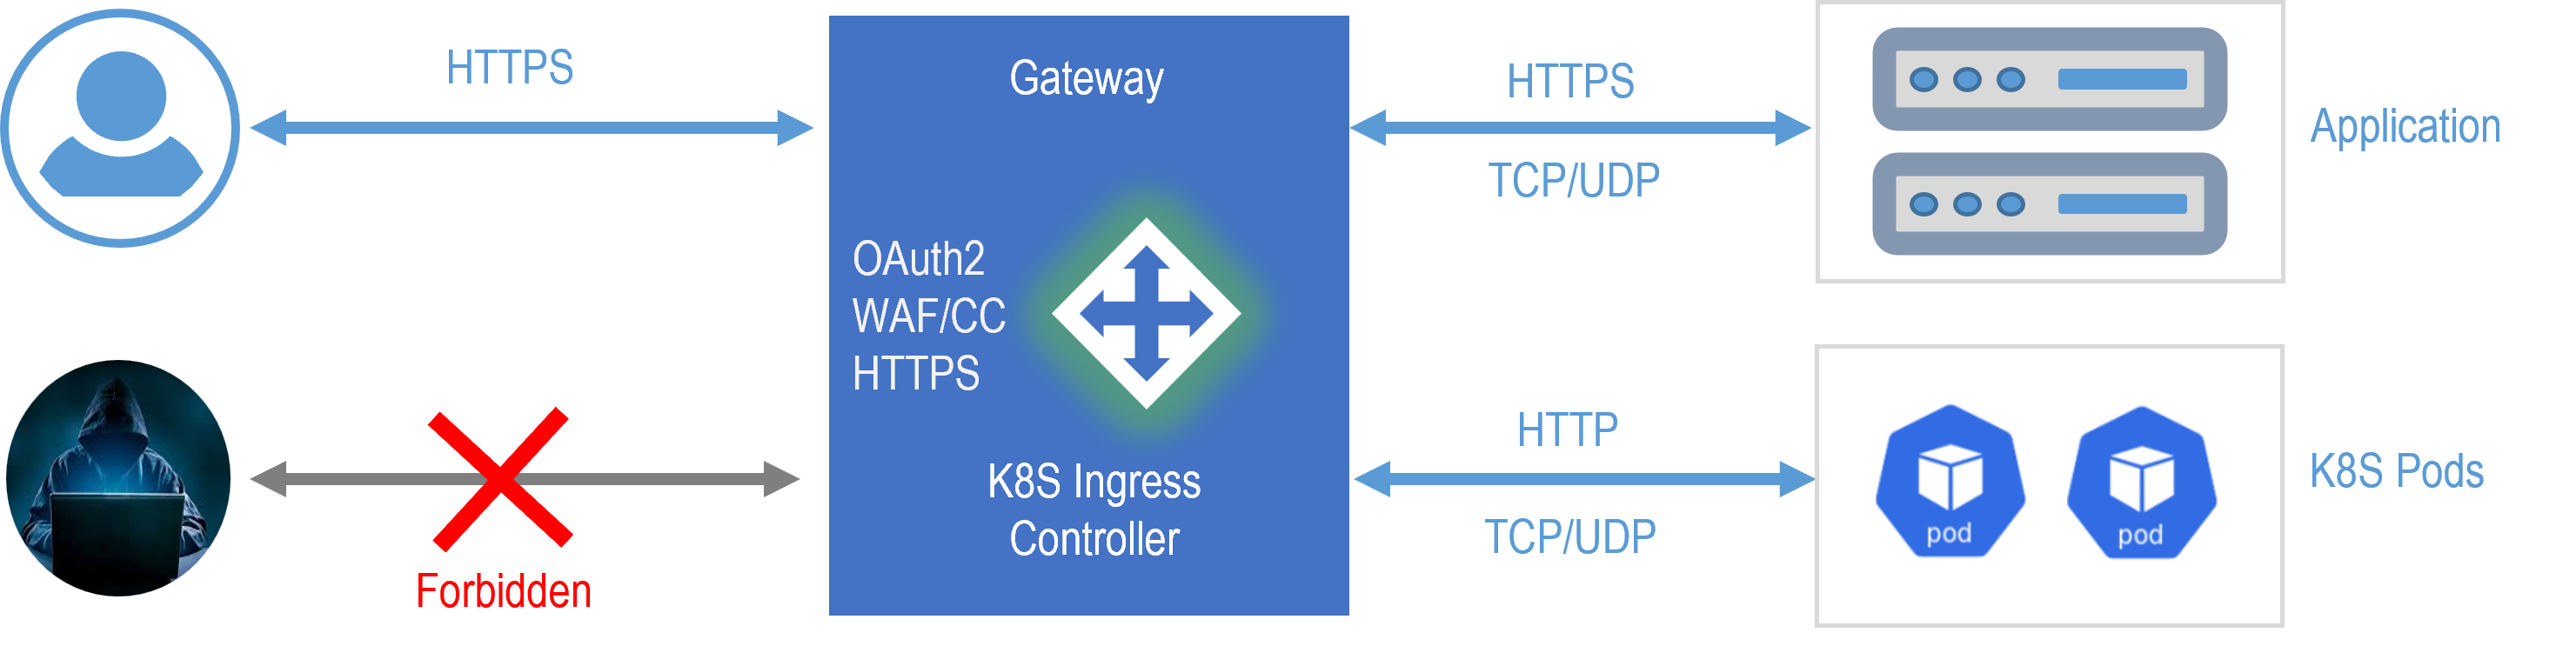 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
 rbih-boulanouar/cve-2024-4040
Proof-of-concept exploit for CVE-2024-4040, a server-side template injection in CrushFTP allowing unauthenticated file read, authentication bypass,…
 polosss/by-poloss..-..cve-2026-15038-poc
POC 4 CVE-2026-15038