
Modlishka
 drk1wi/modlishka
Modlishka. Reverse Proxy.
authenticationimpersonation-toolspenetration-testing+6
drk1wi/modlishkaModlishka. Reverse Proxy.
 lgandx/responder
Responder is a LLMNR, NBT-NS and MDNS poisoner, with built-in HTTP/SMB/MSSQL/FTP/LDAP rogue authentication server supporting NTLMv1/NTLMv2/LMv2,…
 61106960/adpeas
Powershell tool to automate Active Directory enumeration.
 secdev02/easytokens
Kali365 - EvilTokens Replica
 boydhacks/ntlmscout
Unauthenticated NTLM endpoint reconnaissance tool that decodes Type-2 challenges across HTTP, SMB, MSSQL, SMTP, IMAP, POP3, NNTP, LDAP, and RDP to…
 ghostpack/rubeus
Trying to tame the three-headed dog.
 kgretzky/evilginx
PLEASE USE NEW VERSION: https://github.com/kgretzky/evilginx2
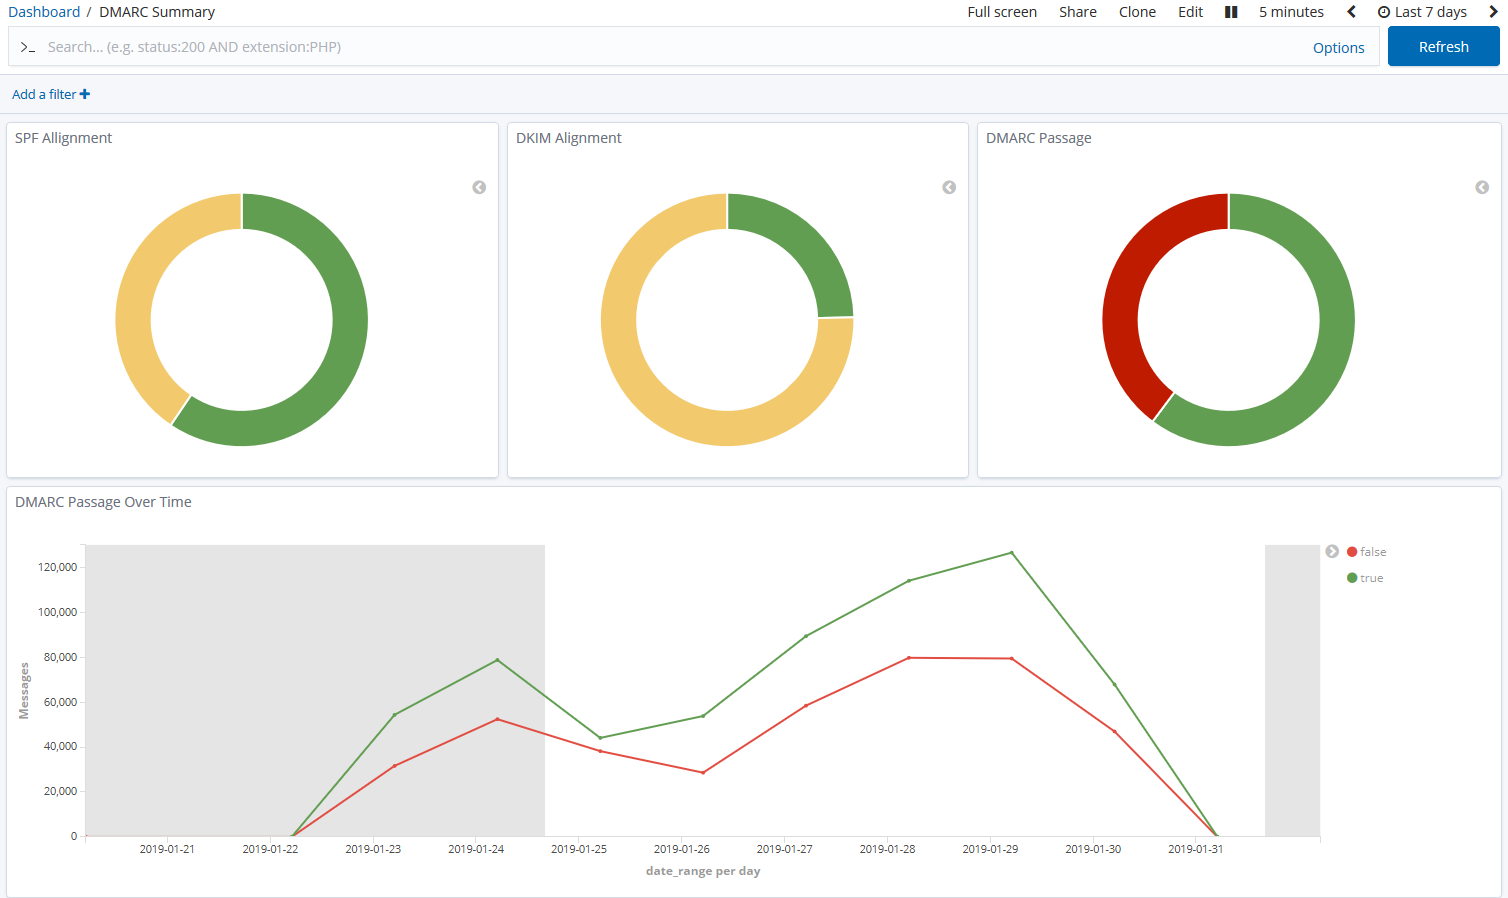 domainaware/parsedmarc
A Python package and CLI for parsing aggregate and forensic DMARC reports
 x011/smtp-tunnel-proxy
A high-speed covert tunnel that disguises TCP traffic as SMTP email communication to bypass Deep Packet Inspection (DPI) firewalls.
 lkarlslund/ldapnomnom
Quietly and anonymously bruteforce Active Directory usernames at insane speeds from Domain Controllers by (ab)using LDAP Ping requests (cLDAP)
 trustedsec/ridenum
Rid_enum is a null session RID cycle attack for brute forcing domain controllers.
 lissy93/awesome-privacy
🦄 A curated list of privacy & security-focused software and services
 ropnop/kerbrute
A tool to perform Kerberos pre-auth bruteforcing
 dafthack/msolspray
A password spraying tool for Microsoft Online accounts (Azure/O365). The script logs if a user cred is valid, if MFA is enabled on the account, if a…
 v-jfanca/cve-2026-20833-rc4-kerberos
Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)
 cube0x0/sharpmapexec
Windows-native penetration testing swiss army knife for lateral movement, credential access, data exfiltration, and vulnerability scanning across…
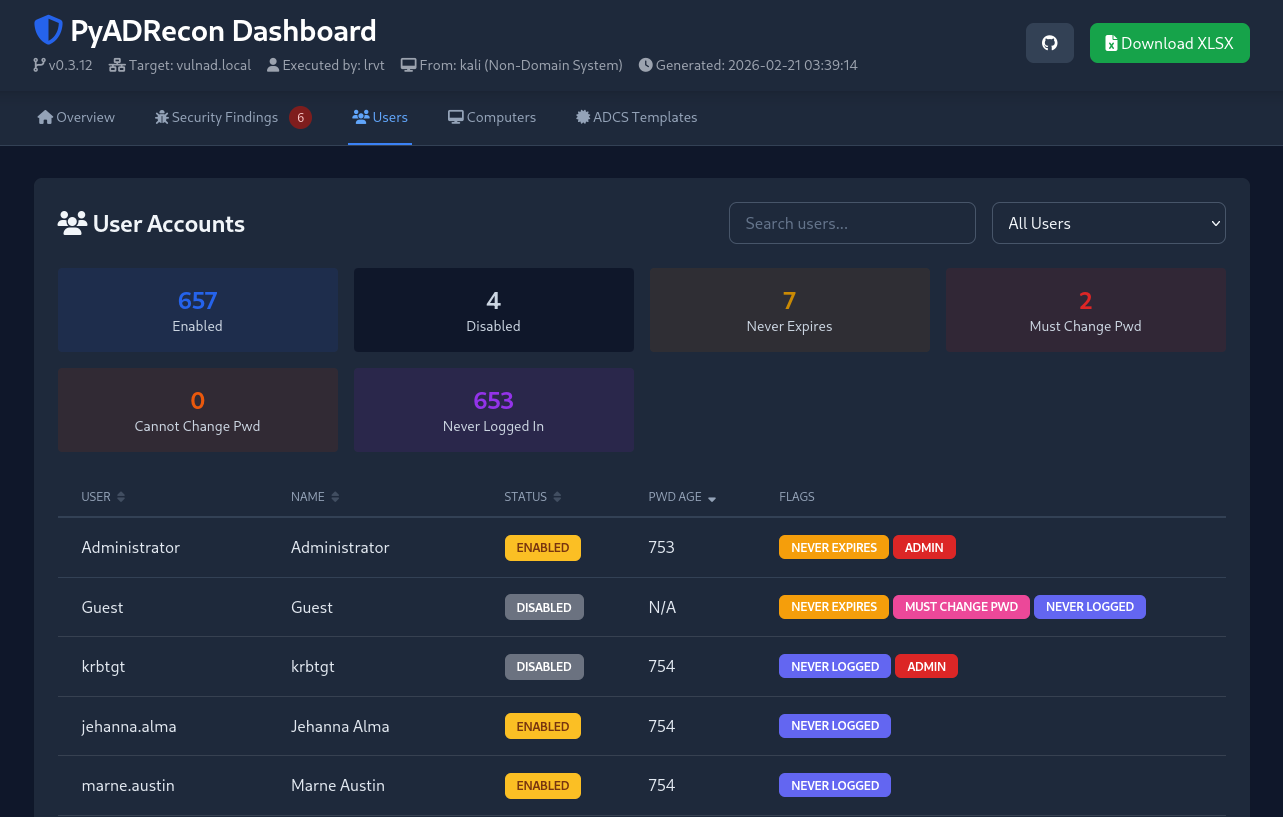 l4rm4nd/pyadrecon
Python3 implementation of ADRecon with support for NTLM and Kerberos authentication querying LDAP. Generates individual CSV files and a single XSLX +…
 jenderal92/cve-2026-41940
Bulk scanner and mass exploitation tool for CVE-2026-41940 on cPanel/WHM, built for automated target validation and high-speed multi-threaded…