
cve-2024-55591-poc
 ull0a/cve-2024-55591-poc
Educational implementation in Go for CVE-2024-55591 (Fortinet FortiOS Authentication Bypass). Designed for security research, vulnerability…
authenticationexploitationpenetration-testing+2
1
ull0a/cve-2024-55591-pocEducational implementation in Go for CVE-2024-55591 (Fortinet FortiOS Authentication Bypass). Designed for security research, vulnerability…
 g-u-i-d/cve-2024-10449-patch
Patch for CVE-2024-10449: replaces vulnerable loginAction.php with a hardened version that requires database configuration for secure authentication.
 d-raco/cve-2024-31964
Proof-of-concept exploit for CVE-2024-31964, a temporary authentication bypass in Mitel 6900w Series SIP phones allowing unauthenticated POST…
 castro-ian/cve-2024-4573-mitigation-script
Detects NTLM authentication status by checking LmCompatibilityLevel registry value to assess exposure to CVE-2024-43451 and mitigate credential relay…
 chandrimanath04-hue/cve-2024-31218-webhood-lab
Docker-based lab reproducing CVE-2024-31218, an unauthenticated PocketBase admin creation flaw in Webhood, with PoC, detection, and remediation…
 joshuavanderpoll/cve-2024-56348
Go-based exploit for CVE-2024-56348 targeting JetBrains TeamCity authentication bypass and remote code execution. Provides interactive shell, reverse…
 harydhk7/cve-2024-4358
Pre-authenticated remote code execution exploit for Telerik Report Server (CVE-2024-4358/CVE-2024-1800) with authentication bypass and…
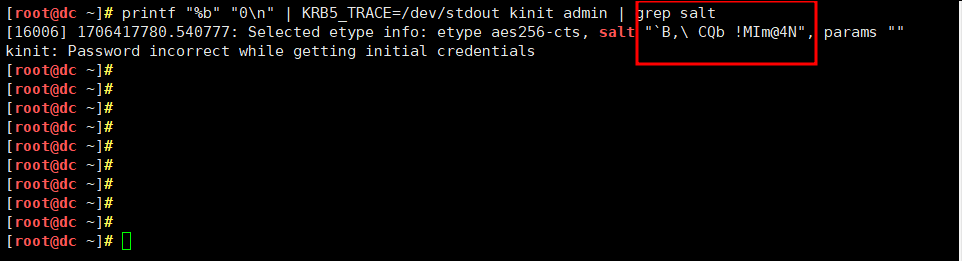 im10n/cve-2024-3183-poc
POC for CVE-2024-3183 (FreeIPA Rosting)
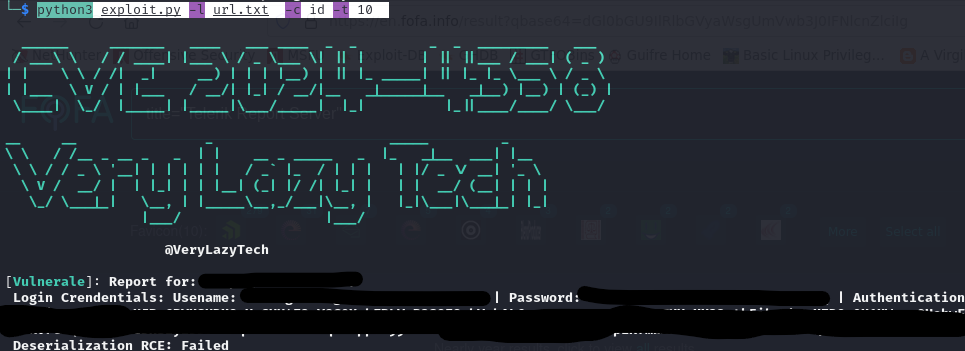 verylazytech/cve-2024-4358
Authentication Bypass Vulnerability — CVE-2024–4358 — Telerik Report Server 2024
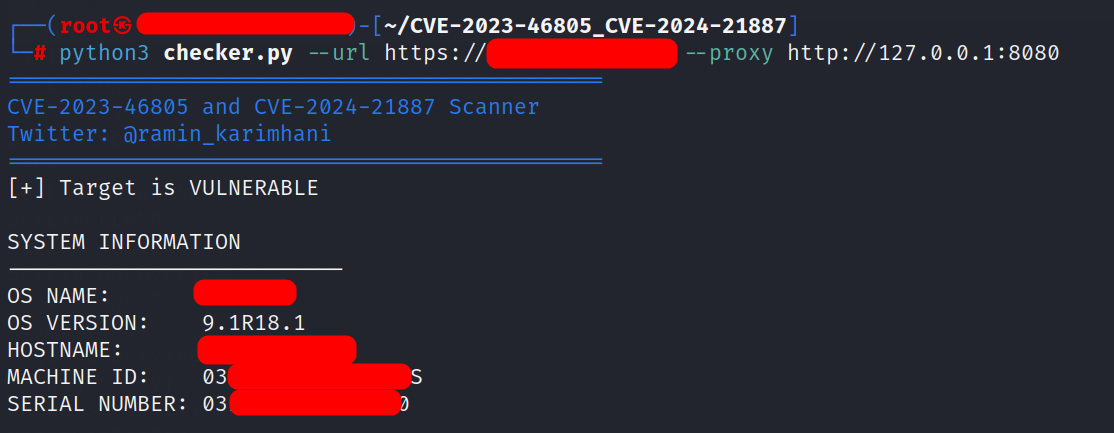 raminkarimkhani1996/cve-2023-46805_cve-2024-21887
The script in this repository only checks whether the vulnerabilities specified in the Ivanti Connect Secure product exist.
 0xjessie21/cve-2024-0012
CVE-2024-0012 PAN-OS: Authentication Bypass in the Management Web Interface (PAN-SA-2024-0015) RCE POC
 redteampentesting/watchguard-sso-client
Client Implementation for the WatchGuard SSO Agent Protocol used for Security Research (CVE-2024-6592, CVE-2024-6593, CVE-2024-6594)
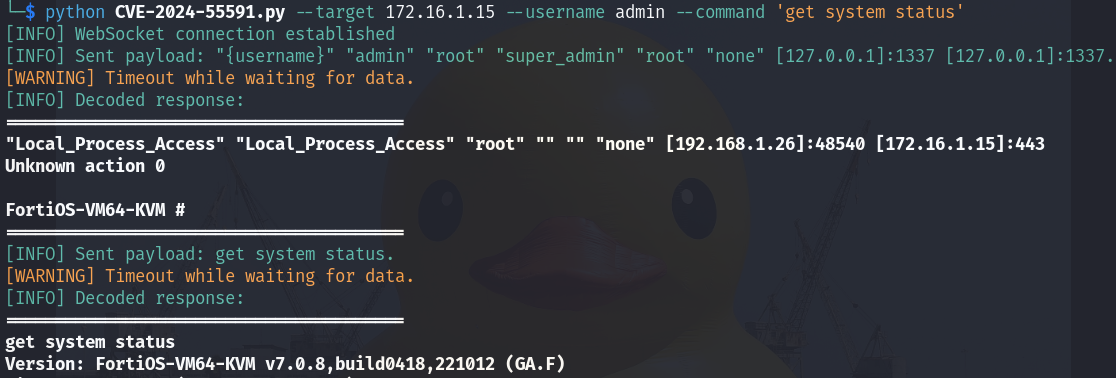 virus-or-not/cve-2024-55591
An Authentication Bypass Using an Alternate Path or Channel vulnerability [CWE-288] affecting FortiOS and FortiProxy may allow a remote attacker to…
 gpotter2/cve-2024-20674
Exploit for CVE-2024-20674: Kerberos mutual authentication bypass via logic bug in client-side U2U TGT-REP handling. Enables unauthenticated network…
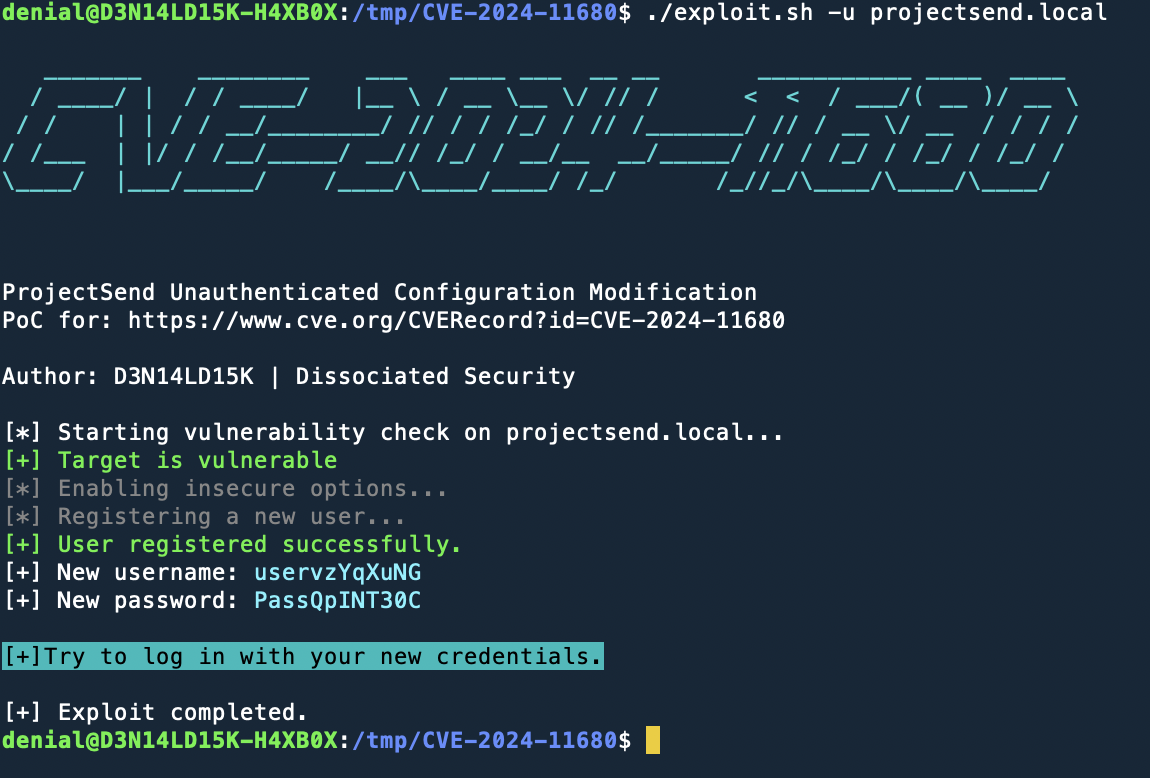 d3n14ld15k/cve-2024-11680_poc_exploit
This repository contains a Proof of Concept (PoC) exploit for CVE-2024-11680, a critical vulnerability in ProjectSend r1605 and older versions. The…
 geniuszly/gencrushsstiexploit
is a PoC for CVE-2024-4040 tool for exploiting the SSTI vulnerability in CrushFTP
 umchacker/cve-2024-55591-poc
Proof-of-concept exploit for CVE-2024-55591, enabling unauthenticated WebSocket CLI access to FortiOS devices, with interactive shell and admin…
 horizon3ai/cve-2024-28987
Proof-of-concept exploit for CVE-2024-28987 targeting SolarWinds Web Help Desk hardcoded credential vulnerability. Automates exploitation via URL…