
CVE-2022-26923
 yowise/cve-2022-26923
Detailed technical write-up and proof-of-concept for CVE-2022-26923, an Active Directory Certificate Services privilege escalation vulnerability,…
authenticationeducationencryption-decryption-tools+3
yowise/cve-2022-26923Detailed technical write-up and proof-of-concept for CVE-2022-26923, an Active Directory Certificate Services privilege escalation vulnerability,…
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
 dante01yoon/cve-2025-29927
Demonstration of CVE-2025-29927: Next.js middleware authentication bypass via x-middleware-subrequest header spoofing. Includes vulnerable and fixed…
 karaaslanlabs/kl-security-key
Experimental RP2040 FIDO2/WebAuthn authenticator with packed attestation and documented Windows/Entra interoperability
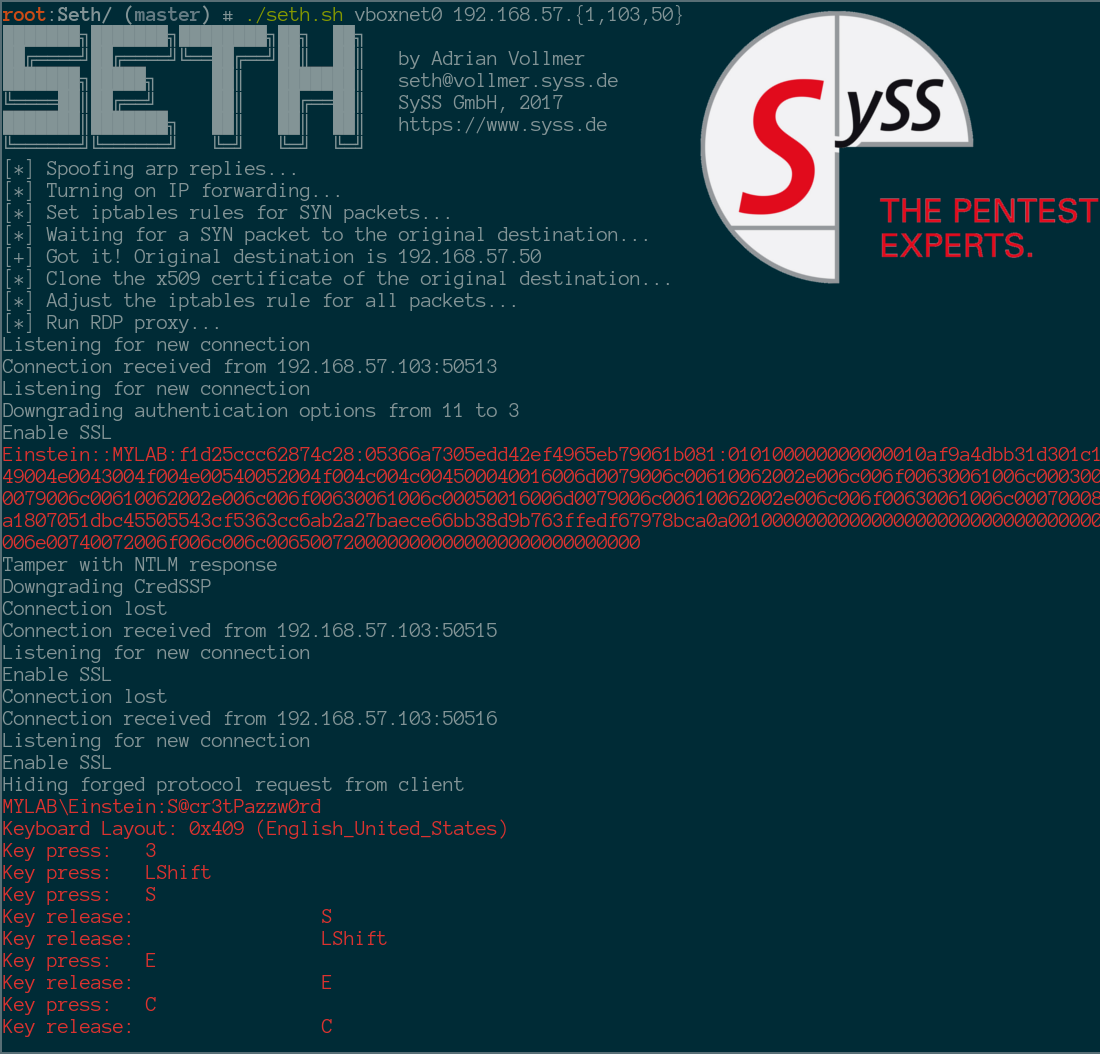 syss-research/seth
Perform a MitM attack and extract clear text credentials from RDP connections
 hakaioffsec/cve-2026-44706
Chatwoot SQL injection in FilterService
 eliasdekiniweek/cve-2022-26923
Exploitation de CVE-2022-26923
 swapnildeshpande/cve-2025-29927-lab
Reproduction lab for CVE-2025-29927 — Next.js middleware authorization bypass (CVSS 9.1)
 enochgitgamefied/nextjs-cve-2025-29927
Intentionally vulnerable Next.js application demonstrating CVE-2025-29927 authentication bypass via middleware WAF evasion. Designed for security…

 kartik2005221/cve-2025-58434-poc
Proof-of-concept exploit for CVE-2025-58434, demonstrating unauthenticated account takeover in Flowise via leaked password reset tokens. Includes…

 xaoczenon/cve-2026-20896
this is a modified POC of rz1027 for CVE-2026-20896
 pervinzahidli/cve-2026-77771
Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…
 lucastran05/cve-2026-29000
Local lab simulating CVE-2026-29000 JWT/JWE authentication bypass in pac4j-jwt. Provides login, token forging, and dashboard APIs for practicing web…
 kso4more/cve-2025-0108
Reproduces CVE-2025-0108 path confusion vulnerability in Nginx/Apache stacks. Includes a vulnerable PoC and a patched implementation demonstrating…
 wh0am123/cve-2025-54918-poc
POC for CVE-2025-54918 and a technical demonstration.
 red-darkin/cve-2026-18963-keycloak
Proof-of-concept exploit for CVE-2026-18963, a critical Keycloak reset-credentials bypass enabling unauthenticated account takeover. Includes lab…