
Apache-APISIX-CVE-2022-24112
 m4xsec/apache-apisix-cve-2022-24112
Apache APISIX Remote Code Execution (CVE-2022-24112) proof of concept exploit
api-securityapi-security-testingexploitation+3
15
m4xsec/apache-apisix-cve-2022-24112Apache APISIX Remote Code Execution (CVE-2022-24112) proof of concept exploit
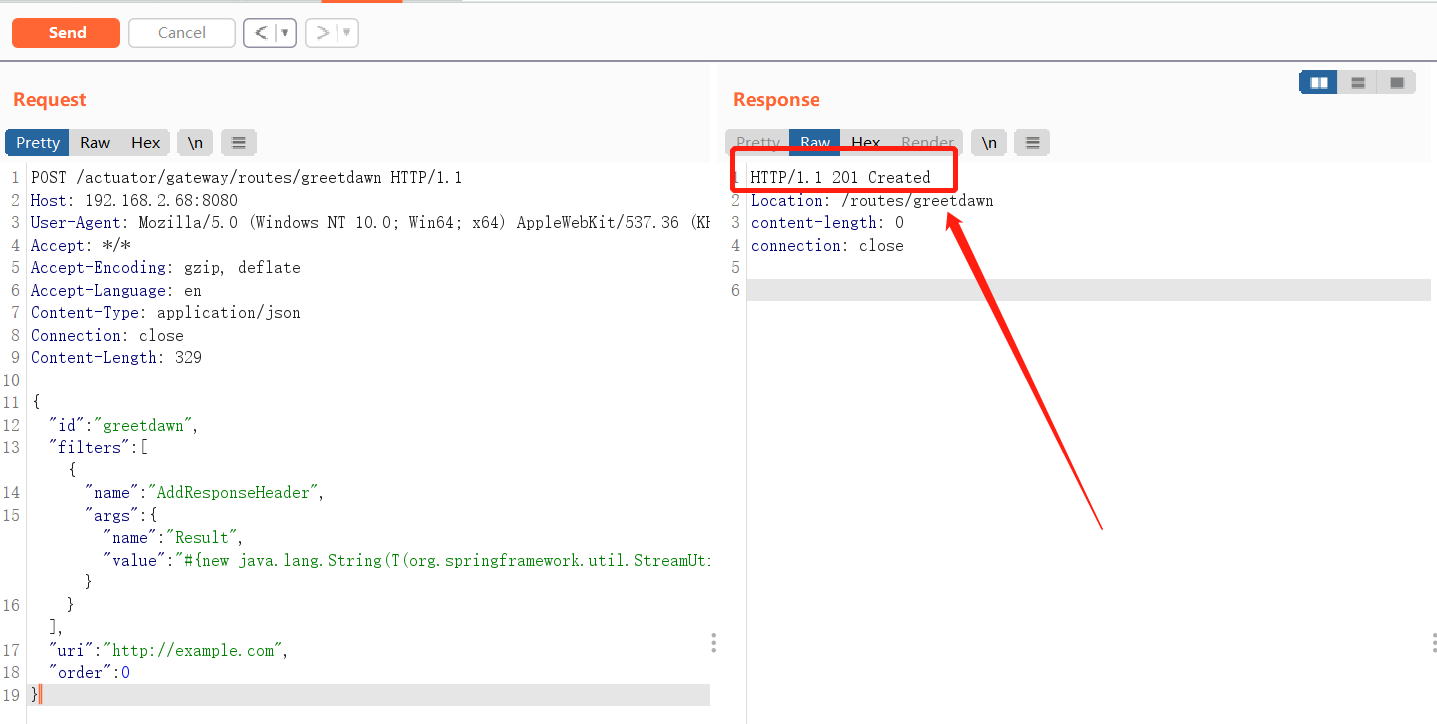 greetdawn/cve-2022-22947
PoC exploit for CVE-2022-22947: SpEL injection in Spring Cloud Gateway enabling remote command execution via crafted Actuator API routes.
 loaxert/cve-2025-59528-poc
PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB
 kavishkagihan/cve-2022-24112-poc
Apache APISIX 2.12.1 Remote Code Execution by IP restriction bypass and using default admin AIP token
 mxm0z/r2s
A web-based vulnerability scanner for CVE-2025-55182, a critical Remote Code Execution (RCE) vulnerability in React Server Components.
 shoucheng3/apache__dubbo_cve-2021-30180_2-7-9
Exploit for CVE-2021-30180 targeting Apache Dubbo RPC framework, enabling remote code execution via crafted RPC requests in vulnerable versions.
 grtmaldet/big-ip-next-cve-2024-26026
Proof-of-concept exploit for CVE-2024-26026: unauthenticated SQL injection in F5 BIG-IP Next Central Manager API, enabling remote data extraction and…
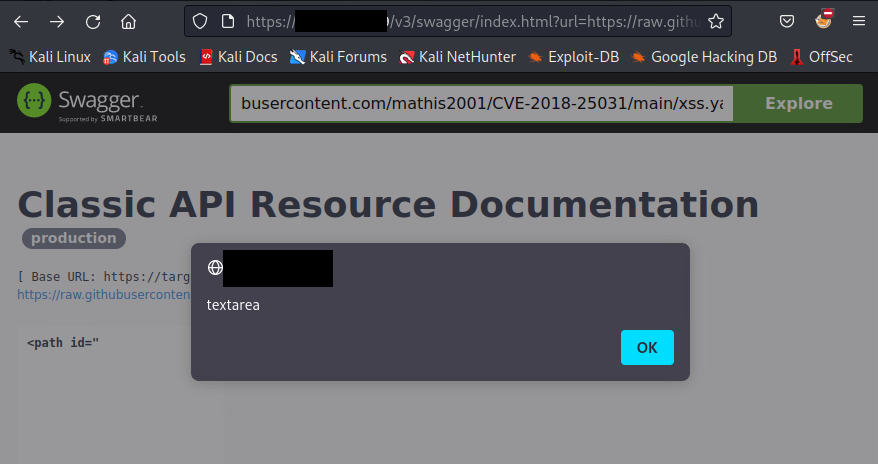 mathis2001/cve-2018-25031
CVE-2018-25031 tests
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 punitdarji/gitlab-cve-2026-19478
Dockerized exploit lab and script for CVE-2026-19478, a critical unauthenticated GitLab GraphQL code injection enabling arbitrary Ruby method calls,…
 k3ystr0k3r/cve-2026-9198
PoC and detection guide for the critical unauthenticated RCE in IBM Langflow OSS, covering the auto_login token bypass and unsafe /validate/code…
 dylvie/cve-2026-30824-flowise-nvidia-nim-authentication
A proof-of-concept exploit for **CVE-2026-30824**, a critical authentication bypass vulnerability in Flowise that exposes NVIDIA NIM API endpoints…