

crAPI
 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
api-securityapi-security-testingeducation+3
1.6k18 days ago
owasp/crapiDeliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
 owasp/dvsa
a Damn Vulnerable Serverless Application
 owasp/apicheck
Modular DevSecOps toolset for REST API security testing, designed for developers, sysadmins, and penetration testers to automate security checks…
 mindpatch/simple-maven
Deliberately vulnerable C# API application for practicing web application exploitation and security testing. Includes Docker setup and documentation…
 appsecco/dvcsharp-api
Damn Vulnerable C# Application (API)
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 roottusk/vapi
vAPI is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios through Exercises.
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
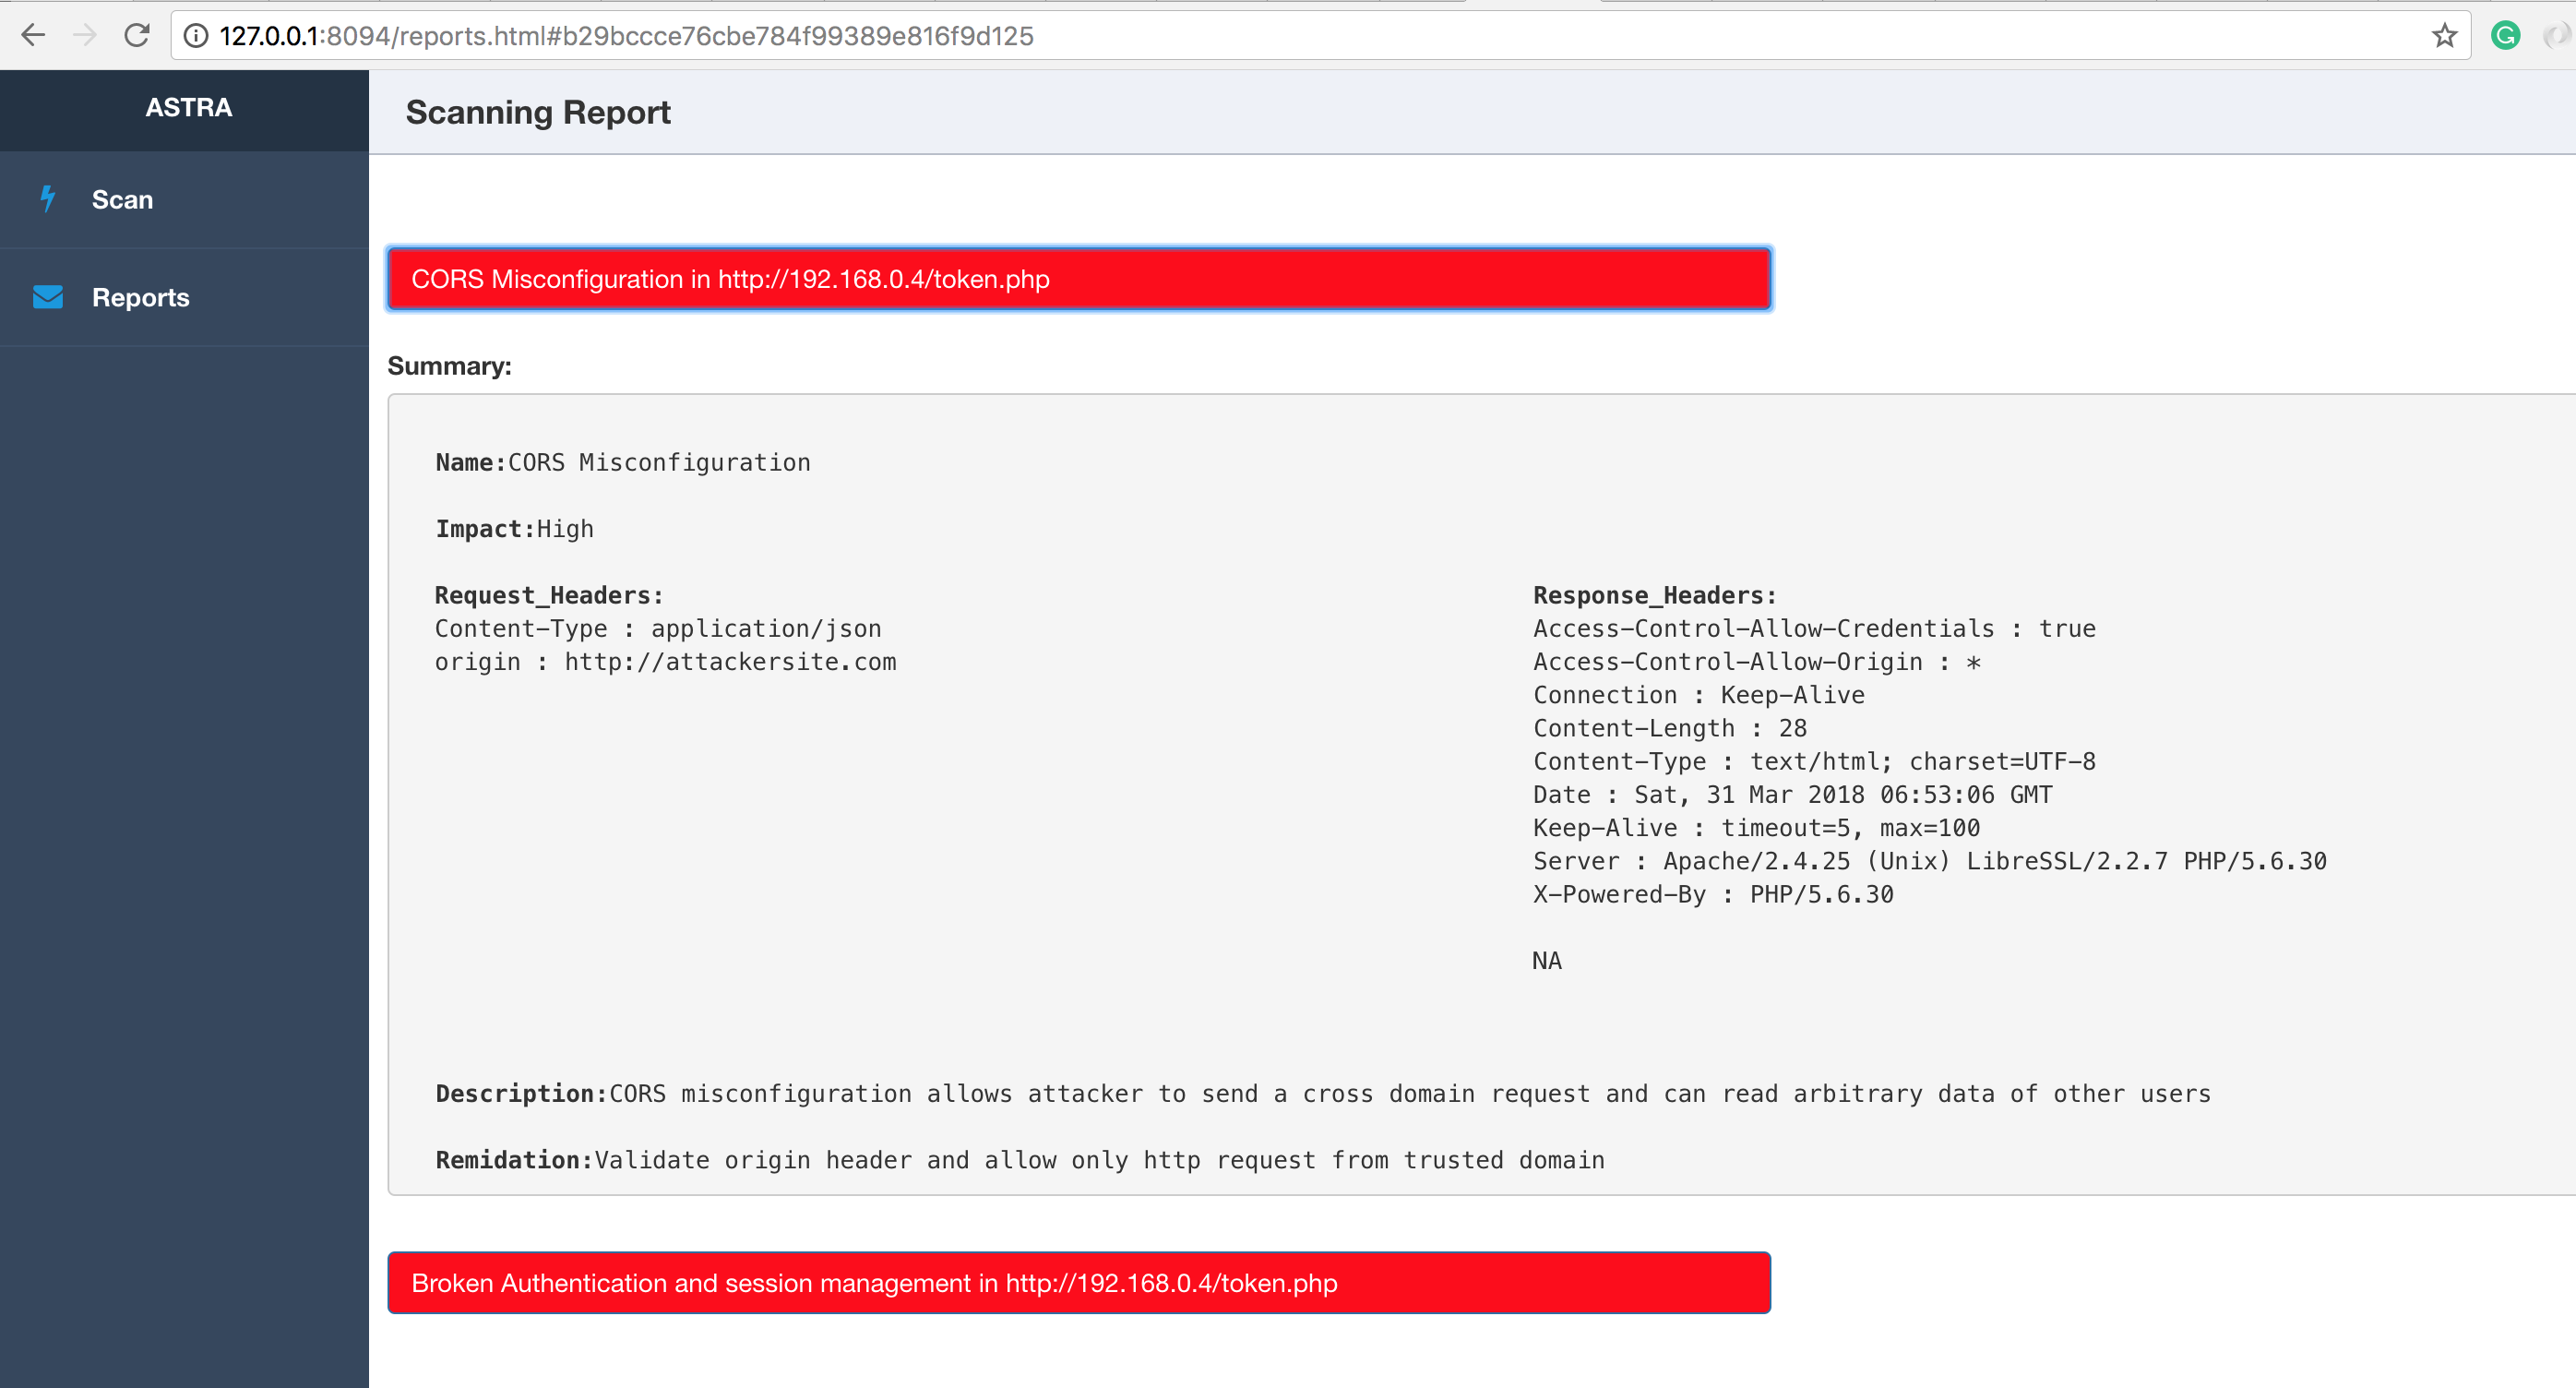 flipkart-incubator/astra
Automated Security Testing For REST API's
 keyvaluesoftwaresystems/agent-opfor
Open-source adversary emulation for AI agents and MCP servers.
 bbva/apicheck
The DevSecOps toolset for REST APIs
 owasp/raider
OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security
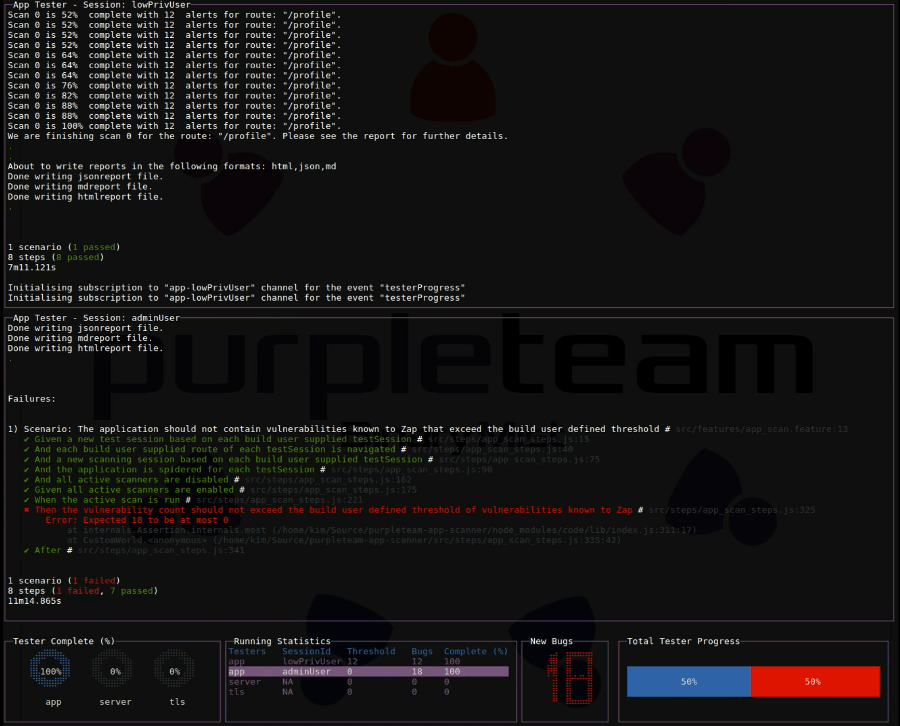
 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam