
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
92 results
URL_CHECKER preview

URL_CHECKER

GitHubmannansainicyber/url_checker

Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…

api-security-testingeducationmachine-learning+3
1
7 months ago
automatic-api-attack-tool preview

automatic-api-attack-tool

GitHubimperva/automatic-api-attack-tool

Imperva's customizable API attack tool takes an API specification as an input, generates and runs attacks that are based on it as an output.
api-securityapi-security-testingfuzzing+2
4966 years ago
authz0 preview

authz0

GitHubhahwul/authz0

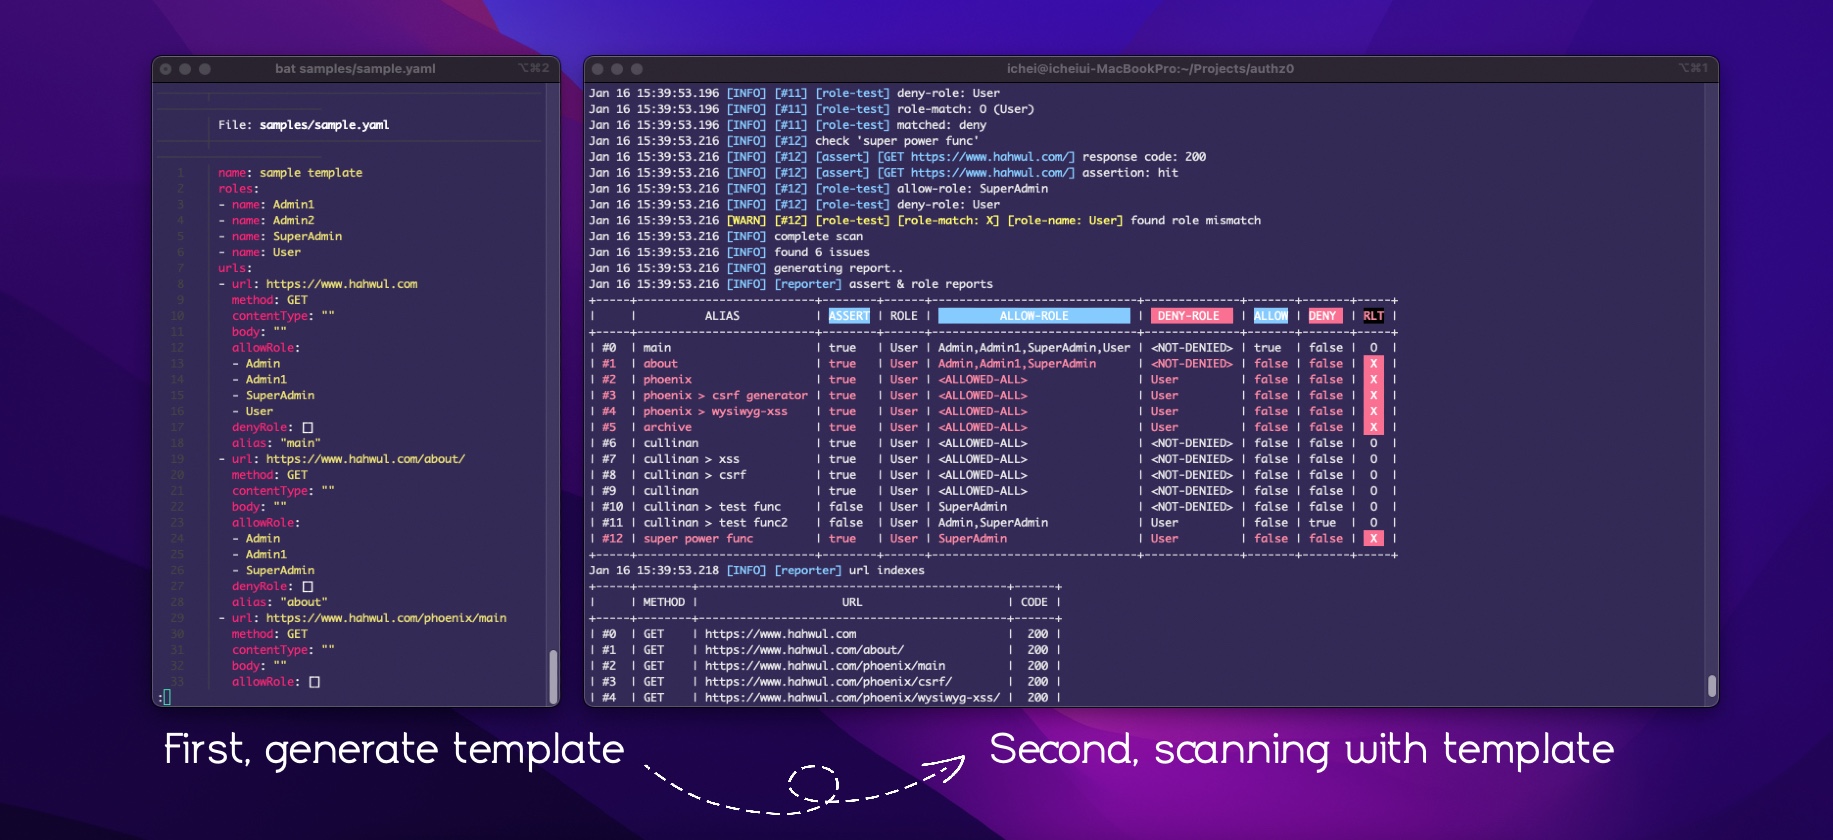
Automated authorization testing tool that detects unauthorized access by scanning URLs with role-based credentials using YAML templates.
api-security-testingvulnerability-scannersweb-security
4284 months ago
CVE-2026-44848-PoC preview

CVE-2026-44848-PoC

GitHubboreas37/cve-2026-44848-poc

PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.

api-security-testingauthentication-authorizationcontainer-security+3
12 months ago
akca preview

akca

GitHubakha-security/akca

Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.

api-security-testingdefensive-toolsdynamic-analysis-sandboxing+9
24212 days ago
Securiscan preview

Securiscan

GitHubvighnesh91/securiscan

Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…

ai-securityapi-securityapi-security-testing+8
20 days ago
kiterunner preview

kiterunner

GitHubassetnote/kiterunner

High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
api-securityapi-security-testingdynamic-code-analysis+5
3.3k5 years ago
OWASP-WSTG-Rag preview

OWASP-WSTG-Rag

GitHubzilbonn/owasp-wstg-rag

OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
ai-securityapi-security-testingauthentication+8
2310 months ago
Pegasus-Pentest-Arsenal preview

Pegasus-Pentest-Arsenal

GitHubsobri3195/pegasus-pentest-arsenal

A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
api-security-testingctfeducation+9
606 months ago
Detect_polyfill_CVE-2024-38537- preview

Detect_polyfill_CVE-2024-38537-

GitHubhavoc10-sw/detect_polyfill_cve-2024-38537-

Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.

api-security-testingconfiguration-auditingmisconfiguration+2
2 years ago
smugglex preview

smugglex

GitHubhahwul/smugglex

Rust-powered HTTP Request Smuggling Scanner.
api-security-testingdevsecopspenetration-testing+3
1354 days ago
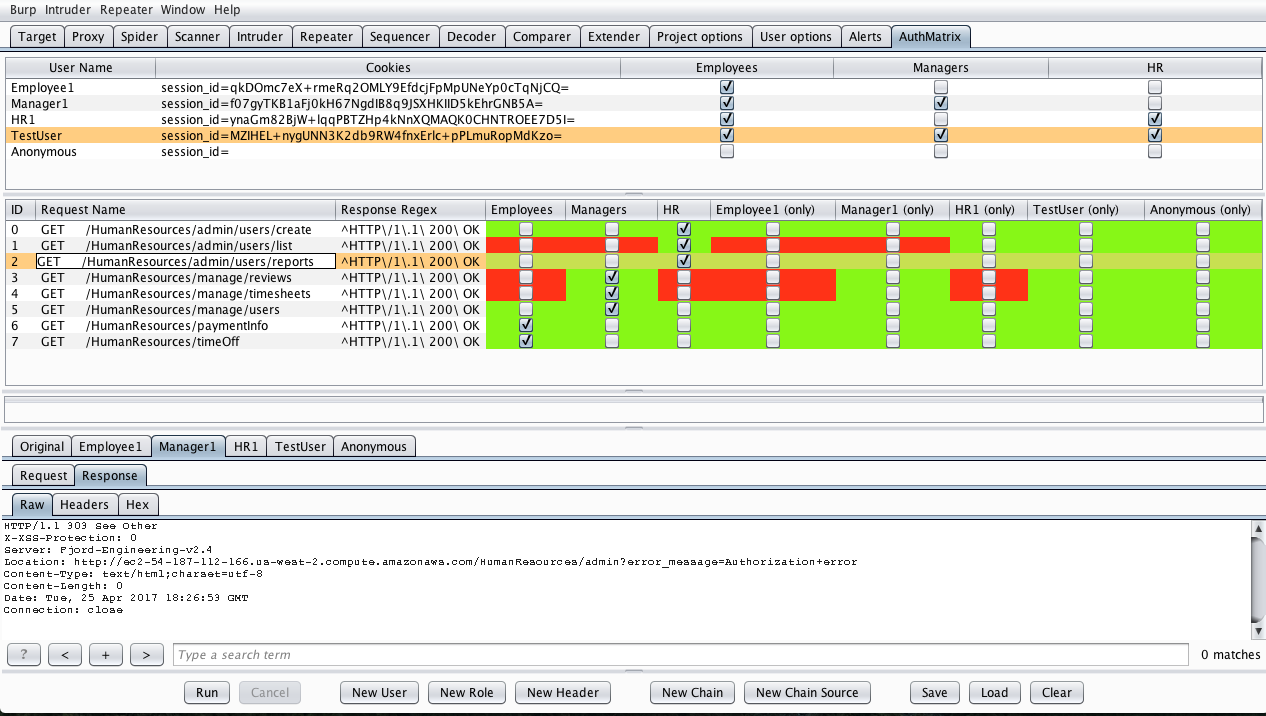
AuthMatrix preview

AuthMatrix

GitHubsecurityinnovation/authmatrix

AuthMatrix is a Burp Suite extension that provides a simple way to test authorization in web applications and web services.
api-security-testingpenetration-testingweb-security
6475 years ago
hackazon preview
Archived

hackazon

GitHubrapid7/hackazon

A modern vulnerable web app

api-security-testingeducationpenetration-testing+3
1.0k5 years ago
ActiveScanPlusPlus preview

ActiveScanPlusPlus

GitHubalbinowax/activescanplusplus

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
api-security-testingdefensive-toolsexploitation+7
6691 day ago
corsair_scan preview

corsair_scan

GitHubsantandersecurityresearch/corsair_scan

Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…

api-security-testingmisconfigurationvulnerability-scanners+1
1235 years ago
shadow-repeater preview

shadow-repeater

GitHubhackvertor/shadow-repeater

Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…

ai-securityapi-security-testingfuzzing+6
4311 months ago
nuclei preview

nuclei

GitHubprojectdiscovery/nuclei

Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

anti-botapi-securityapi-security-testing+21
32.2k1 day ago
SafeLine preview

SafeLine

GitHubchaitin/safeline

Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…

anti-botapi-securityapi-security-testing+8
22.9k10h 22m ago
Previous123456Next