
masq
 wattocyber/masq
Live recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
ai-securityapi-security-testingconfiguration-auditing+6
wattocyber/masqLive recon and posture auditing for AI agent infrastructure: scans MCP configs, session logs, and APIs for secrets, poisoned catalogs, and CoT leaks.
 n0xdaemon/cve-2026-19478
Provides PoC exploits and root-cause analysis for two GitLab GraphQL `@gl_introduced` directive vulnerabilities: unauthenticated method execution and…
 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 perufitlife/directus-security
Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
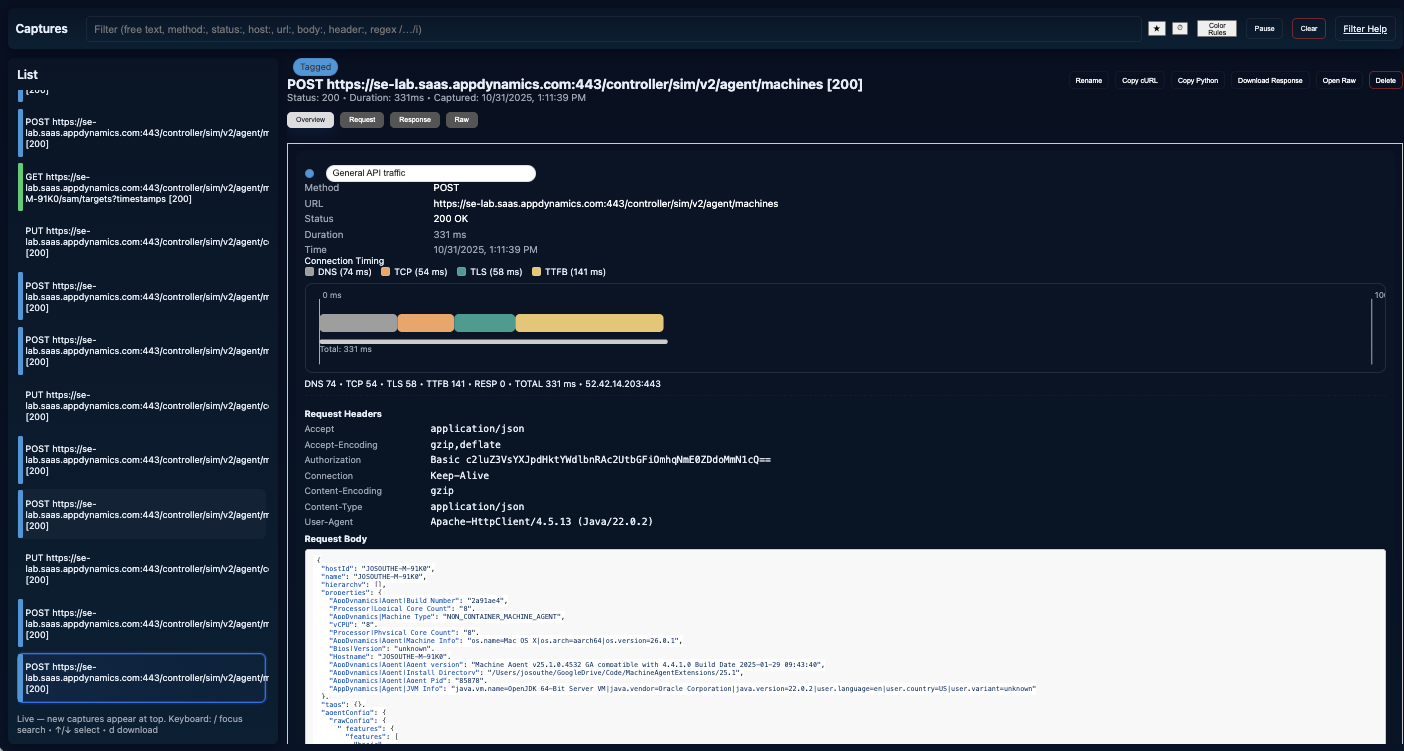 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 aquibpro/reconix
Advanced recon engine that finds real secrets, validates them live, and builds exploit paths from client-side intelligence.
 randomrobbiebf/cve-2023-45828
RumbleTalk Live Group Chat <= 6.1.9 - Missing Authorization via handleRequest
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…
 usebruno/bruno
Opensource IDE For Exploring and Testing API's (lightweight alternative to Postman/Insomnia)
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
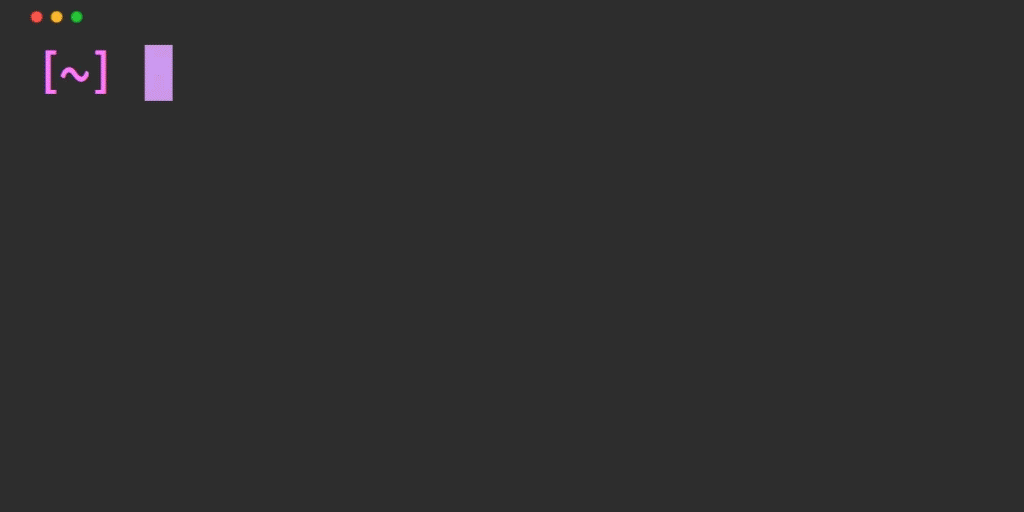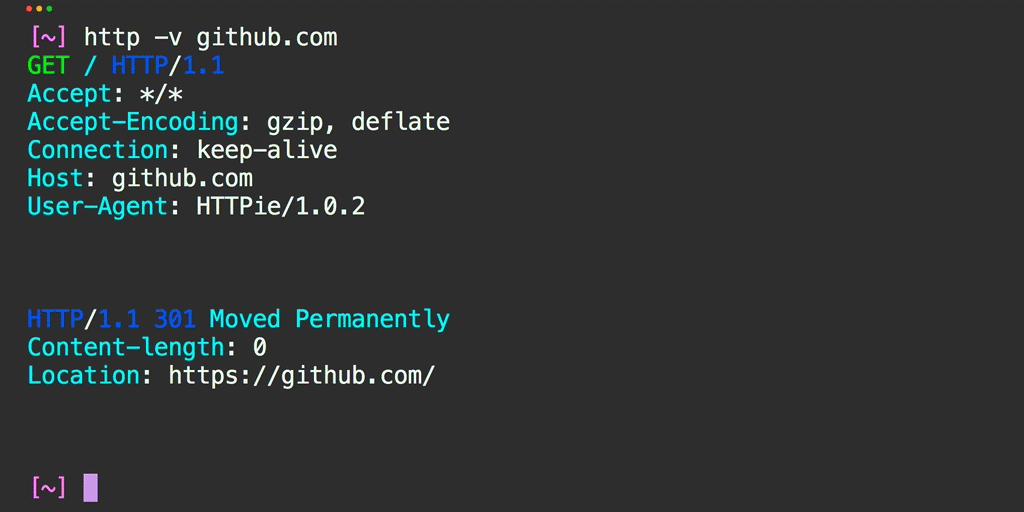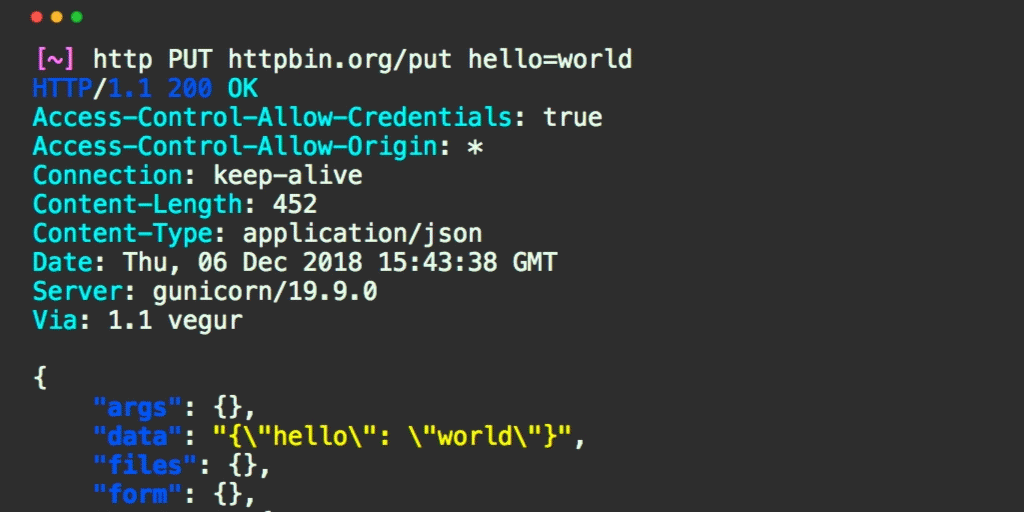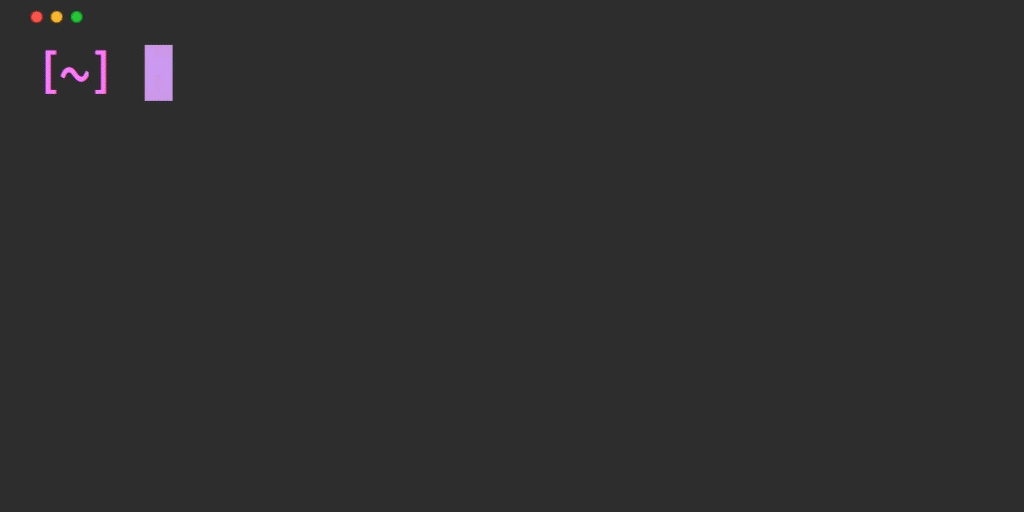 httpie/cli
🥧 HTTPie CLI — modern, user-friendly command-line HTTP client for the API era. JSON support, colors, sessions, downloads, plugins & more.
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…