
SpringVulScan
 tpt11fb/springvulscan
burpsuite 的Spring漏洞扫描插件。SpringVulScan:支持检测:路由泄露|CVE-2022-22965|CVE-2022-22963|CVE-2022-22947|CVE-2016-4977
api-security-testingexploitationpenetration-testing+3
155
tpt11fb/springvulscanburpsuite 的Spring漏洞扫描插件。SpringVulScan:支持检测:路由泄露|CVE-2022-22965|CVE-2022-22963|CVE-2022-22947|CVE-2016-4977
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
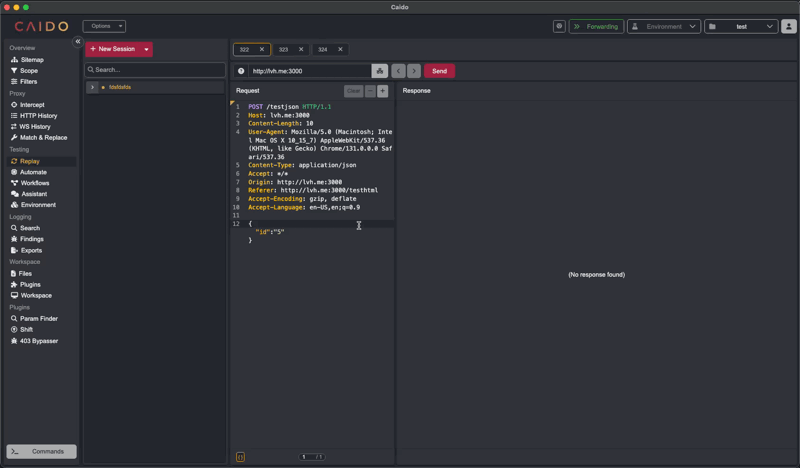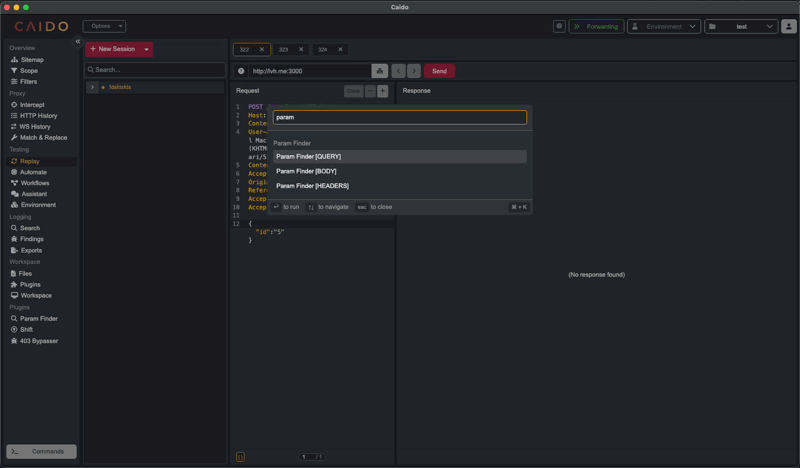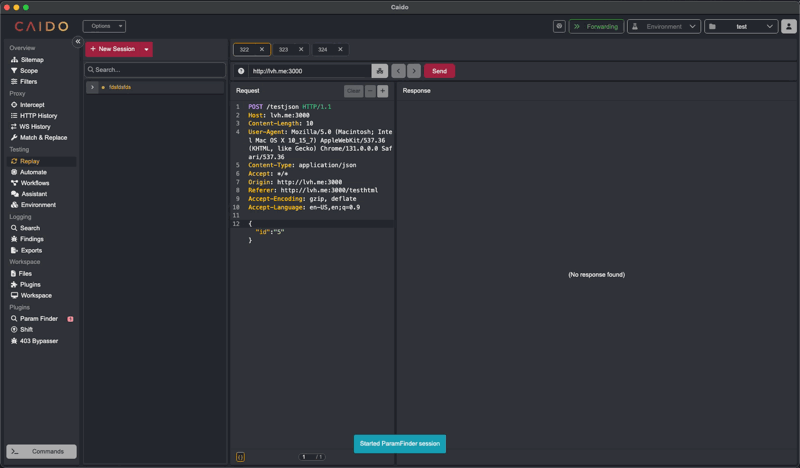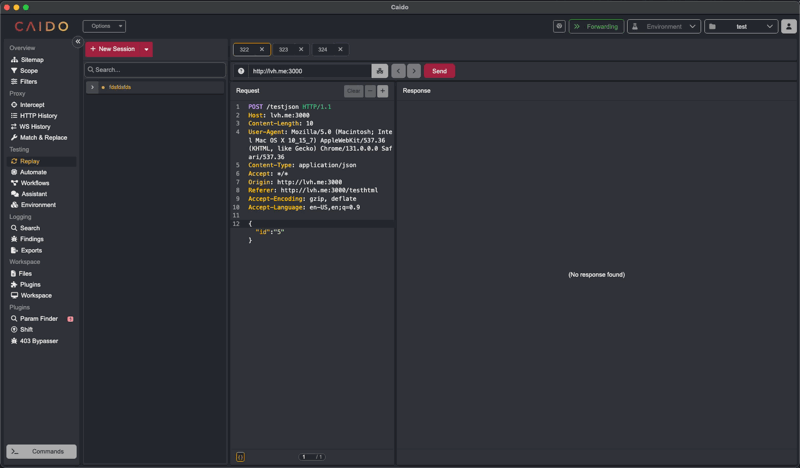 caido-community/paramfinder
Discover hidden parameters in Caido
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 joanbono/gurp
Burp Commander written in Go
 morpheuslord/nmap-api
RESTful API wrapping Nmap for automated network scanning, port detection, service enumeration, and vulnerability analysis with optional AI-powered…
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 mirfansulaiman/customheader
This Burp Suite extension allows you to customize header with put a new header into HTTP REQUEST BurpSuite (Scanner, Intruder, Repeater, Proxy…
 nccgroup/wcfdser-ngng
A Burp Extender plugin, that will make binary soap objects readable and modifiable.
 emo-crab/slinger
An HTTP client specifically developed for security researchers
 logisek/huntcyberark
CyberArk Security Audit
 raz0r/burp-radamsa
Radamsa fuzzer extension for Burp Suite
 nccgroup/amfdser-ngng
A Burp Extender plugin, that will take deserialized AMF objects and encode them in XML using the Xtream library
 projectdiscovery/collaborator
BurpSuite Standard/Private Collaborator Library
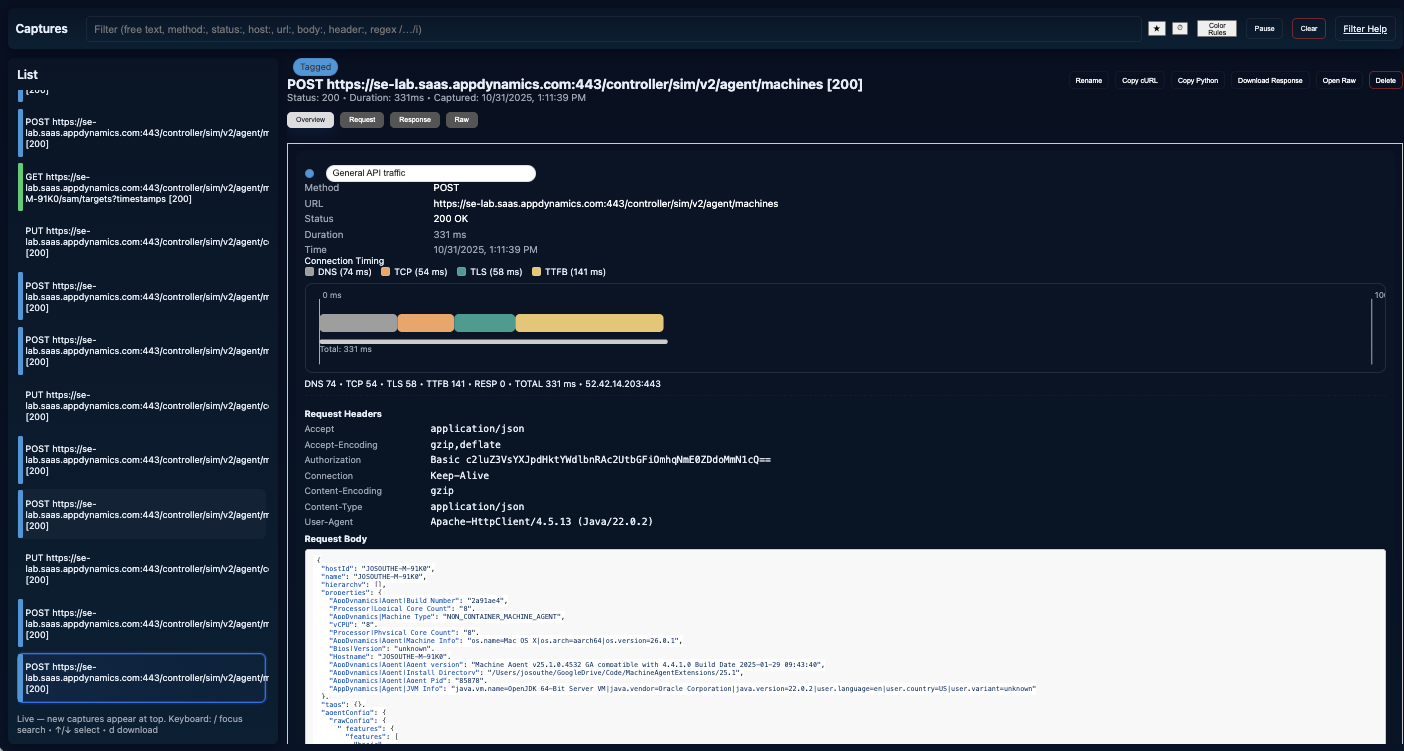 jbsouthe/http-breakout-proxy
HTTP Proxy Analysis for reverse engineering protocol communication
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…