perwendel__spark_CVE-2018-9159_2_7_2_fixed

Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.

Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.

Type-safe HTTP client library for Android and Java, enabling REST API communication with annotation-based request configuration and converter support.

Type-safe HTTP client for Android and Java with annotation-based API binding, converter support, and integration with OkHttp for network…

Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…

API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…

The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…

Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.

An interactive TLS-capable intercepting HTTP proxy for penetration testers and software developers.


A fast, simple, recursive content discovery tool written in Rust.

Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!

A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.

Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…

A coverage-guided REST API fuzzer developed on top of LibAFL

Burp Suite Extension useful to verify OAUTHv2 and OpenID security

OWASP Raider: a novel framework for manipulating the HTTP processes of persistent sessions

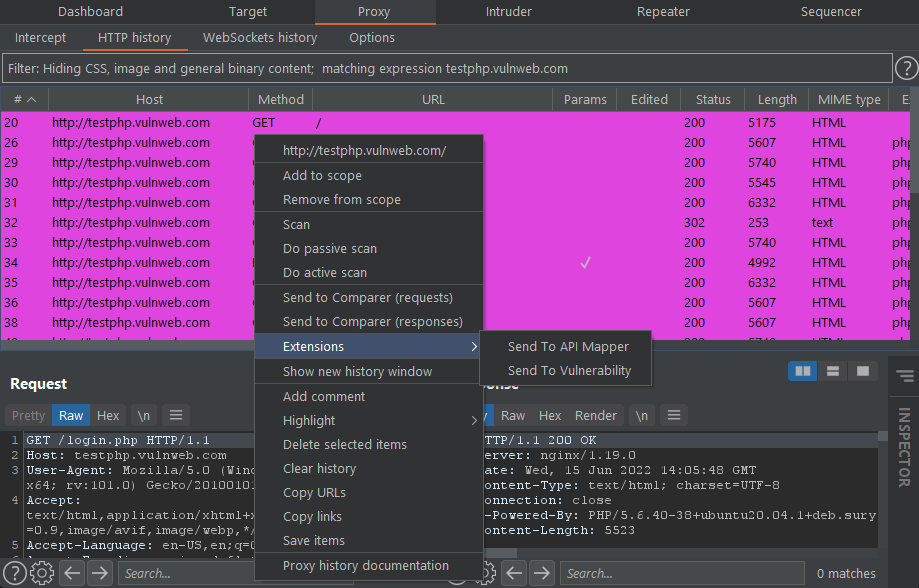
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities

Performing automated scan using Burp Suite Pro & Vmware Burp Rest API