
area51
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
api-security-testingcloud-securityemail-security+4
6
thoropass-public/area51The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 randomrobbiebf/cve-2023-32117
Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints
 bogdanticu88/ratrace
A lightweight CLI tool for systematically detecting and exploiting race conditions in web applications, APIs, and modern services.
 kabiri-labs/cve-2024-40094
This script exploits the CVE-2024-40094 vulnerability in graphql-java
 george0papasotiriou/cve-2026-11103-graphql-batching-alias-rate-limit-bypass
Proof-of-concept exploit for CVE-2026-11103 demonstrating GraphQL rate-limit bypass through batching and field aliases; includes vulnerable Node.js…
 oscerd/cve-2026-48204
Reproducer for CVE-2026-48204: Apache Camel camel-mongodb-gridfs gridfs.* header injection overriding the GridFS operation (enumerate/read/delete…
 biitts/cve-2026-54917-seaweedfs-cross-bucket-traversal
PoC + analysis for CVE-2026-54917 — SeaweedFS S3 gateway cross-bucket path traversal (CVSS 10.0, <4.30). Read/write any bucket via .. in the object…
 oscerd/cve-2026-48206
Reproducer for CVE-2026-48206: Apache Camel camel-jira IssueKey (and other non-Camel-prefixed) header injection driving arbitrary JIRA issue…
 kovachvl/cve-2026-54356
Proof-of-concept exploit and advisory for CVE-2026-54356, a Budibase missing-authorization flaw that lets low-privilege users mint S3 pre-signed…
 oscerd/cve-2026-46592
Reproducer for CVE-2026-46592: Apache Camel camel-cxf operationName header injection redirecting the invoked SOAP operation (confused deputy) from a…
 oscerd/cve-2026-49099
PoC reproducer for CVE-2026-49099 (Apache Camel camel-salesforce): the non-Camel-prefixed sObjectQuery header escapes the HTTP header filter and…
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 fopje/cve-2022-36539
Insecure Permissions WeDayCare
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 richard-natan/poc-cve-2025-63406
Proof-of-concept for CVE-2025-63406 in GroupOffice, demonstrating API-based object manipulation and authentication flow for vulnerability analysis…
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
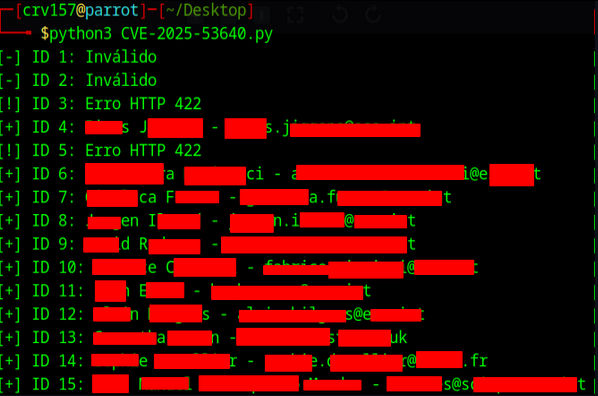 rafaelcorvino1/cve-2025-53640
Broken Object Level Authorization (BOLA) in CERN's Indico leads to authenticated user enumeration.