

faraday_burp
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
api-security-testingdevsecopspenetration-testing+3
infobyte/faraday_burpBurp Extension for collaboration in Faraday
 rushi9/zimaos-cve-2026-28286-arbitrary-file-write
PoC and verification toolkit for CVE-2026-28286, an arbitrary file write vulnerability in ZimaOS, exploiting API misconfiguration to write files…
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
 mateustesser/cve-2023-31719
Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…

 bishopfox/snowpick
find sensitive data leaking from ServiceNow instances.
 aquibpro/reconix
Advanced recon engine that finds real secrets, validates them live, and builds exploit paths from client-side intelligence.
 digeex/raider
DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
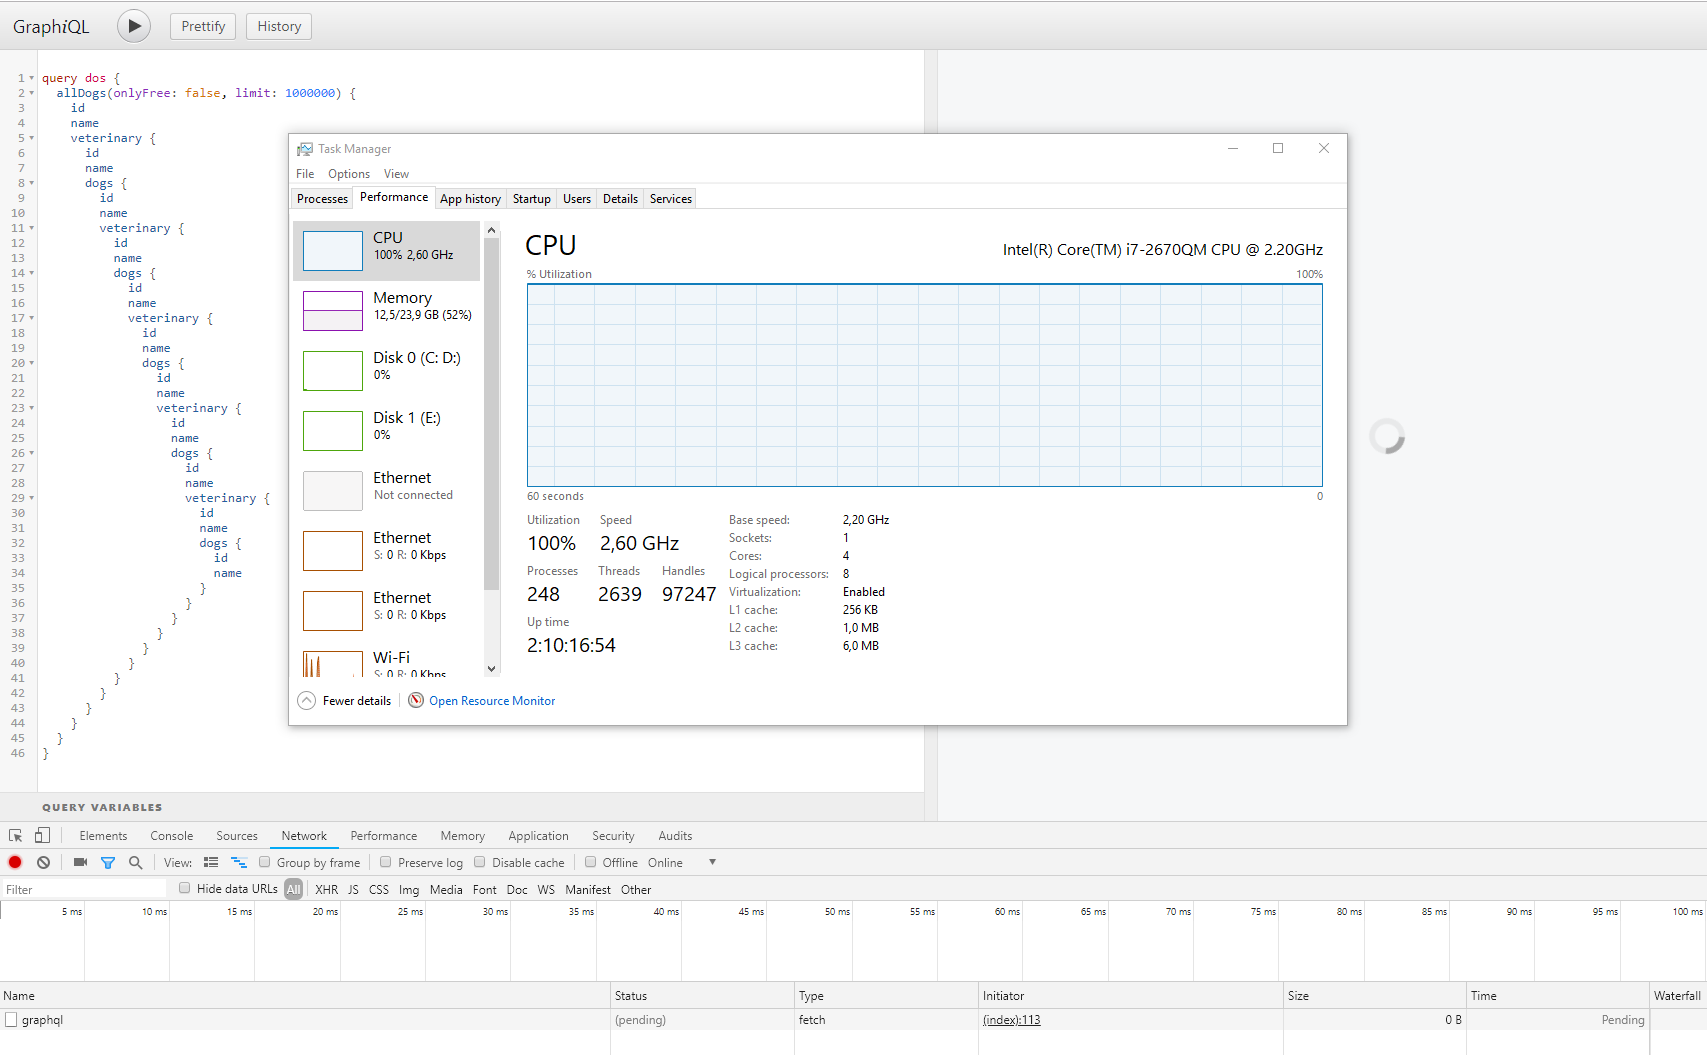 righettod/poc-graphql
Research on GraphQL from an AppSec point of view.
 joanbono/gurp
Burp Commander written in Go
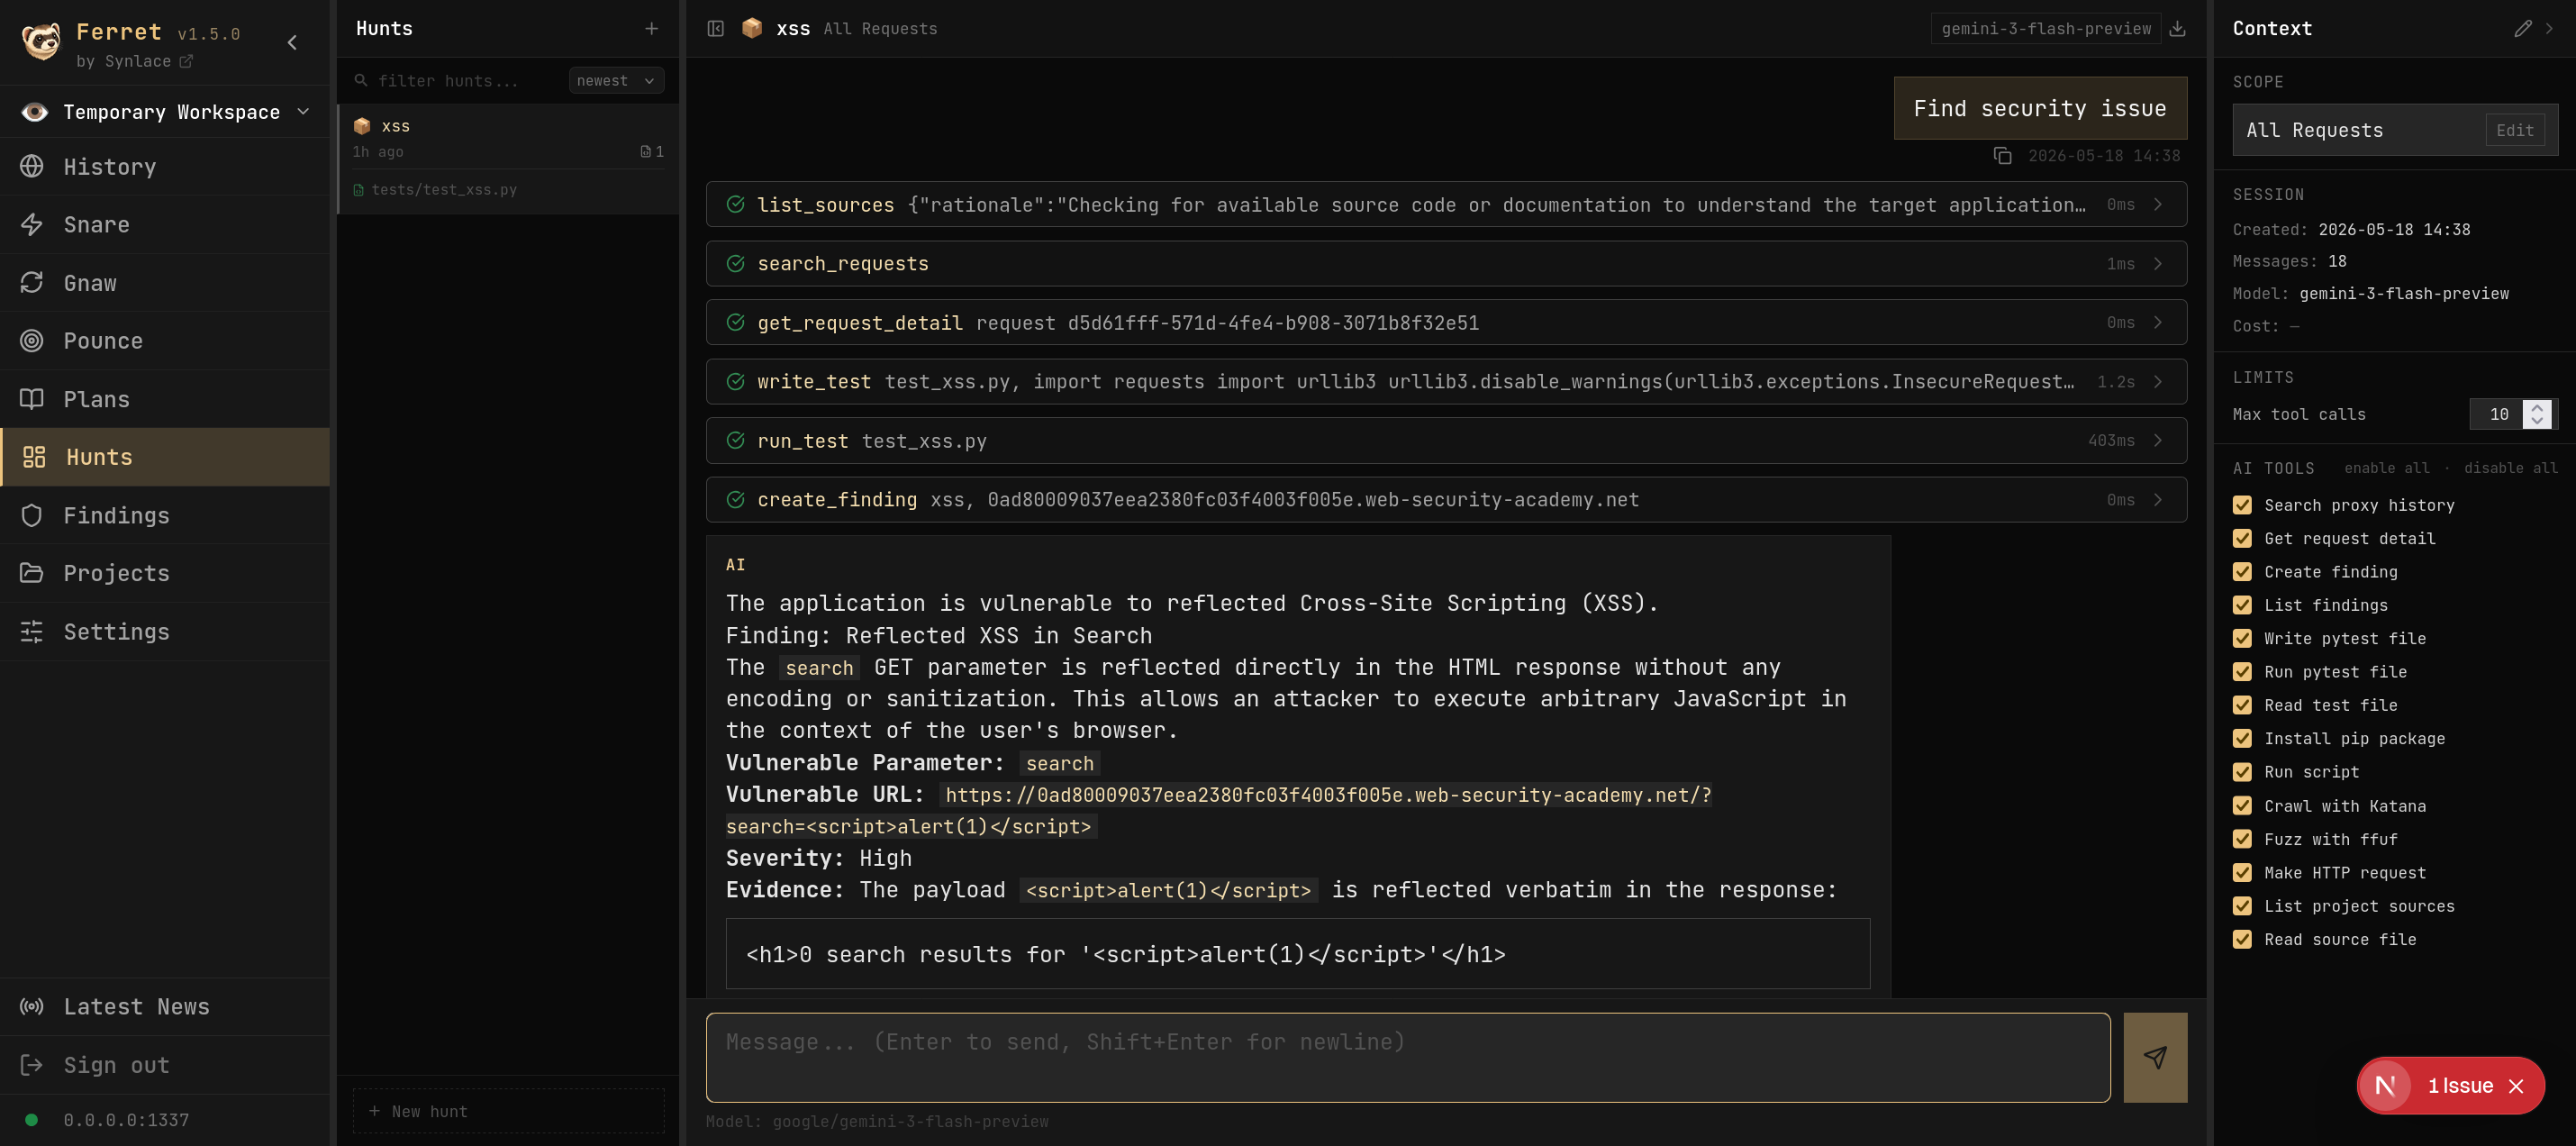 synlace/ferret
The collaborative web app pentest suite
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…