
nuclei-burp-plugin
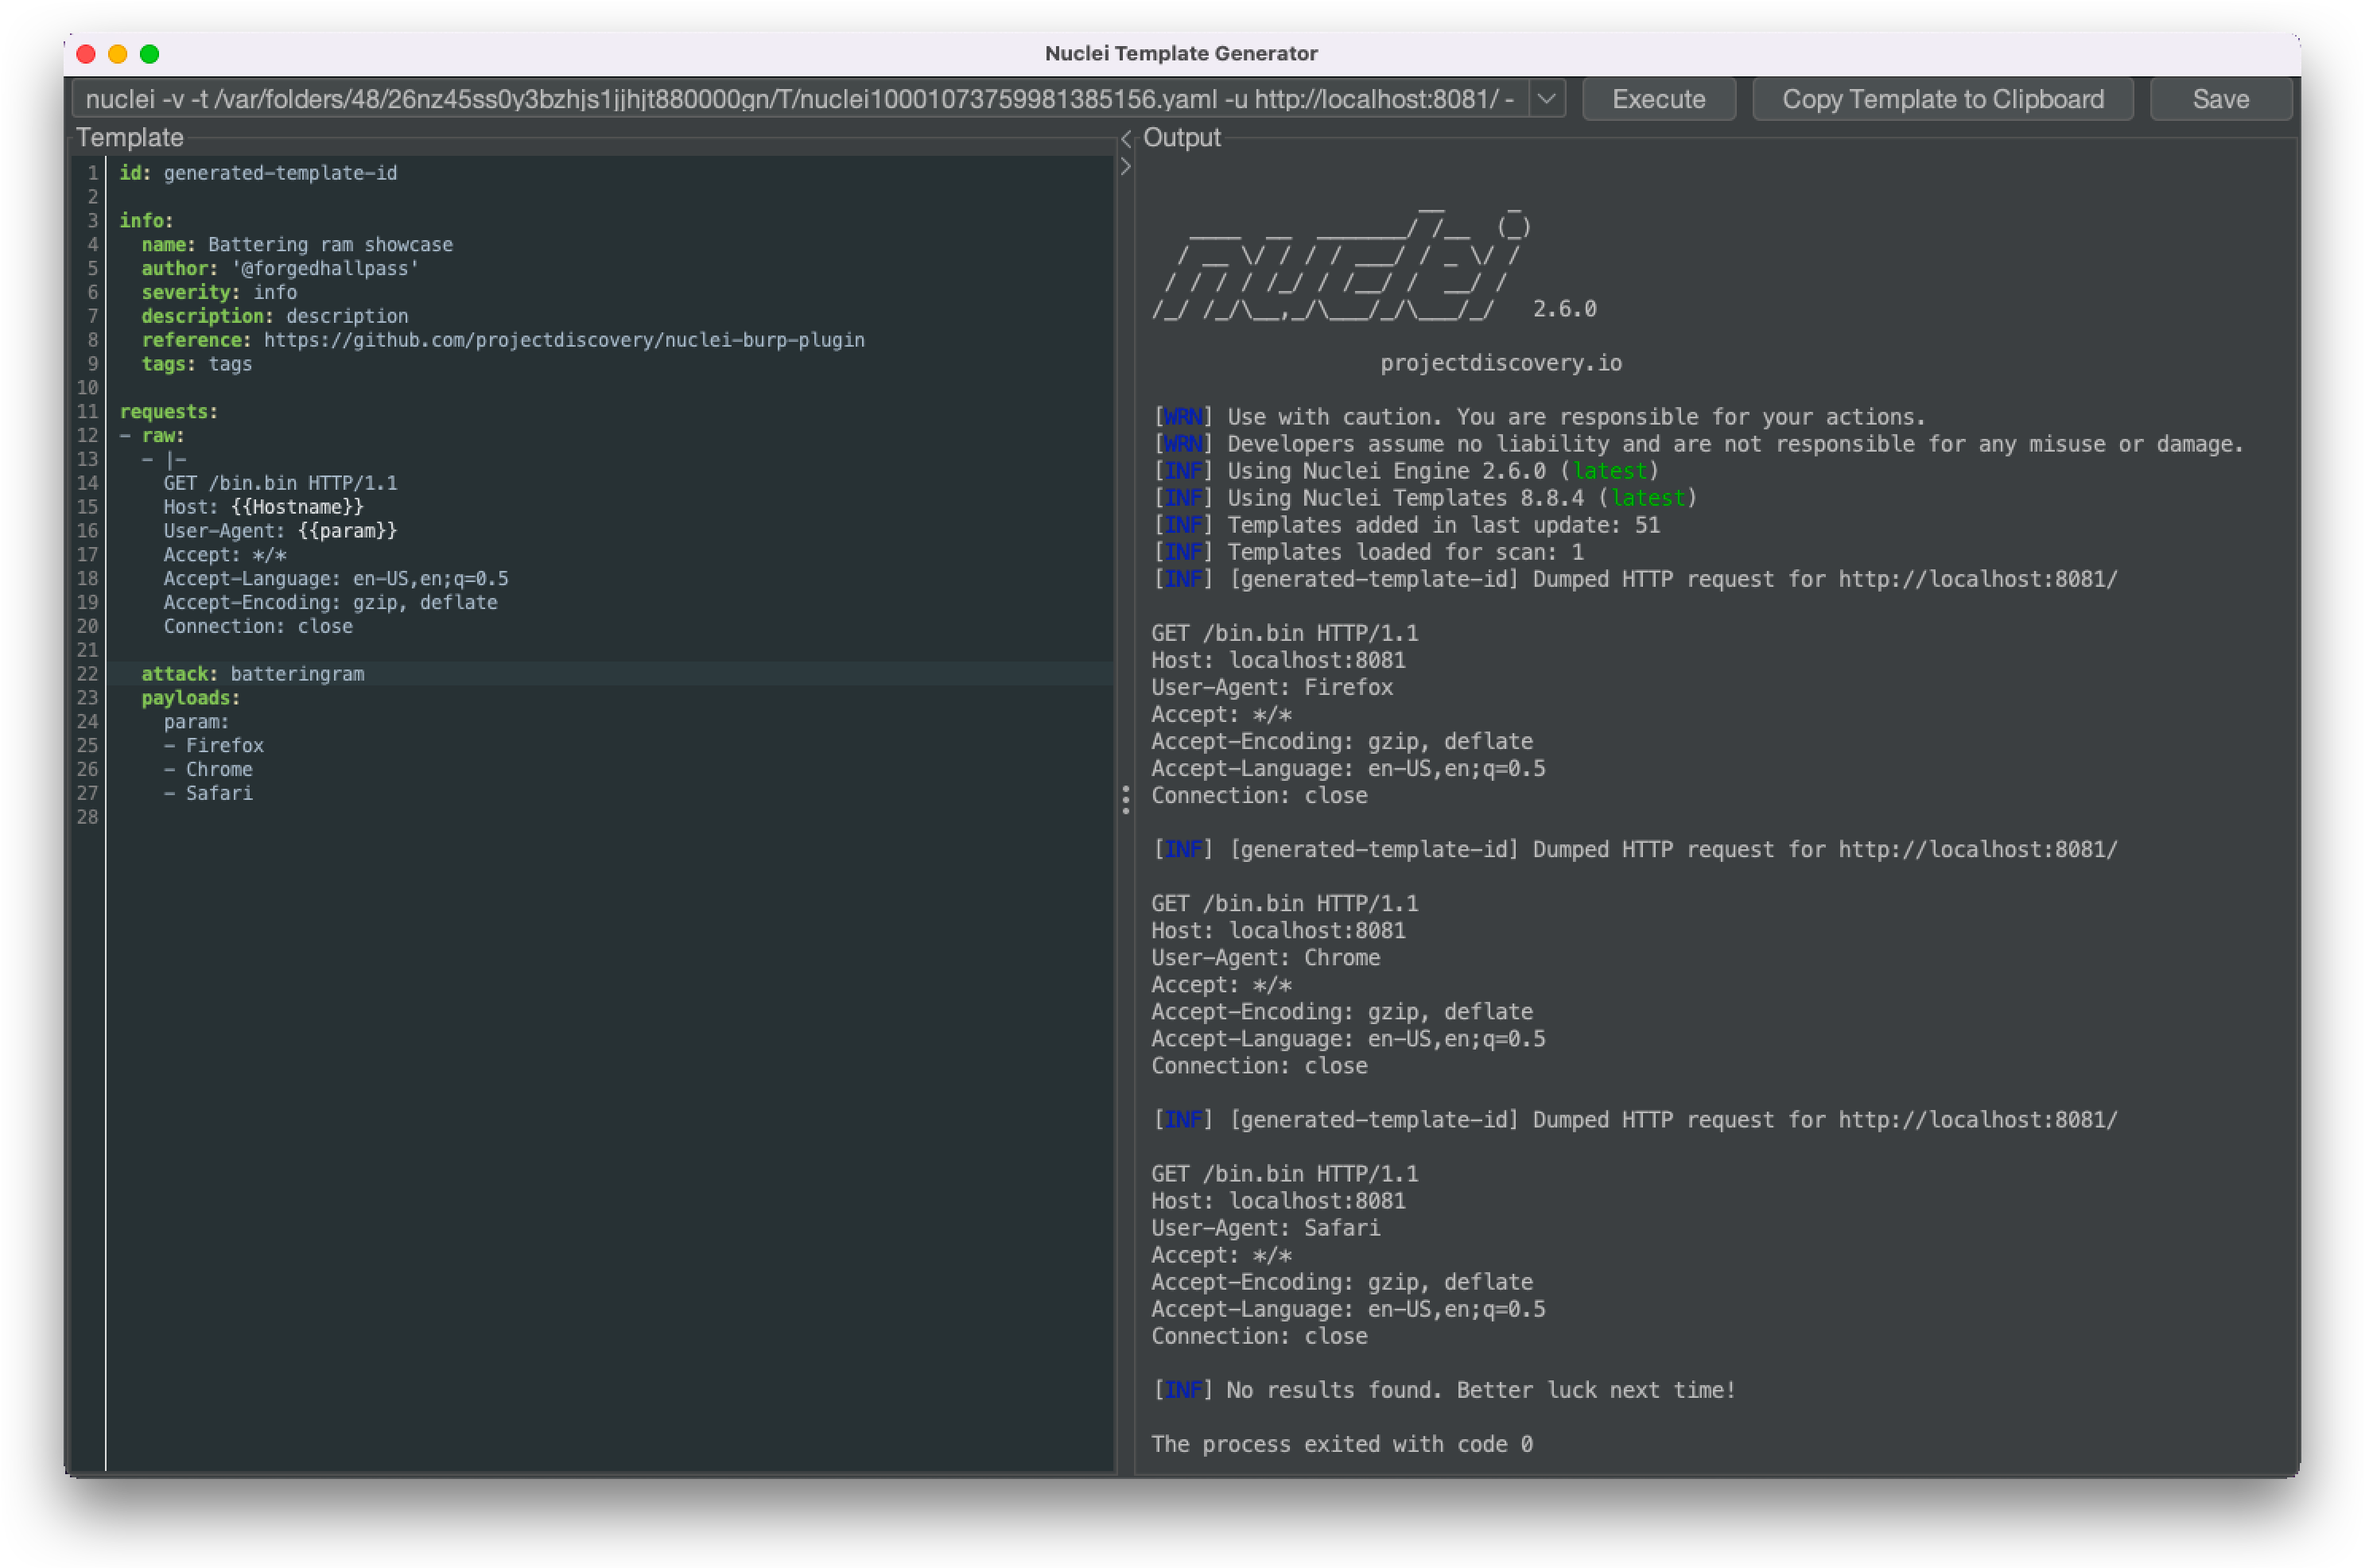
Burp Suite plugin for generating and executing Nuclei vulnerability templates directly from HTTP requests and responses, with YAML auto-complete and…

Burp Suite plugin for generating and executing Nuclei vulnerability templates directly from HTTP requests and responses, with YAML auto-complete and…

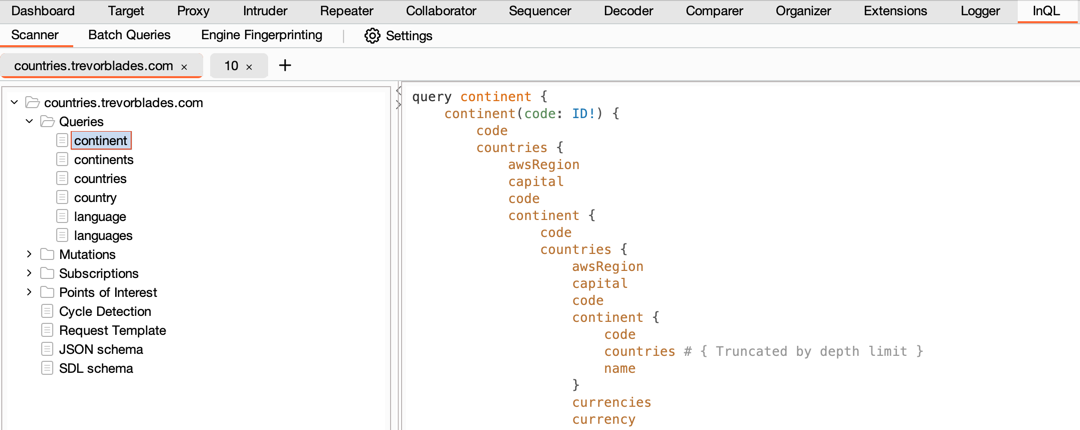
InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…

Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…

RESTful API wrapping Nmap for automated network scanning, port detection, service enumeration, and vulnerability analysis with optional AI-powered…

Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.

A proof-of-concept exploit for **CVE-2026-30824**, a critical authentication bypass vulnerability in Flowise that exposes NVIDIA NIM API endpoints…

The code for personally reproducing the corresponding vulnerability

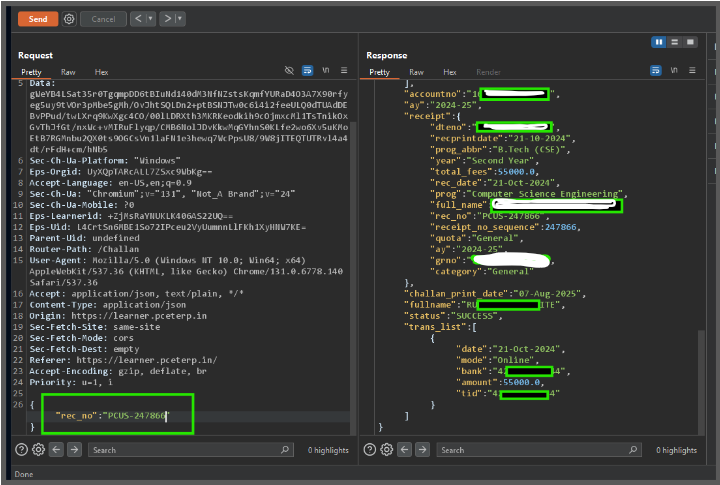
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…

Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…

Spring Cloud Gateway repository demonstrating CVE-2022-22947 exploitation for API security testing and vulnerability analysis.

Proof-of-concept exploit for CVE-2024-50633, a Broken Object Level Authorization (BOLA) vulnerability in Indico v3.2.9–v3.3.2, enabling unauthorized…

Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …

CVE-2026-27944 - Nginx UI Unauthenticated Backup Download & Decryption

PortSwigger Burp Plugin for the Log4j (CVE-2021-44228)

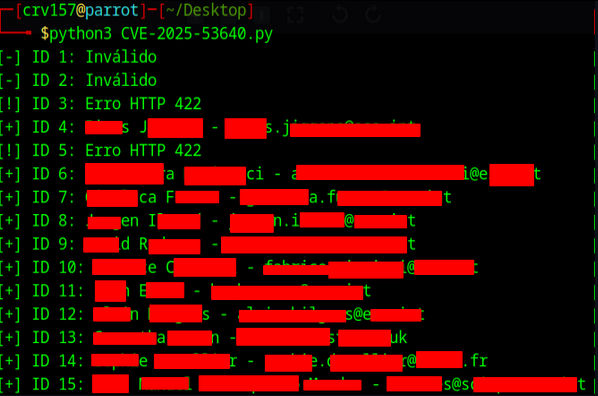
Broken Object Level Authorization (BOLA) in CERN's Indico leads to authenticated user enumeration.

PoC de CVE-2026-35616: control de acceso indebido en FortiClient EMS.

Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324

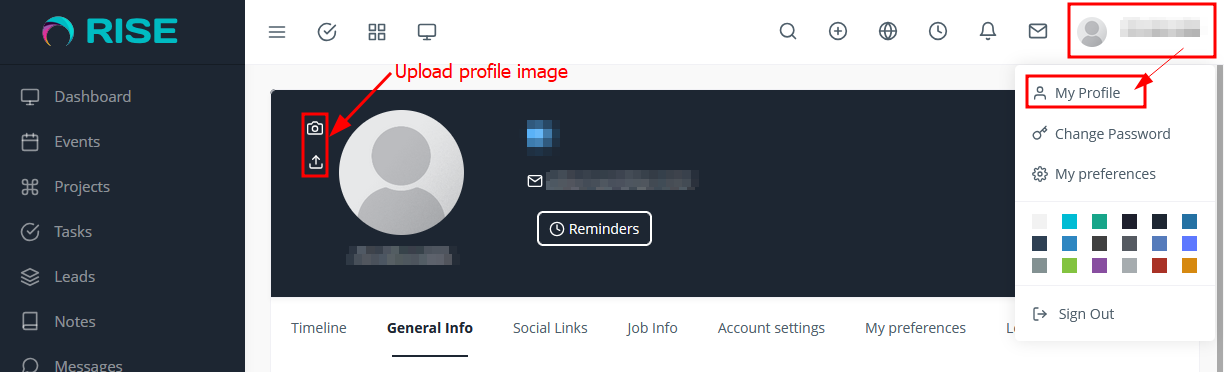
CVE-2025-3855 - RISE Ultimate Project Manager - IDOR