
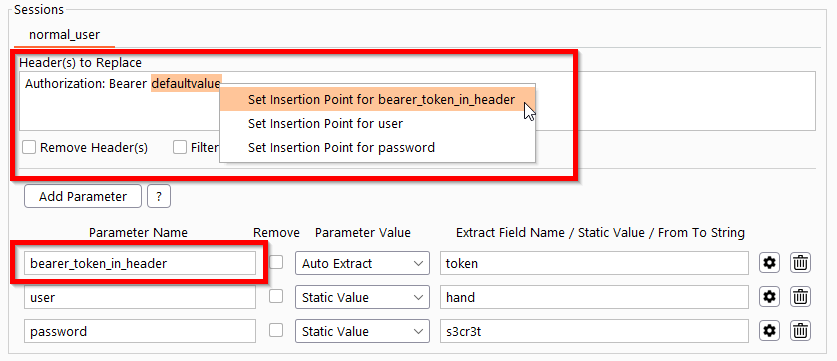
auth_analyzer
 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
api-security-testingauthentication-authorizationpenetration-testing+1
226
simioni87/auth_analyzerBurp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
 assetnote/batchql
GraphQL security auditing script with a focus on performing batch GraphQL queries and mutations
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 zjuicsr/actbench
Code for paper "ActBench: Self-Evolving Benchmark of Behavioral Safety in Cowork Agents"
 loaxert/cve-2025-59528-poc
PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
 clemfavre/cve-2023-45612_exploit
Reproduction of a high severty security problem that allows XXE (XML eXternal Entity) attacks on Ktor's XML serialization.
 0xsu3ks/cve-2025-29556
PoC for CVE-2025-29556 creating Security Officer accounts on ExaGrid EX10 backup appliances via a low-privilege API session, enabling privilege…
 ashiqrehan-21/mcp-inspector-cve-2025-49596
MCP-Inspector-vulncheck is a Python script that checks if an MCP Inspector server is vulnerable to CVE-2025-49596. It tests whether the /sse endpoint…
 mindpatch/simple-maven
Deliberately vulnerable C# API application for practicing web application exploitation and security testing. Includes Docker setup and documentation…
 h2non/toxy
Hackable HTTP proxy for resiliency testing and simulated network conditions
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
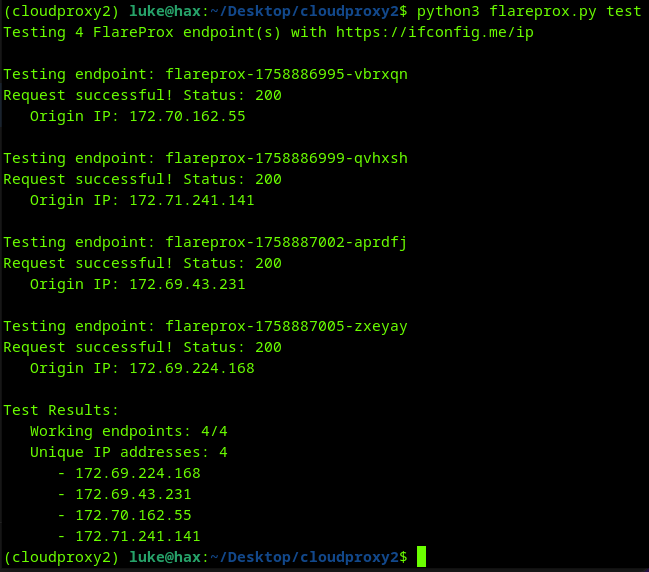 mrturvey/flareprox
Use Cloudflare to create HTTP pass-through proxies for unique IP rotation, similar to fireprox
 appsecco/dvcsharp-api
Damn Vulnerable C# Application (API)
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…