
Archived
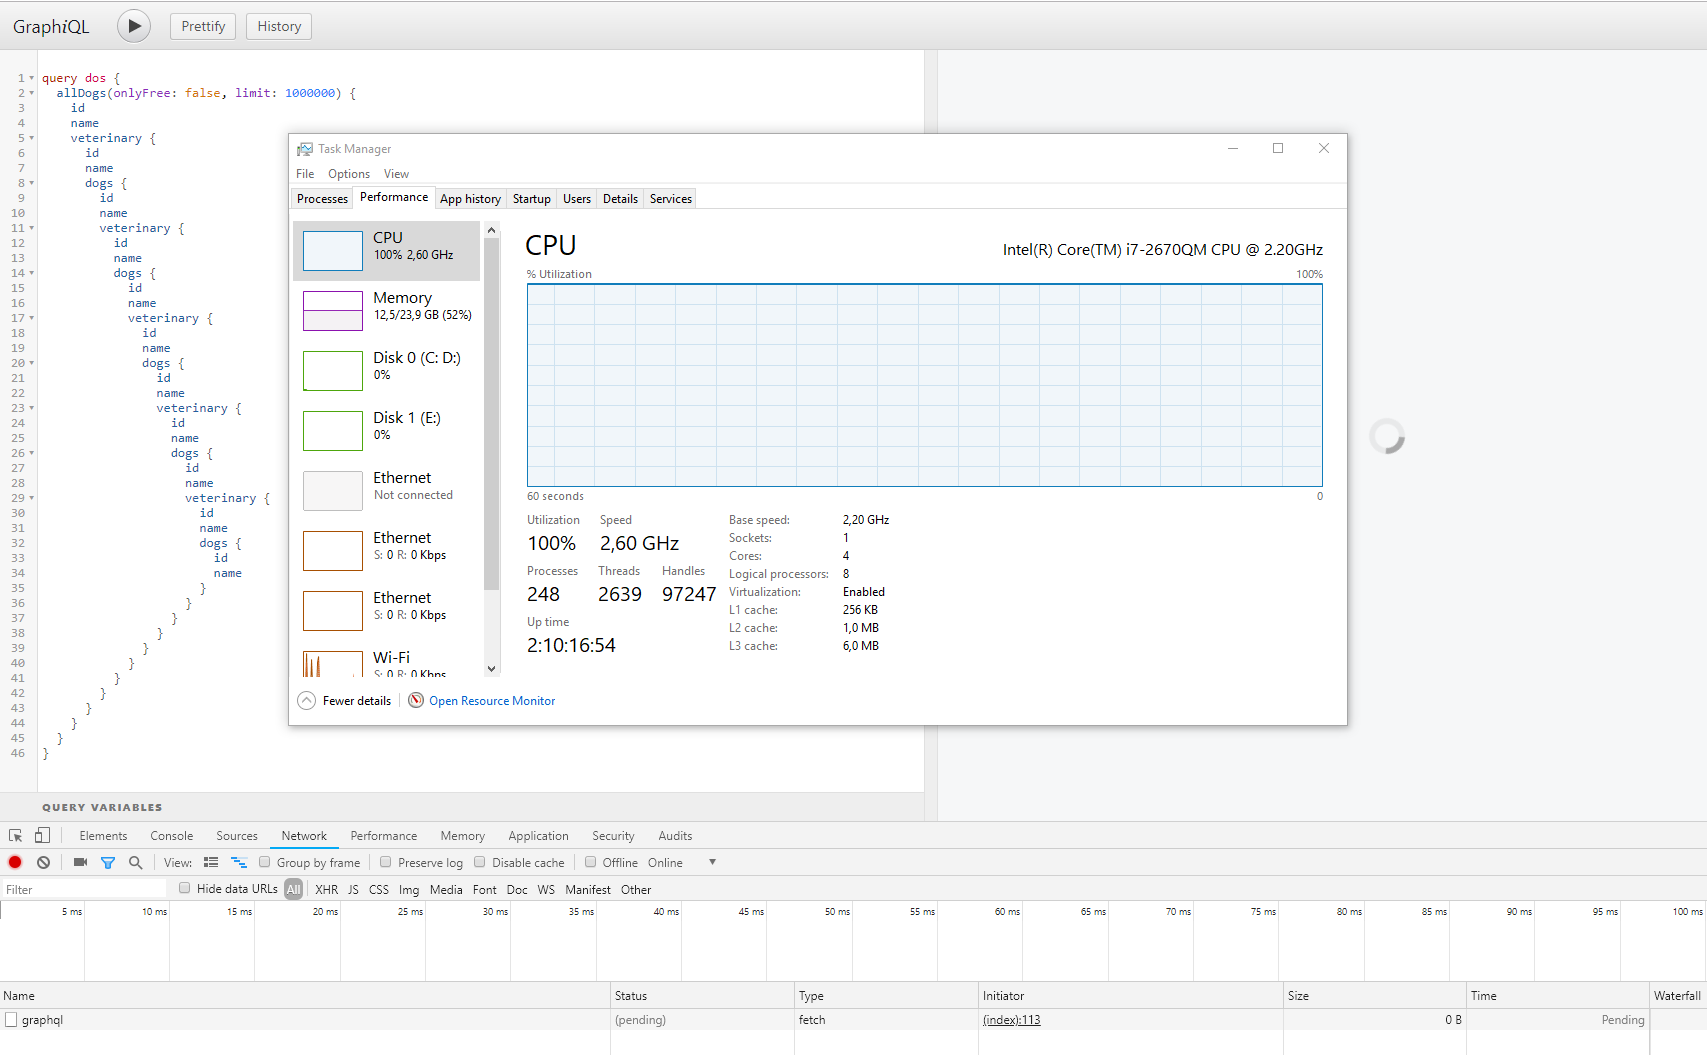
poc-graphql
 righettod/poc-graphql
Research on GraphQL from an AppSec point of view.
api-security-testingeducationlabs-practice+3
417
righettod/poc-graphqlResearch on GraphQL from an AppSec point of view.

 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
 sauravrao637/oproxy
Open-source MITM proxy to intercept, inspect, and mock network traffic.
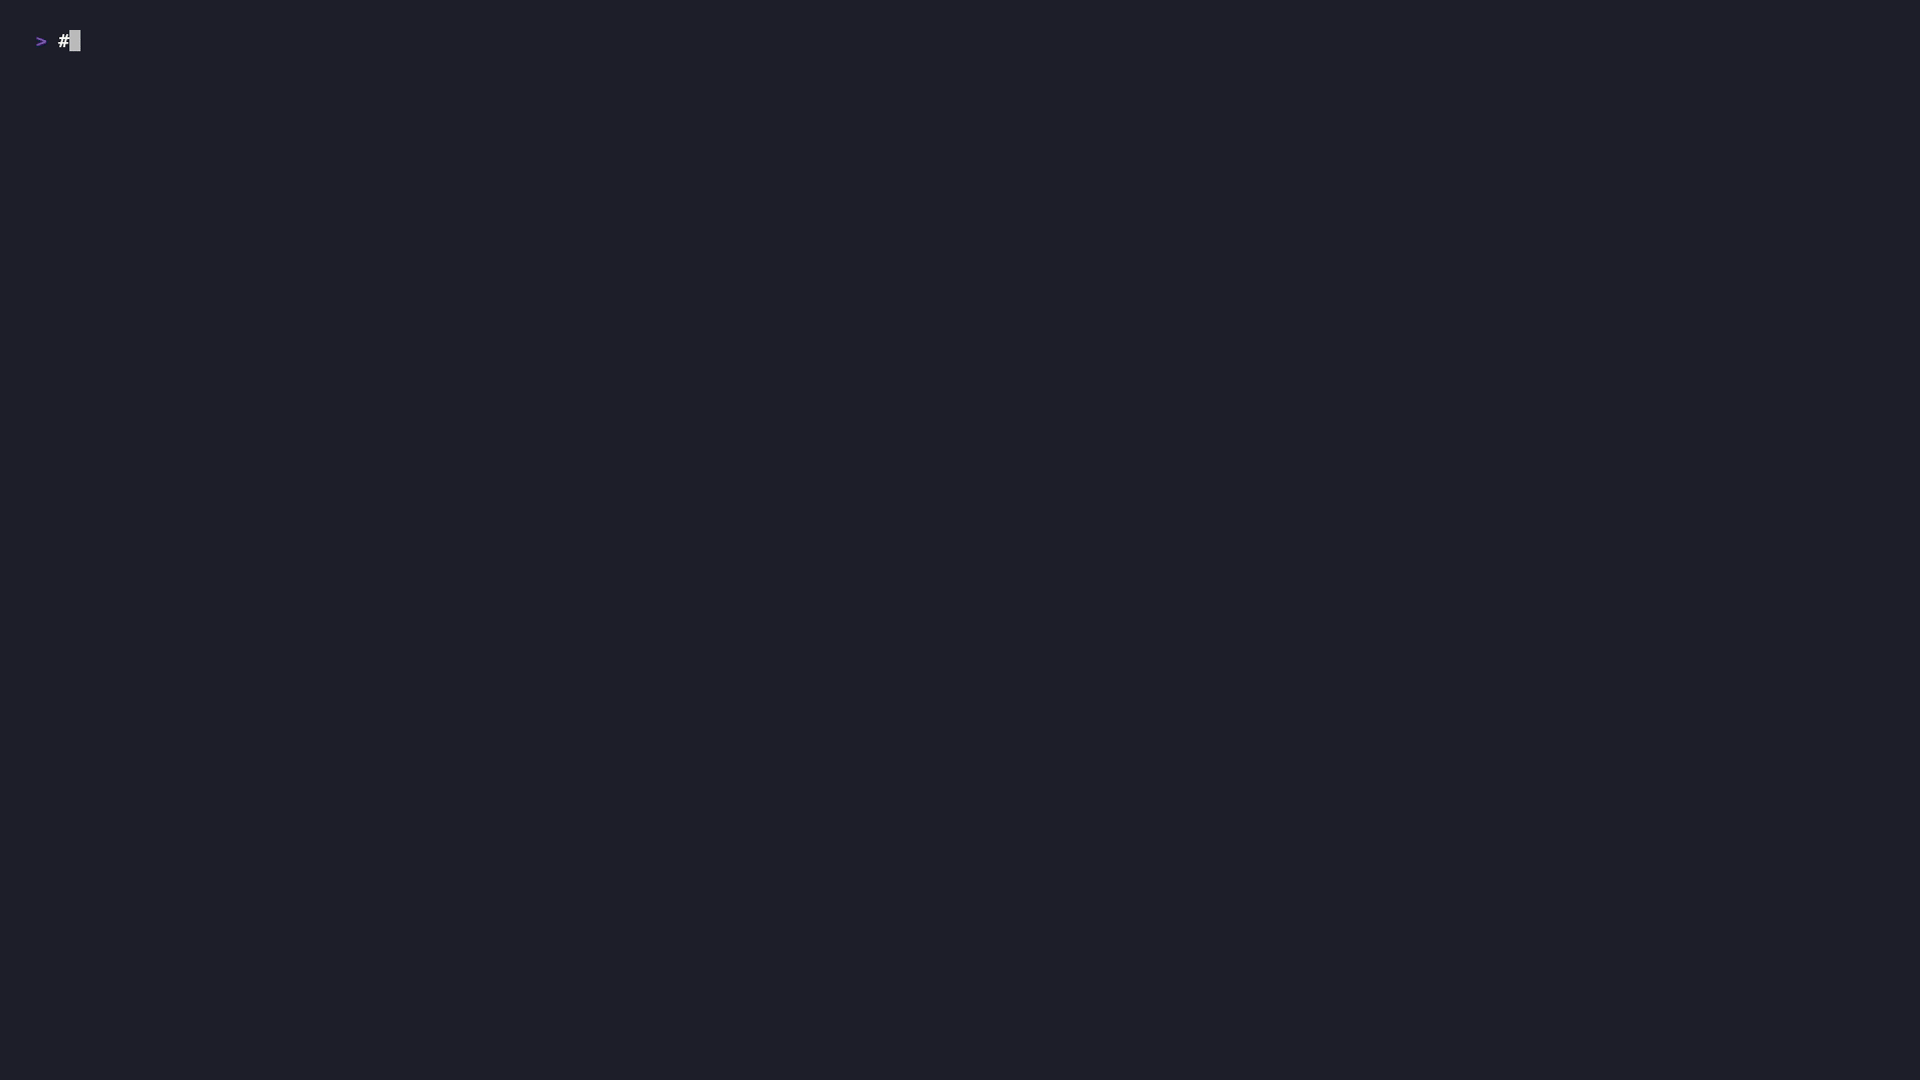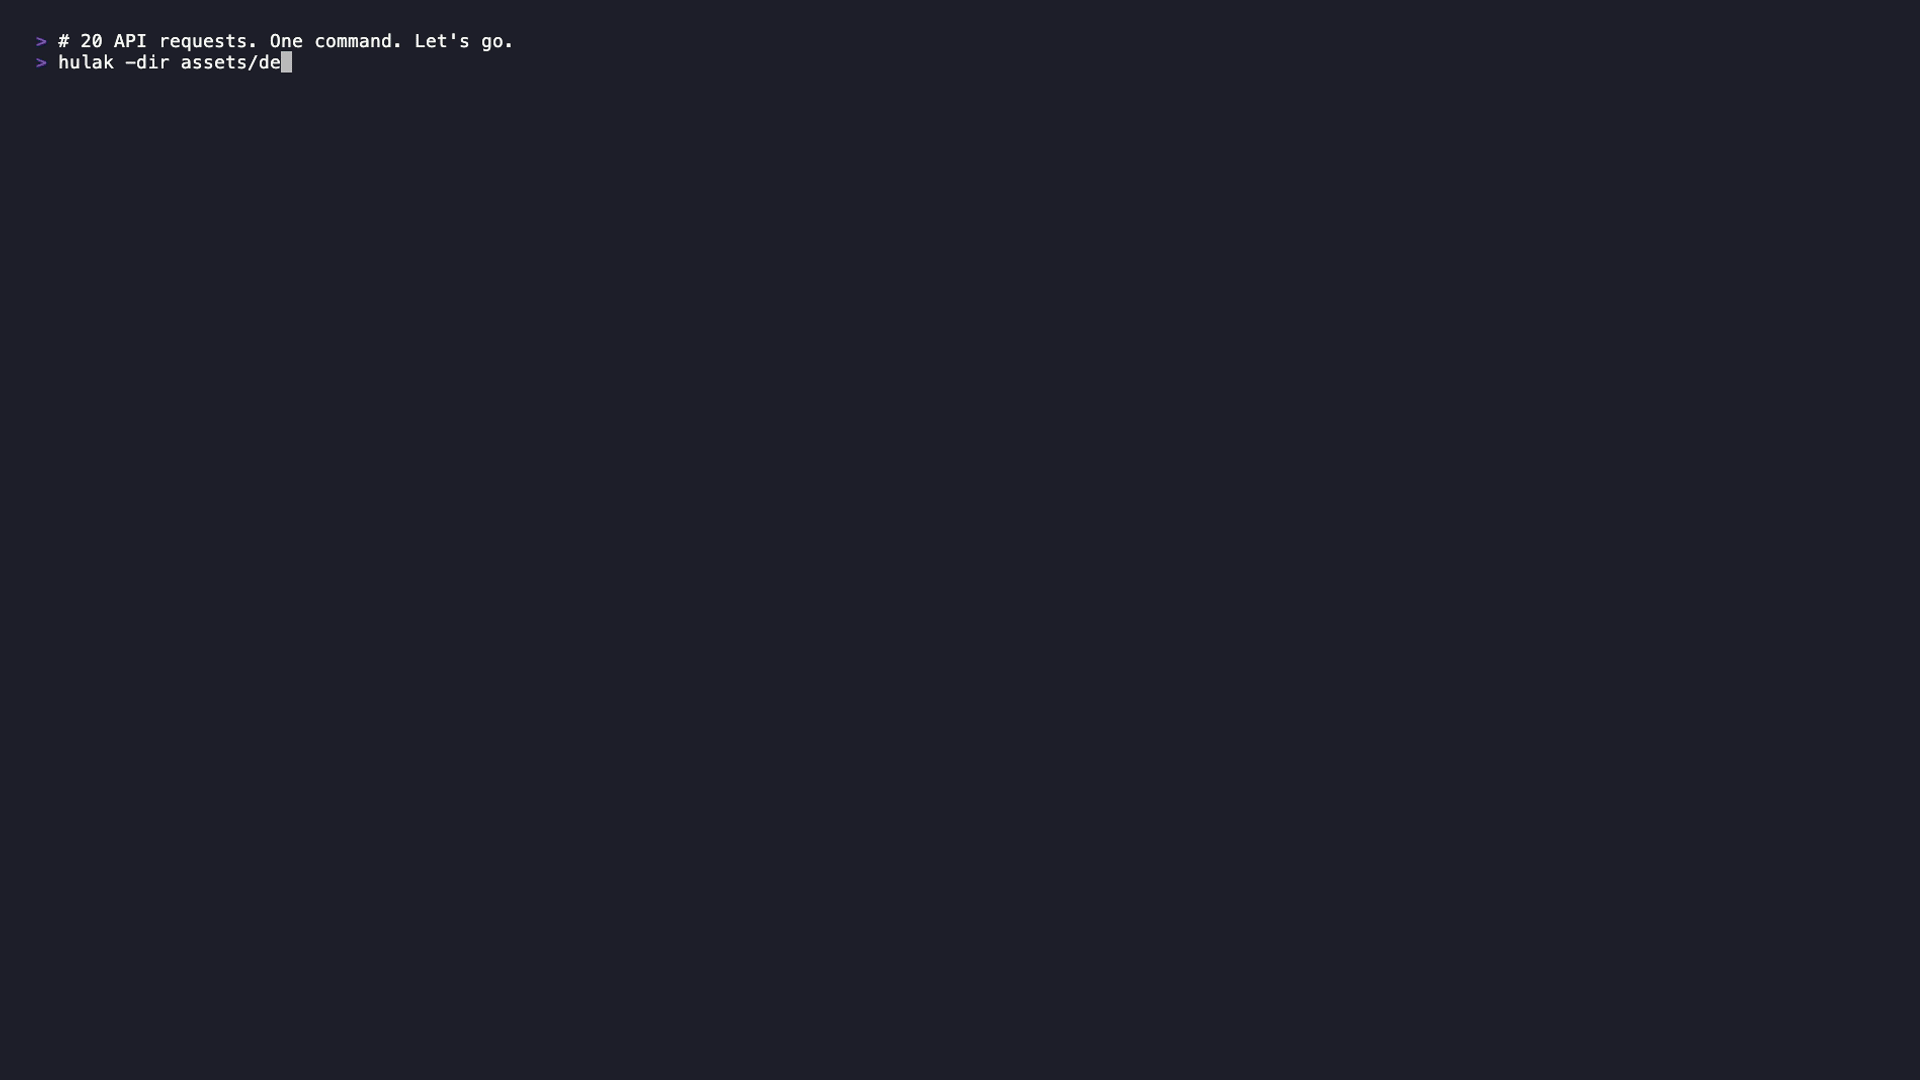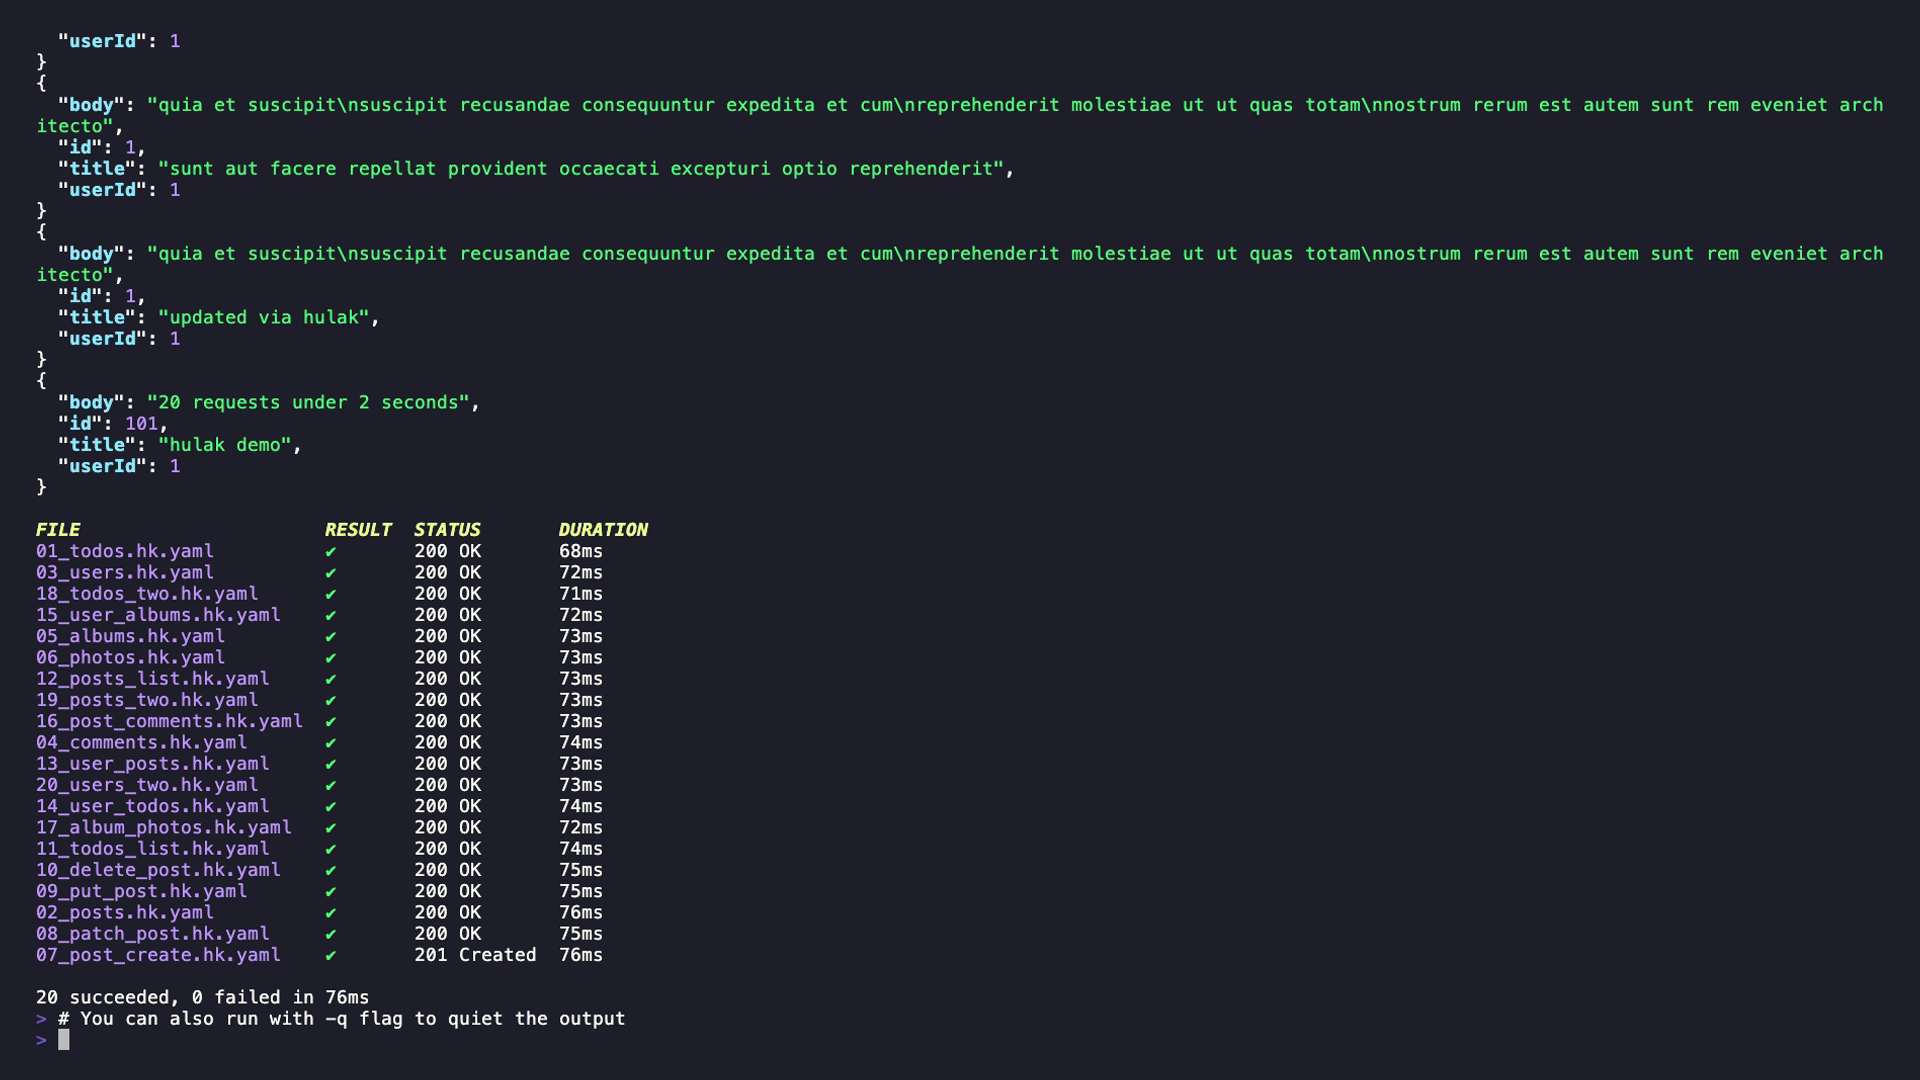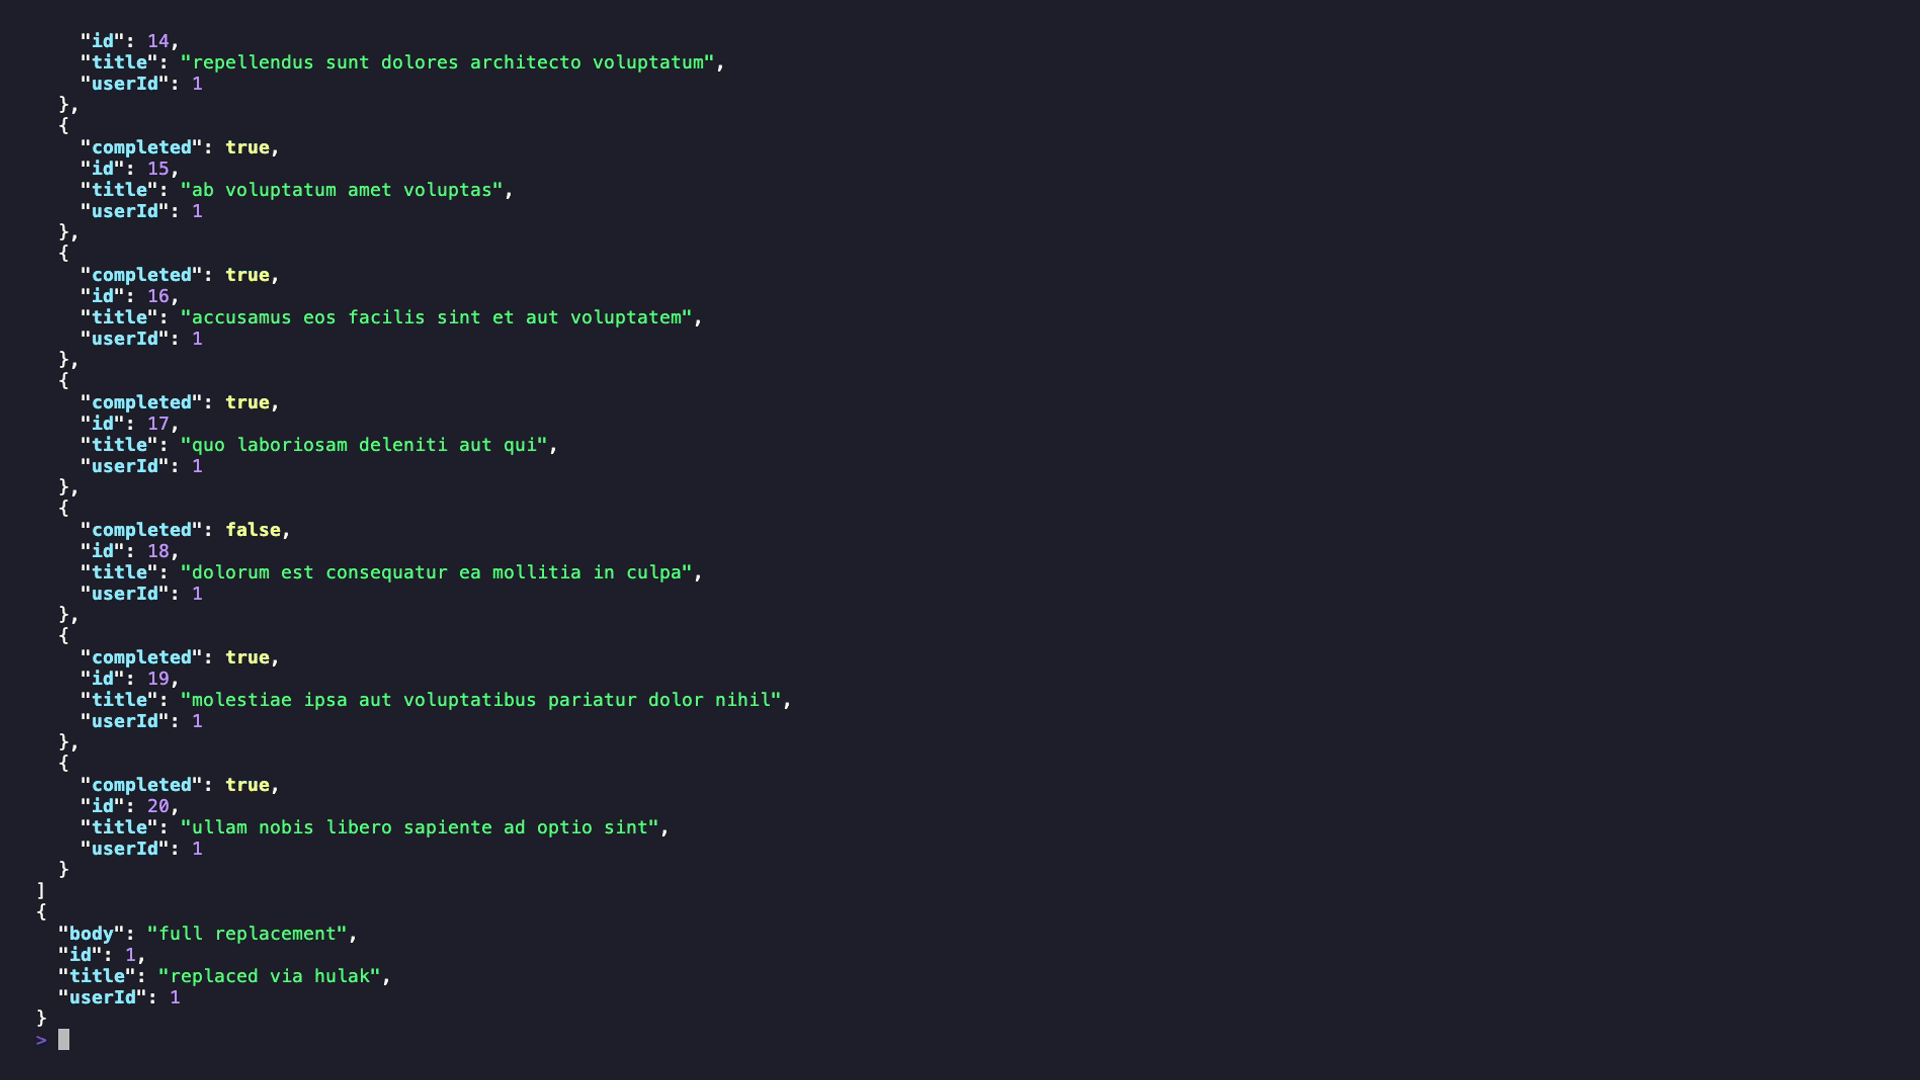 xaaha/hulak
A lightweight, file-based CLI API client with age-encrypted secrets, first-class GraphQL support, and a built-in MCP server for AI agent workflows.
 joanbono/gurp
Burp Commander written in Go
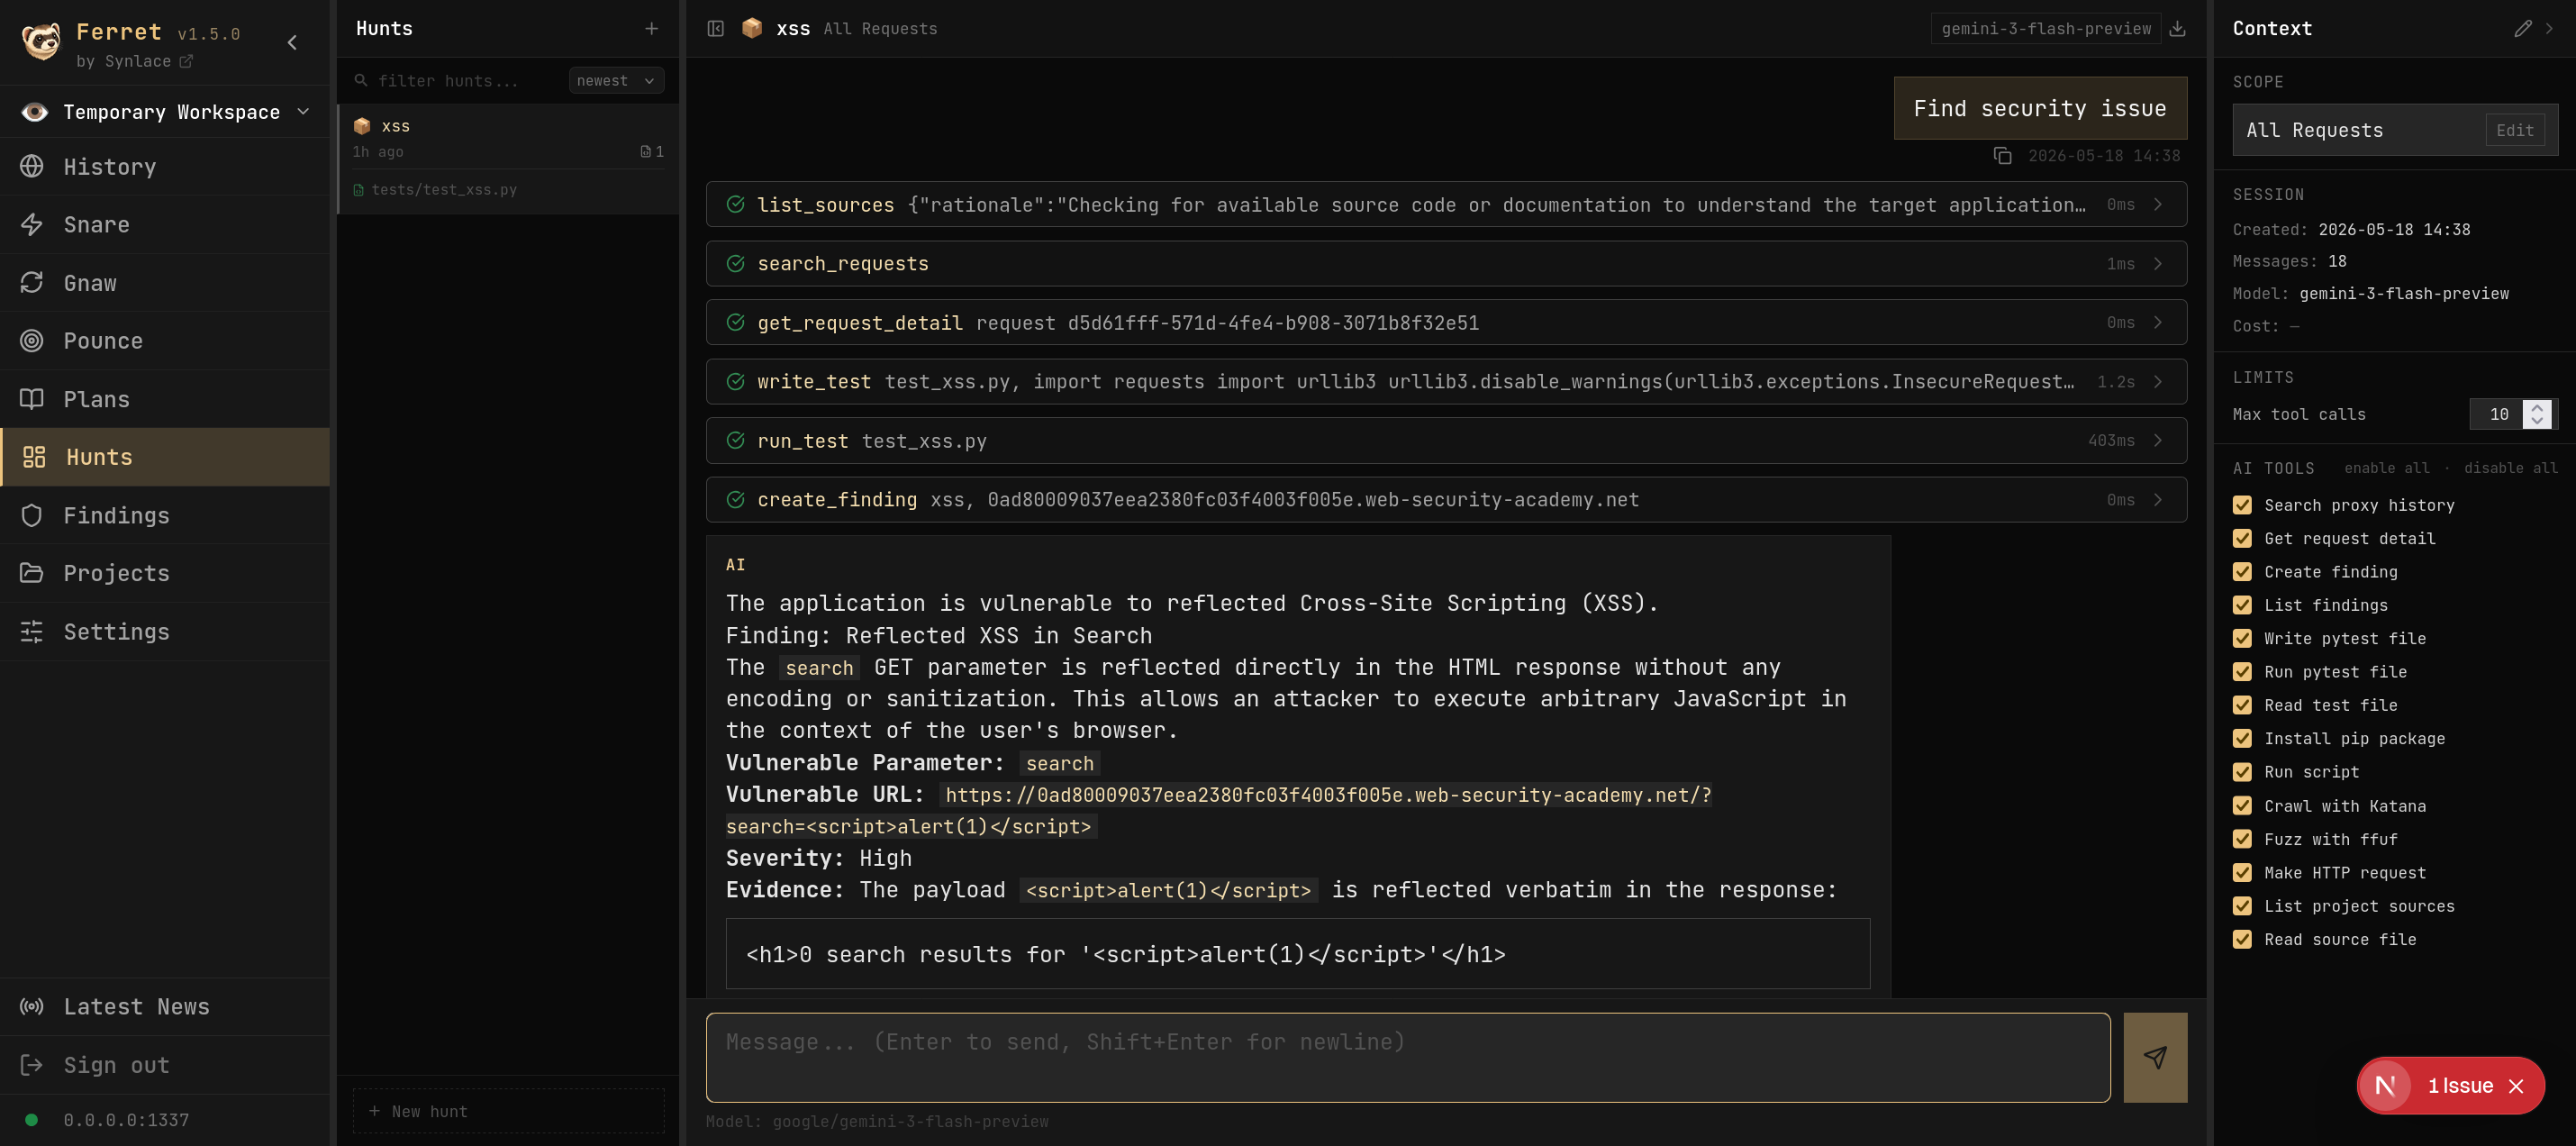 synlace/ferret
The collaborative web app pentest suite
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday
 bandit92/cve2022-1388_testapi
A Test API for testing the POC against CVE-2022-1388
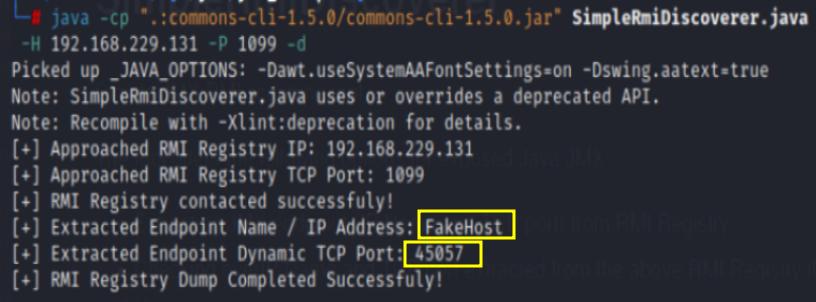 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
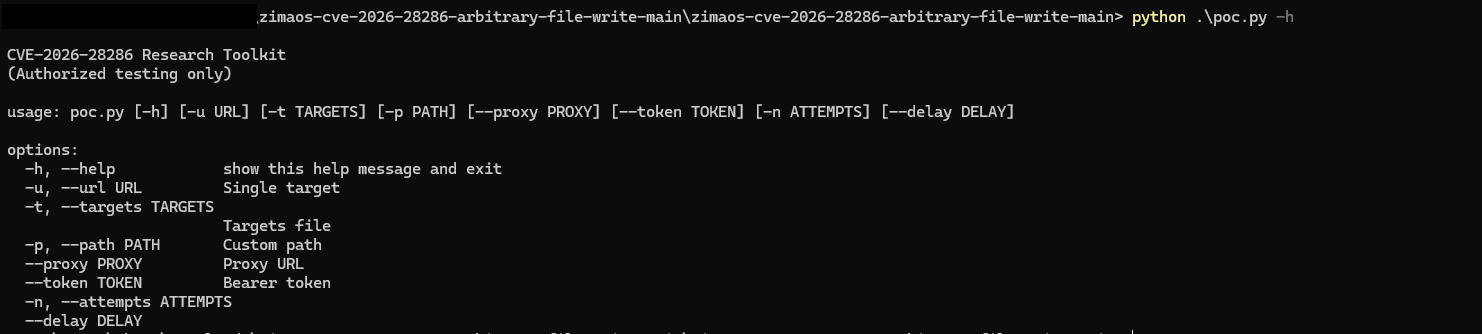 rushi9/zimaos-cve-2026-28286-arbitrary-file-write
PoC and verification toolkit for CVE-2026-28286, an arbitrary file write vulnerability in ZimaOS, exploiting API misconfiguration to write files…
 george0papasotiriou/cve-2026-5432-graphql-batching-alias-confusion-sql-injection
Demonstrates a critical GraphQL batching alias-confusion SQL injection (CVE-2026-5432) with a vulnerable Node.js server and Python exploit for…
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 mateustesser/cve-2023-31719
Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…