
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
38 results
CVE-2026-47101-PoC preview

CVE-2026-47101-PoC

GitHublearner202649/cve-2026-47101-poc

The code for personally reproducing the corresponding vulnerability
api-security-testingauthentication-authorizationeducation+7
5 months ago
spring-cloud__spring-cloud-gateway_CVE-2022-22947_3-0-6 preview

spring-cloud__spring-cloud-gateway_CVE-2022-22947_3-0-6

GitHubshoucheng3/spring-cloud__spring-cloud-gateway_cve-2022-22947_3-0-6

Spring Cloud Gateway repository demonstrating CVE-2022-22947 exploitation for API security testing and vulnerability analysis.
api-securityapi-security-testingexploitation+3
1 year ago
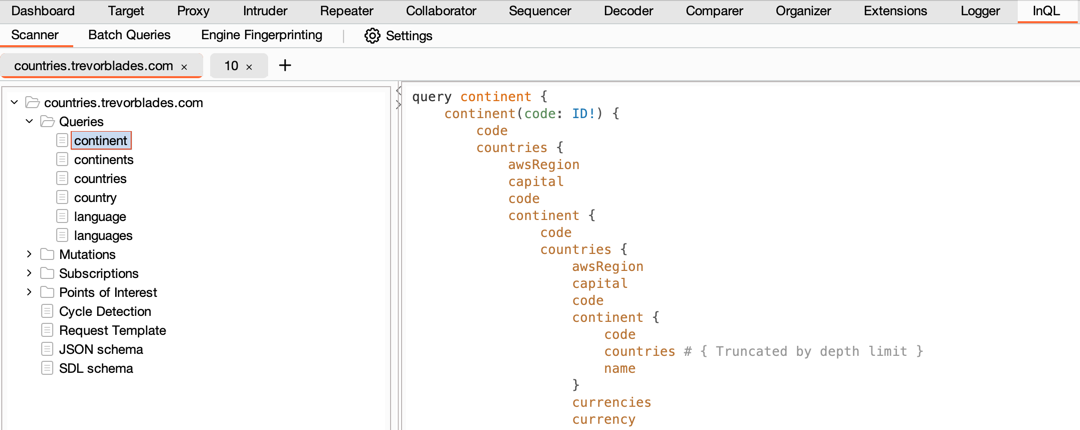
inql preview

inql

GitHubdoyensec/inql

InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…
api-security-testingpenetration-testingvulnerability-scanners
1.8k8 months ago
CVE-2026-30824-Flowise-NVIDIA-NIM-Authentication preview

CVE-2026-30824-Flowise-NVIDIA-NIM-Authentication

GitHubdylvie/cve-2026-30824-flowise-nvidia-nim-authentication

A proof-of-concept exploit for **CVE-2026-30824**, a critical authentication bypass vulnerability in Flowise that exposes NVIDIA NIM API endpoints…
api-security-testingexploitationpenetration-testing+3
6 months ago
yLog4j preview

yLog4j

GitHuby-security/ylog4j

PortSwigger Burp Plugin for the Log4j (CVE-2021-44228)

api-security-testingexploitationpenetration-testing+2
24 years ago
CVE-2024-50633 preview

CVE-2024-50633

GitHubcetinpy/cve-2024-50633

Proof-of-concept exploit for CVE-2024-50633, a Broken Object Level Authorization (BOLA) vulnerability in Indico v3.2.9–v3.3.2, enabling unauthorized…
api-security-testingexploitationinformation-gathering+3
1 year ago
Nmap-API preview

Nmap-API

GitHubmorpheuslord/nmap-api

RESTful API wrapping Nmap for automated network scanning, port detection, service enumeration, and vulnerability analysis with optional AI-powered…
api-security-testingnetwork-mappingosint+2
811 year ago
wpx preview

wpx

GitHubgreg-randall/wpx

Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…

api-security-testingcrawlerinformation-gathering+6
107 months ago
api-scanner-docker preview

api-scanner-docker

GitHubcspf-founder/api-scanner-docker

Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
api-securityapi-security-testingconfiguration-auditing+5
98 months ago
Damn-Vulnerable-GraphQL-Application preview

Damn-Vulnerable-GraphQL-Application

GitHubdolevf/damn-vulnerable-graphql-application

Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…

api-securityapi-security-testingctf+5
1.7k1 year ago
akca preview

akca

GitHubakha-security/akca

Evidence-oriented DAST scanner in Go that crawls web apps and APIs, then runs adaptive SQLi, XSS, RCE, SSRF, and auth checks with replayable proof.
api-security-testingdefensive-toolsdynamic-analysis-sandboxing+9
2519 days ago
CVE-2026-9830 preview

CVE-2026-9830

GitHubopaxial/cve-2026-9830

CVE-2026-9830 Proof of Concept
api-security-testingexploitationinformation-gathering+3
40012 days ago
bug-reaper preview

bug-reaper

GitHubshaniidev/bug-reaper

Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.

api-security-testingctfeducation+8
668 months ago
CVE-2025-61148 preview

CVE-2025-61148

GitHubsharma19d/cve-2025-61148

The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
api-security-testingeducationinformation-gathering+3
11 months ago
CVE-2025-51867 preview

CVE-2025-51867

GitHubsecsys-fdu/cve-2025-51867

Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…

api-security-testinginformation-gatheringpenetration-testing+3
1 year ago
SafeLine preview

SafeLine

GitHubchaitin/safeline

Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
anti-botapi-securityapi-security-testing+8
22.3k12 days ago
CVE-2025-53640 preview

CVE-2025-53640

GitHubrafaelcorvino1/cve-2025-53640

Broken Object Level Authorization (BOLA) in CERN's Indico leads to authenticated user enumeration.
api-security-testinginformation-gatheringosint+3
19 months ago
forticlient_ems_cve_2026_35616_poc.py preview

forticlient_ems_cve_2026_35616_poc.py

GitHubfevar54/forticlient_ems_cve_2026_35616_poc.py

PoC de CVE-2026-35616: control de acceso indebido en FortiClient EMS.

api-security-testingexploitationpenetration-testing+2
7 months ago
Previous123Next