
CVE-2023-32117
 randomrobbiebf/cve-2023-32117
Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints
api-security-testingexploitationinformation-gathering+3
6
randomrobbiebf/cve-2023-32117Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints
 7h30th3r0n3/cve-2026-53625-glpi-poc
GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…
 razureink/arisu
Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…
 ebrasha/abdal-cve-2026-63030
Abdal CVE-2026-63030 is a professional WordPress vulnerability scanner designed to detect exposure to CVE-2026-63030 through version analysis and…
 dylvie/cve-2026-30824-flowise-nvidia-nim-authentication
A proof-of-concept exploit for **CVE-2026-30824**, a critical authentication bypass vulnerability in Flowise that exposes NVIDIA NIM API endpoints…
 alt3kx/cve-2018-7691
The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10
 alt3kx/cve-2018-7690
The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10
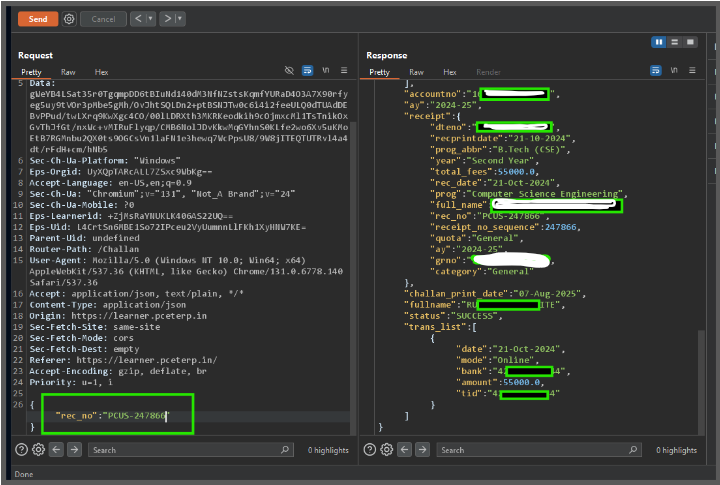 sharma19d/cve-2025-61148
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
 jfriedli/cve-2025-6792
Proof-of-concept exploit for CVE-2025-6792 demonstrating unauthorized Pusher channel subscription and event eavesdropping in a WordPress plugin via…
 adelittle/cve-2021-4191_exploits
Exploit script for CVE-2021-4191 that enumerates GitLab users via the GraphQL API, useful for security assessments and validating exposure.
 secsys-fdu/cve-2025-51867
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…
 cetinpy/cve-2024-50633
Proof-of-concept exploit for CVE-2024-50633, a Broken Object Level Authorization (BOLA) vulnerability in Indico v3.2.9–v3.3.2, enabling unauthorized…
 androidhooker/hooker
Hooker is an opensource project for dynamic analyses of Android applications. This project provides various tools and applications that can be use to…
 opaxial/cve-2026-9830
CVE-2026-9830 Proof of Concept
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
 bishopfox/snowpick
find sensitive data leaking from ServiceNow instances.
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 k3ystr0k3r/cve-2021-4191-exploit
A PoC exploit for CVE-2021-4191 - GitLab User Enumeration.