square__retrofit_CVE-2018-1000850_2-4-0

Type-safe HTTP client library for Android and Java, enabling REST API communication with annotation-based request configuration and converter support.

Type-safe HTTP client library for Android and Java, enabling REST API communication with annotation-based request configuration and converter support.
Spring Cloud Config CVE-2019-3799|CVE_2020_5410 漏洞检测

Type-safe HTTP client for Android and Java with annotation-based API binding, converter support, and integration with OkHttp for network…

Burp Suite extension that intercepts requests and sends them over HTTP/3, converting responses back for Burp, with support for kettled requests and…

Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…

Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.

CVE-2025-41090 (brokeCLAUDIA): Broken access control in microCLAUDIA, the anti-ransomware platform by CCN-CERT.

Martian is a library for building custom HTTP/S proxies

GraphQL automated security testing toolkit

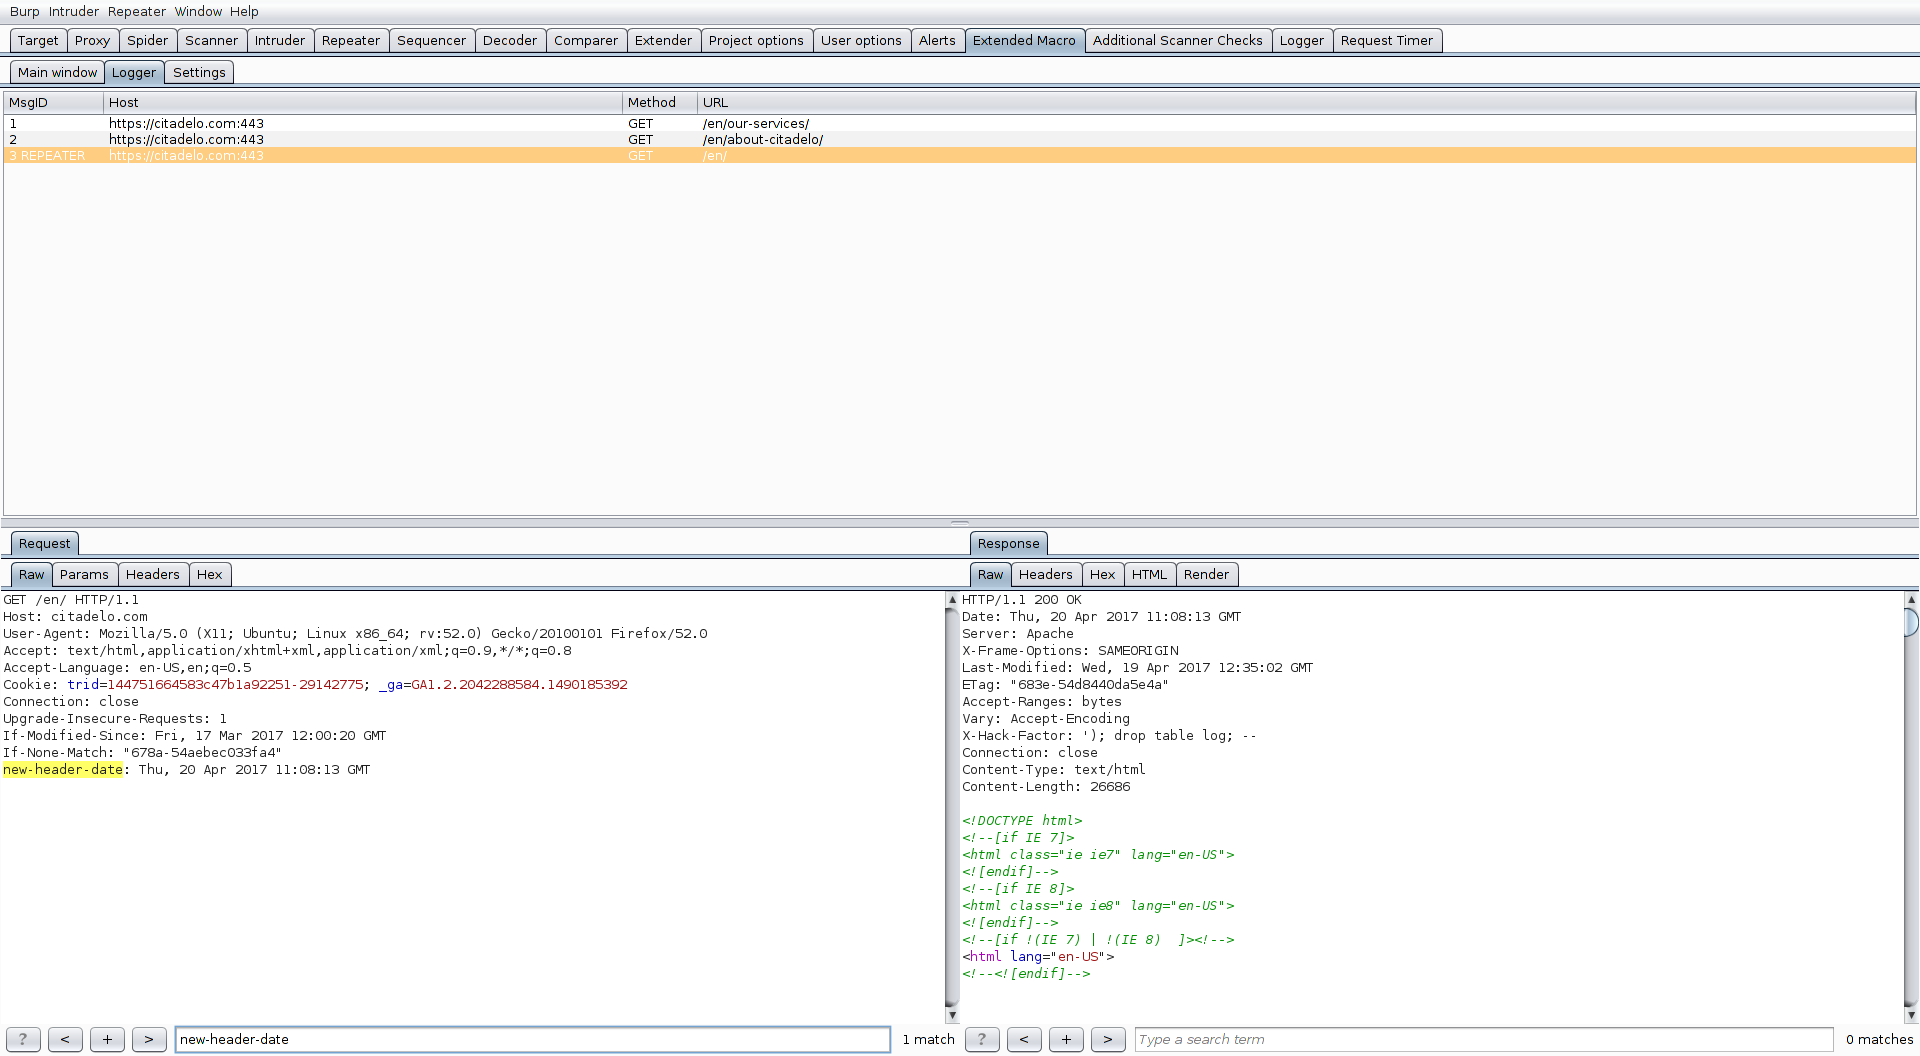
ExtendedMacro - BurpSuite plugin providing extended macro functionality

This experimetal fuzzer is meant to be used for API in-memory fuzzing.

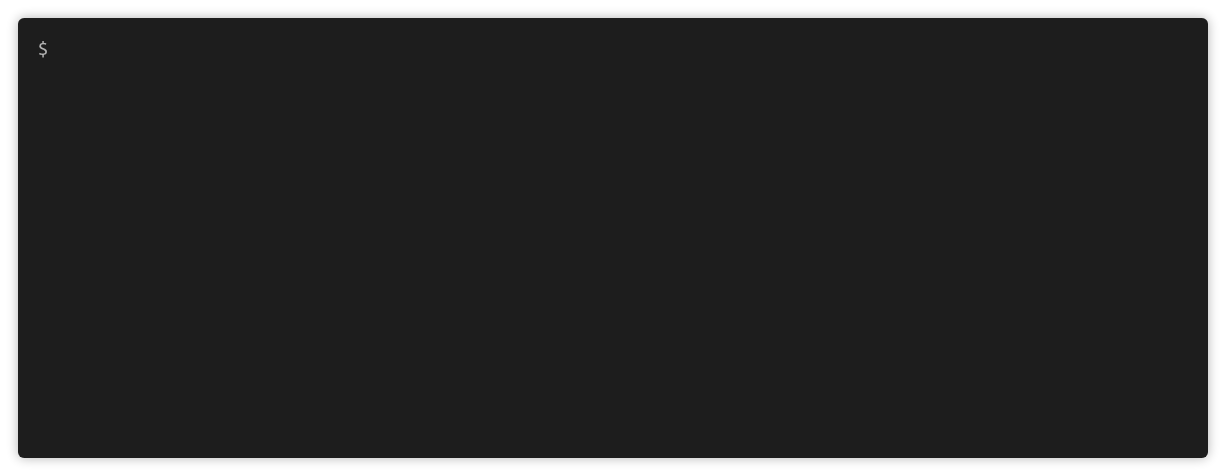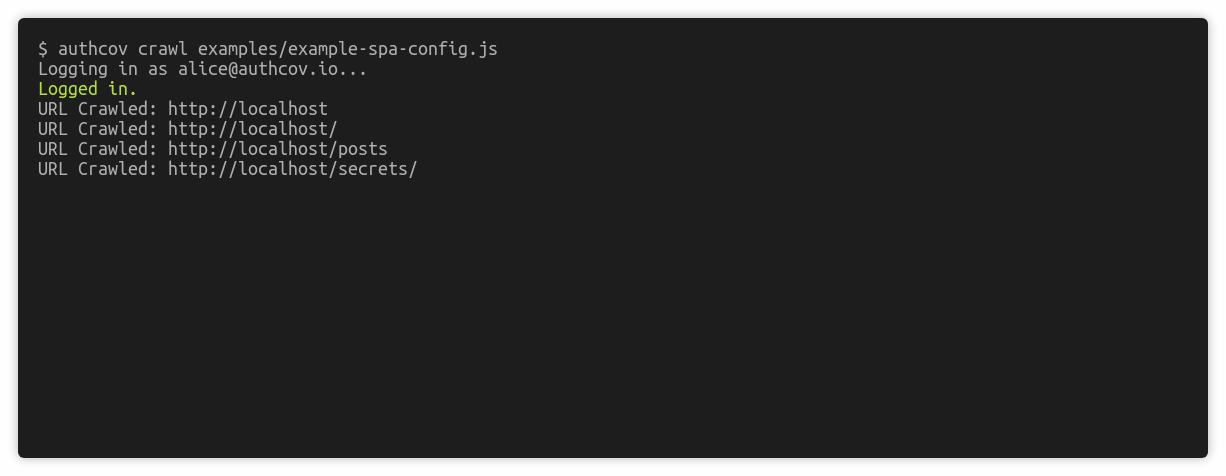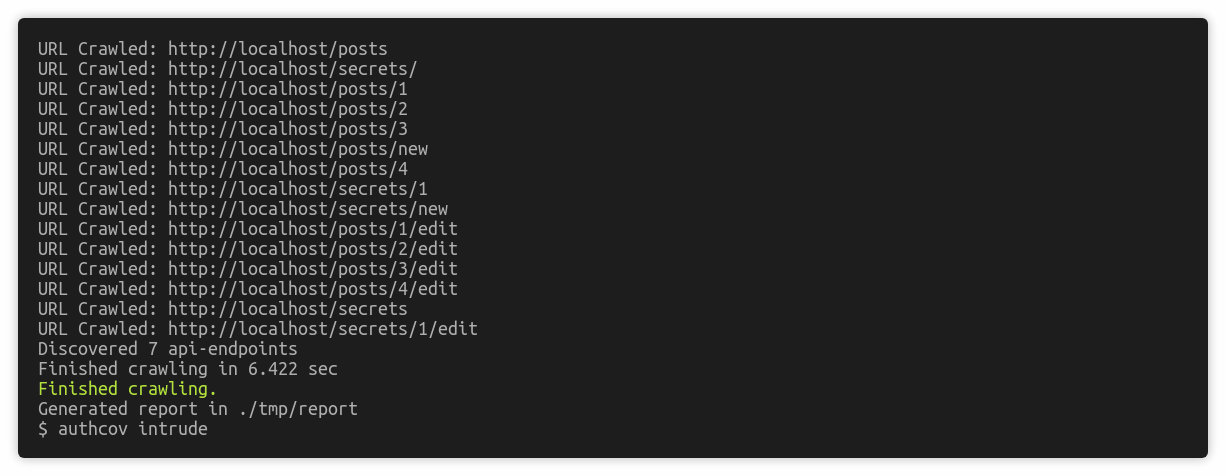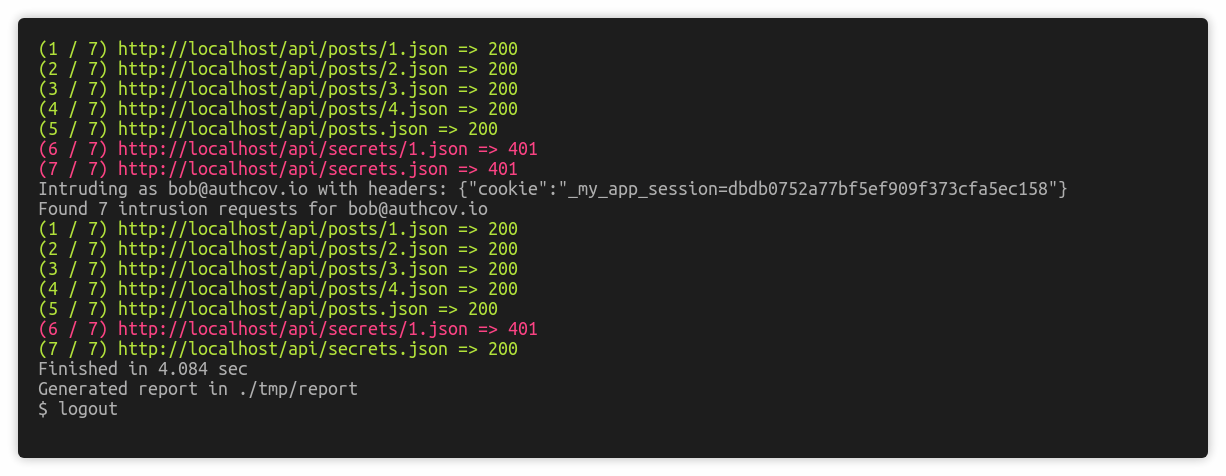
Web app authorisation coverage scanning

Http request smuggling vulnerability scanner

Hackable HTTP proxy for resiliency testing and simulated network conditions

API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…

A modern vulnerable web app

Python API security testing tool from OpenStack Security Group

REST/JSON API to the Burp Suite security tool.