

CVE-2024-9707
 randomrobbiebf/cve-2024-9707
Hunk Companion <= 1.8.4 - Missing Authorization to Unauthenticated Arbitrary Plugin Installation/Activation
api-security-testingexploitationpenetration-testing+3
1
randomrobbiebf/cve-2024-9707Hunk Companion <= 1.8.4 - Missing Authorization to Unauthenticated Arbitrary Plugin Installation/Activation
 randomrobbiebf/cve-2024-51665
Magical Addons For Elementor <= 1.2.1 - Authenticated (Subscriber+) Server-Side Request Forgery
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 filipegaudard/cve-2026-24134-poc
Proof-of-concept exploit for CVE-2026-24134, a Broken Object Level Authorization vulnerability in StudioCMS, demonstrating unauthorized access to…
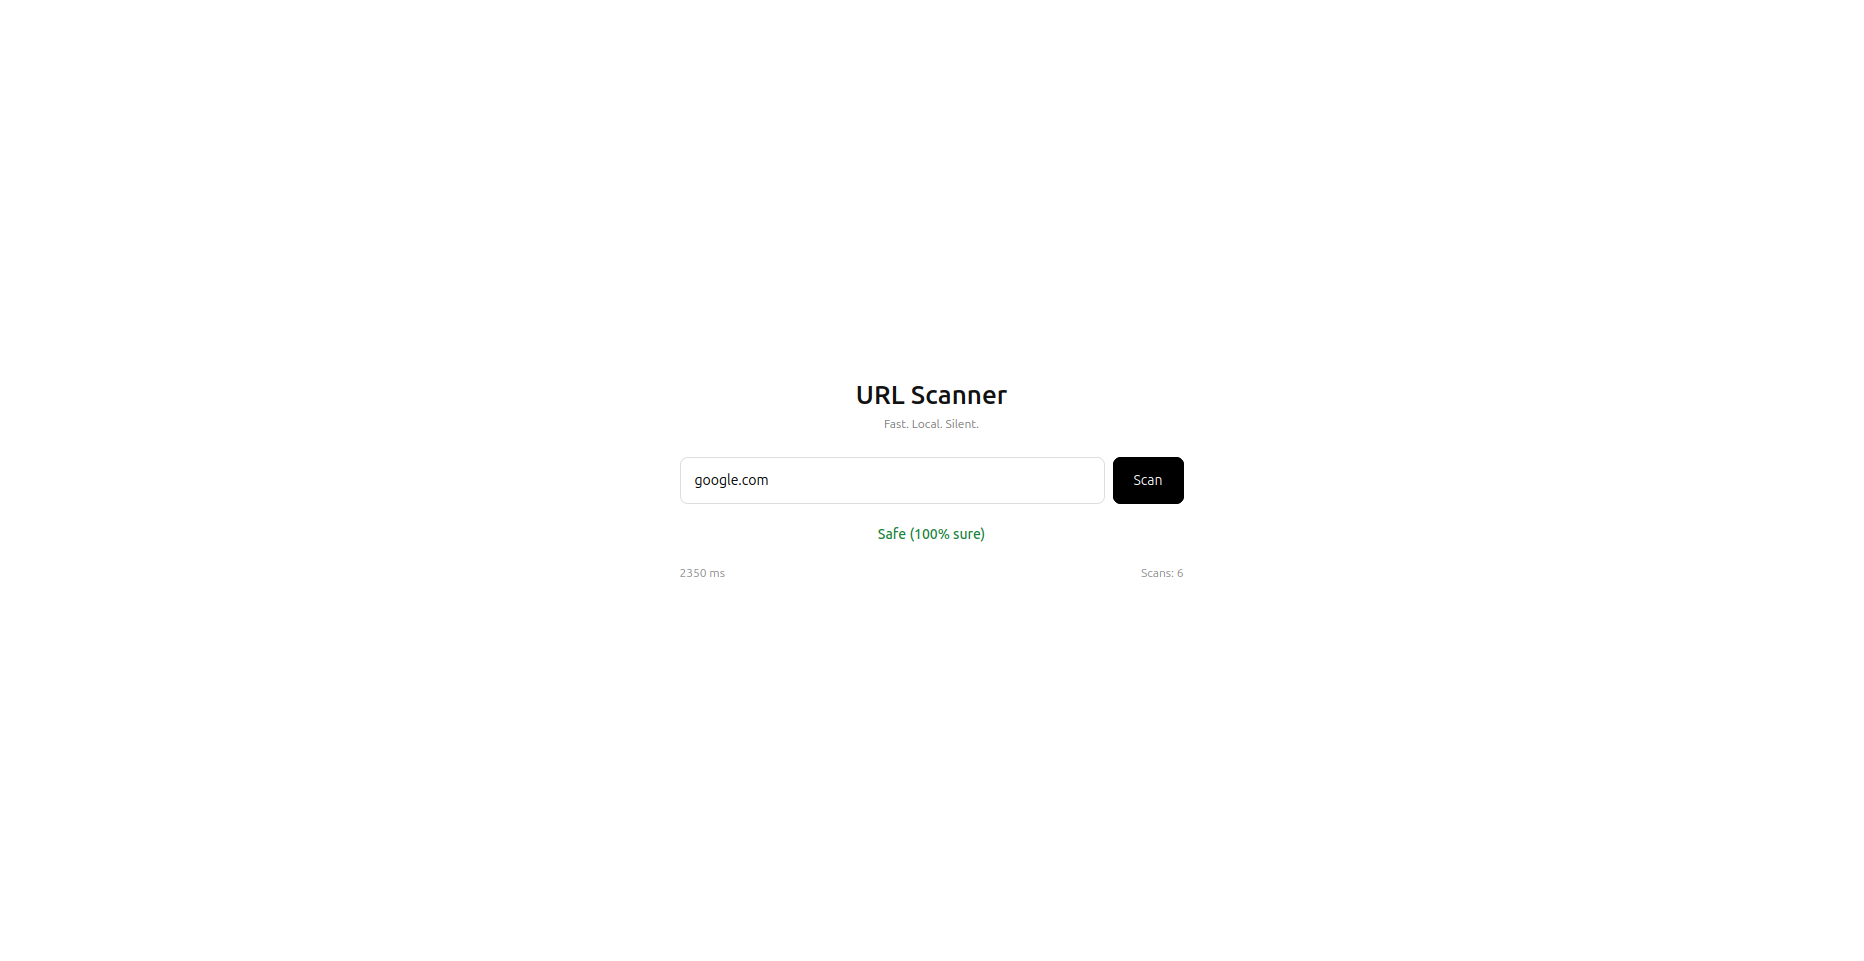 mannansainicyber/url_checker
Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
 filipegaudard/cve-2026-30944-poc
Python proof-of-concept for CVE-2026-30944, exploiting a BOLA vulnerability in StudioCMS to escalate privileges via insecure API token generation.
 sharma19d/cve-2025-61148
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
 jfriedli/cve-2025-6783
Proof-of-concept exploit for CVE-2025-6783 demonstrating SQL injection via crafted HTTP headers and JSON payload against WordPress GoZen Forms REST…
 jfriedli/cve-2025-6792
Proof-of-concept exploit for CVE-2025-6792 demonstrating unauthorized Pusher channel subscription and event eavesdropping in a WordPress plugin via…
 jfriedli/cve-2025-11771
Proof-of-concept exploit for CVE-2025-11771 demonstrating unauthenticated sale record creation via a WordPress REST API endpoint, with browser…
 mxm0z/r2s
A web-based vulnerability scanner for CVE-2025-55182, a critical Remote Code Execution (RCE) vulnerability in React Server Components.
 d0n601/cve-2025-12720
g-FFL Cockpit <= 1.7.1 - Improper Authorization to Unauthenticated Product Deletion
 fuyuooumi1027/cve-2023-45857-demo
Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…
 adelittle/cve-2021-4191_exploits
Exploit script for CVE-2021-4191 that enumerates GitLab users via the GraphQL API, useful for security assessments and validating exposure.
 clemfavre/cve-2023-45612_exploit
Reproduction of a high severty security problem that allows XXE (XML eXternal Entity) attacks on Ktor's XML serialization.
 prestonhashworth/cve-2025-55182
CVE-2025-55182 testing toolkit with Postman collection, cURL examples, and F5 WAF signature validation for vulnerability assessment and protection…
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 secsys-fdu/cve-2025-51867
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…