
BadHost-CVE-2026-48710-Exploit
 bhanunamikaze/badhost-cve-2026-48710-exploit
Detection scanner for CVE-2026-48710 - Host-header auth bypass in Starlette/FastAPI
api-security-testingauthentication-authorizationexploitation+4
1
bhanunamikaze/badhost-cve-2026-48710-exploitDetection scanner for CVE-2026-48710 - Host-header auth bypass in Starlette/FastAPI
 amnnrth/cve-2025-34291_cors_security_scanner
A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.
 rachidafaf/bola-cve-2023-27524
Demonstrates CVE-2023-27524 Broken Object Level Authorization (BOLA) vulnerability with vulnerable and fixed Flask API implementations for security…
 n0xdaemon/cve-2026-19478
Provides PoC exploits and root-cause analysis for two GitLab GraphQL `@gl_introduced` directive vulnerabilities: unauthenticated method execution and…
 jvr2022/cve-2026-25126
Proof-of-concept for CVE-2026-25126 demonstrating vote count manipulation in PolarLearn via improper runtime validation of the forum vote direction…
 randomrobbiebf/cve-2024-9707
Hunk Companion <= 1.8.4 - Missing Authorization to Unauthenticated Arbitrary Plugin Installation/Activation
 ronf98/cve-2024-11972-poc
CVE-2024-11972 in Hunk Companion <1.9.0 allows unauthenticated attackers to exploit insecure REST API endpoints and install vulnerable plugins,…
 talentsec/spring-cloud-gateway-cve-2022-22947
Spring-Cloud-Gateway-CVE-2022-22947
 randomrobbiebf/cve-2024-51665
Magical Addons For Elementor <= 1.2.1 - Authenticated (Subscriber+) Server-Side Request Forgery
 alt3kx/cve-2018-7691
The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10
 alt3kx/cve-2018-7690
The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 fevar54/forticlient_ems_cve_2026_35616_poc.py
PoC de CVE-2026-35616: control de acceso indebido en FortiClient EMS.
 mannansainicyber/url_checker
Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
 diegobaelen/cve-2026-26012
Proof-of-concept exploit for CVE-2026-26012, demonstrating an authenticated organization collection permissions bypass and cipher enumeration in…
 mxm0z/r2s
A web-based vulnerability scanner for CVE-2025-55182, a critical Remote Code Execution (RCE) vulnerability in React Server Components.
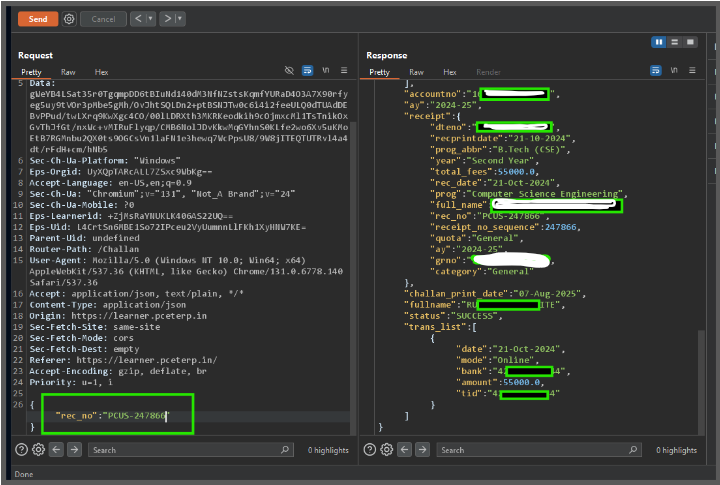 sharma19d/cve-2025-61148
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
 filipegaudard/cve-2026-30944-poc
Python proof-of-concept for CVE-2026-30944, exploiting a BOLA vulnerability in StudioCMS to escalate privileges via insecure API token generation.