
yLog4j
 y-security/ylog4j
PortSwigger Burp Plugin for the Log4j (CVE-2021-44228)
api-security-testingexploitationpenetration-testing+2
2
y-security/ylog4jPortSwigger Burp Plugin for the Log4j (CVE-2021-44228)
 learner202649/cve-2026-47101-poc
The code for personally reproducing the corresponding vulnerability
 adelittle/cve-2021-4191_exploits
Exploit script for CVE-2021-4191 that enumerates GitLab users via the GraphQL API, useful for security assessments and validating exposure.
 clemfavre/cve-2023-45612_exploit
Reproduction of a high severty security problem that allows XXE (XML eXternal Entity) attacks on Ktor's XML serialization.
 mateustesser/cve-2023-31719
Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…
 aureum01/cve-2023-23752
A bash automation that exploits the vulnerable endpoints for the Joomla! API 4.0 - 4.2.7
 osirium/suds
Clone of suds 0.4 + suds-0.4-CVE-2013-2217.patch
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
 thoropass-public/area51
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 themalwareguardian/brokeclaudia
CVE-2025-41090 (brokeCLAUDIA): Broken access control in microCLAUDIA, the anti-ransomware platform by CCN-CERT.
 purpleteam-labs/purpleteam-server-scanner
Server scanning component of purpleteam
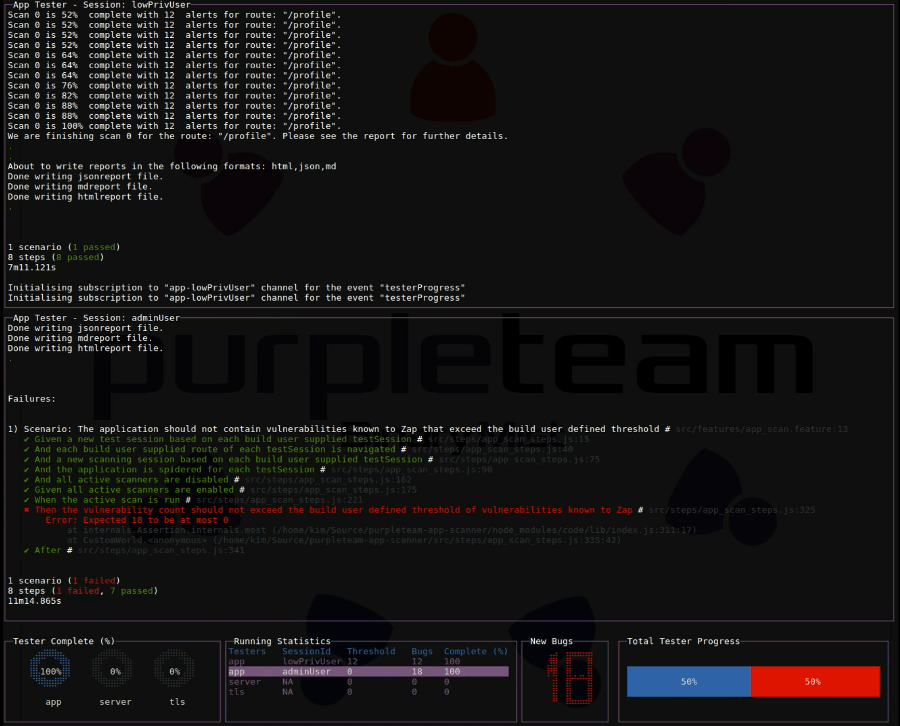 purpleteam-labs/purpleteam
CLI component of purpleteam
 purpleteam-labs/purpleteam-app-scanner
Application scanning component of purpleteam
 semgrep/semgrep
Lightweight static analysis for many languages. Find bug variants with patterns that look like source code.
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
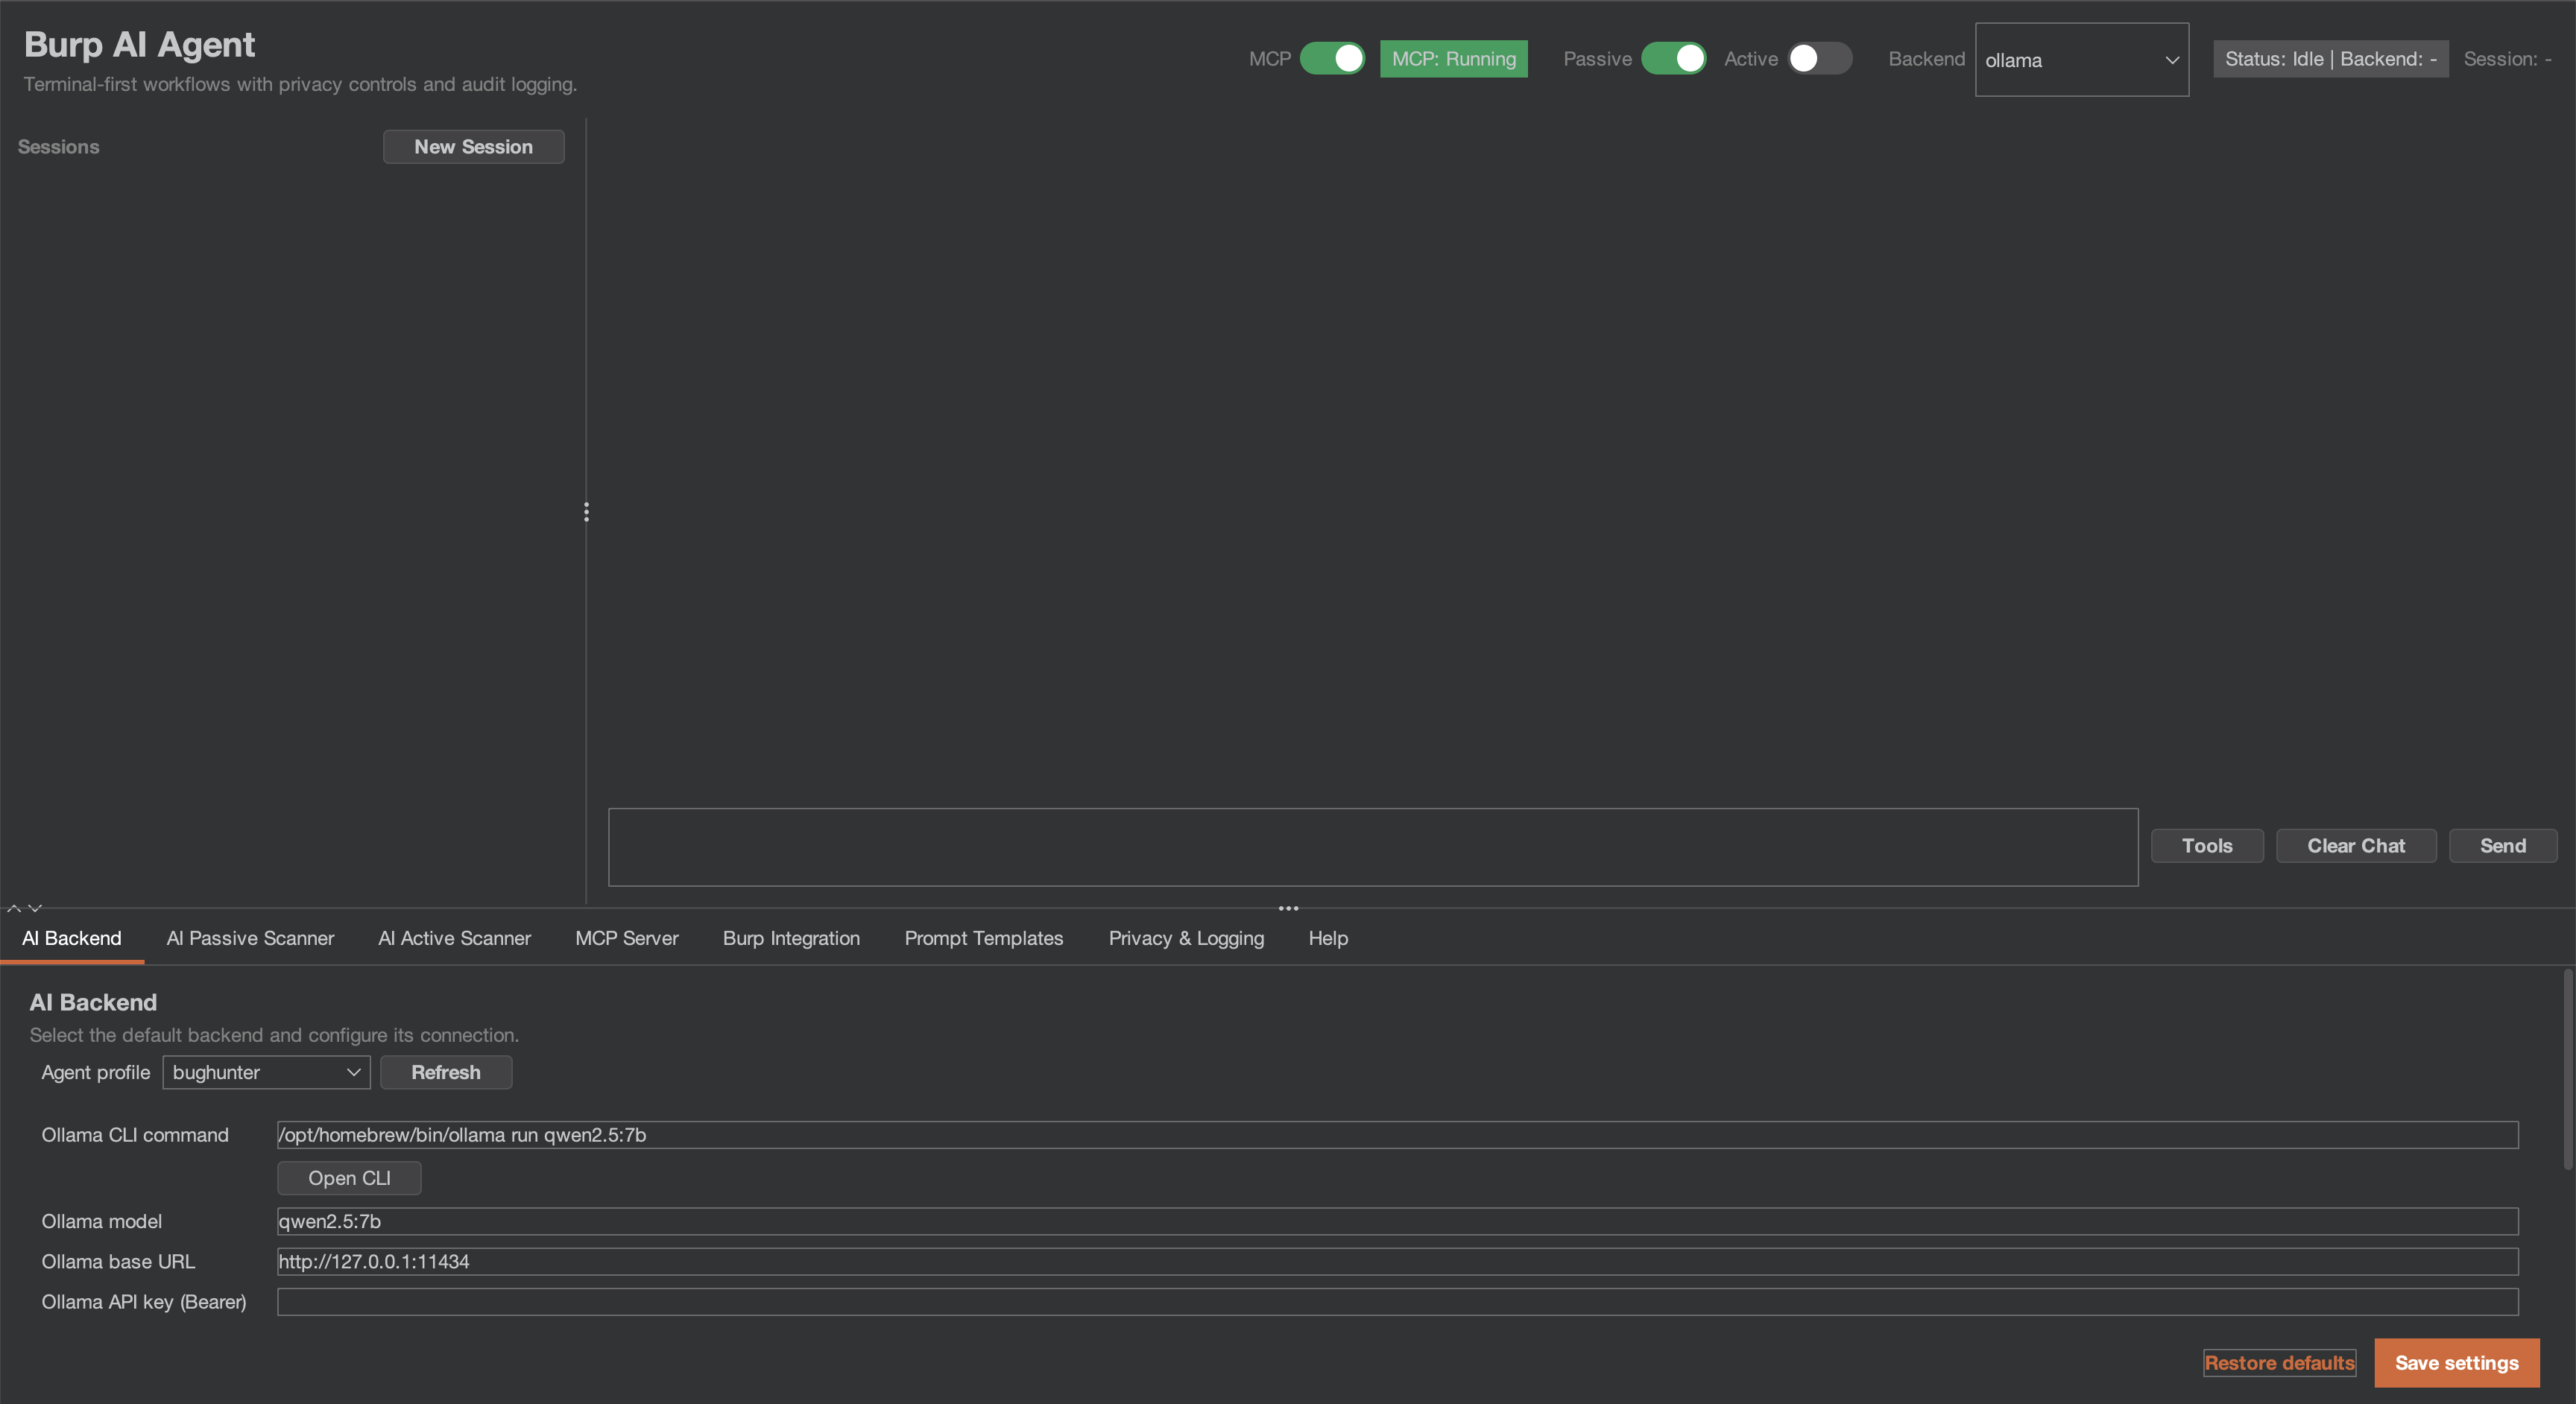 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more