
CVE-2026-9198
 k3ystr0k3r/cve-2026-9198
PoC and detection guide for the critical unauthenticated RCE in IBM Langflow OSS, covering the auto_login token bypass and unsafe /validate/code…
api-security-testingexploitationpenetration-testing+2
1
k3ystr0k3r/cve-2026-9198PoC and detection guide for the critical unauthenticated RCE in IBM Langflow OSS, covering the auto_login token bypass and unsafe /validate/code…
 saboor-hakimi/cve-2023-23752
CVE-2023-23752 nuclei template
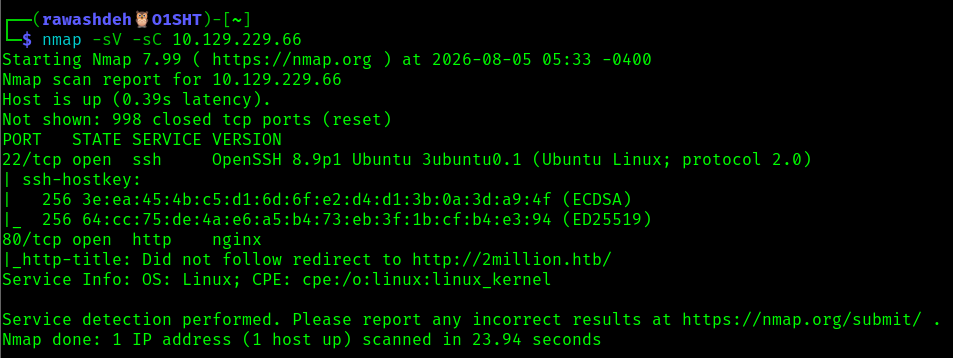 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 ridhinva/langflow-cors-scanner
Scanner: CVE-2025-34291 Langflow Origin Validation Error / CORS Misconfiguration — Python checker (CISA KEV)
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 randomrobbiebf/cve-2024-11423
Ultimate Gift Cards for WooCommerce <= 3.0.6 - Missing Authorization to Infinite Money Glitch
 bishopfox/cve-2026-35616-check
Non-destructive scanner for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Detects vulnerability by comparing HTTP responses…
 murataydemir/cve-2016-4014
[CVE-2016-4014] SAP Netweaver AS JAVA UDDI Component XML External Entity (XXE)
 fopje/cve-2022-36539
Insecure Permissions WeDayCare
 renzi25031469/cve-2026-19478
Detects CVE-2026-19478 in GitLab CE/EE with a non-destructive Nuclei template that triggers the GraphQL fallback-field method invocation via touch…
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 cve-2023-49954/cve-2023-49954.github.io
SQL Injection in 3CX CRM Integration
 0x00phantom-hat/cve-2026-12400-exploit
Authenticated WordPress IDOR exploit for CVE-2026-12400; enumerates FlowForms REST form IDs and modifies form content or hijacks email notifications.
 qianlijaingshan/ragflow-audit
RAGFlow 三洞审计工具 (CVE-2026-28797 / CVE-2026-24770 / CVE-2025-69286)
 aquibpro/reconix
Advanced recon engine that finds real secrets, validates them live, and builds exploit paths from client-side intelligence.