
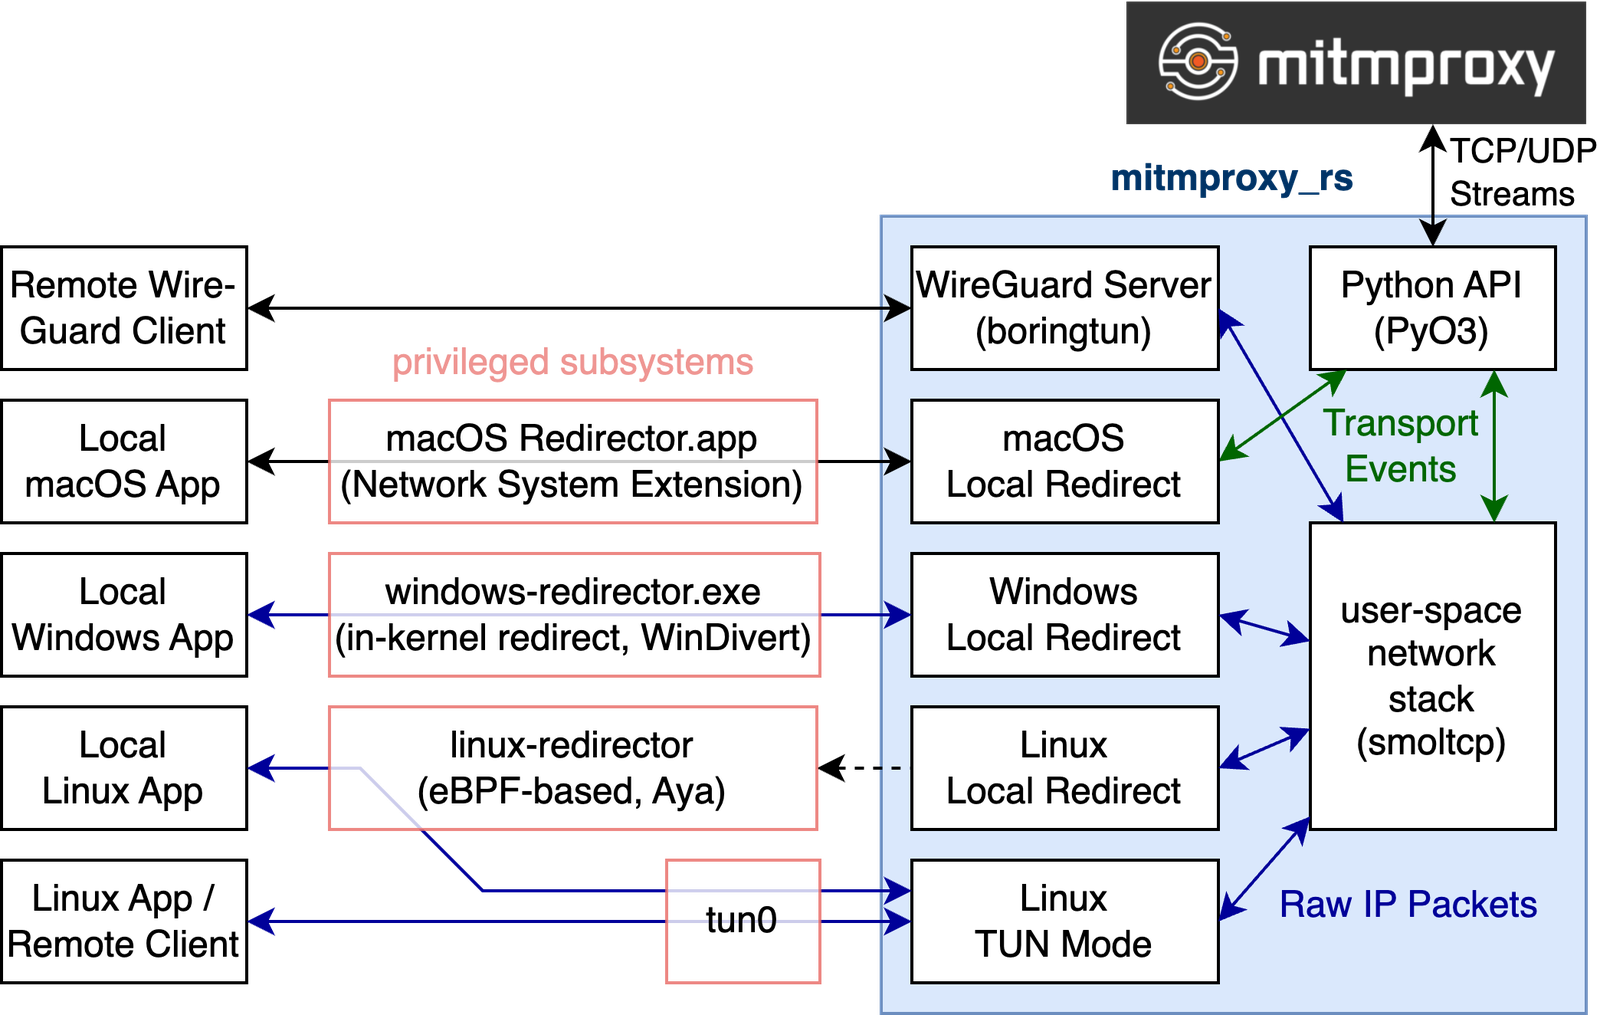
mitmproxy_rs
 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
api-security-testingmobile-app-pentestingnetwork-security+2
452
mitmproxy/mitmproxy_rsRust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 keygraphhq/shannon
Shannon is an autonomous, white-box AI pentester for web applications and APIs. It analyzes your source code, identifies attack vectors, and executes…

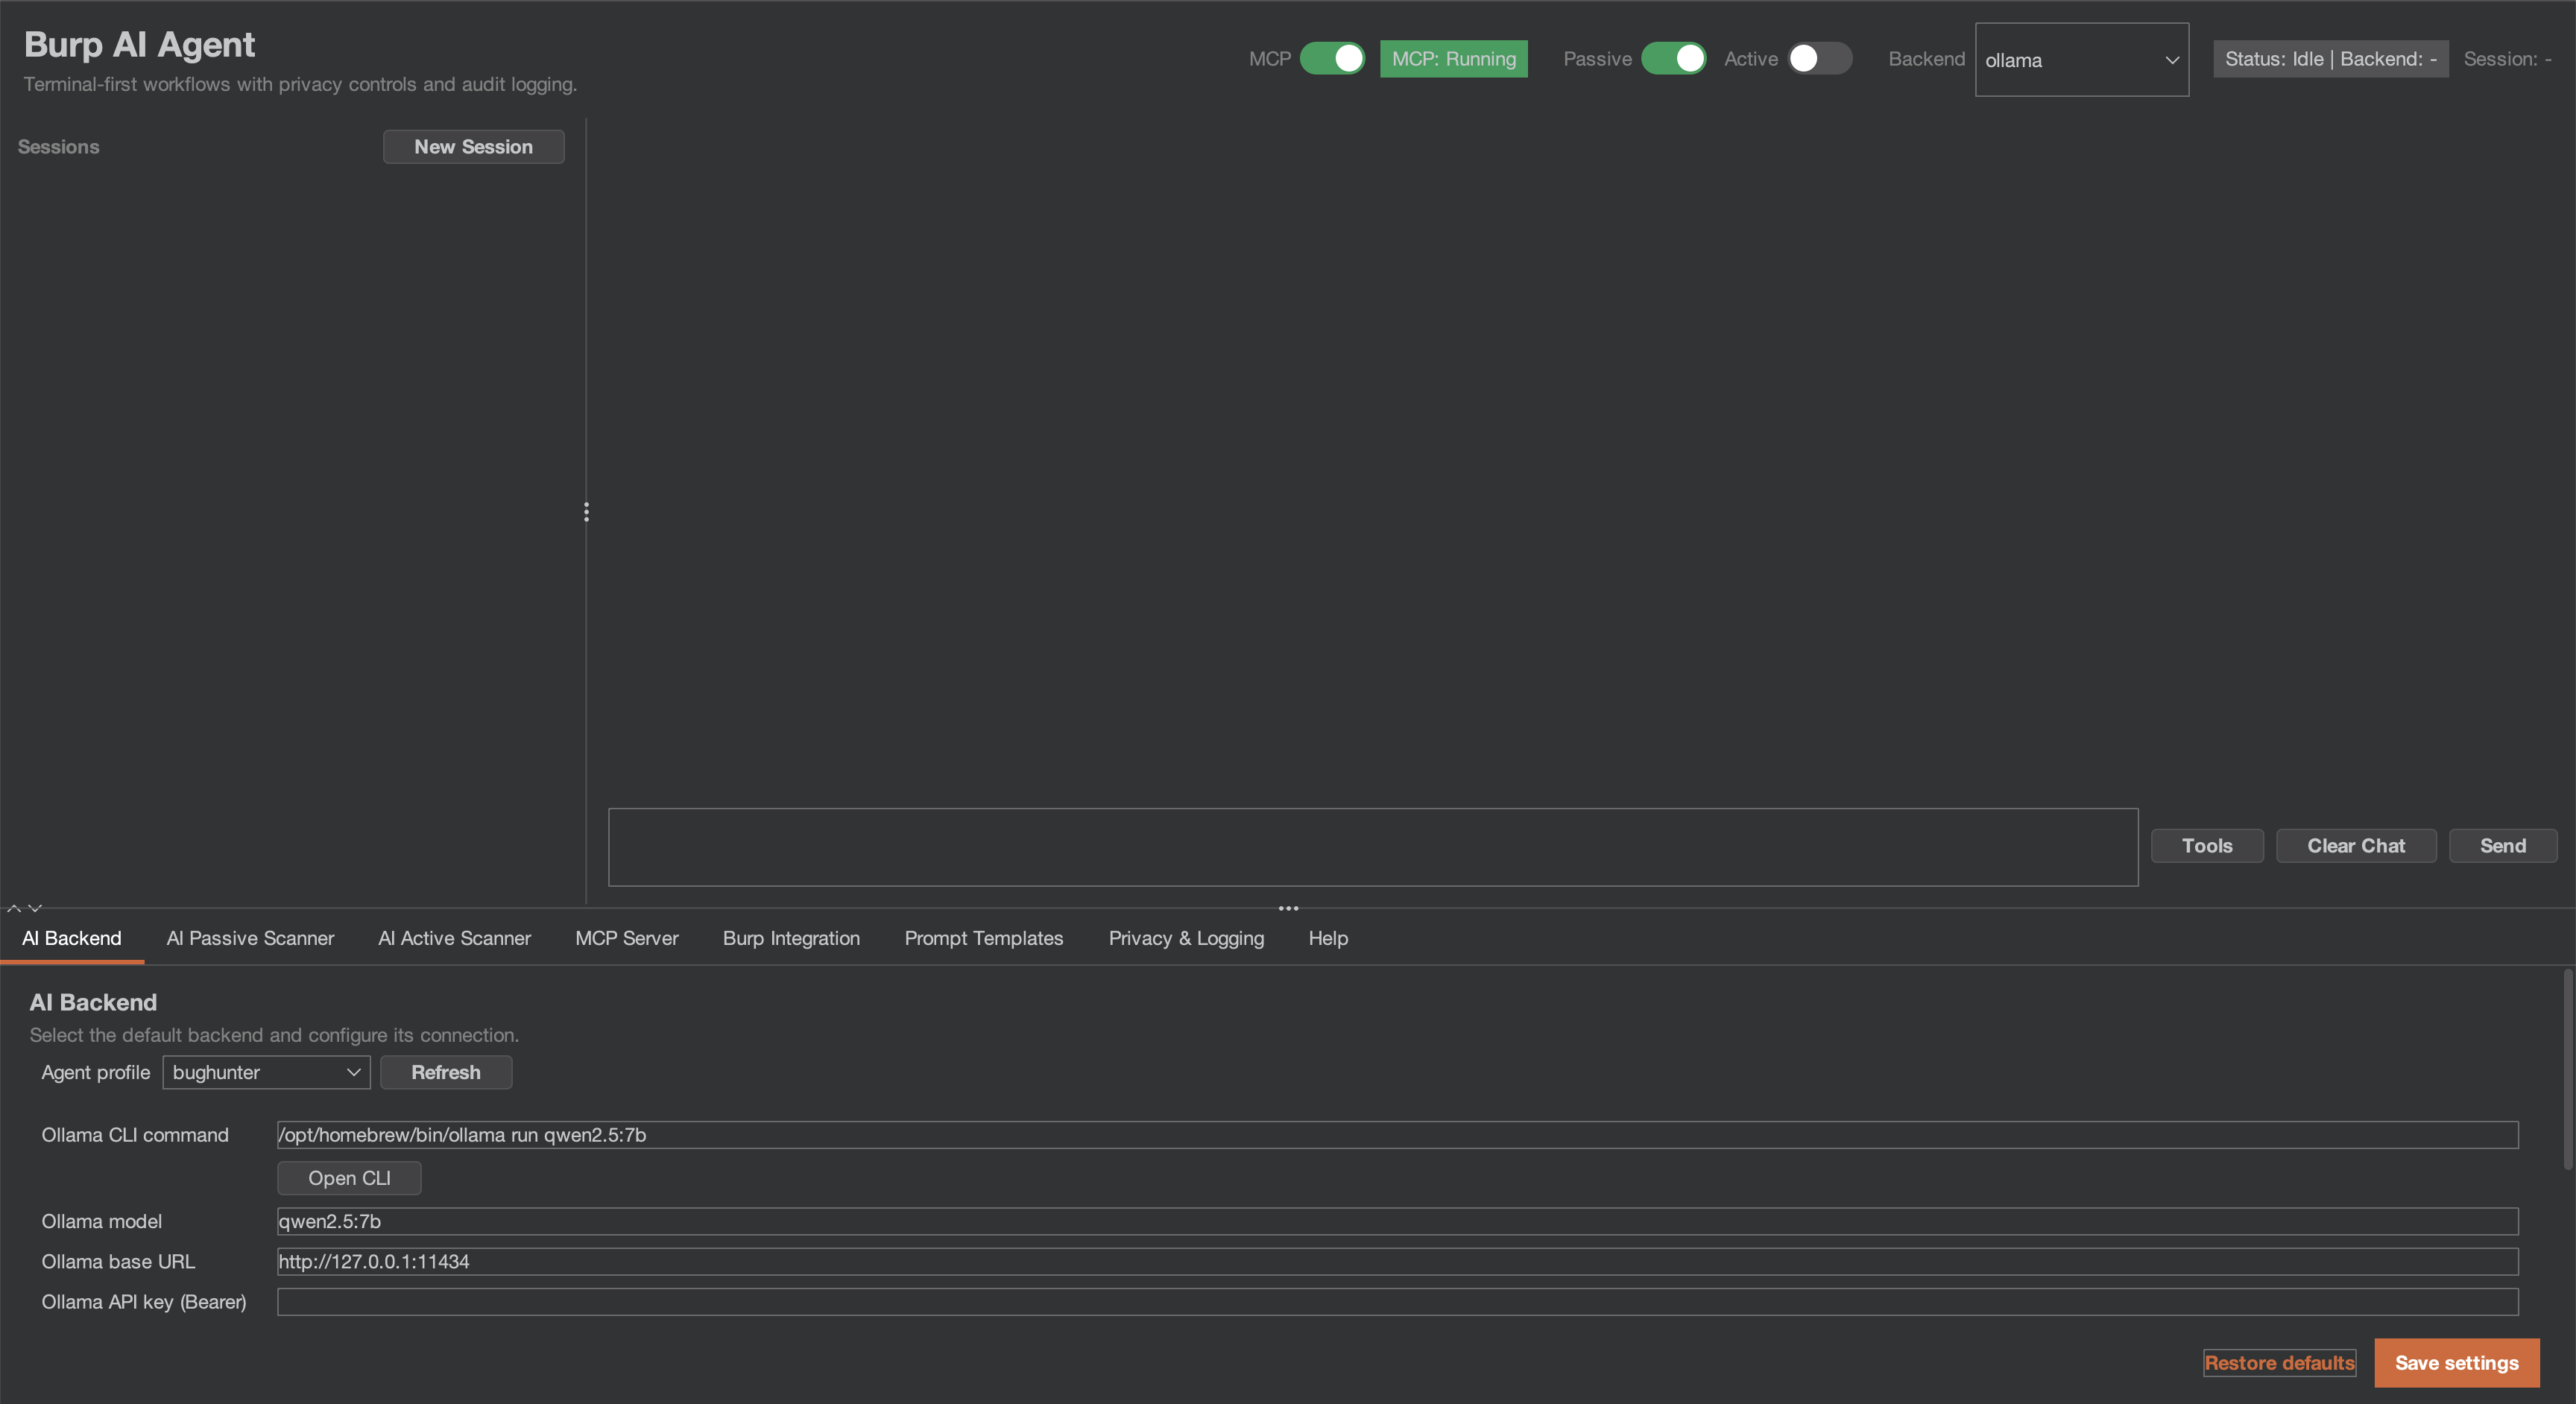 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 kovachvl/cve-2026-54356
Proof-of-concept exploit and advisory for CVE-2026-54356, a Budibase missing-authorization flaw that lets low-privilege users mint S3 pre-signed…
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.
 weirdmachine64/redom
A Burp Suite extension that brings full DOM rendering capabilities directly into Burp, enabling effective security testing of modern JavaScript-heavy…
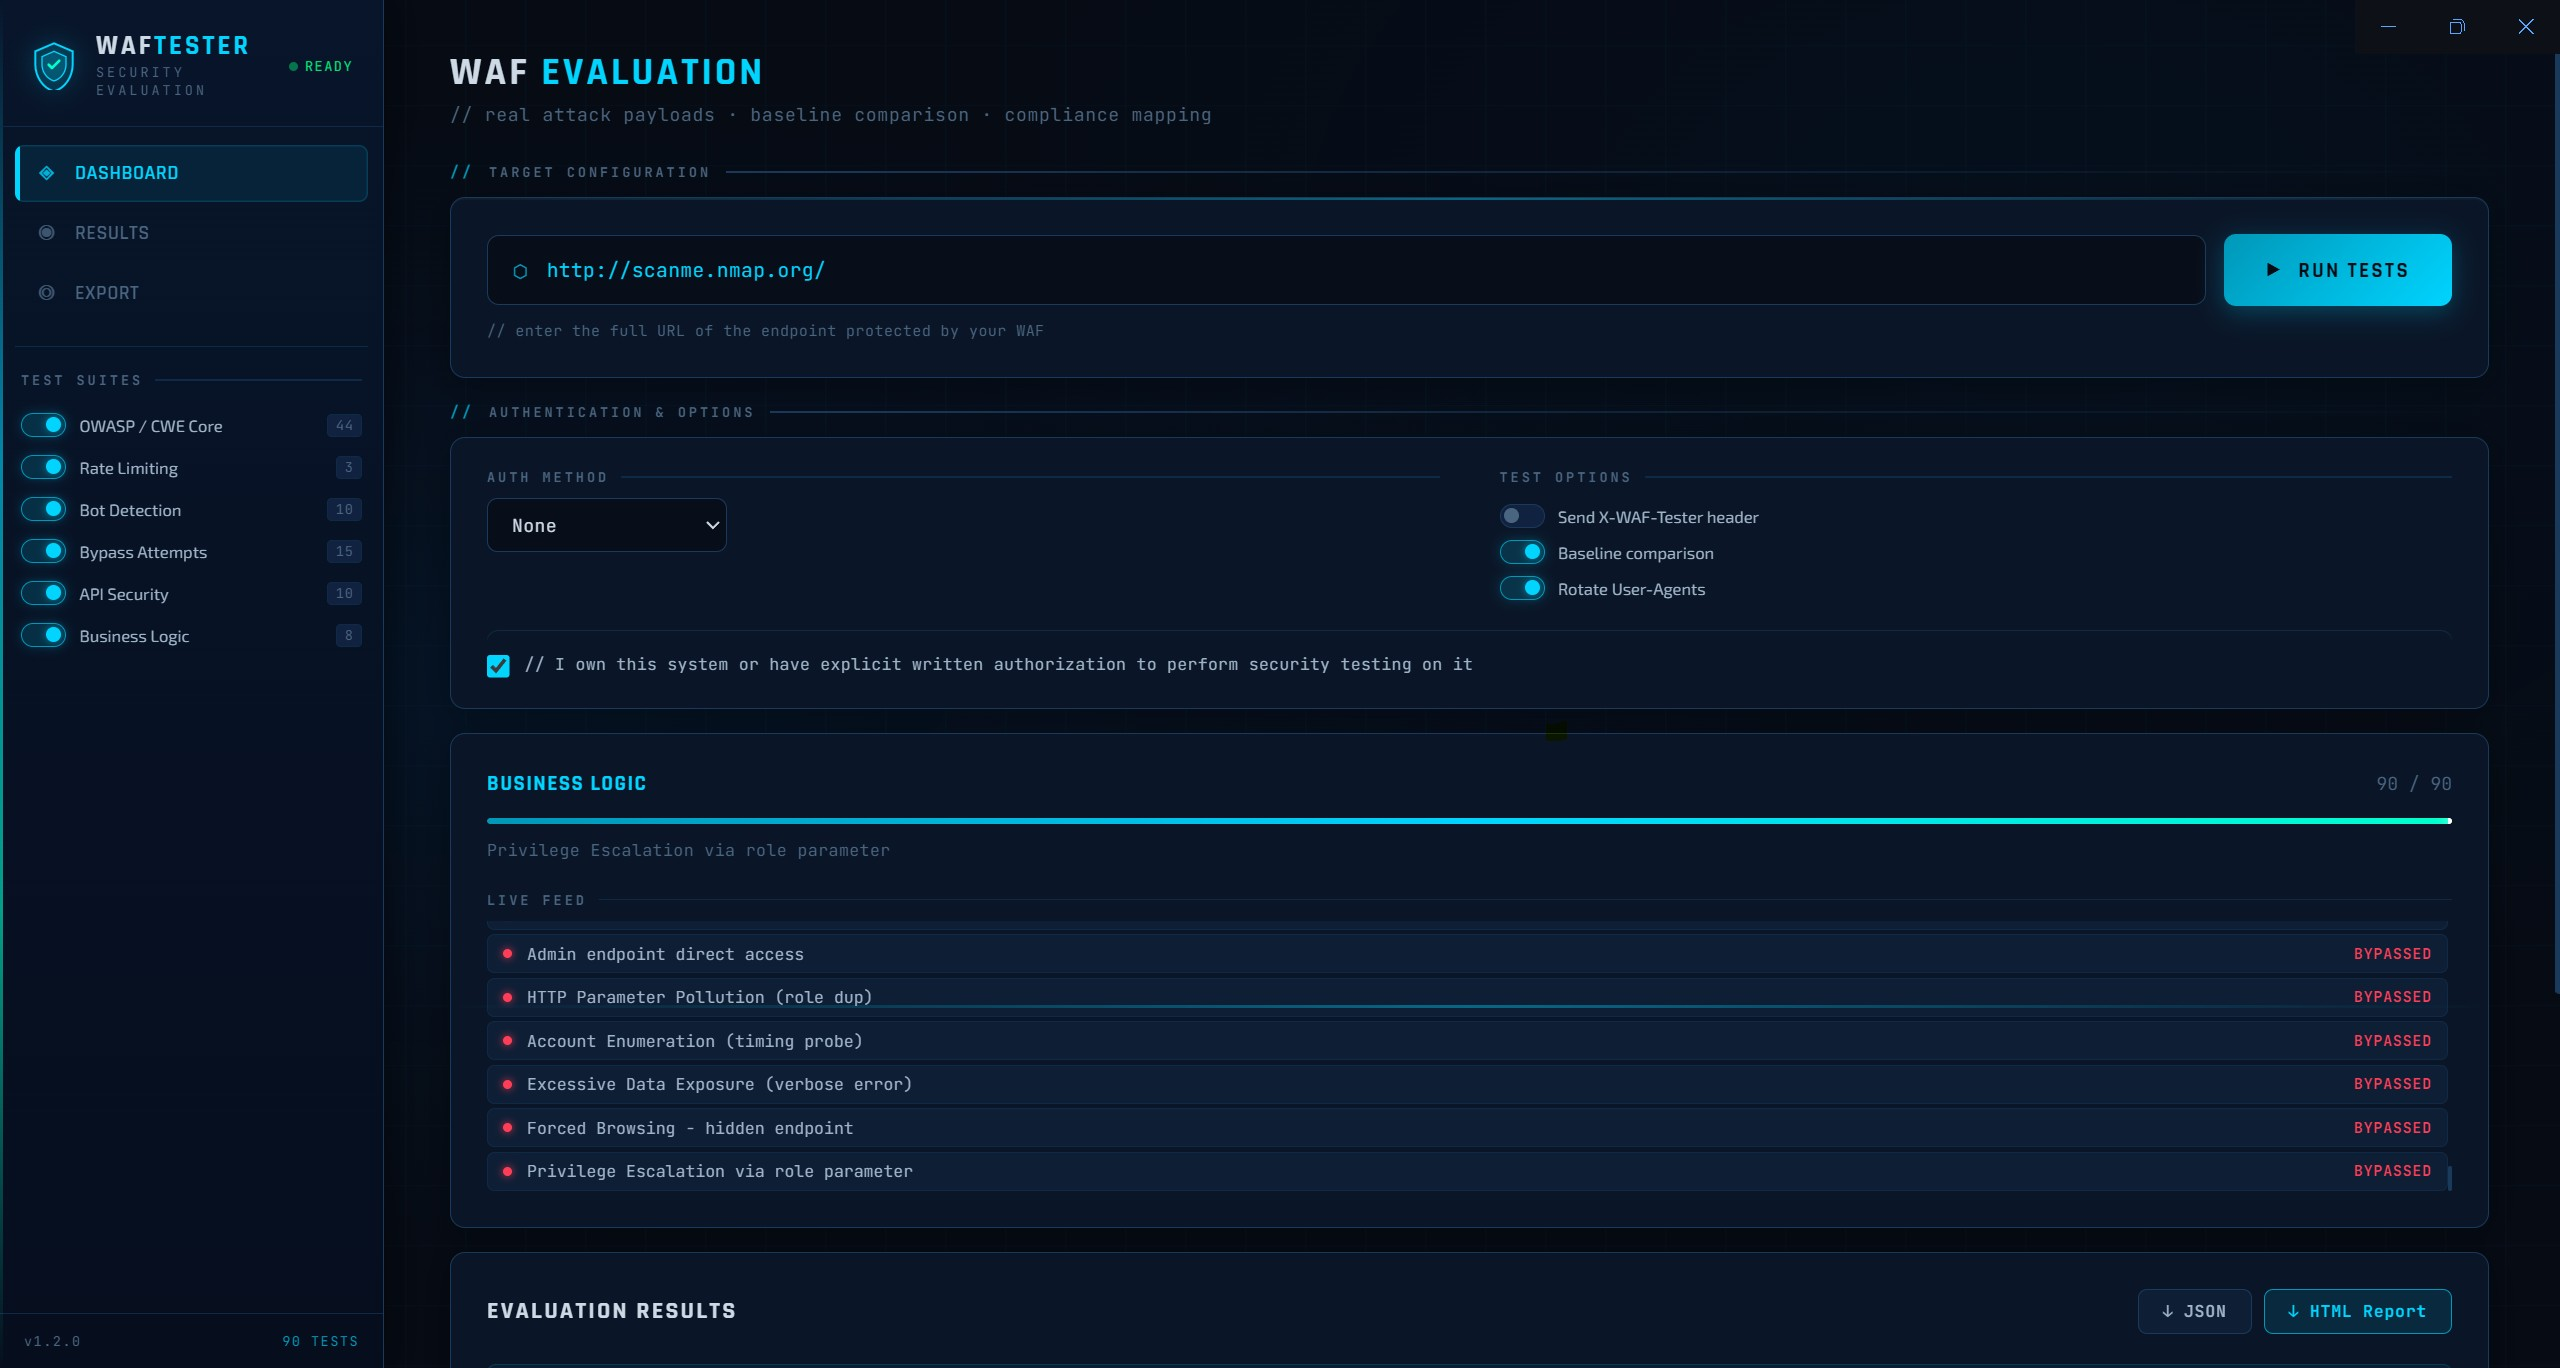 kpomin57/waf-tester
A program for testing WAF functionality
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 secsys-fdu/cve-2025-51867
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…
 httpie/cli
🥧 HTTPie CLI — modern, user-friendly command-line HTTP client for the API era. JSON support, colors, sessions, downloads, plugins & more.
 k3ystr0k3r/cve-2021-4191-exploit
A PoC exploit for CVE-2021-4191 - GitLab User Enumeration.
 digeex/raider
DEPRECATED, please use the new repository from OWASP: https://github.com/OWASP/raider
 ac-pm/inspeckage
Android Package Inspector - dynamic analysis with api hooks, start unexported activities and more. (Xposed Module)