zimaos-cve-2026-28286-arbitrary-file-write

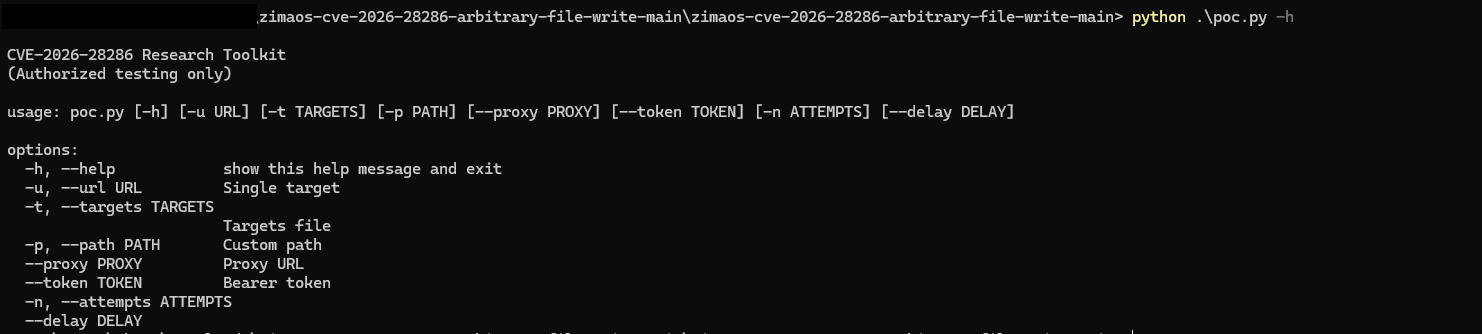
PoC and verification toolkit for CVE-2026-28286, an arbitrary file write vulnerability in ZimaOS, exploiting API misconfiguration to write files…

PoC and verification toolkit for CVE-2026-28286, an arbitrary file write vulnerability in ZimaOS, exploiting API misconfiguration to write files…

Exploit for CVE-2018-12542 in Vert.x-Web, a Java web framework. Demonstrates a path traversal vulnerability allowing unauthorized access to static…

Time-based blind SQL injection proof-of-concept for LiteLLM v1.65.4. Exploits the `/key/block` endpoint to extract database contents and read server…

Reproducer for CVE-2026-48204: Apache Camel camel-mongodb-gridfs gridfs.* header injection overriding the GridFS operation (enumerate/read/delete…

Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…

Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …

An strace-like program for the Windows 'native' API

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…


WEB SERVICE SECURITY ASSESSMENT TOOL

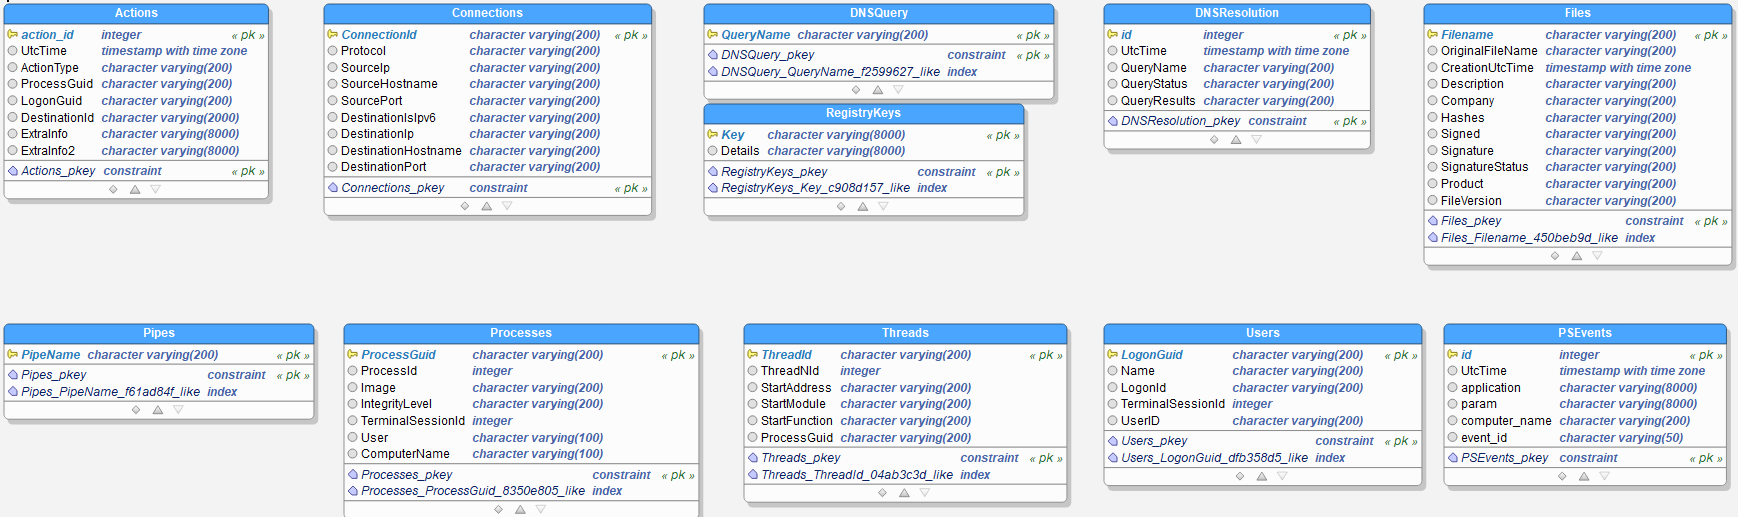
Threat Hunting tool about Sysmon and graphs

A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.