

-LogicSentry-AI
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
ai-securityapi-security-testingcode-analysis+9
1
vighnesh91/-logicsentry-aiOffline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
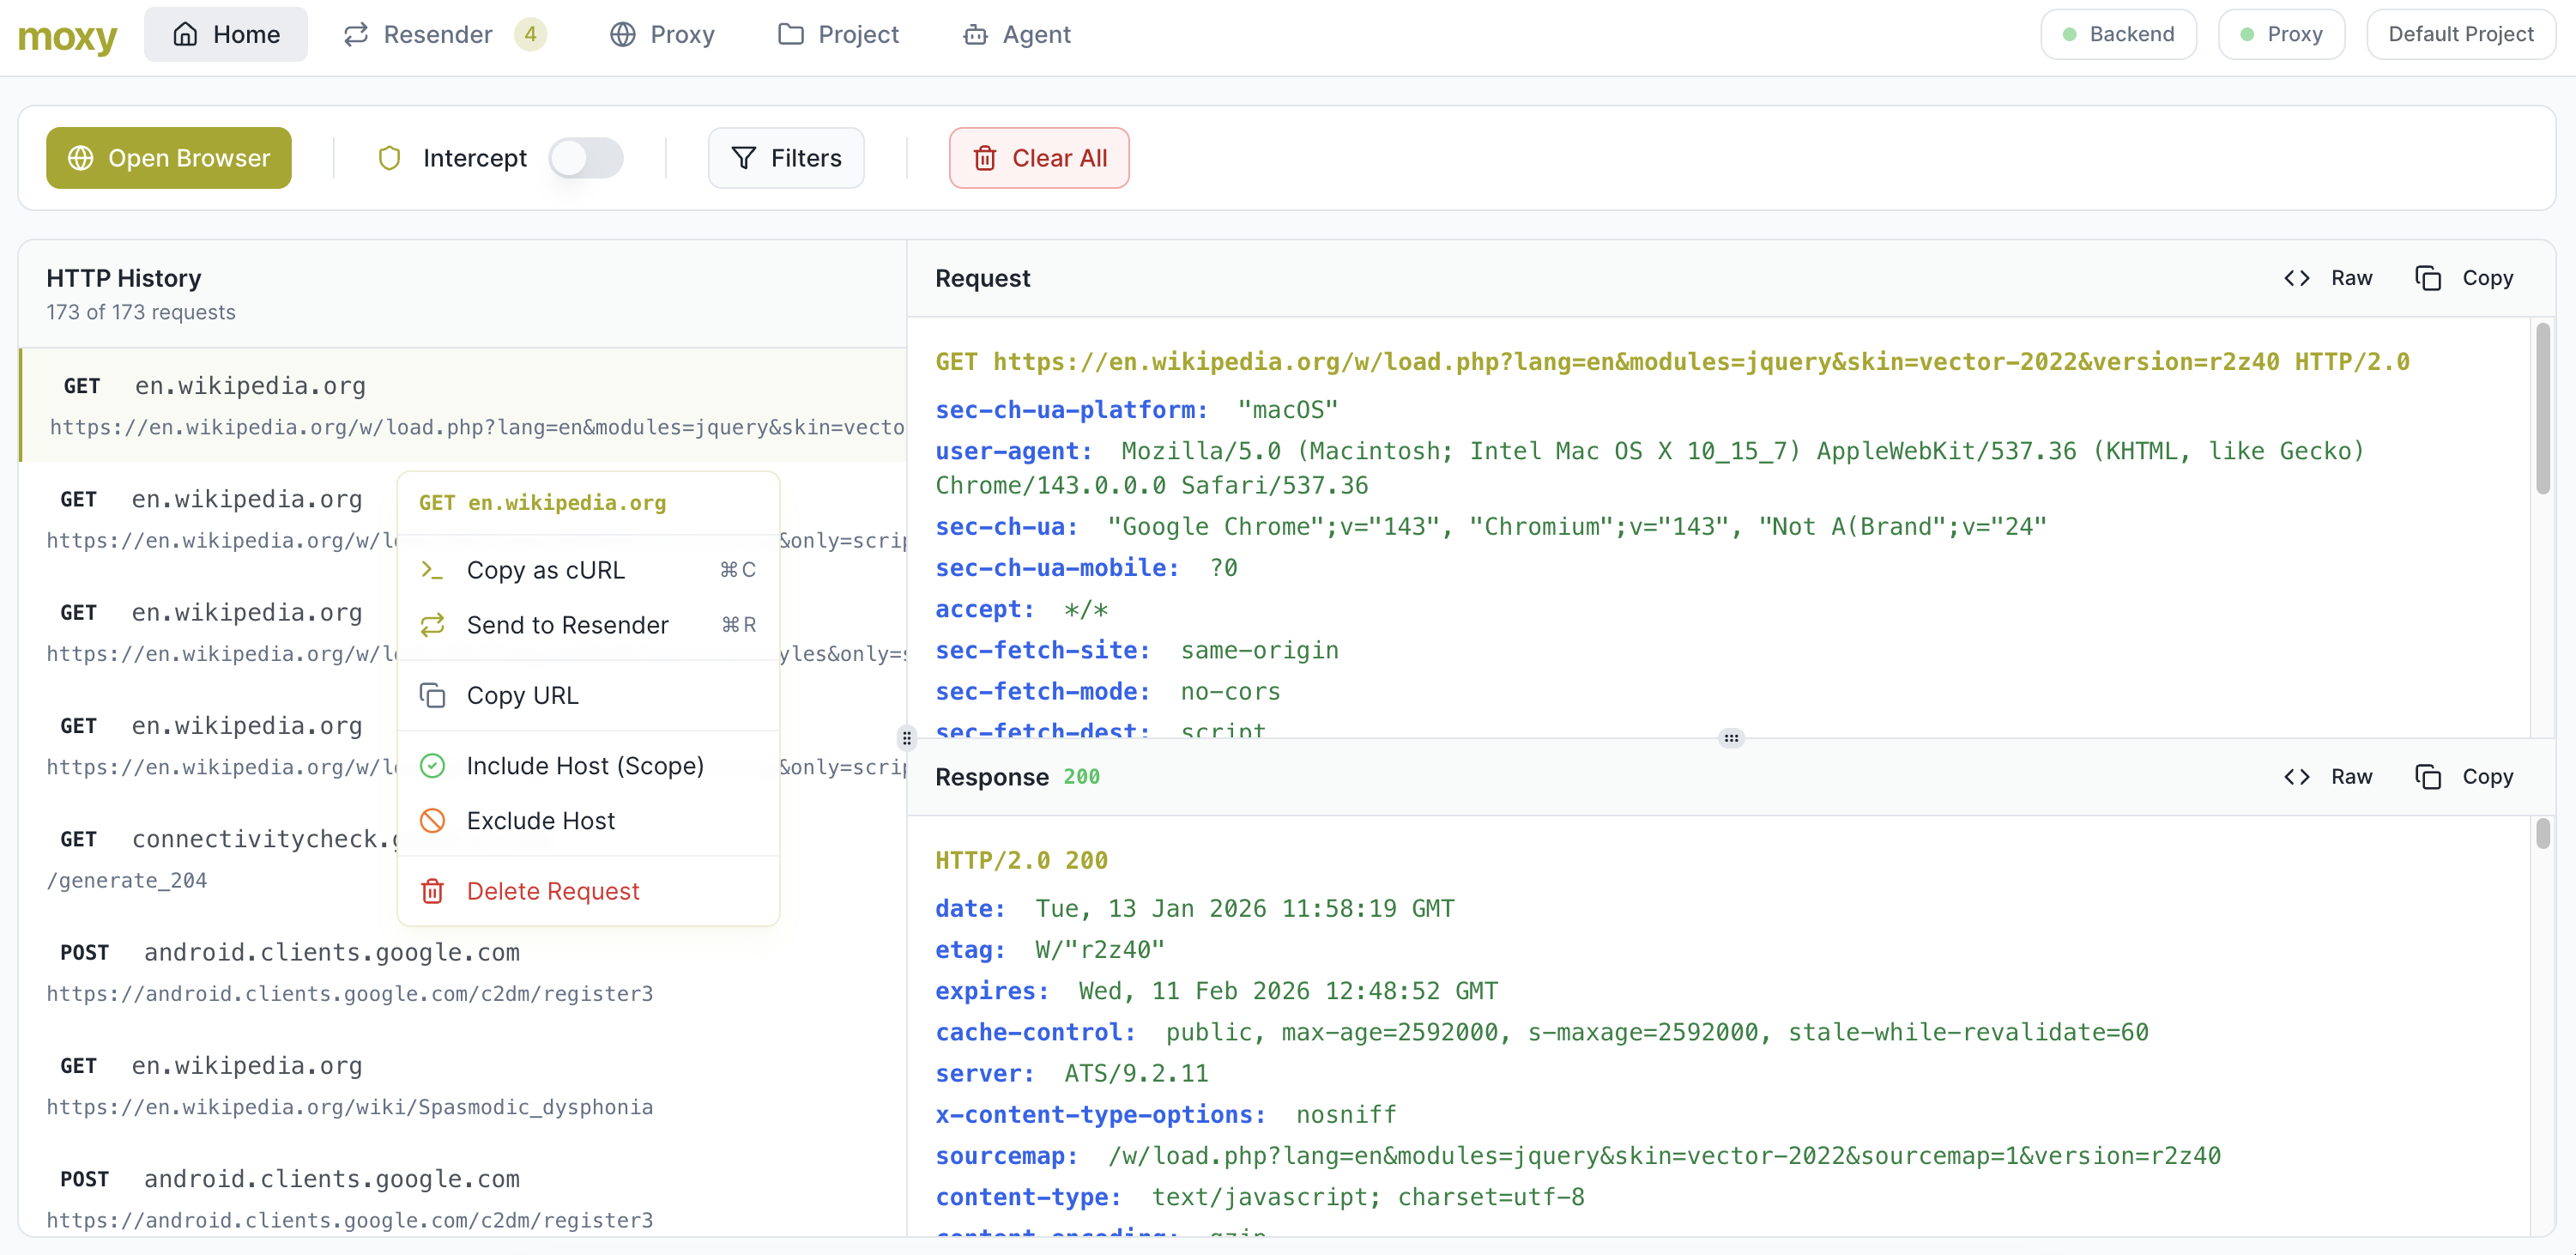 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 wi3memake/react2shell-scanner
Command-line security assessment framework for React and Next.js applications, analyzing React Server Components for misconfigurations, with…
 theronielanddaronpodcastshow/svja
The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
 sn1r/mass-assigner
Automated tool to probe for mass assignment vulnerabilities by extracting parameters from one HTTP request and applying them to another, with support…
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…