

archerysec
 archerysec/archerysec
ASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
api-securitycode-analysisconfiguration-auditing+5
2.5k1 year ago
archerysec/archerysecASOC, ASPM, DevSecOps, Vulnerability Management Using ArcherySec.
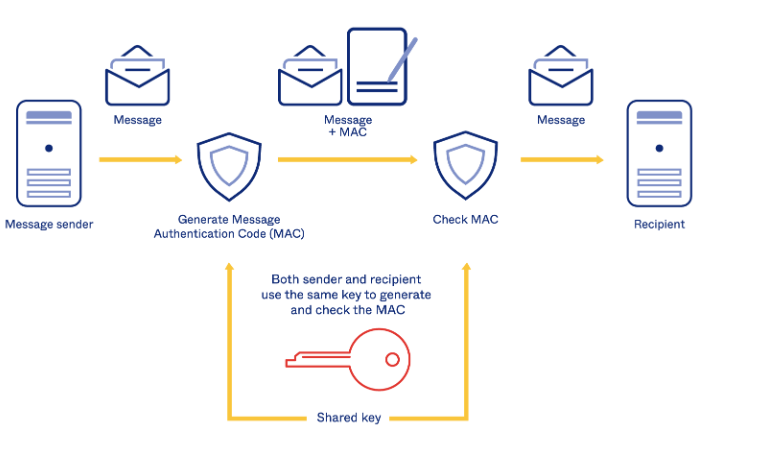 password123456/about-hmac
HMAC Implementation Example and Explanation
 cph/rabl-old
Ruby templating system for generating JSON and XML APIs, with a fix for CVE-2014-4671. Supports partials, inheritance, and custom nodes for flexible…
 shoucheng3/apache__dubbo_cve-2021-30180_2-7-9
Exploit for CVE-2021-30180 targeting Apache Dubbo RPC framework, enabling remote code execution via crafted RPC requests in vulnerable versions.
 jassics/security-study-plan
Complete Practical Study Plan to become a successful cybersecurity engineer based on roles like Pentest, AppSec, Cloud Security, DevSecOps and so…
 imperva/automatic-api-attack-tool
Imperva's customizable API attack tool takes an API specification as an input, generates and runs attacks that are based on it as an output.
 fariszr/knocker
Knocker, a knock based access control service for your homelab
 ch4n3-yoon/cve-2025-62727-demo
Proof of concept of CVE-2025-62727 that can cause denial-of-service in FastAPI (based Starlette <= 0.48.0)
 cilium/cilium
eBPF-based Networking, Security, and Observability
 siriusscan/sirius
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…
 0xdad0/papimonitor
Frida-based runtime API monitor for Android apps that logs invoked APIs, parameters, return values, and call origins across predefined or custom…
 qarait/gate0
A small, auditable, terminating, deterministic micro-policy engine
 wadesweaponshed/checkpoint-cve-webscanner
A web version of the bash scripts wrote for Check Point CVE-2026-50751 and CVE-2026-50752. This uses a local server to scan and make changes using…
 george0papasotiriou/cve-2026-11103-graphql-batching-alias-rate-limit-bypass
Proof-of-concept exploit for CVE-2026-11103 demonstrating GraphQL rate-limit bypass through batching and field aliases; includes vulnerable Node.js…
 remenis/cve-2025-63667
Vatilon-based IP camera firmwares issue Session-Id tokens without verifying credentials, allowing attackers to obtain sessions and retrieve plaintext…
 shanika04/apache_skywalking
CVE-2020-9483 OR CVE-2020-13921
 osirium/suds
Clone of suds 0.4 + suds-0.4-CVE-2013-2217.patch