

Nest
 owasp/nest
Your gateway to OWASP. Discover, engage, and help shape the future!
api-securitycurated-resourceseducation+2
owasp/nestYour gateway to OWASP. Discover, engage, and help shape the future!
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
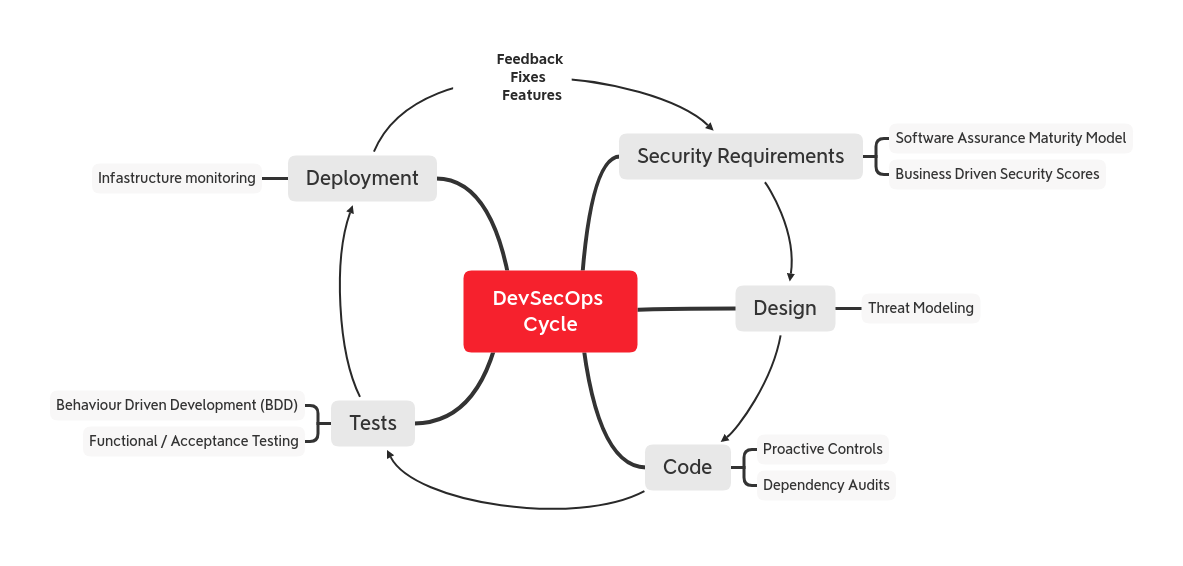 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 owasp/offat
Automated API security testing tool that generates tests from OpenAPI specs, fuzzes inputs, and checks for OWASP API Top 10 vulnerabilities including…
 spiderlabs/owasp-modsecurity-crs
OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 owasp/crapi
Deliberately vulnerable microservices API designed for hands-on training in the OWASP API Security Top 10 risks, with built-in challenges and a…
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-23457_2-2-3-1
Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input validation,…
 hakaioffsec/cve-2026-16764
Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 owasp/apicheck
Modular DevSecOps toolset for REST API security testing, designed for developers, sysadmins, and penetration testers to automate security checks…
 owasp/agent-skills-security-standard
Security standard for agent skills, providing guidelines and best practices to secure AI-driven autonomous agents in cloud and API environments.
 owasp/api-security
OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
 owasp/threat-dragon
An open source threat modeling tool from OWASP