
cloudflared
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
api-securitycloud-infrastructure-securitycloud-security+3
16.1k
cloudflare/cloudflaredClient for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
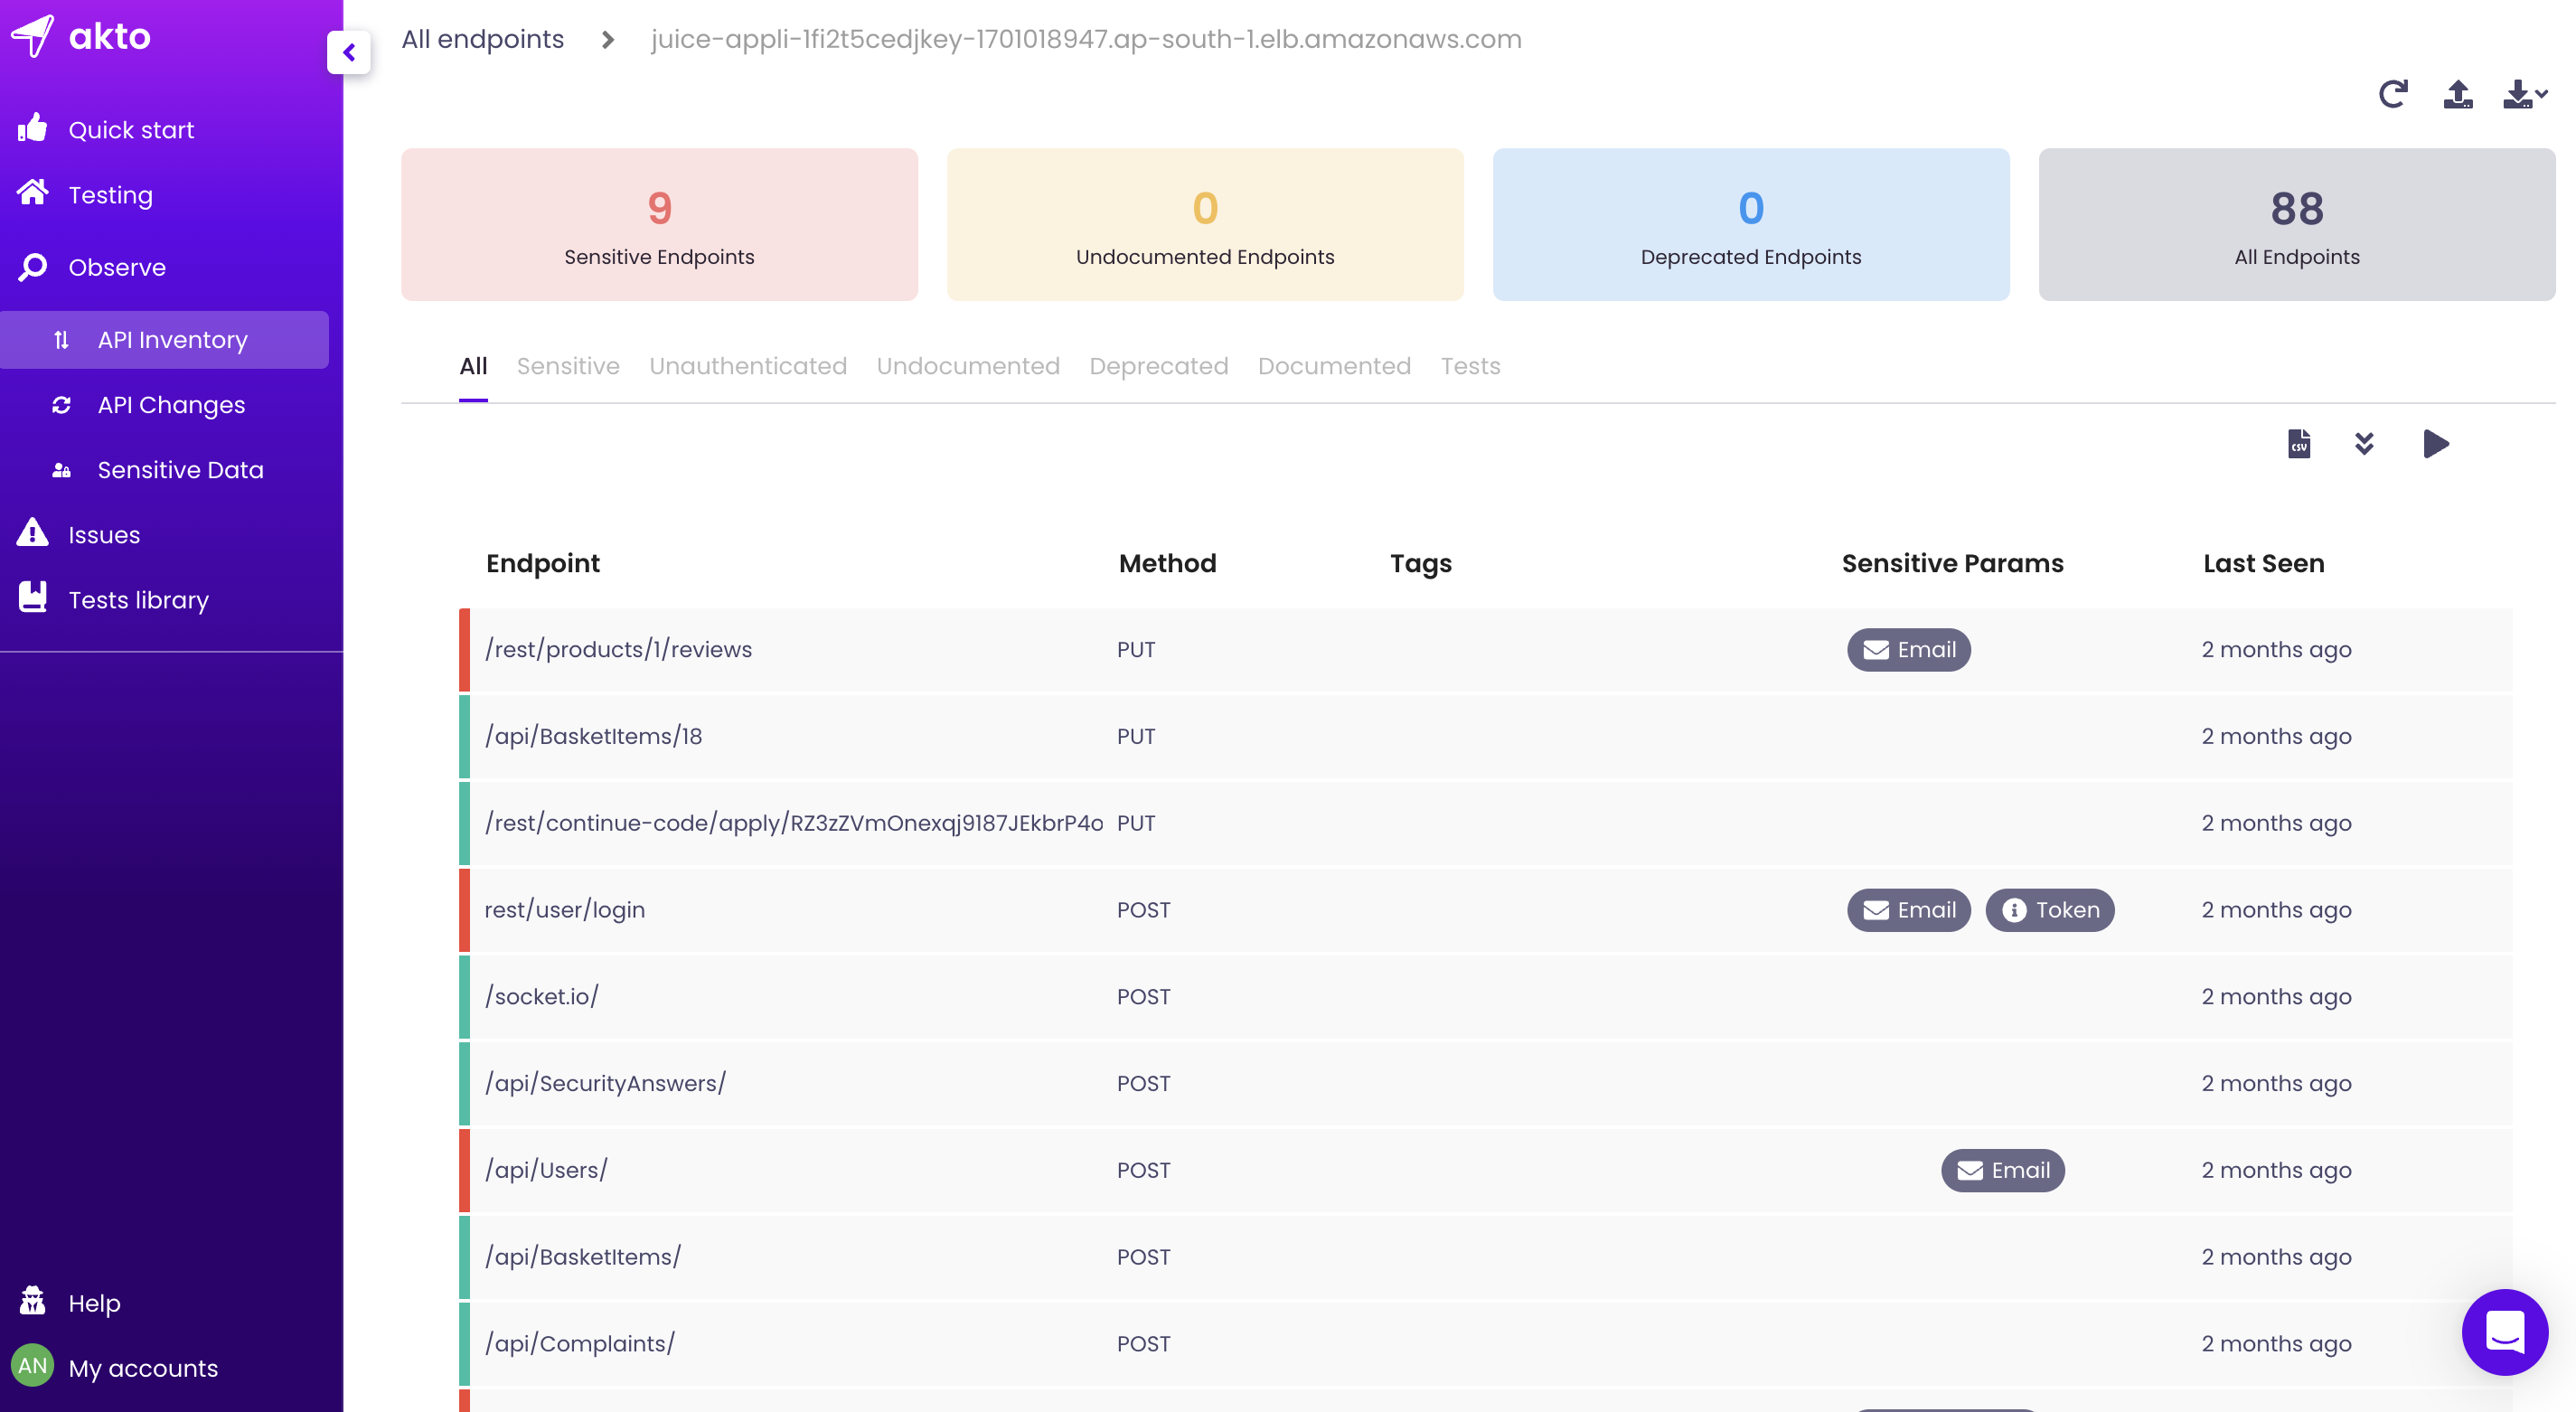 akto-api-security/akto
Open-source API security platform for continuous API discovery, vulnerability testing, and runtime threat detection. Integrates with CI/CD pipelines…
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 seqra/opentaint
Formal inter-procedural taint analysis engine for application security. Tracks untrusted data across function boundaries, persistence layers, and…
 aress31/openapi-parser
Parse OpenAPI documents into Burp Suite for automating OpenAPI-based APIs security assessments (approved by PortSwigger for inclusion in their…
 inflightsec/agent-vault-proxy
Just-in-time API keys for AI agents - and any other process you route through it: the caller only ever sees a placeholder.
 juanlunaia/aegis-latent-core
Self-hosted evidence gateway for AI systems: fail-closed policy, WAF, egress controls, signed durable MMR proofs, and offline verification across LLM…
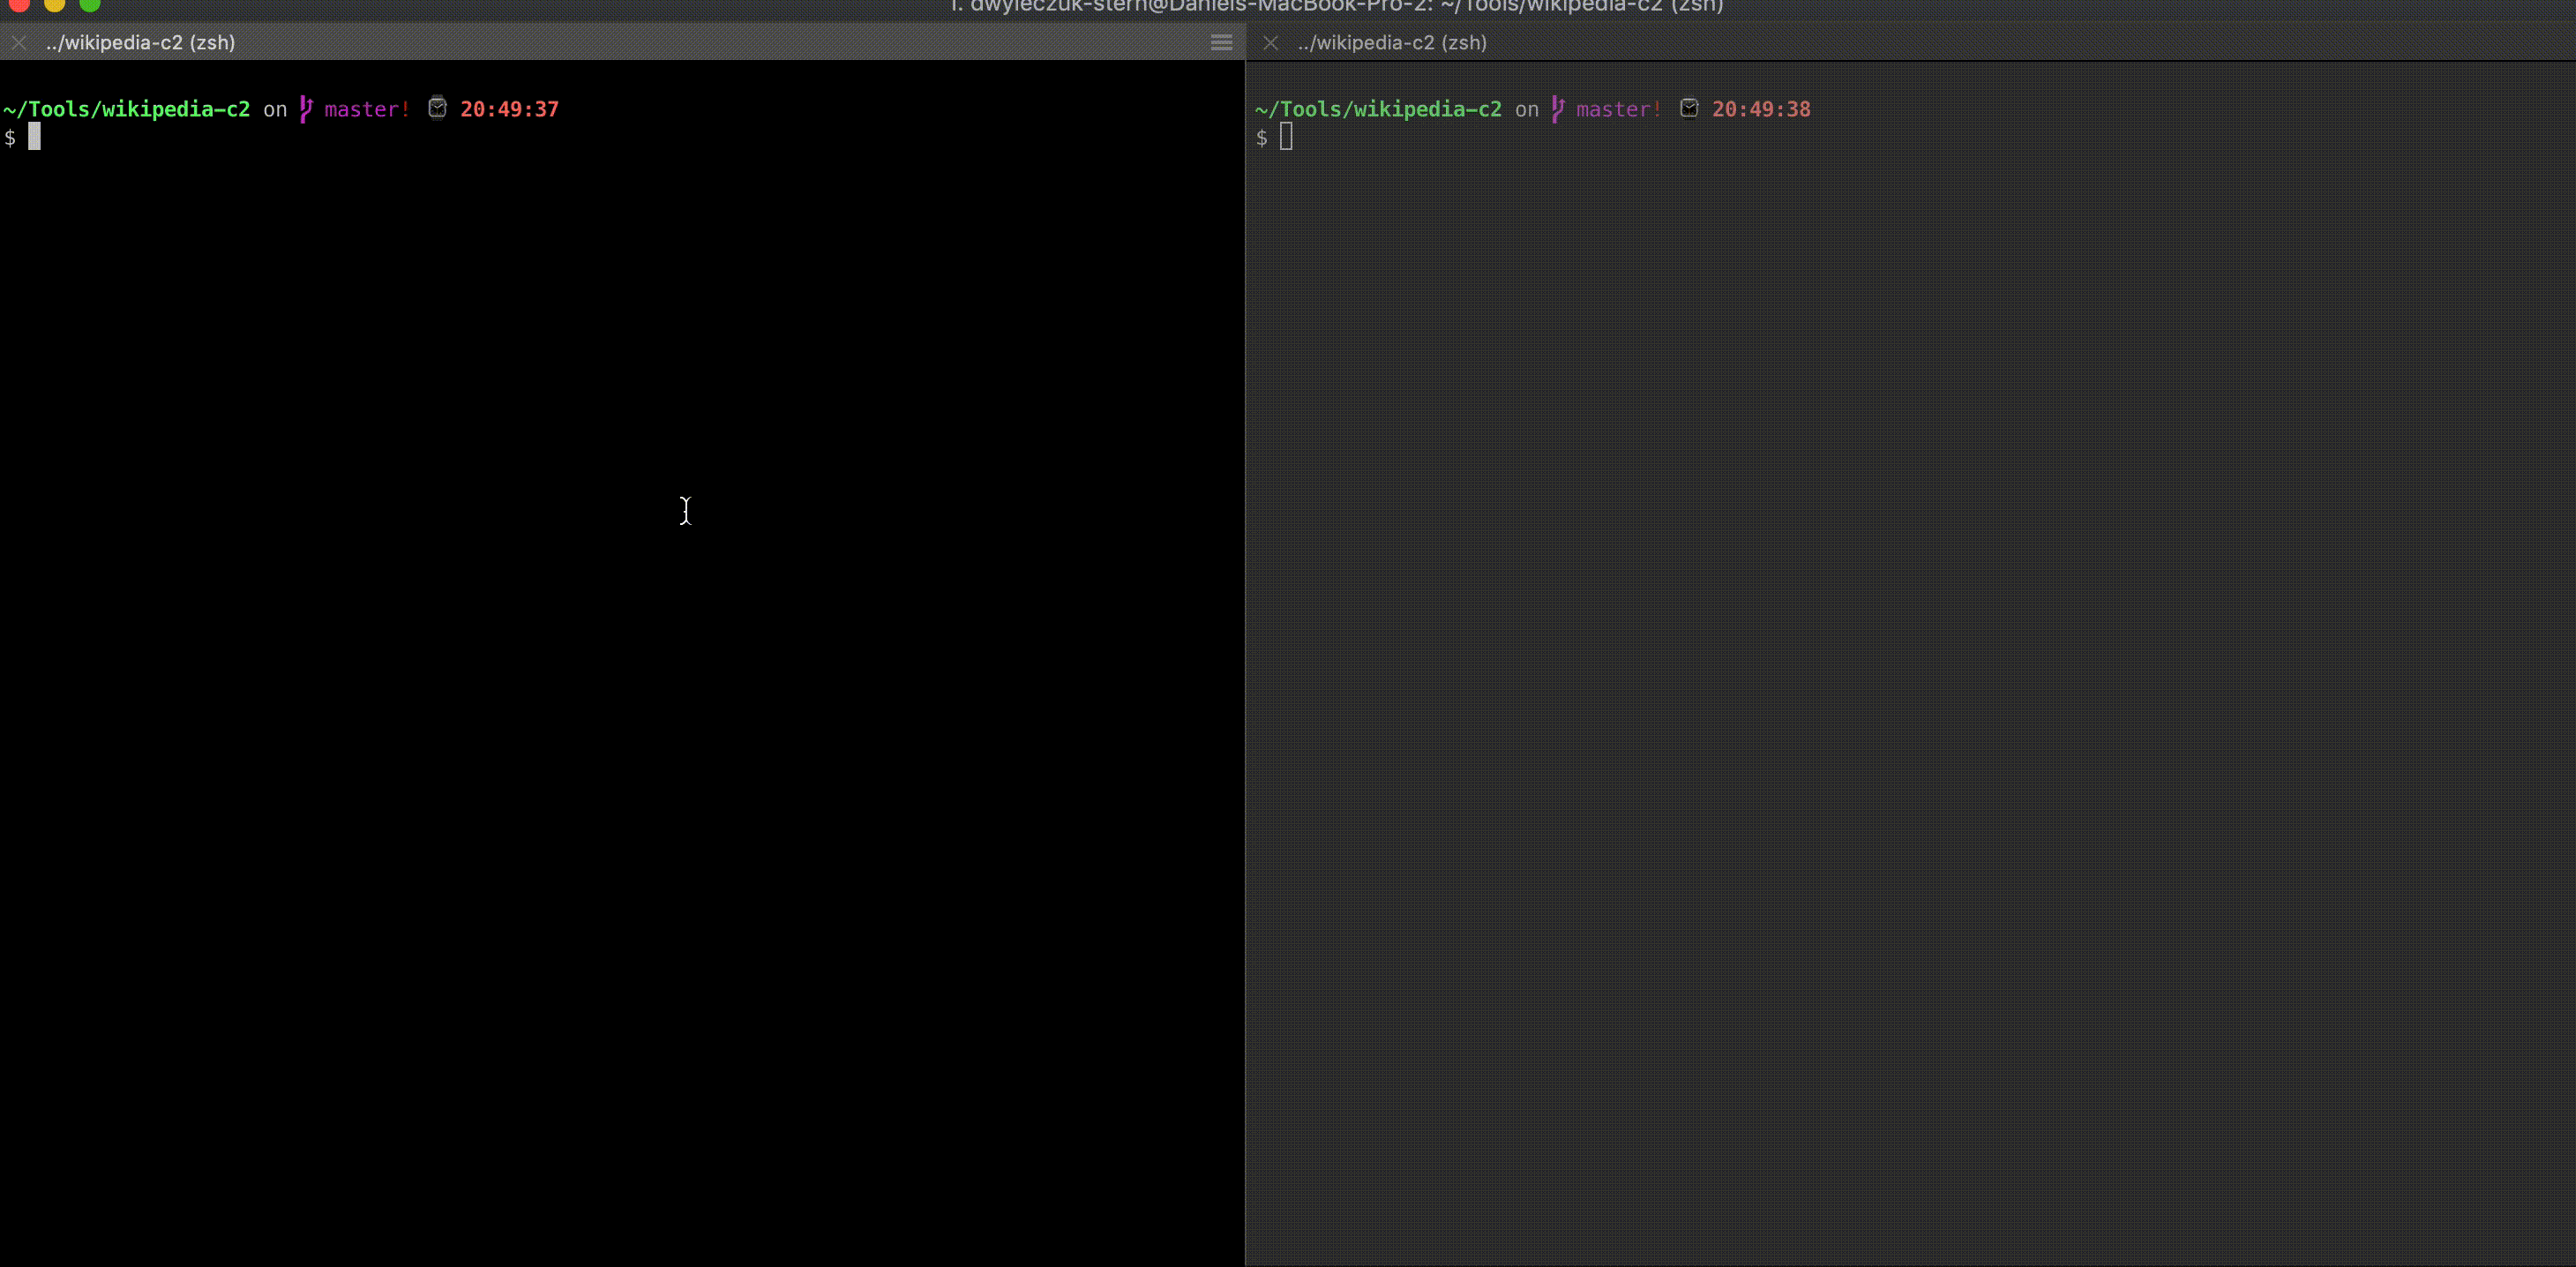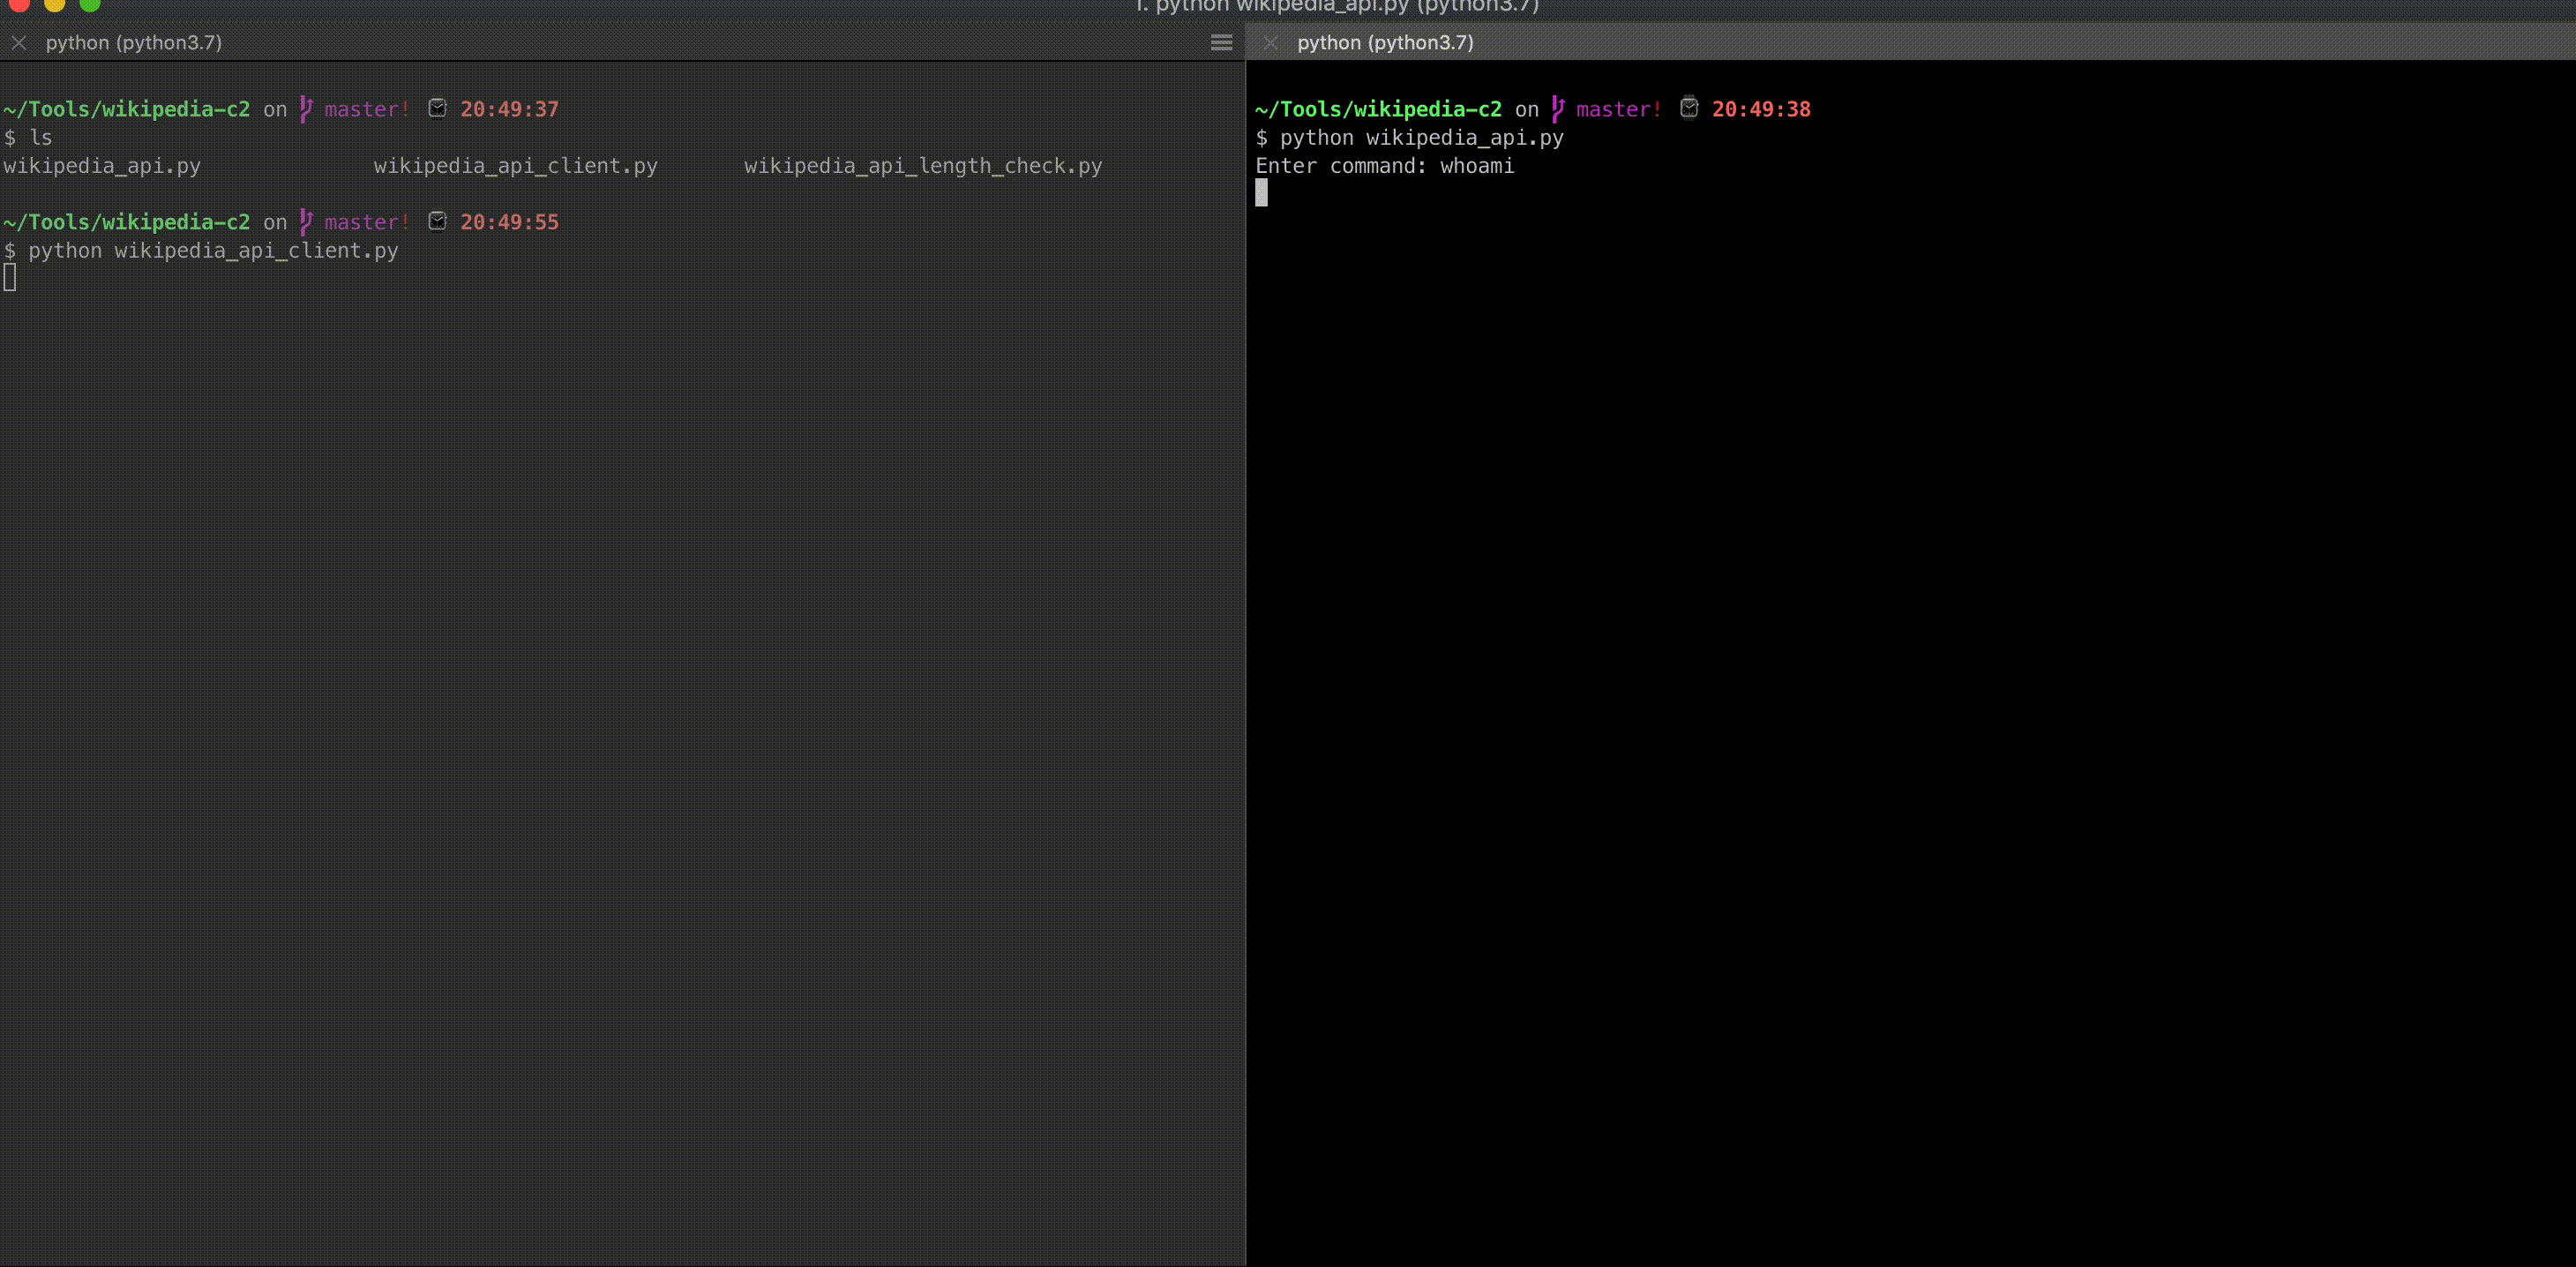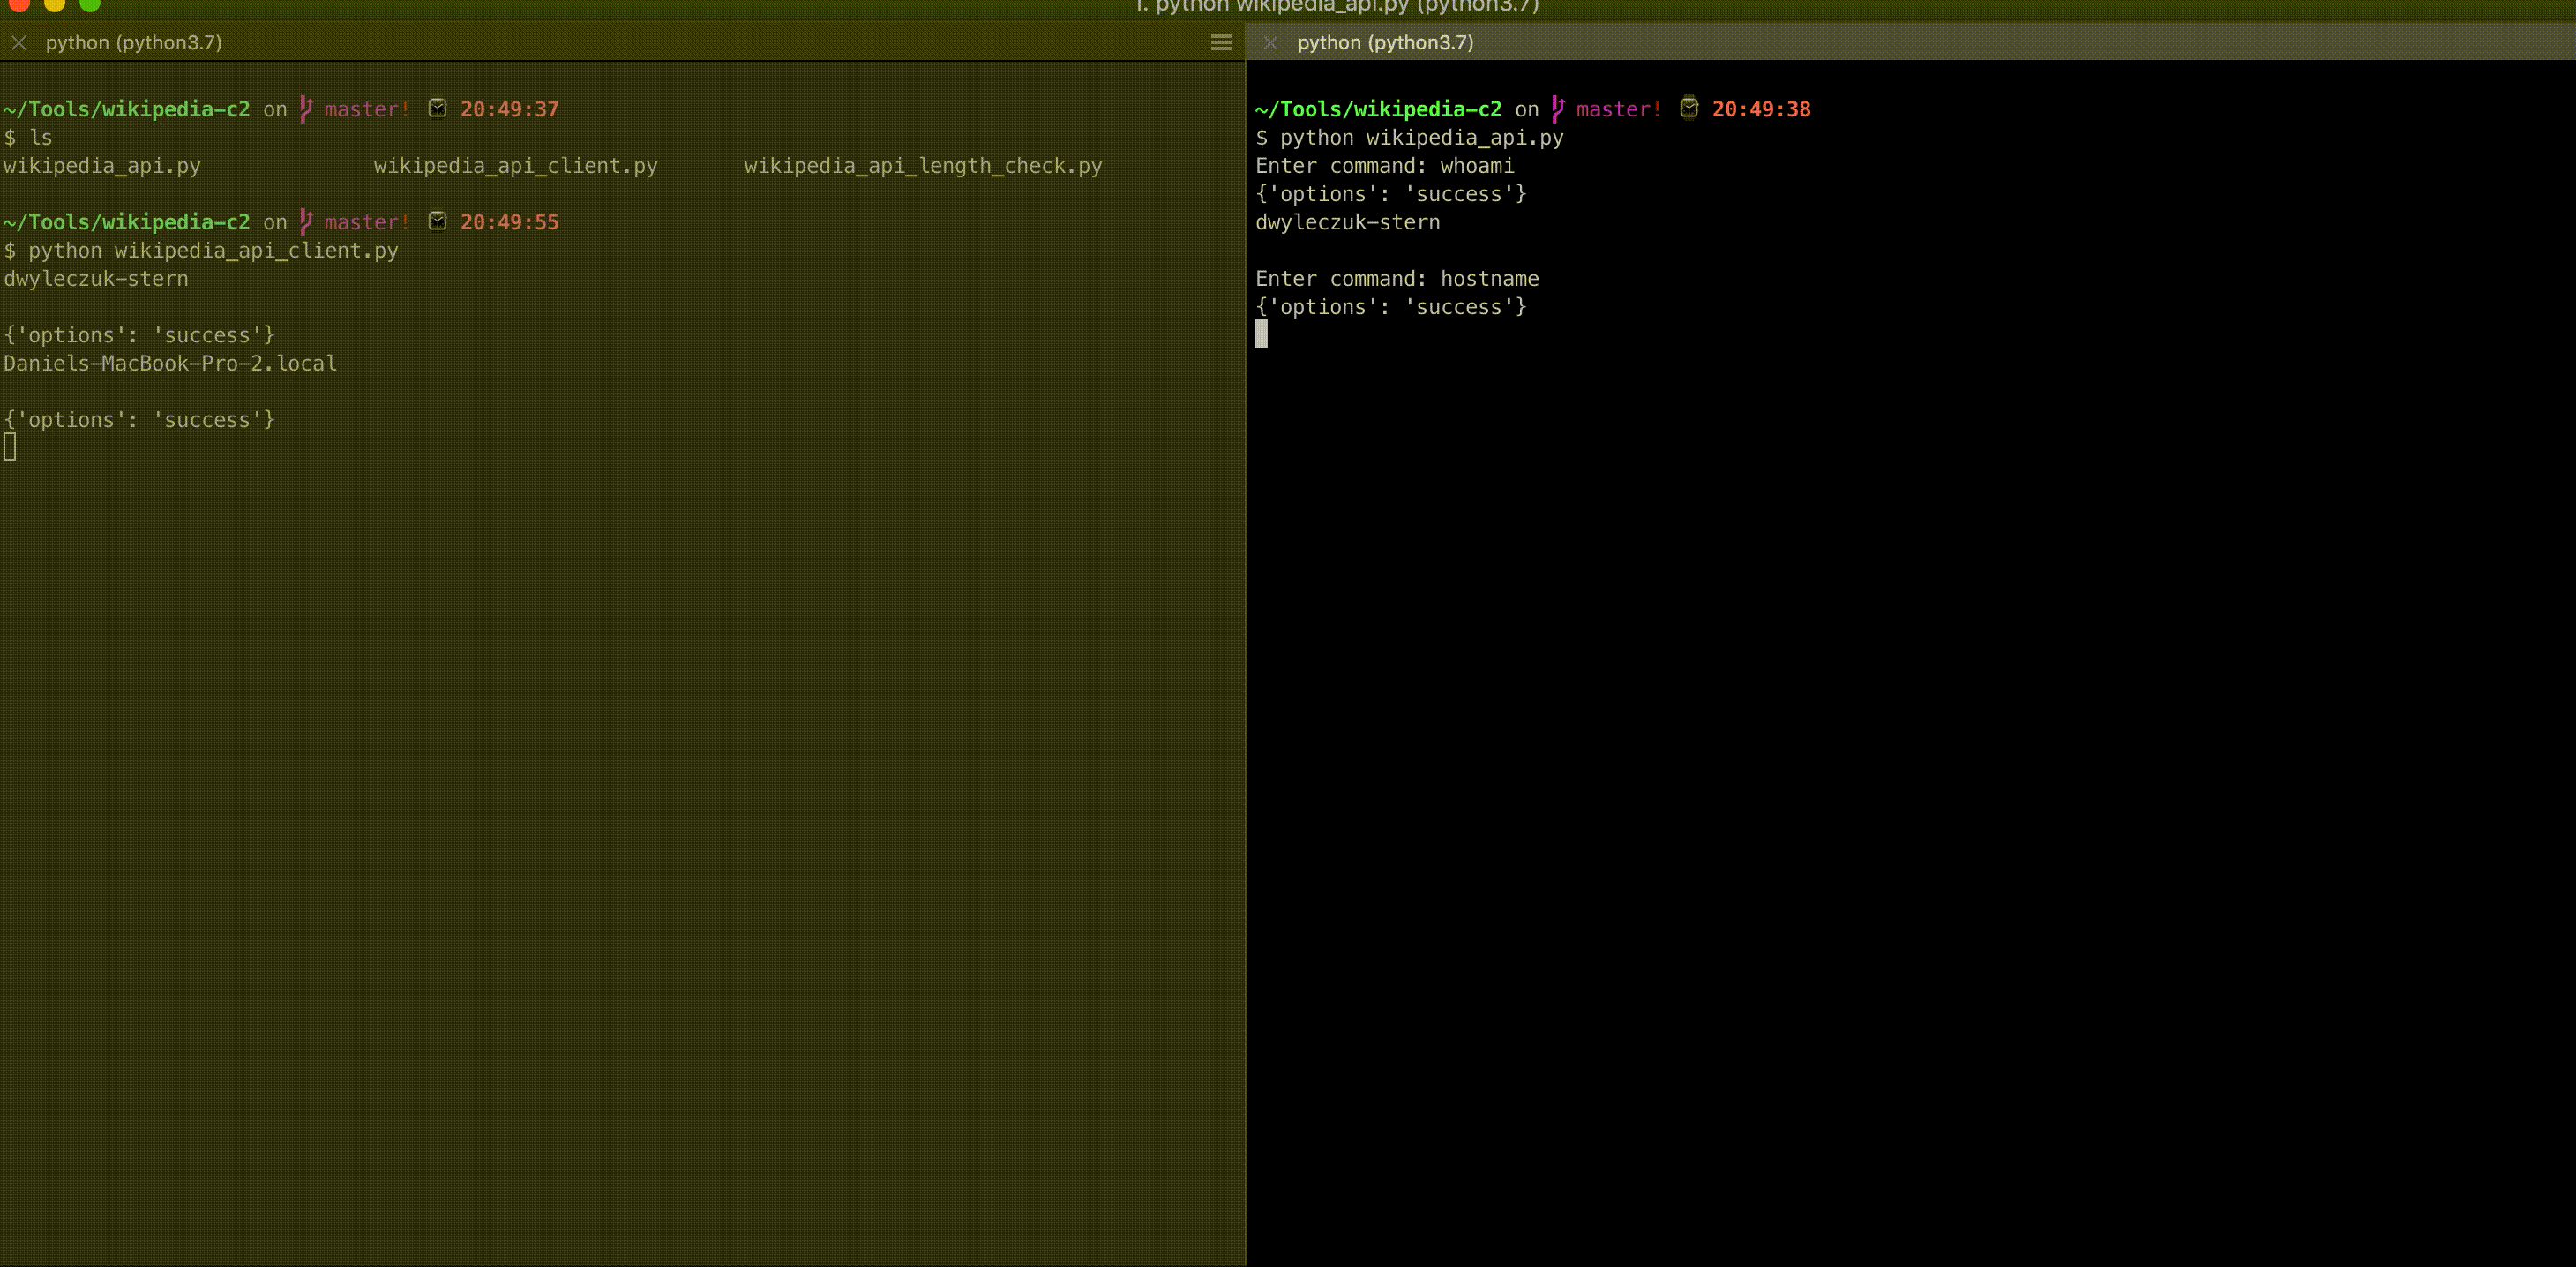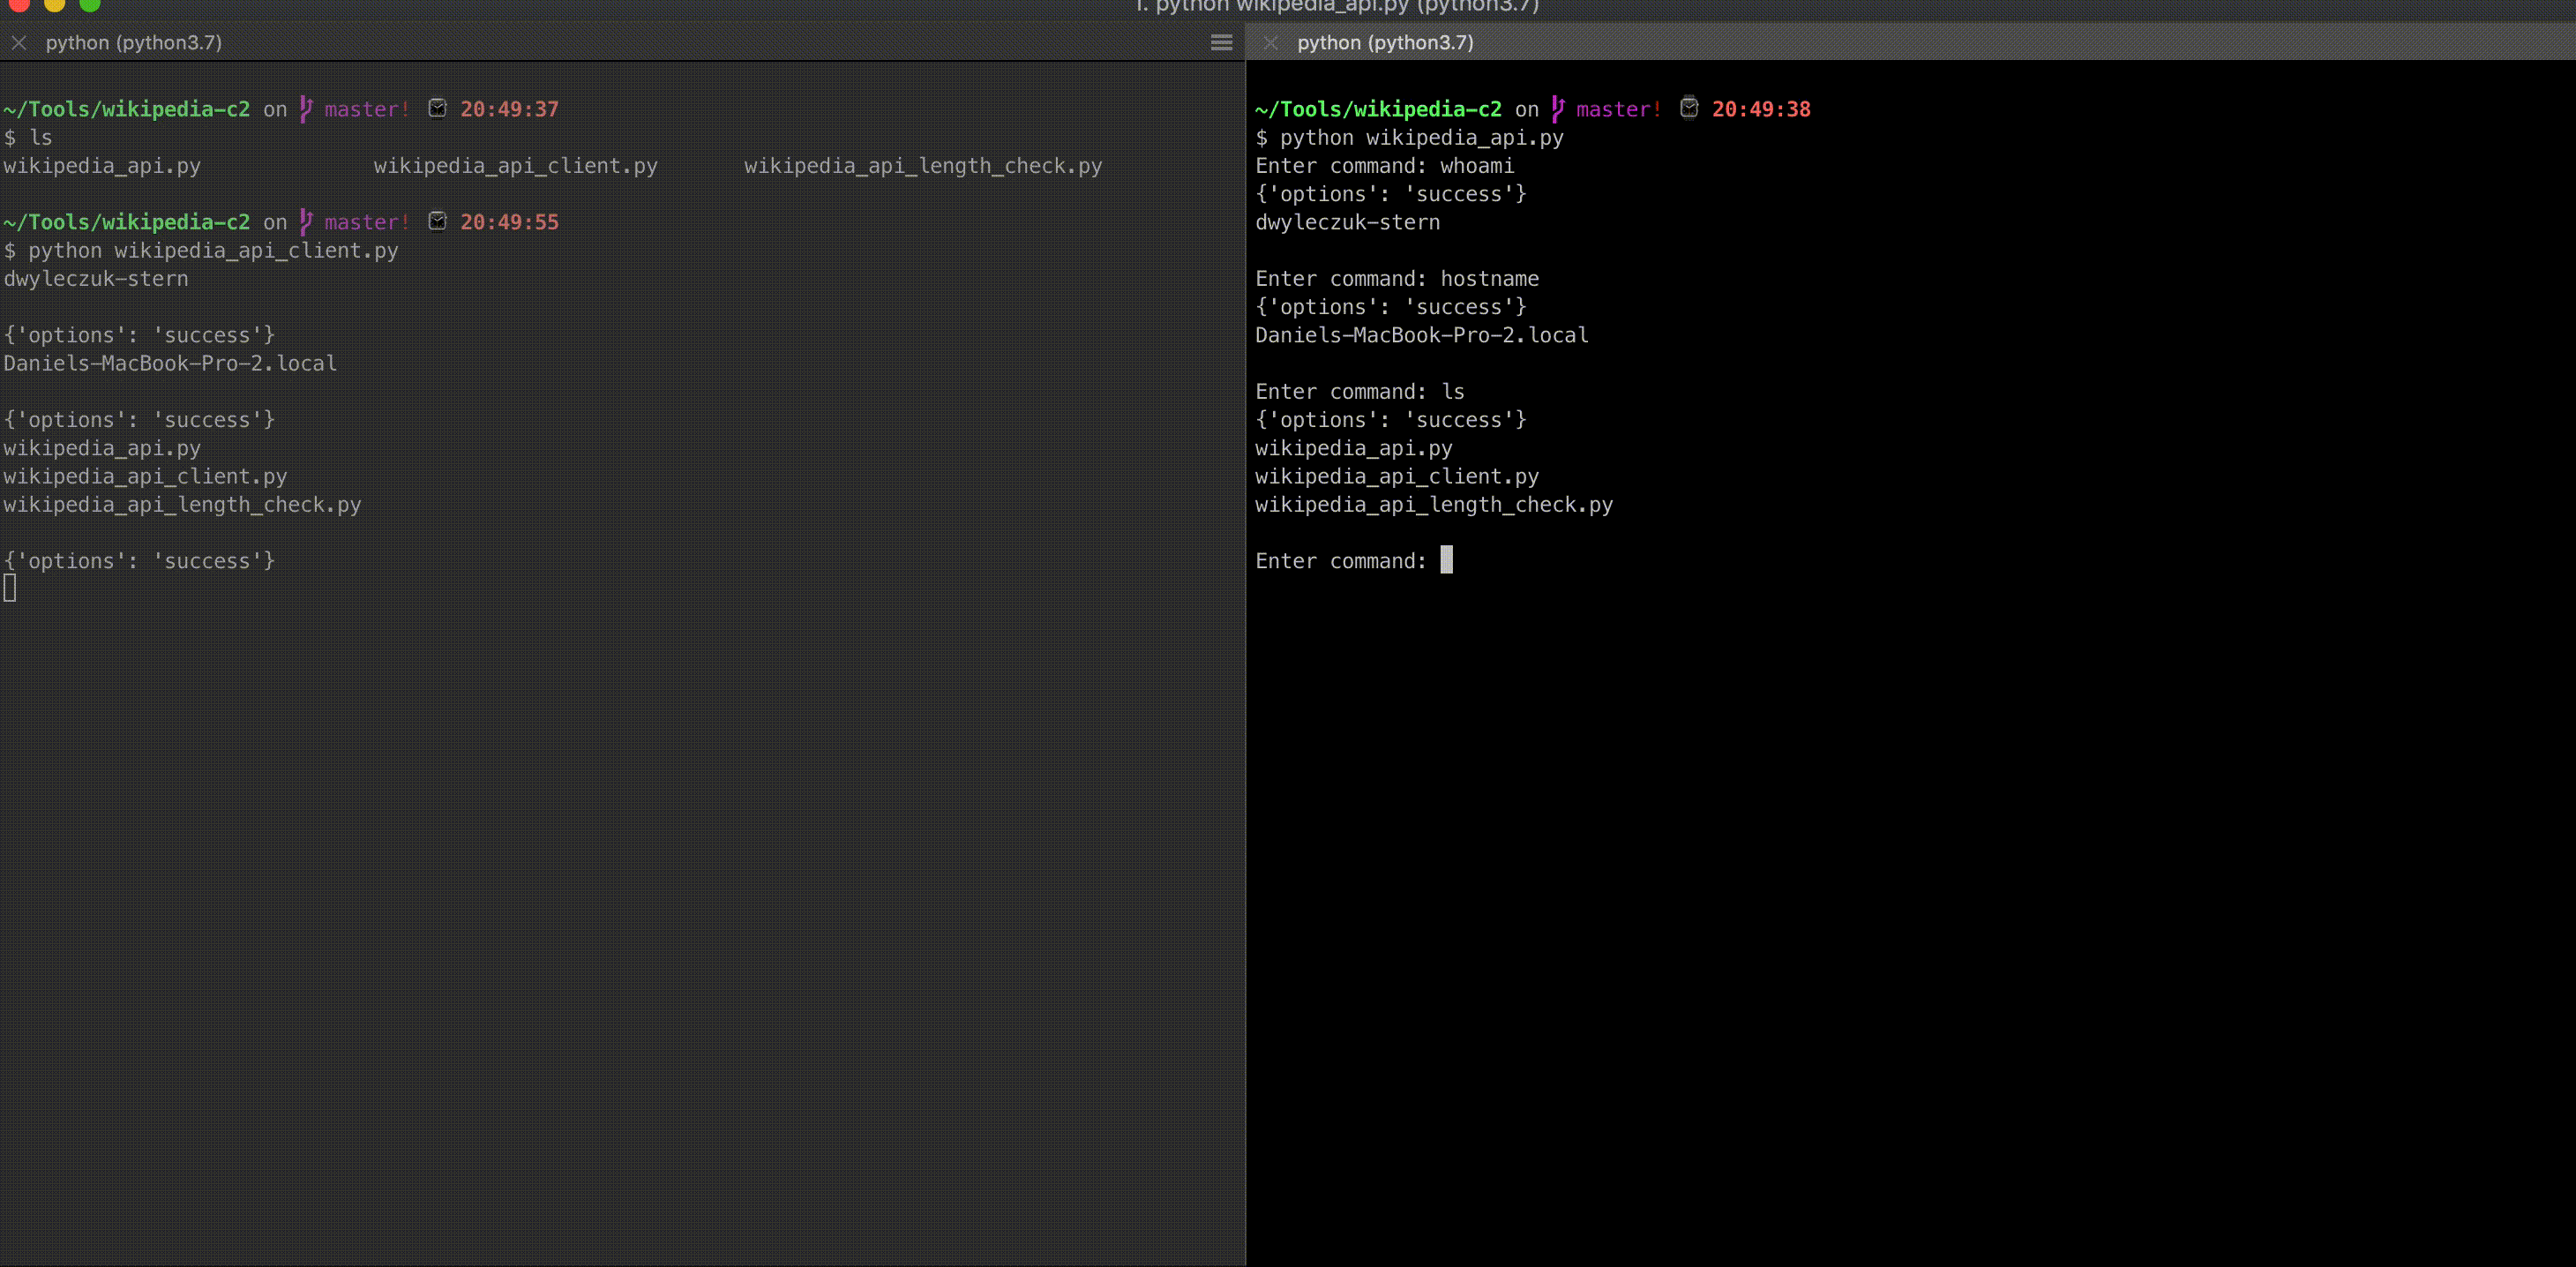 daniel-infosec/wikipedia-c2
POC for utilizing wikipedia API for Command and Control
 studiomeyer-io/mcp-stdio-shellguard
Defense-in-depth bundle for MCP stdio servers: drop-in guardExec/guardSpawn wrappers, AST audit CLI, reference MCP server. Closes the Ox-Security…
 cappricio-securities/cappriciosec-university
A Hacker's E-learning App for Tamil People
 usebruno/bruno
Opensource IDE For Exploring and Testing API's (lightweight alternative to Postman/Insomnia)
 everywall/ladder
Selfhosted alternative to 12ft.io. and 1ft.io. Proxy to remove CORS headers and modify HTML
 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 furkankayapinar/react-next-scanner
CVE-2025-55182 and CVE-2025-66478
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.